
user-scanner
 kaifcodec/user-scanner
Multi-platform OSINT scanner for email and username reconnaissance across 295+ vectors. Extracts profile metadata, checks account registrations, and…
email-harvestinginformation-gatheringosint+2
5.3k
kaifcodec/user-scannerMulti-platform OSINT scanner for email and username reconnaissance across 295+ vectors. Extracts profile metadata, checks account registrations, and…
 rubysec/ruby-advisory-db
Community-maintained database of security advisories for Ruby gems and runtimes, providing structured CVE/GHSA data with patched versions for…
 0x4d31/fatt
FATT /fingerprintAllTheThings - a pyshark based script for extracting network metadata and fingerprints from pcap files and live network traffic
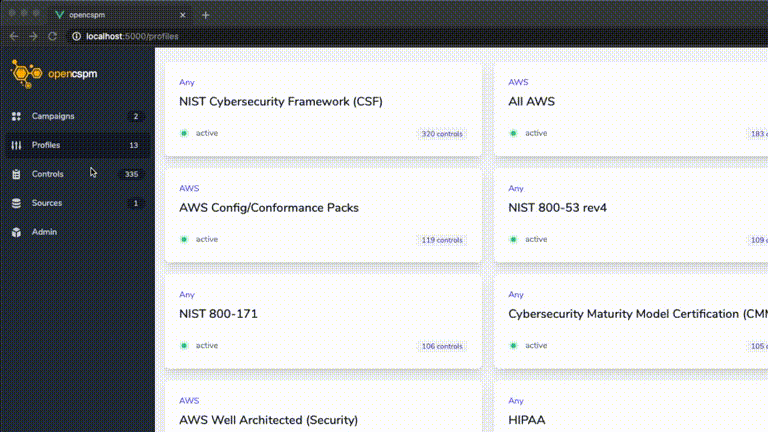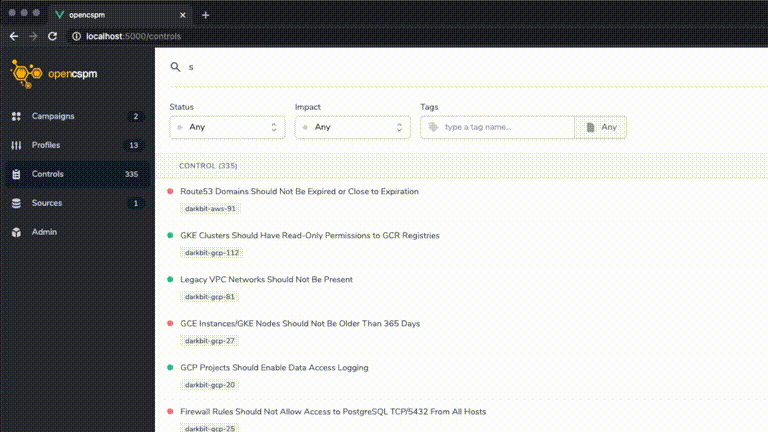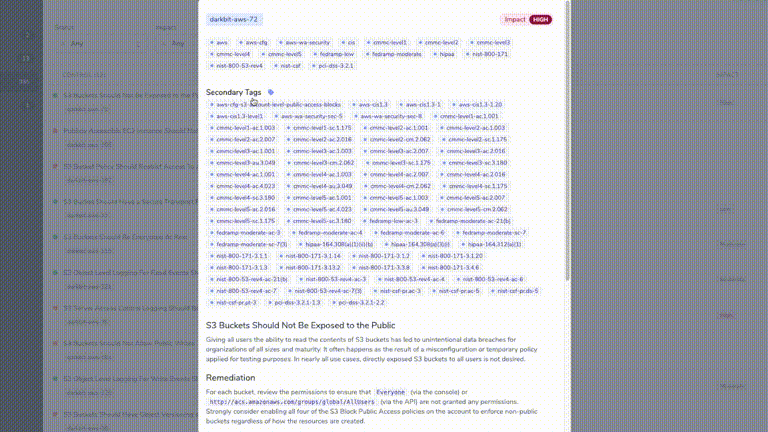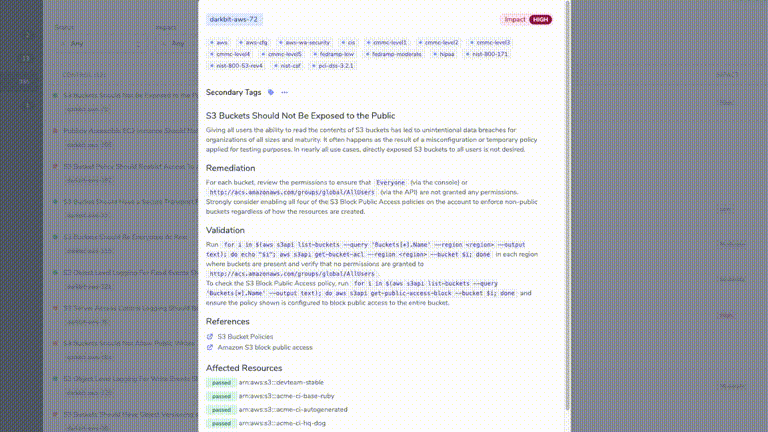 opencspm/opencspm
Open Cloud Security Posture Management Engine
 lockfale/osint-framework
Curated framework of free OSINT tools and resources for gathering intelligence from public sources, organized by category with structured metadata…
 drunkf0x/adspider
Monitor changes in Active Directory with replication metadata
 redsiege/just-metadata
Just-Metadata is a tool that gathers and analyzes metadata about IP addresses. It attempts to find relationships between systems within a large…
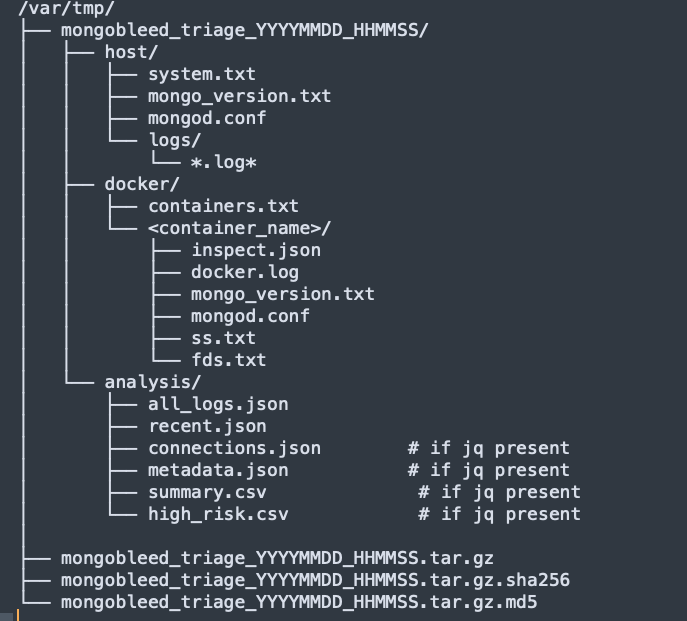 jemhadar/mongobleed-dfir-triage-script-cve-2025-14847
The script focuses on safe artifact acquisition first, followed by optional on-host analysis, and produces a portable, hashed forensic archive…
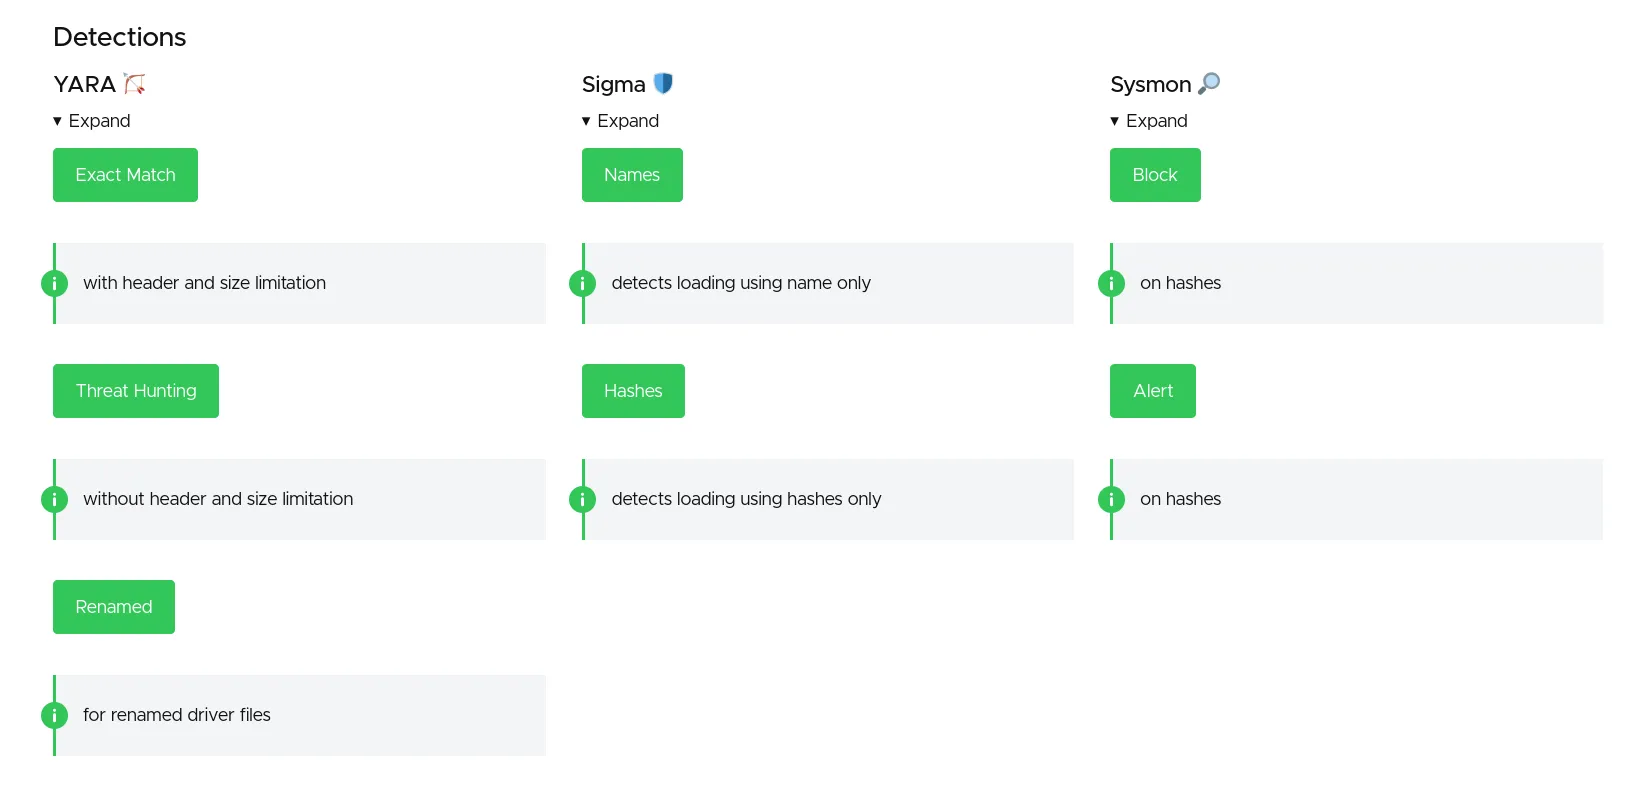 magicsword-io/loldrivers
Curated database of vulnerable and malicious Windows drivers with YARA, Sigma, ClamAV, and Sysmon detection rules for proactive threat hunting and…
 nova-hunting/nova-tracer
NOVA - Claude Code Protection System against prompt injection attacks
 perplexityai/bumblebee
Read-only developer endpoint scanner for on-disk package, extension, and developer-tool metadata, built to check exposure to known software…
 gautamvarmadatla/mcpsafetywarden
Proxy server that wraps MCP servers with behavioral profiling, security scanning, risk gating, and safe execution. Detects prompt injection,…
 darksight-analytics/tgspyder
CLI tool for structured Telegram OSINT data collection. Scrapes members, messages, invite links, and user metadata from public/private groups,…
 pan-unit42/dotnetfile
Python library for parsing CLR/PE metadata in .NET assemblies, exposing streams and hash fingerprints to support malware analysis and threat hunting.
 lupovis/honeypot-for-cve-2025-59287-wsus
Defensive PoC decoy for CVE-2025-59287 (WSUS) - emulates WSUS endpoints, captures request bodies and metadata, saves evidence for forensic analysis,…
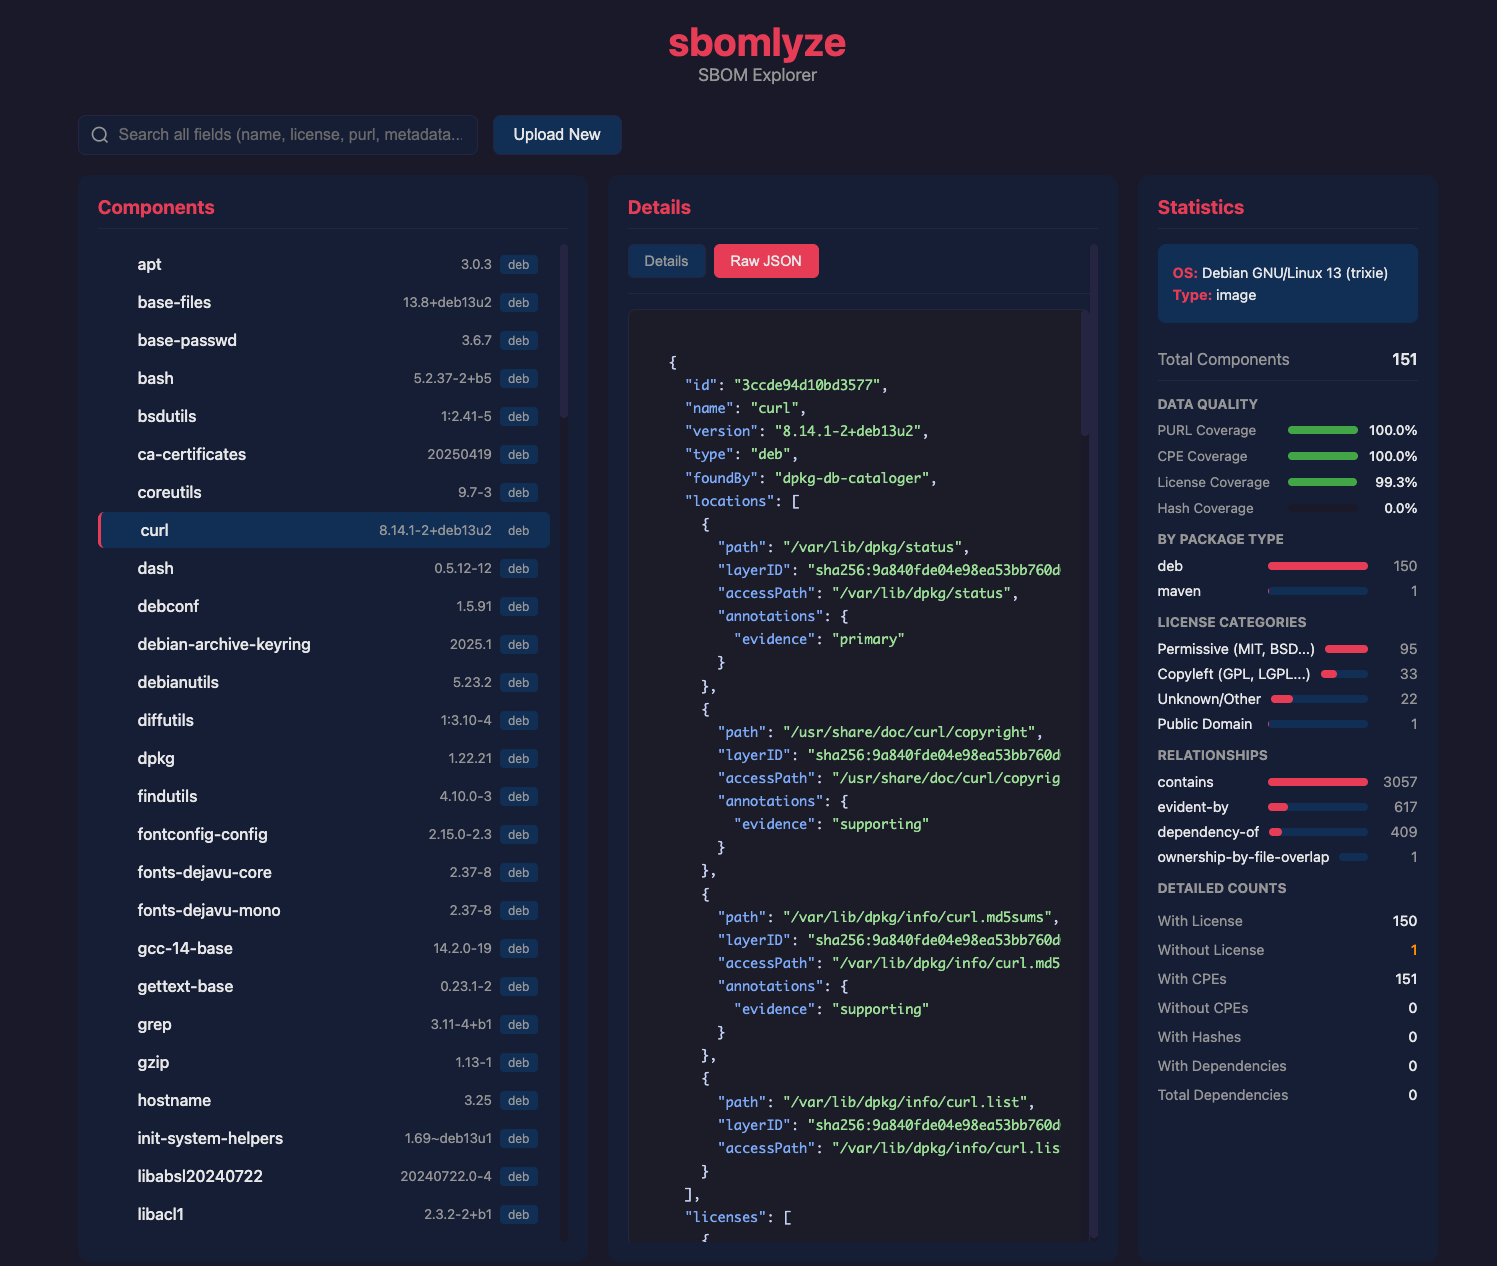 rezmoss/sbomlyze
Git diff for SBOMs—compare CycloneDX, SPDX, and Syft documents, detect tampering, and gate CI.
 zmap/zannotate
Utility for annotating Internet datasets with contextual metadata (e.g., origin AS, MaxMind GeoIP2, reverse DNS, and WHOIS)
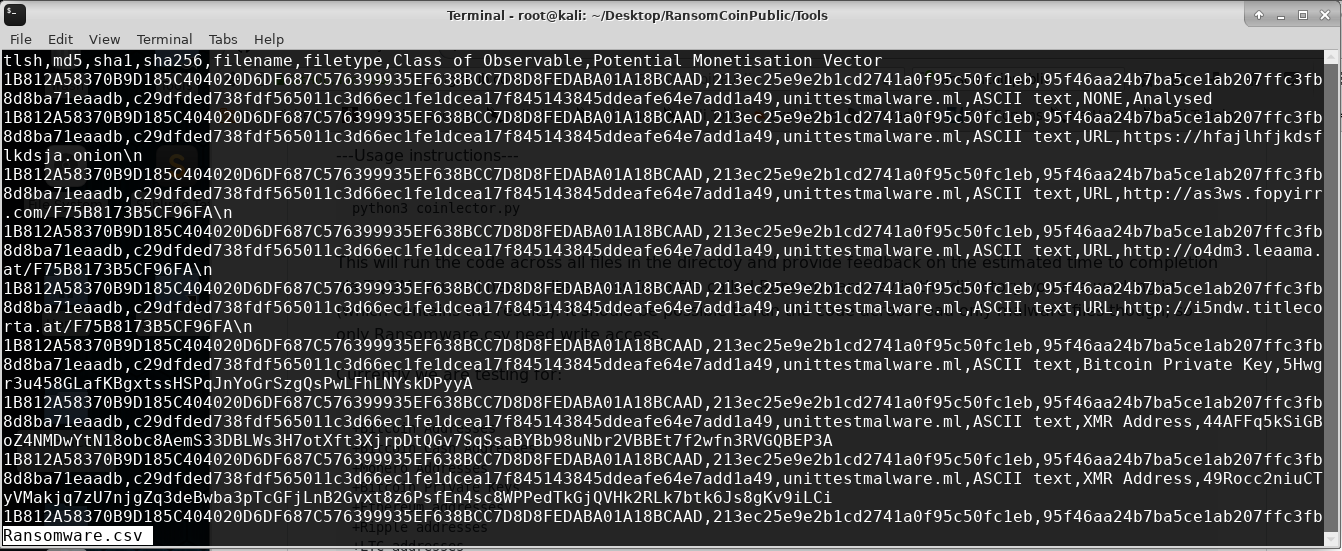 concinnity-risks/ransomcoinpublic
A DFIR tool to extract cryptocoin addresses and other indicators of compromise from binaries.