Incident-Response-Powershell

PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…

PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…

Technical dossier on the DPRK-linked PolinRider supply-chain attack, documenting obfuscated JS payload injection, git history manipulation, C2…

Detects CVE-2026-45321 (TanStack supply chain compromise) and Mini Shai-Hulud worm artifacts. Scans node_modules, lockfiles, persistence hooks…

Tracking history of USB events on GNU/Linux

Daily-updated JSON repository of NVD/CVE vulnerability data, enabling easy retrieval and git-based exploration of CVE modification history for…

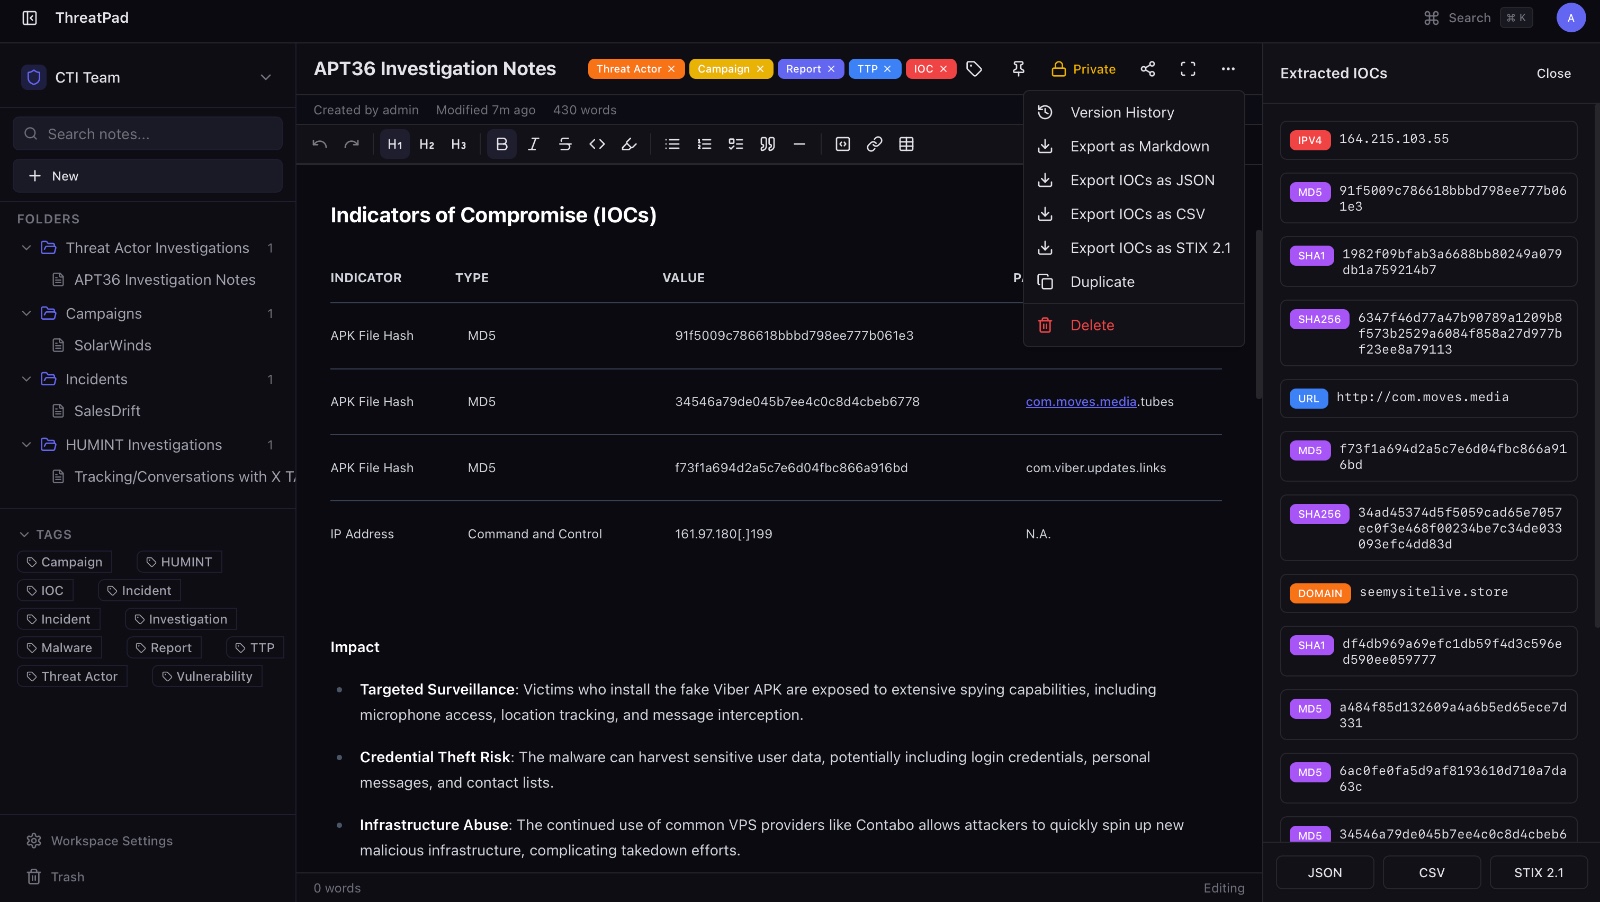
Open-source collaborative note-taking platform for cybersecurity and CTI teams. IOC auto-extraction, STIX 2.1 export, real-time editing, RBAC,…

Collects comprehensive triage data from macOS for incident response, including system logs, file listings, browser data, shell history, and…

A lightweight aviation intelligence tool that queries ADSB-Exchange flight data using tail numbers or ICAO identifiers to quickly profile aircraft…

History of commits related to the xz backdoor Discovered On March 29, 2024: CVE-2024-3094.