
DShield-SIEM
 bruneaug/dshield-siem
DShield Sensor Log Collection with ELK
defensive-toolsincident-responseintrusion-detection+4
bruneaug/dshield-siemDShield Sensor Log Collection with ELK
 adham504/sentinelthread-forensics
High-speed Windows forensic triage platform that orchestrates the Hayabusa engine to transform raw EVTX logs into prioritized threat timelines with…
 payloadsecurity/sandbox_scryer
Parses public sandbox detonation reports to produce threat hunting intelligence, organizes findings via MITRE ATT&CK, assembles IOCs, and generates…
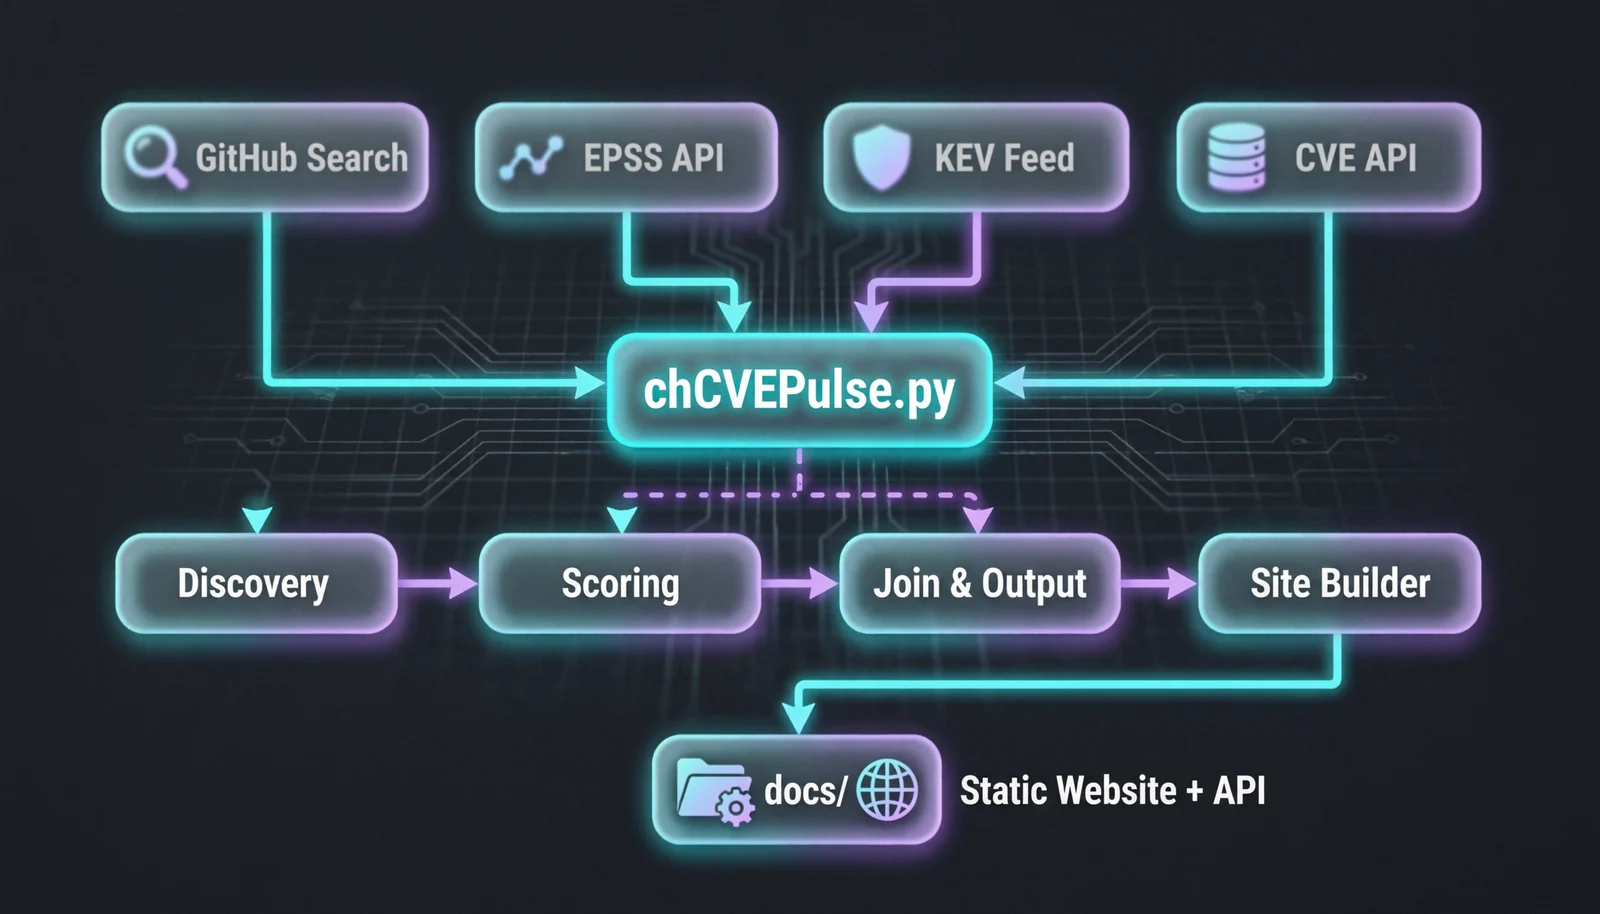 ch4120n/ch4120n-cve-pulse
Live CVE PoC (Proof-of-Concepts) Aggregator with Smart Search & Threat Intelligence
 mthcht/awesome-lists
Curated repository of threat intelligence feeds, IoC lists, YARA rules, and DFIR tool references for SOC/CERT/CTI detection and incident response.
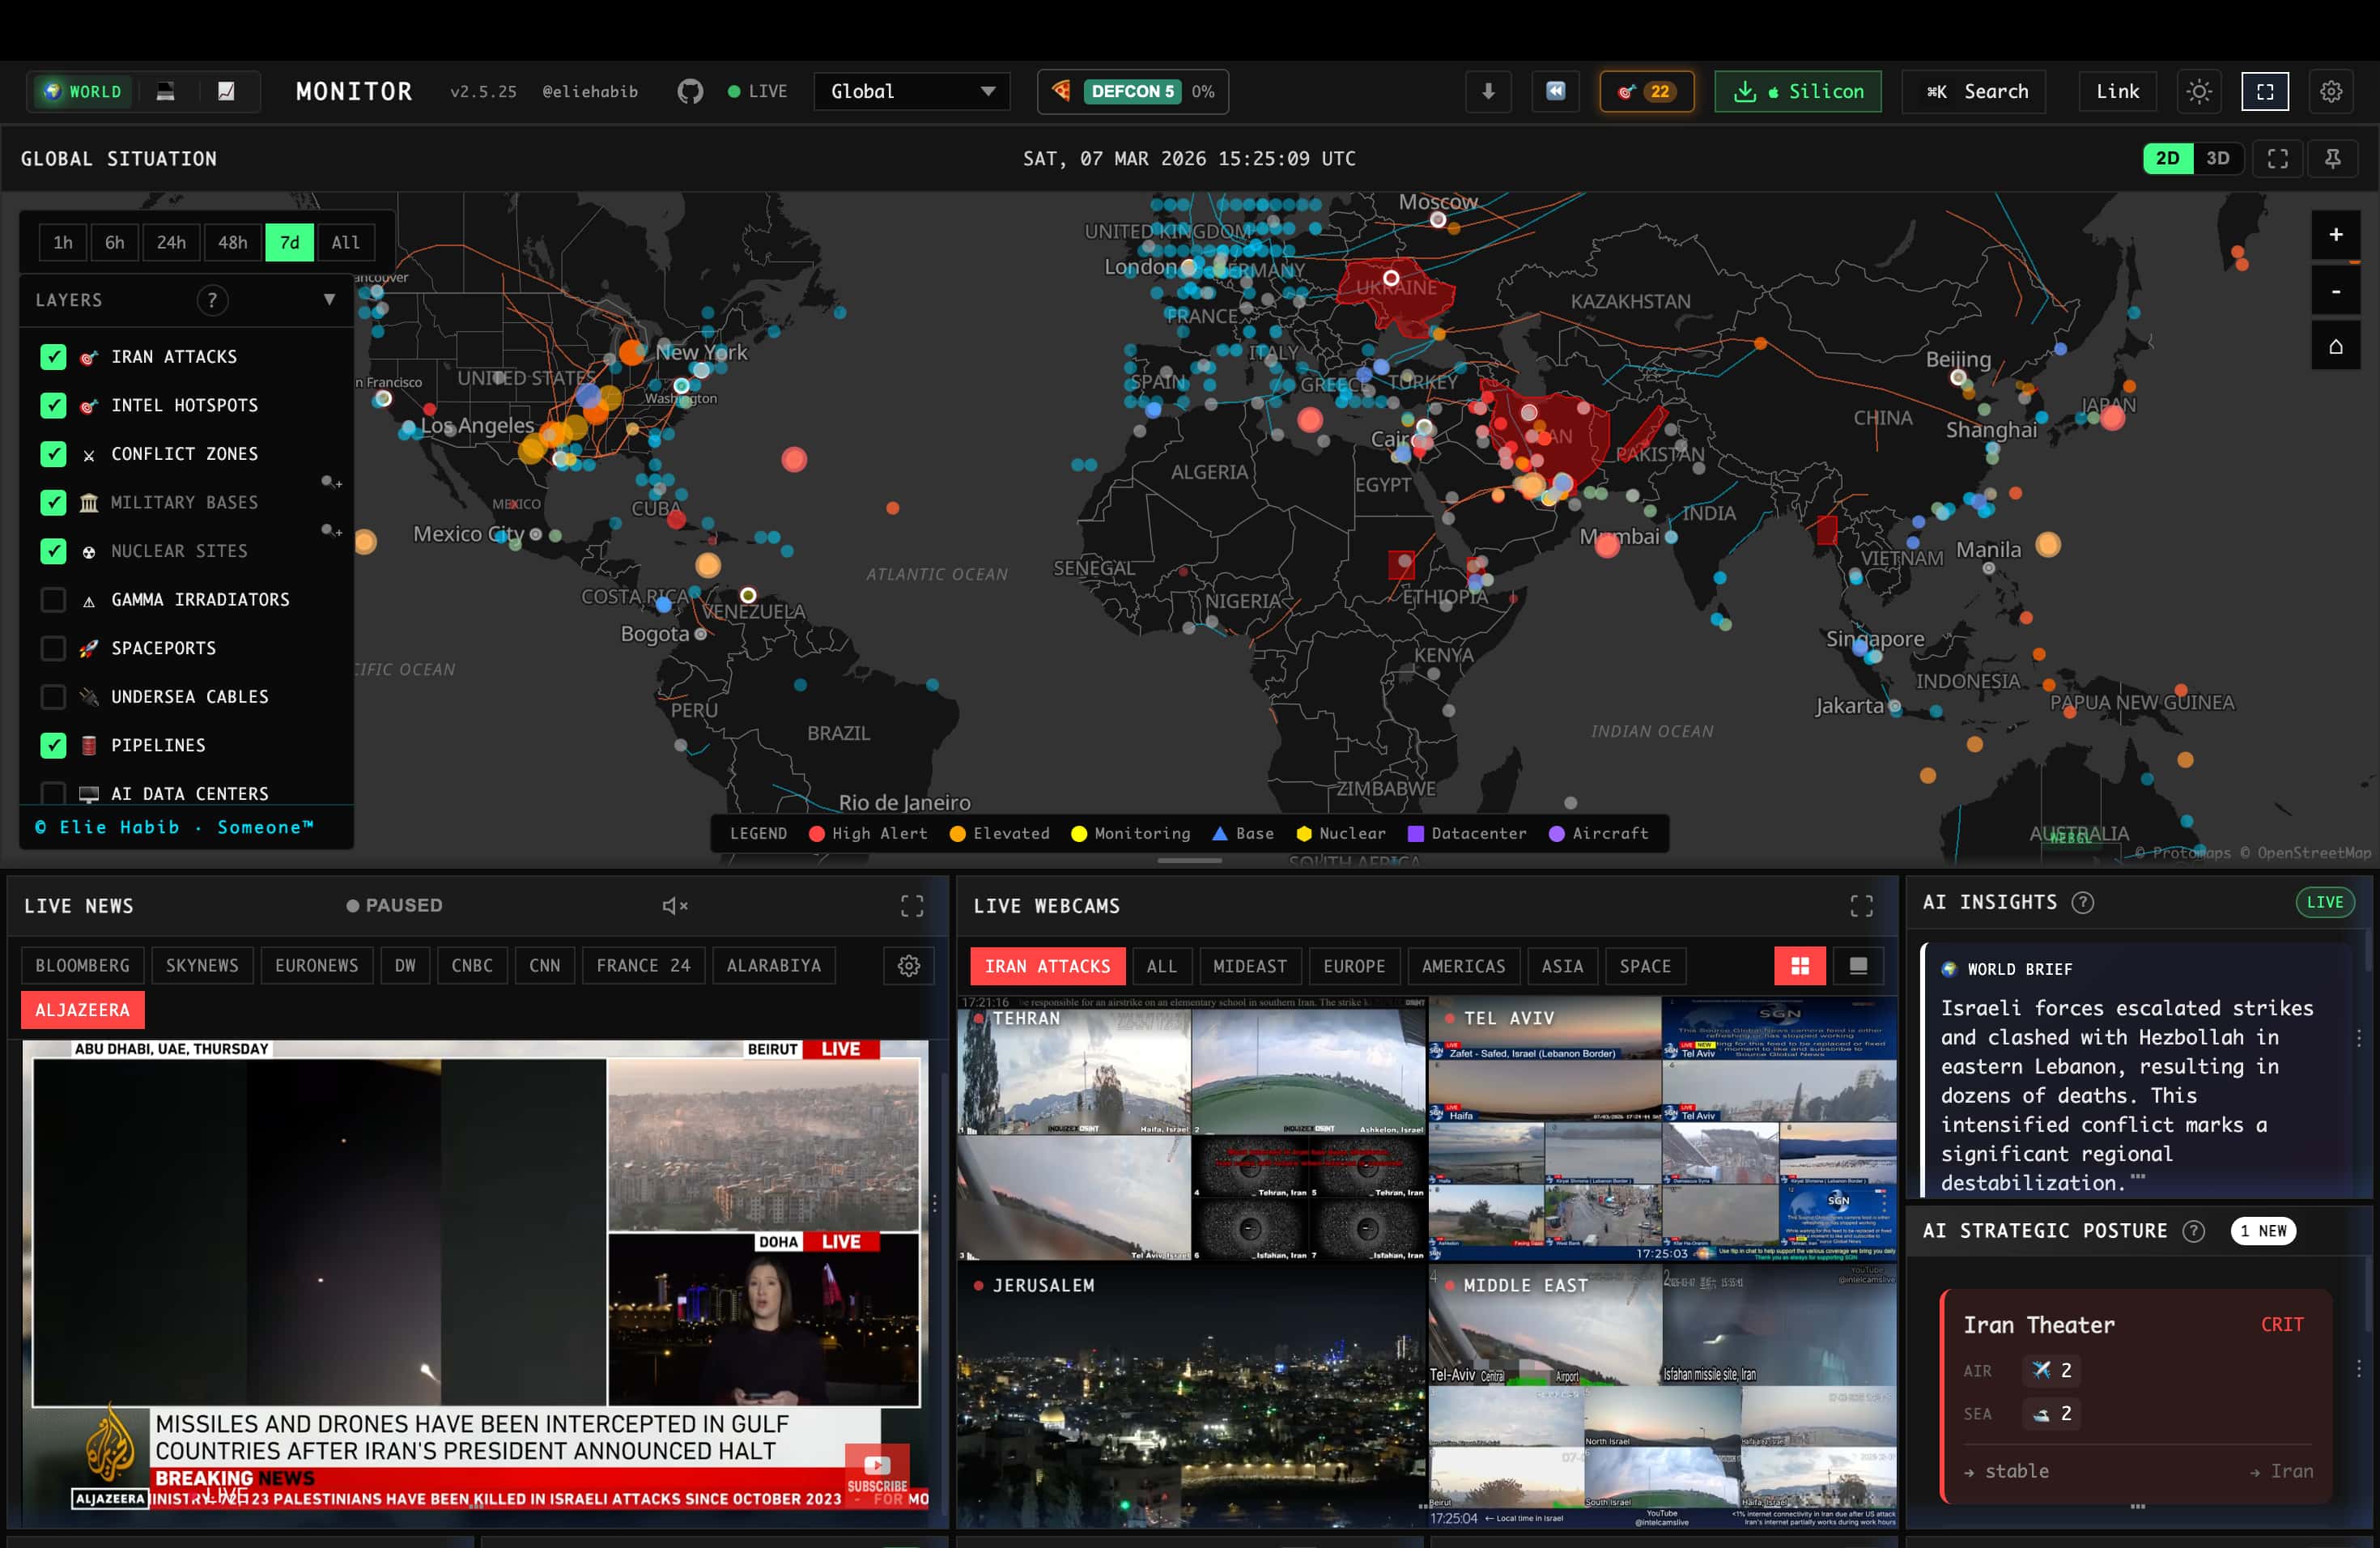 koala73/worldmonitor
Real-time global intelligence dashboard. AI-powered news aggregation, geopolitical monitoring, and infrastructure tracking in a unified situational…
 vxunderground/threatintelligencediscordbot
Gets updates from various clearnet domains and ransomware threat actor domains
 toborrm9/malicious_extension_sentry
Malicious Extension Database
 sumidcyber/zeroscout
🦅 ZeroScout: The Autonomous Local & Cloud Threat Hunter. Visualize attacks in a live War Room, identify APT groups via Genetic Analysis, and…