
log4shell_ioc_ips
 hackinghippo/log4shell_ioc_ips
log4j / log4shell IoCs from multiple sources put together in one big file (IPs) more coming soon (CVE-2021-44228)
incident-responseinformation-gatheringioc-management+3
37
hackinghippo/log4shell_ioc_ipslog4j / log4shell IoCs from multiple sources put together in one big file (IPs) more coming soon (CVE-2021-44228)
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
 bert-janp/open-source-threat-intel-feeds
This repository contains Open Source freely usable Threat Intel feeds that can be used without additional requirements. Contains multiple types such…
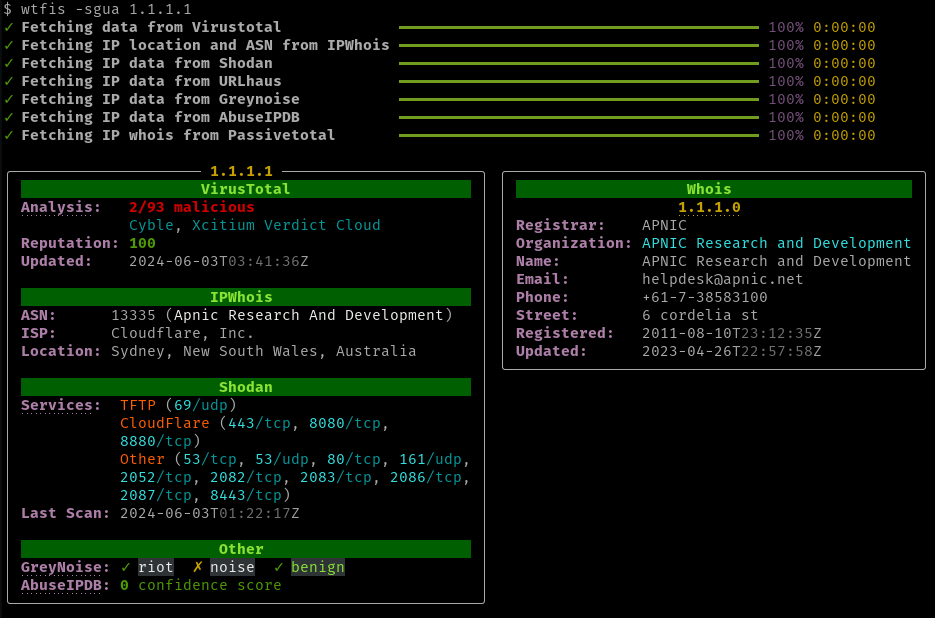 pirxthepilot/wtfis
Passive hostname, domain and IP lookup tool for non-robots
 1an0rmus/tekdefense-automater
Automater - IP URL and MD5 OSINT Analysis
 inquest/threatkb
Knowledge base workflow management for YARA rules and C2 artifacts (IP, DNS, SSL) (ALPHA STATE AT THE MOMENT)
 cred-club/artif
An advanced real time threat intelligence framework to identify threats and malicious web traffic on the basis of IP reputation and historical data.
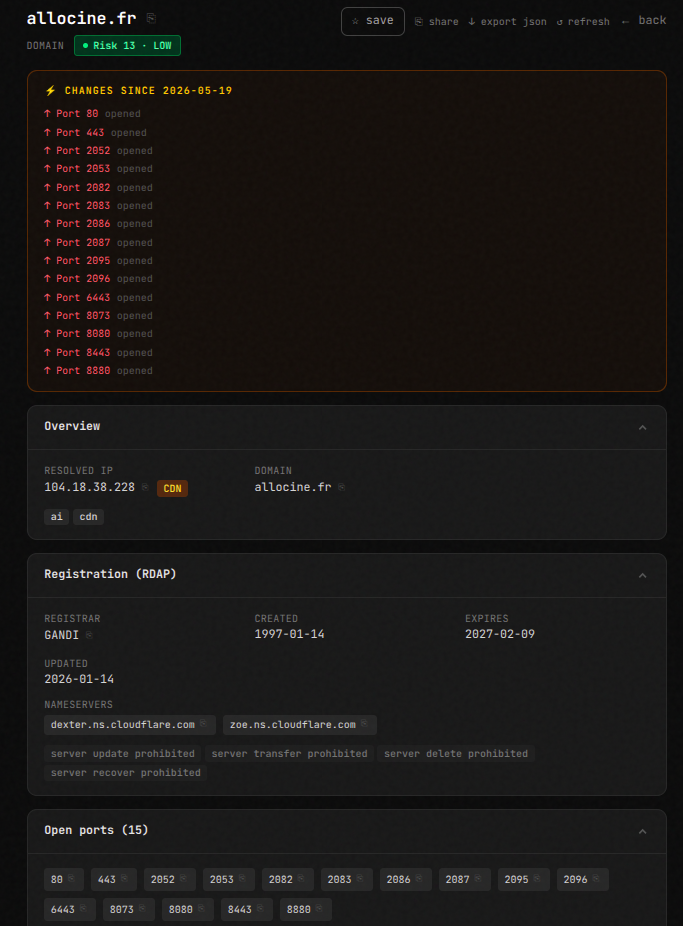 teycir/seekyou
OSINT intelligence on any IP, domain, or ASN
 intelowlproject/intelowl
Scalable threat intelligence platform that enriches observables and files using 200+ analyzers, with built-in GUI, REST API, and automated workflows…
 montysecurity/c2-tracker
Live Feed of C2 servers, tools, and botnets