
pulledpork
 shirkdog/pulledpork
Pulled Pork for Snort and Suricata rule management (from Google code)
configuration-auditingintrusion-detectionnetwork-security+2
4425 years ago
shirkdog/pulledporkPulled Pork for Snort and Suricata rule management (from Google code)
 bfuzzy/auditd-attack
A Linux Auditd rule set mapped to MITRE's Attack Framework
 duggytuxy/data-shield_ipv4_blocklist
Curated IPv4 blocklist of malicious addresses, refreshed every 6 hours for firewall and WAF ingestion, with split lists and CTI-ready formats for…
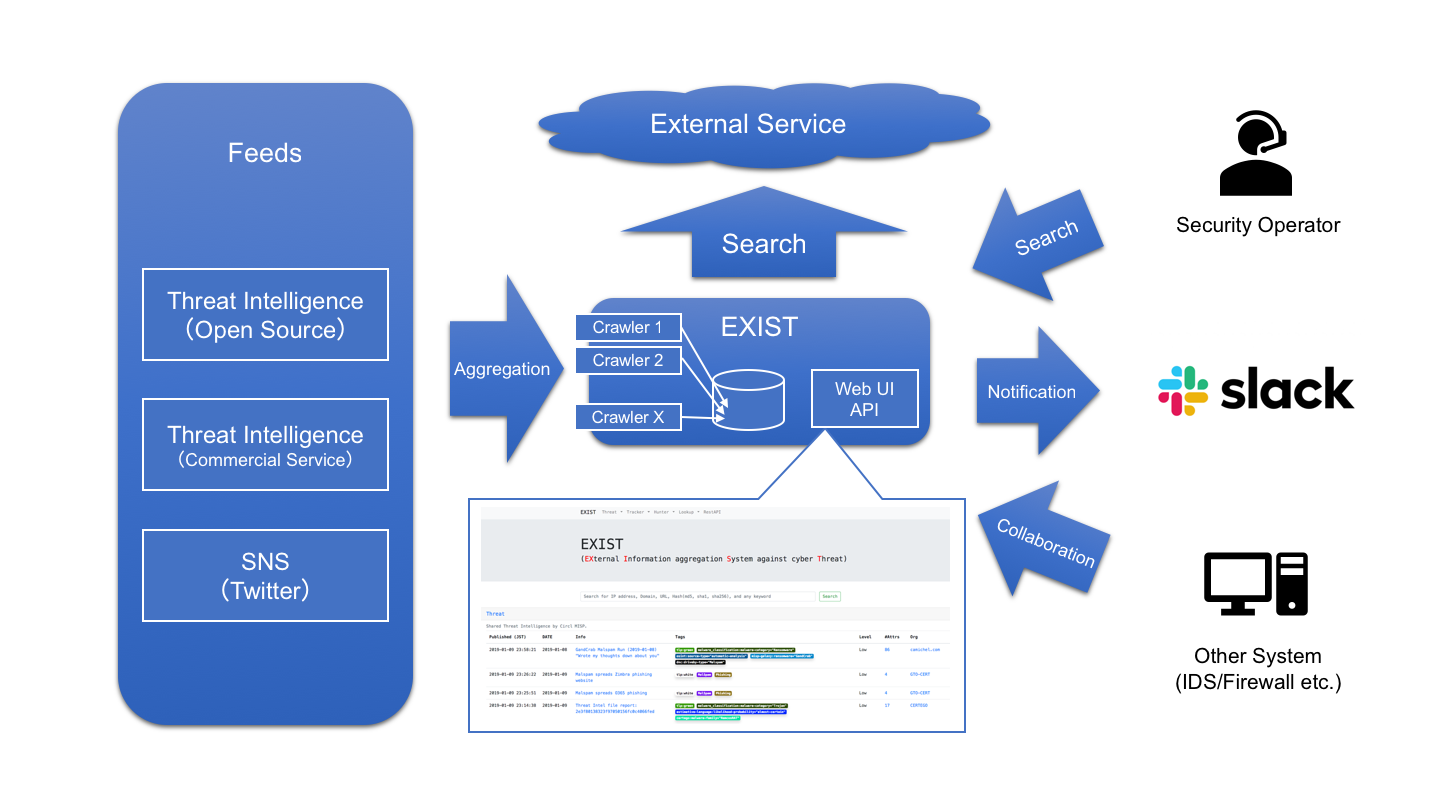 nict-csl/exist
EXIST is a web application for aggregating and analyzing cyber threat intelligence.
 olafhartong/threathunting
A Splunk app mapped to MITRE ATT&CK to guide your threat hunts
 patrowl/patrowlhears
PatrowlHears - Vulnerability Intelligence Center / Exploits
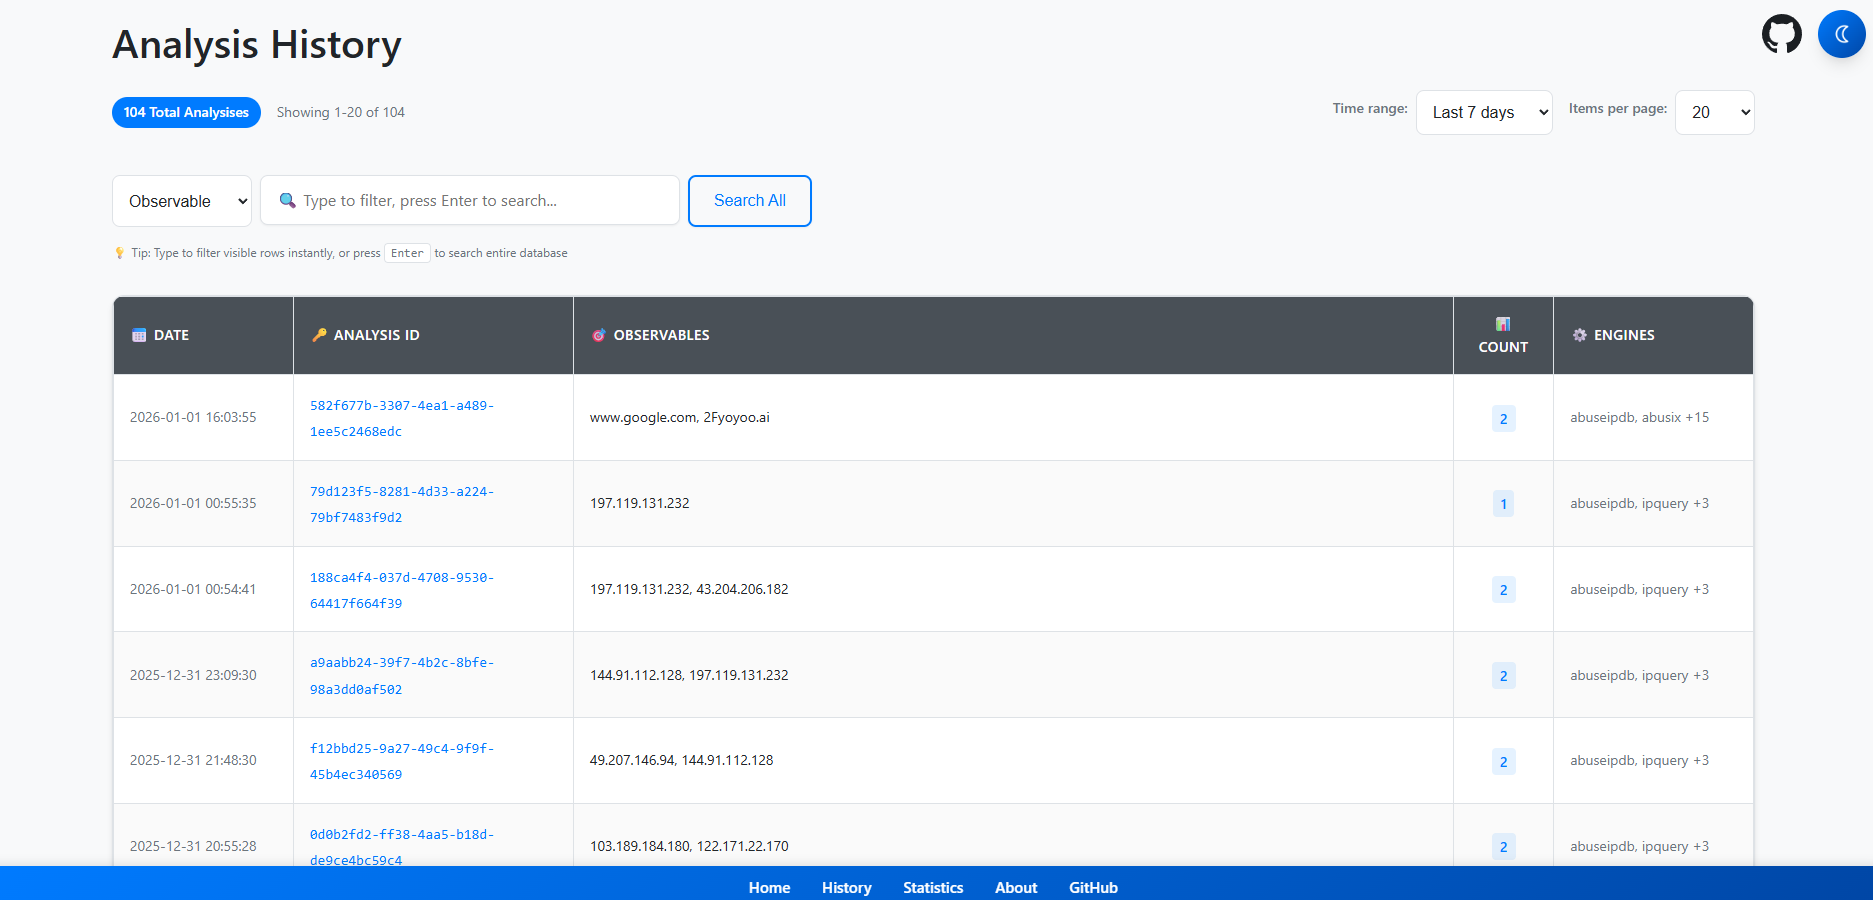 stanfrbd/cyberbro
A simple application that extracts your IoCs from garbage input and checks their reputation using multiple CTI services.
 eclecticiq/opentaxii
TAXII server implementation in Python from EclecticIQ
 aquasecurity/secfixes-tracker
Forked from https://gitlab.alpinelinux.org/kaniini/secfixes-tracker