
ThreatKB
 inquest/threatkb
Knowledge base workflow management for YARA rules and C2 artifacts (IP, DNS, SSL) (ALPHA STATE AT THE MOMENT)
information-gatheringioc-managementmalware-analysis+2
104
inquest/threatkbKnowledge base workflow management for YARA rules and C2 artifacts (IP, DNS, SSL) (ALPHA STATE AT THE MOMENT)
 ciscocsirt/gosint
The GOSINT framework is a project used for collecting, processing, and exporting high quality indicators of compromise (IOCs).
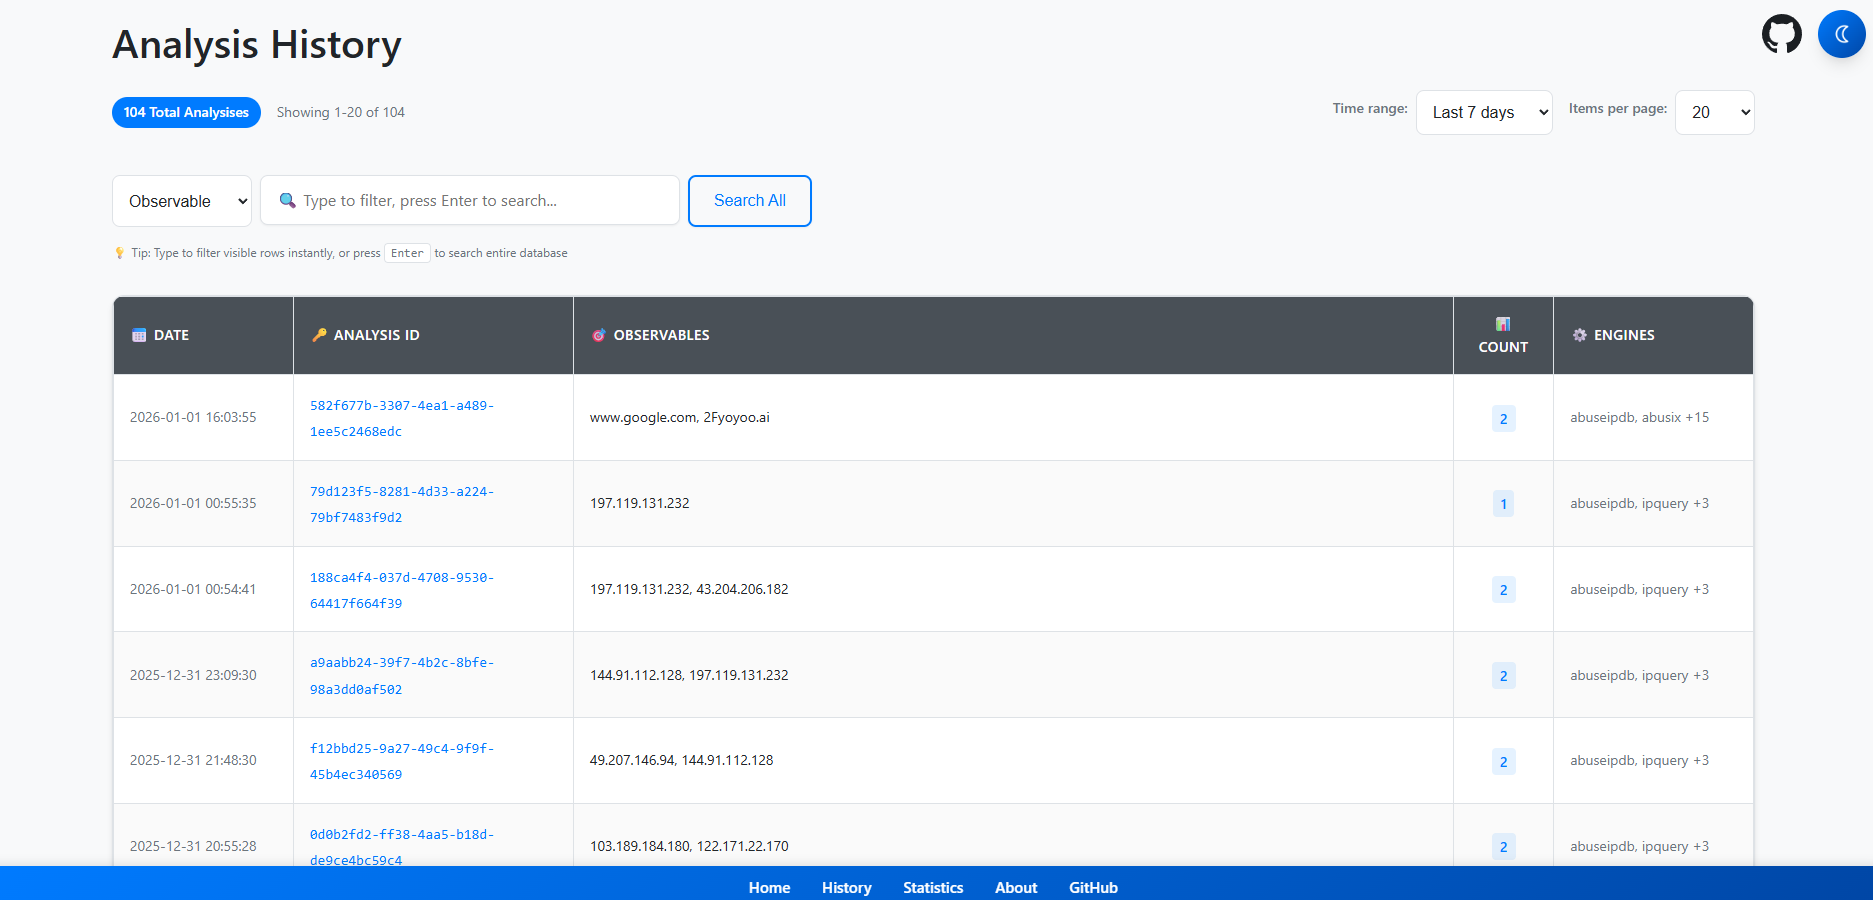 stanfrbd/cyberbro
A simple application that extracts your IoCs from garbage input and checks their reputation using multiple CTI services.
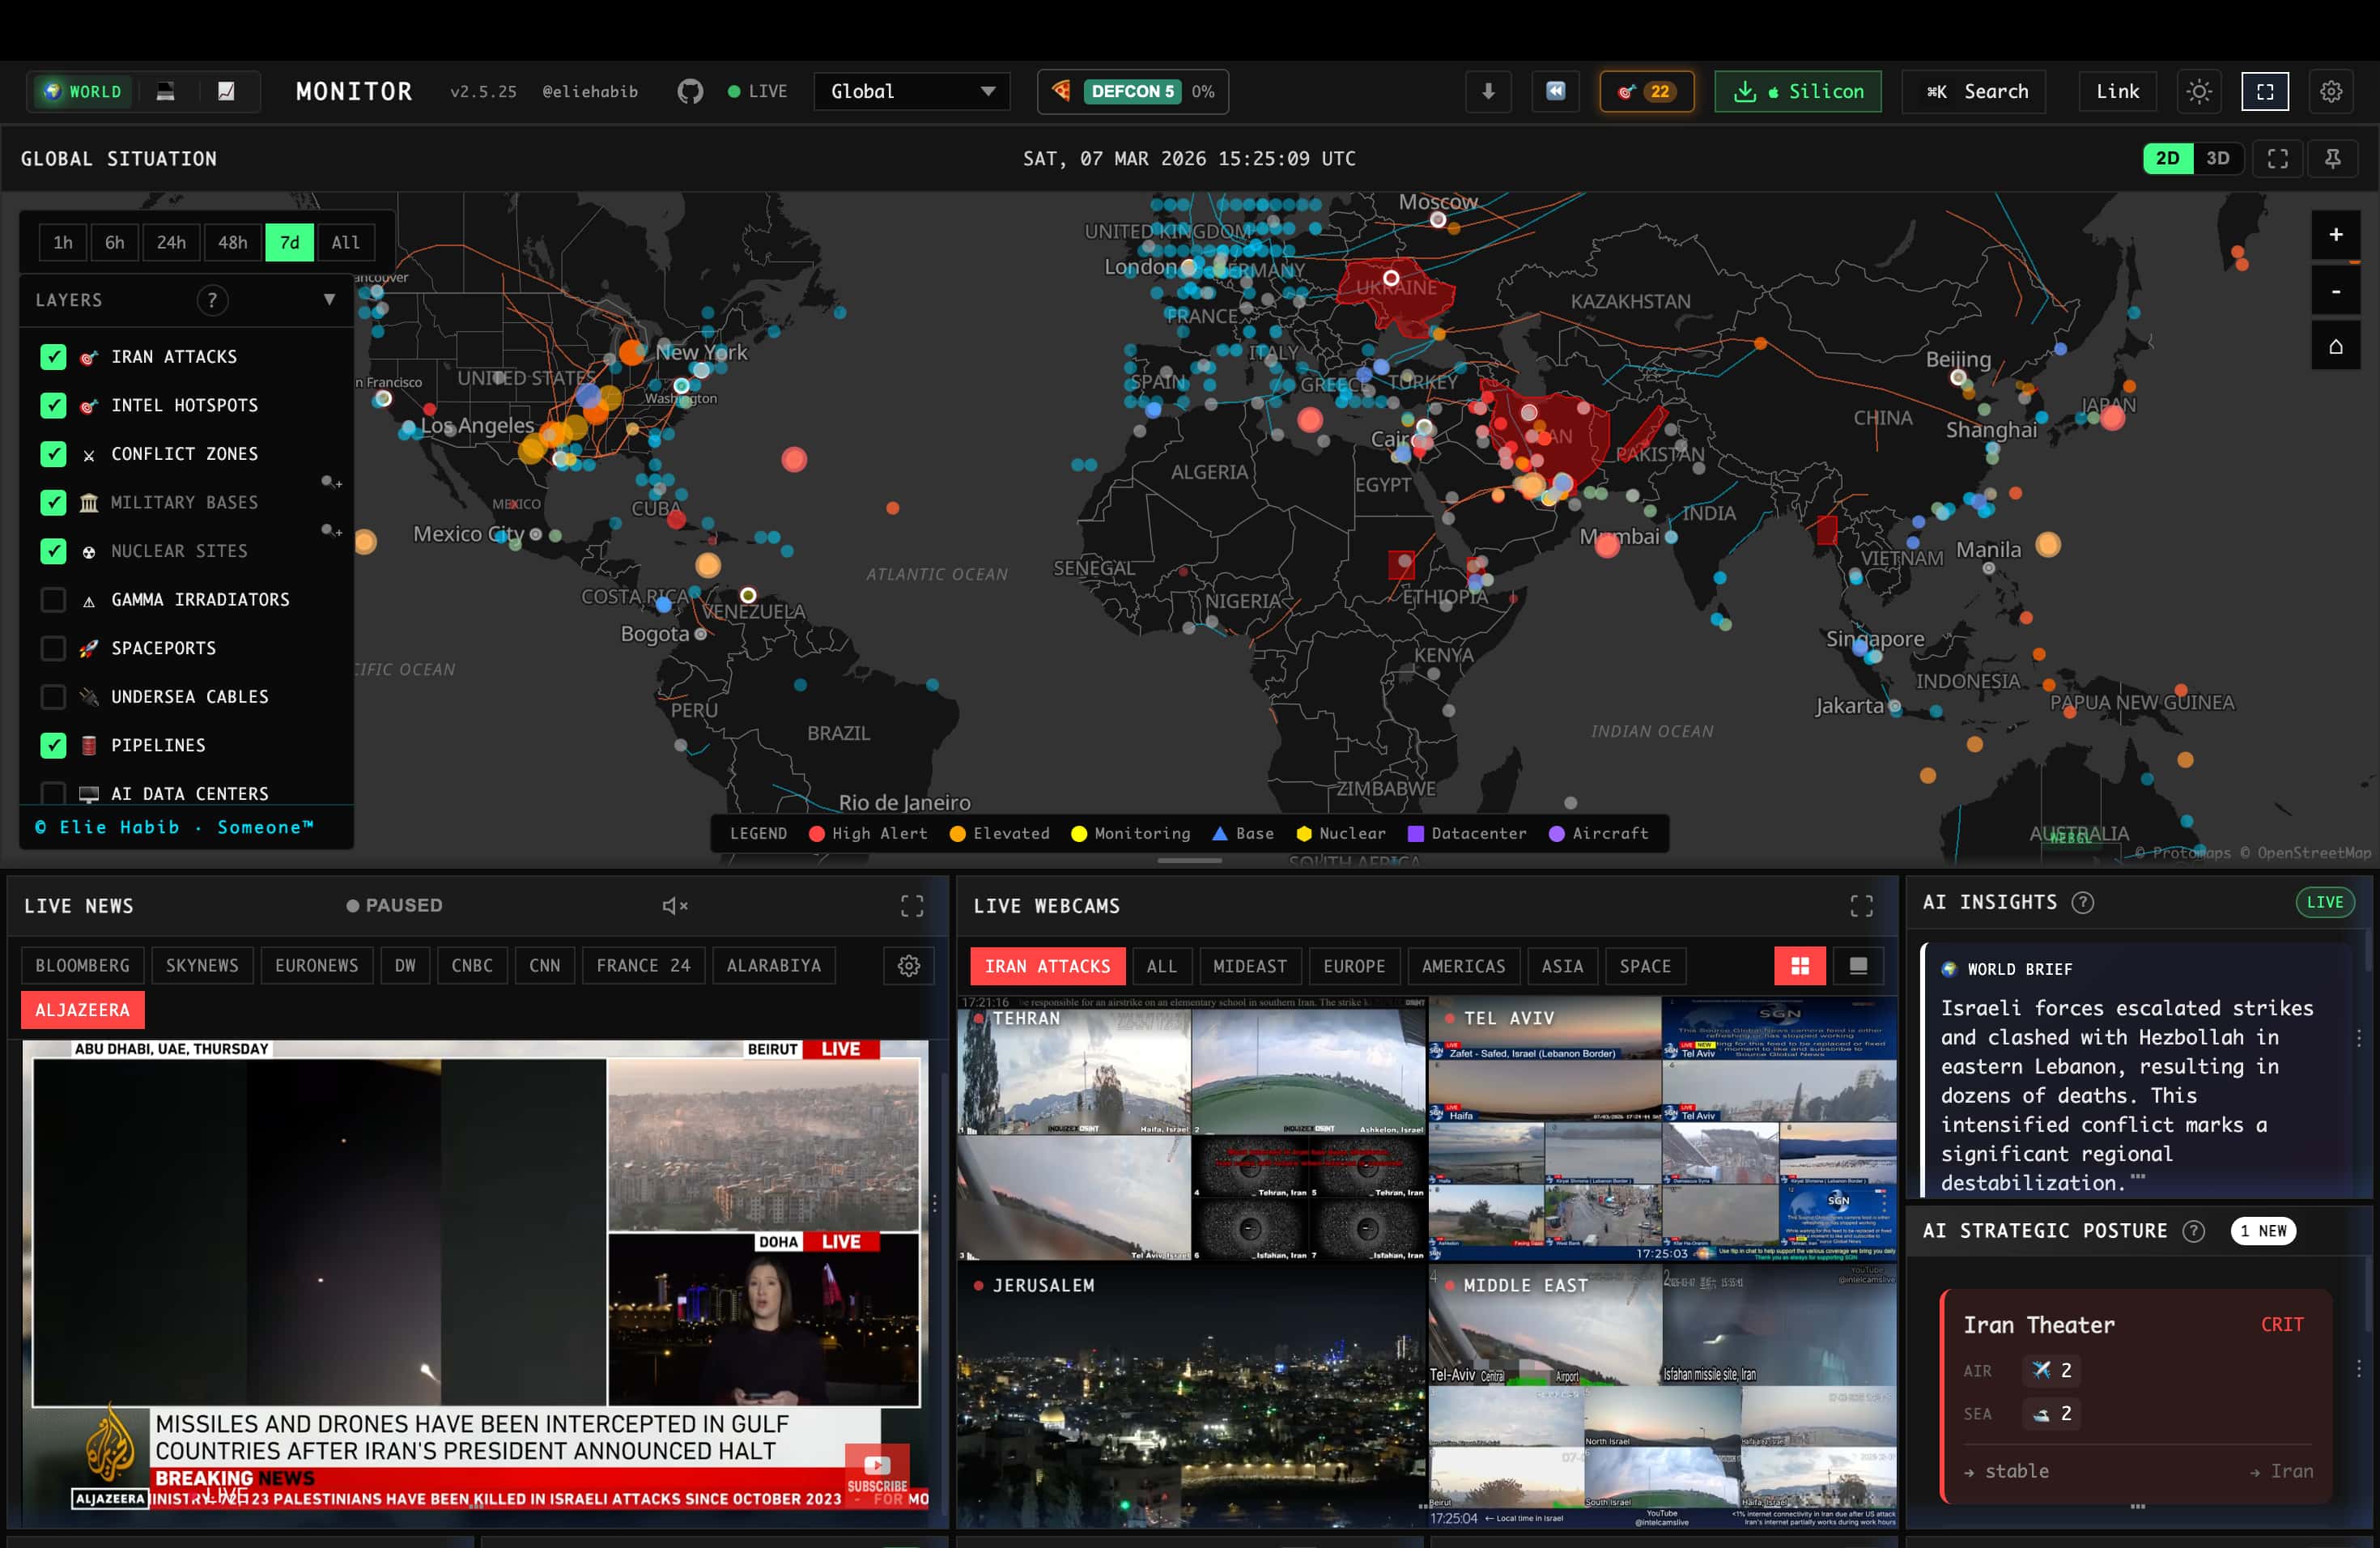 koala73/worldmonitor
Real-time global intelligence dashboard. AI-powered news aggregation, geopolitical monitoring, and infrastructure tracking in a unified situational…
 ethan-andrews/threatintel-aggregator
Self-hosted threat intelligence platform — feed aggregation, AI triage, MITRE ATT&CK coverage, and Sentinel-integrated detection engineering. Runs…
 kaal22/darkgrid
3D threat intelligence dashboard that visualizes malicious infrastructure from OSINT sources like AbuseIPDB and OpenPhish, with a live threat feed,…

 functori/argos/argos
Analysis and Representation of Graphs of Suspicious Operations (Analyse et Représentation des Graphes des Opérations Suspectes)
 bruneaug/dshield-siem
DShield Sensor Log Collection with ELK
 crowdsecurity/crowdsec
Open-source IDS/IPS and WAF engine that analyzes logs and HTTP requests to detect and block malicious IPs, leveraging a crowdsourced community…
 the-art-of-hacking/h4cker
Curated collection of cybersecurity resources, labs, and training materials covering ethical hacking, penetration testing, exploit development,…
 facebook/threatexchange
Trust & Safety tools for working together to fight digital harms.
 eclecticiq/opentaxii
TAXII server implementation in Python from EclecticIQ
 fastfire/ioc_attack_esxi_feb_2023
Collection of IoCs available and related to attacks on ESXi infrastructures that occurred as of Friday February 3, 2023.
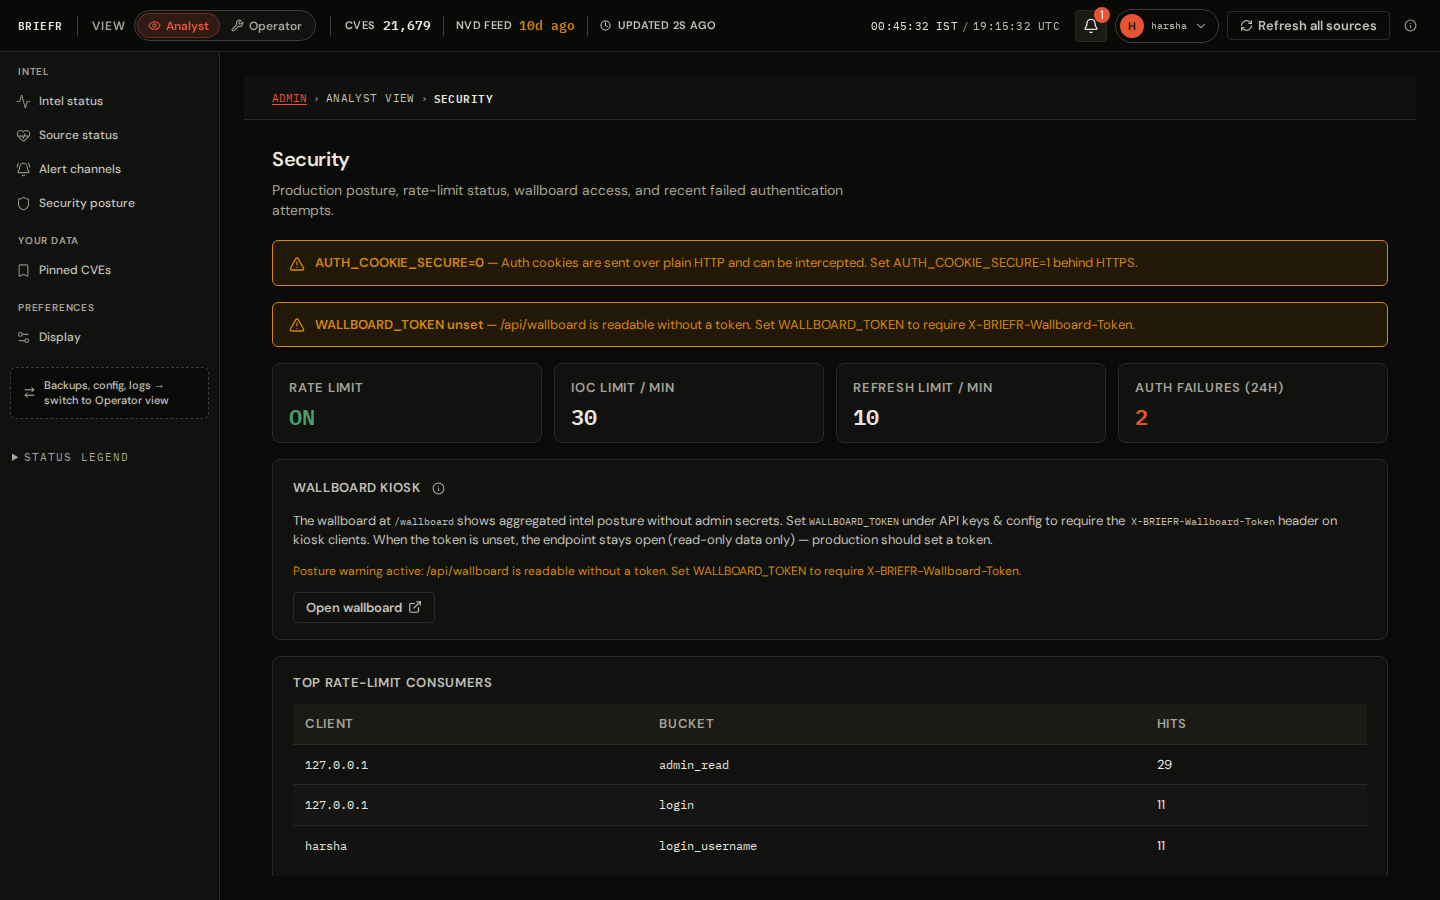 soldier0x0/briefr
Open Vulnerability Intelligence platform, aggregated intel in one dashboard, with correlation and IOC lookups, completely self hosted. All resources…
 cspf-founder/darwis-taxii
A high-performance TAXII (Trusted Automated eXchange of Indicator Information) server written in Rust.