
BRIntelcollector
 qbitseclabs/brintelcollector
Cyber Threat Intelligence (CTI) usando fontes e indicadores de ameaças nacionais, ou até globais, mas com evidencias ou indicadores nacionais do…
information-gatheringosintthreat-feeds-aggregators+1
8
qbitseclabs/brintelcollectorCyber Threat Intelligence (CTI) usando fontes e indicadores de ameaças nacionais, ou até globais, mas com evidencias ou indicadores nacionais do…
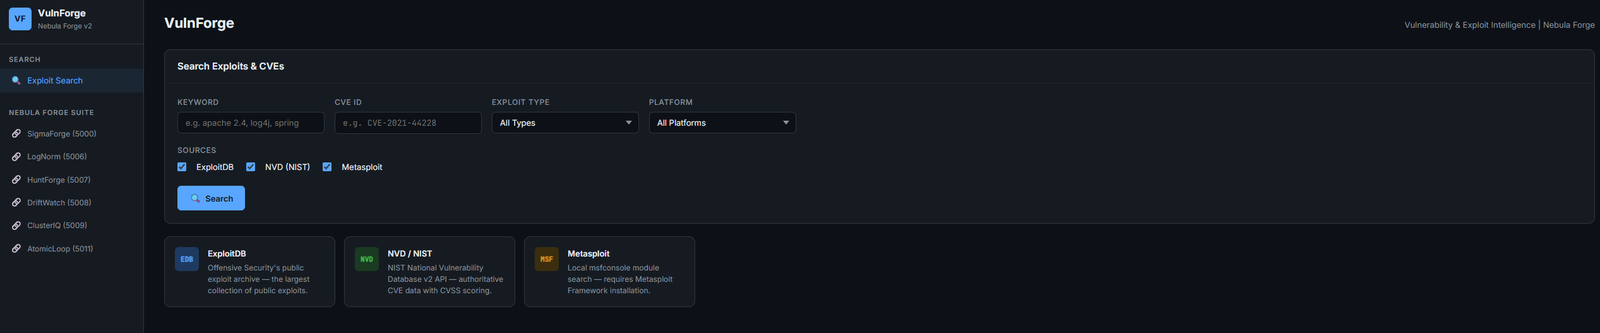 rootless-ghost/vulnforge
Vulnerability & exploit intelligence — ExploitDB, NVD, Metasploit search with CVE→ATT&CK mapping and LogNorm/HuntForge integration | Part of Nebula…
 xghst0/reconkg
Vulnerability triage with provenance. Resolves CVEs from locally built corpora (NVD/KEV/EPSS, ExploitDB, nmap script.db) and emits verification…
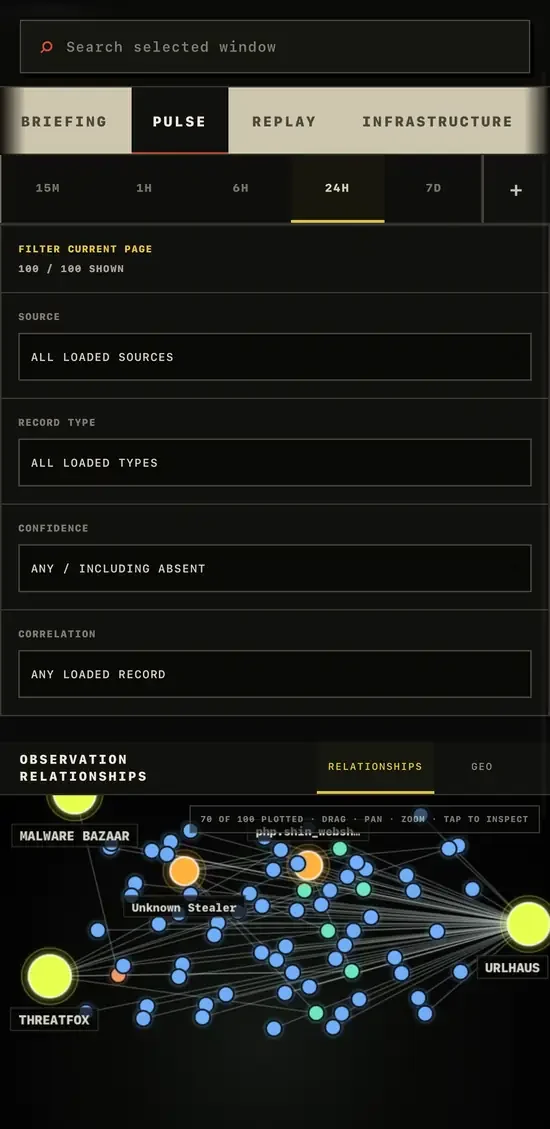
 gnomeman/badbanana-threat-observatory
Threat intel observatory aggregating CISA KEV, ThreatFox, URLhaus, and MalwareBazaar feeds with search, change tracking, and STIX/CSV/JSONL export.
 adham504/sentinelthread-forensics
High-speed Windows forensic triage platform that orchestrates the Hayabusa engine to transform raw EVTX logs into prioritized threat timelines with…

 montysecurity/c2-tracker
Live Feed of C2 servers, tools, and botnets
 danieleperera/onioningestor
An extendable tool to Collect, Crawl and Monitor onion sites on tor network and index collected information on Elasticsearch
 hslatman/awesome-threat-intelligence
Curated directory of threat intelligence sources, feeds, frameworks, tools, and research for SOC/CTI teams—covering IOCs, STIX/TAXII formats, and…
 doctorwebltd/malware-iocs
Curated Indicators of Compromise (IOCs) from Doctor Web malware investigations, published for threat intelligence, detection engineering, and…
 misp/misp-objects
Curated JSON object templates that define MISP attributes and relationship types for structured threat intelligence sharing and interoperable IOC…
 threatlabz/iocs
This repository is for Indicators of Compromise (IOCs) from Zscaler ThreatLabz public reports
 cross-samuel1/soc-analyst-hub
Free, offline SOC Analyst Hub for Tier 1 — IR checklists, alert triage playbooks, threat hunting queries & analyst onboarding. Single HTML file, no…
 renat0z3r0/notepadpp-supply-chain-iocs
IoCs and detection rules for the Notepad++ supply chain attack (CVE-2025-15556) — Lotus Blossom APT, June–December 2025. Includes Falcon LogScale…
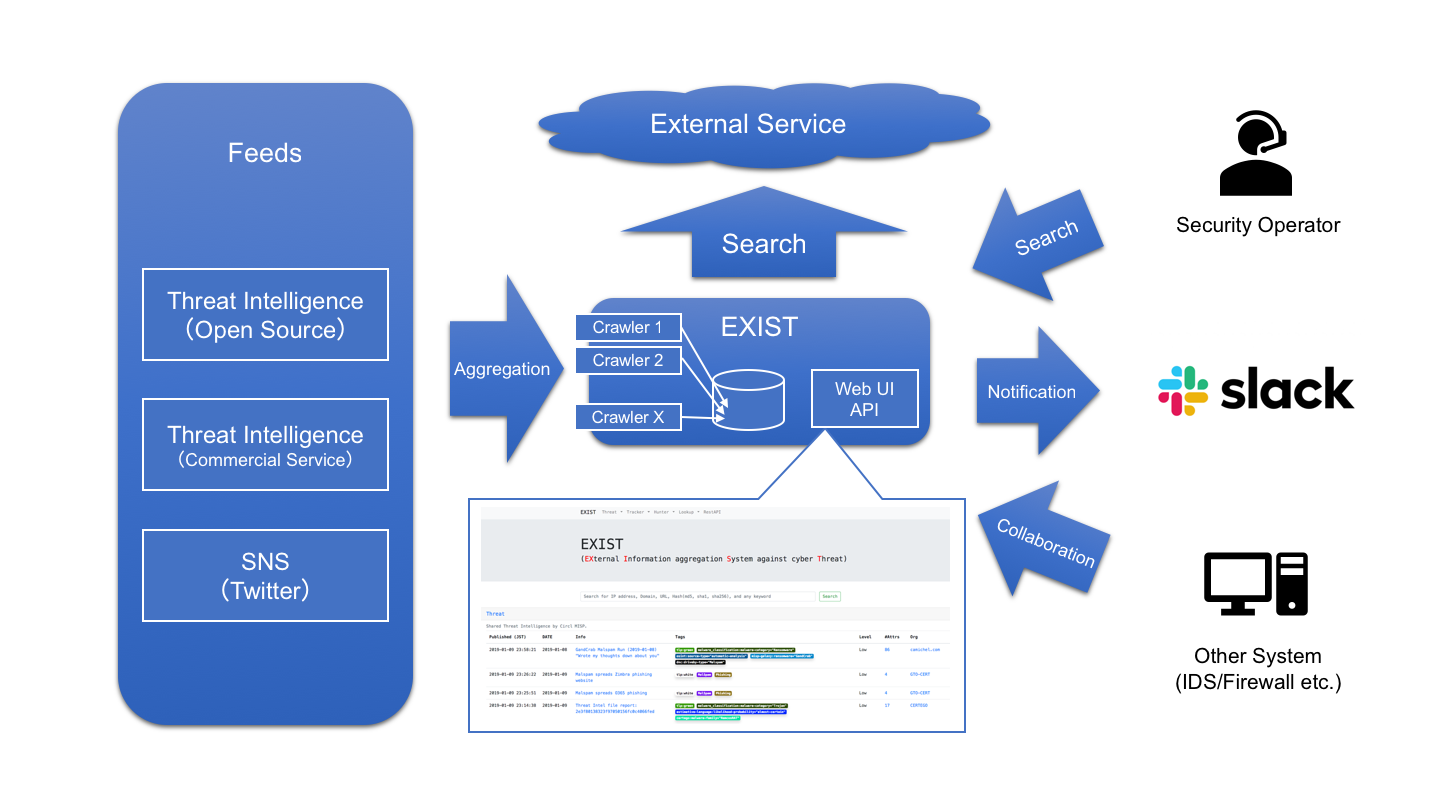 nict-csl/exist
EXIST is a web application for aggregating and analyzing cyber threat intelligence.
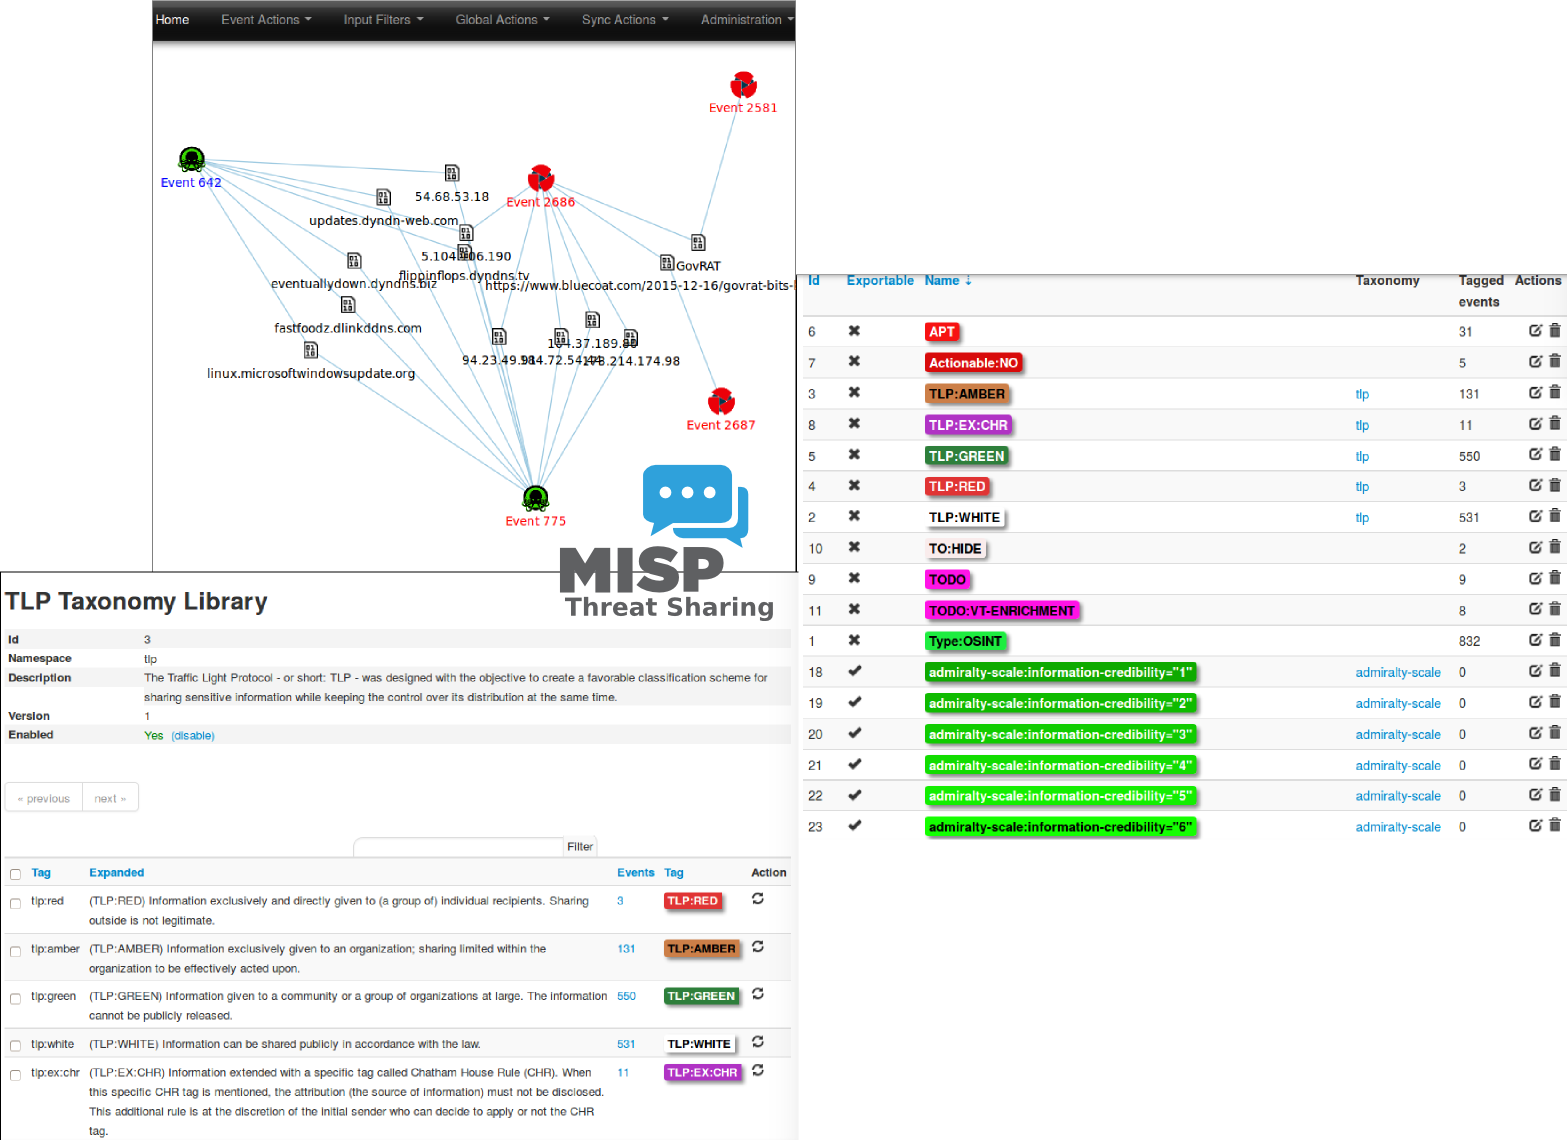 misp/misp
MISP (core software) - Open Source Threat Intelligence and Sharing Platform
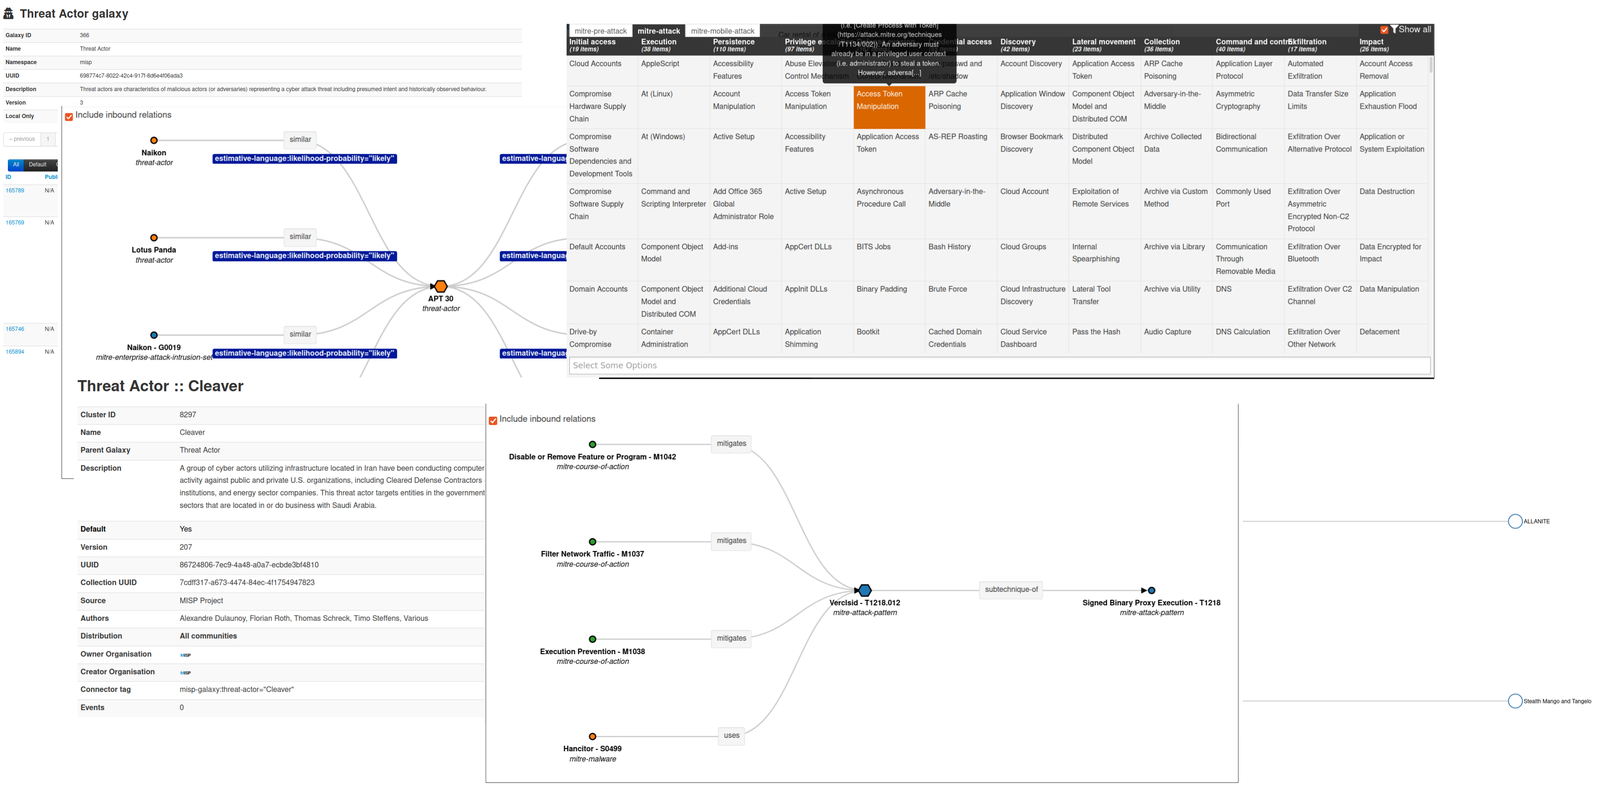 misp/misp-galaxy
Clusters and elements to attach to MISP events or attributes (like threat actors)
 misp/misp-taxonomies
Taxonomies used in MISP taxonomy system and can be used by other information sharing tool.