Archived
exist
 nict-csl/exist
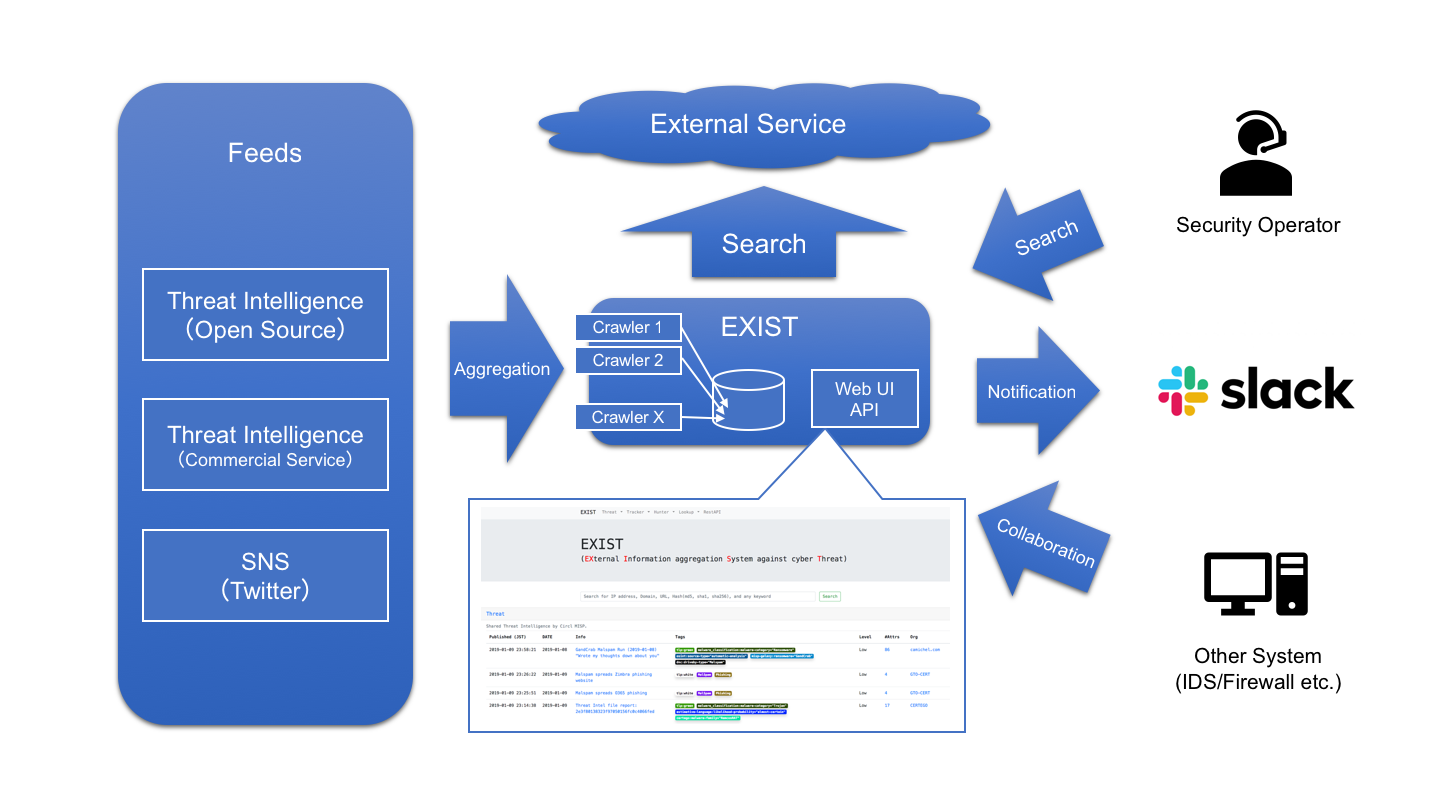
EXIST is a web application for aggregating and analyzing cyber threat intelligence.
educationincident-responseinformation-gathering+6
152
 montysecurity/c2-tracker
Live Feed of C2 servers, tools, and botnets
 grapl-security/grapl
Graph platform for Detection and Response
 hurricanelabs/machinae
Automated security intelligence collector that queries public feeds and APIs for threat data on IPs, domains, URLs, hashes, and SSL fingerprints,…
 pedramamini/threatingestor
Automated threat intelligence aggregation tool that extracts and normalizes indicators from multiple sources (OSINT feeds, malware reports) into a…
 vxunderground/threatintelligencediscordbot
Gets updates from various clearnet domains and ransomware threat actor domains
 emergingthreats/threatresearch
Proofpoint - Emerging Threats - Threat Research tools + publicly shared intel and documentation
 inquest/threatkb
Knowledge base workflow management for YARA rules and C2 artifacts (IP, DNS, SSL) (ALPHA STATE AT THE MOMENT)
 cred-club/artif
An advanced real time threat intelligence framework to identify threats and malicious web traffic on the basis of IP reputation and historical data.
 expel-io/expel-intel
This is the home of the Expel Intel Team. Here, we will share IOCs and other information that is either not suitable for fitting into other mediums…
 guardicode/cve-2021-44228_iocs
Curated collection of public Indicators of Compromise (IoCs) for the Log4j vulnerability (CVE-2021-44228), aggregated from multiple sources for…
 ciscocsirt/gosint
The GOSINT framework is a project used for collecting, processing, and exporting high quality indicators of compromise (IOCs).
 jivoi/awesome-osint
😱 A curated list of amazingly awesome OSINT

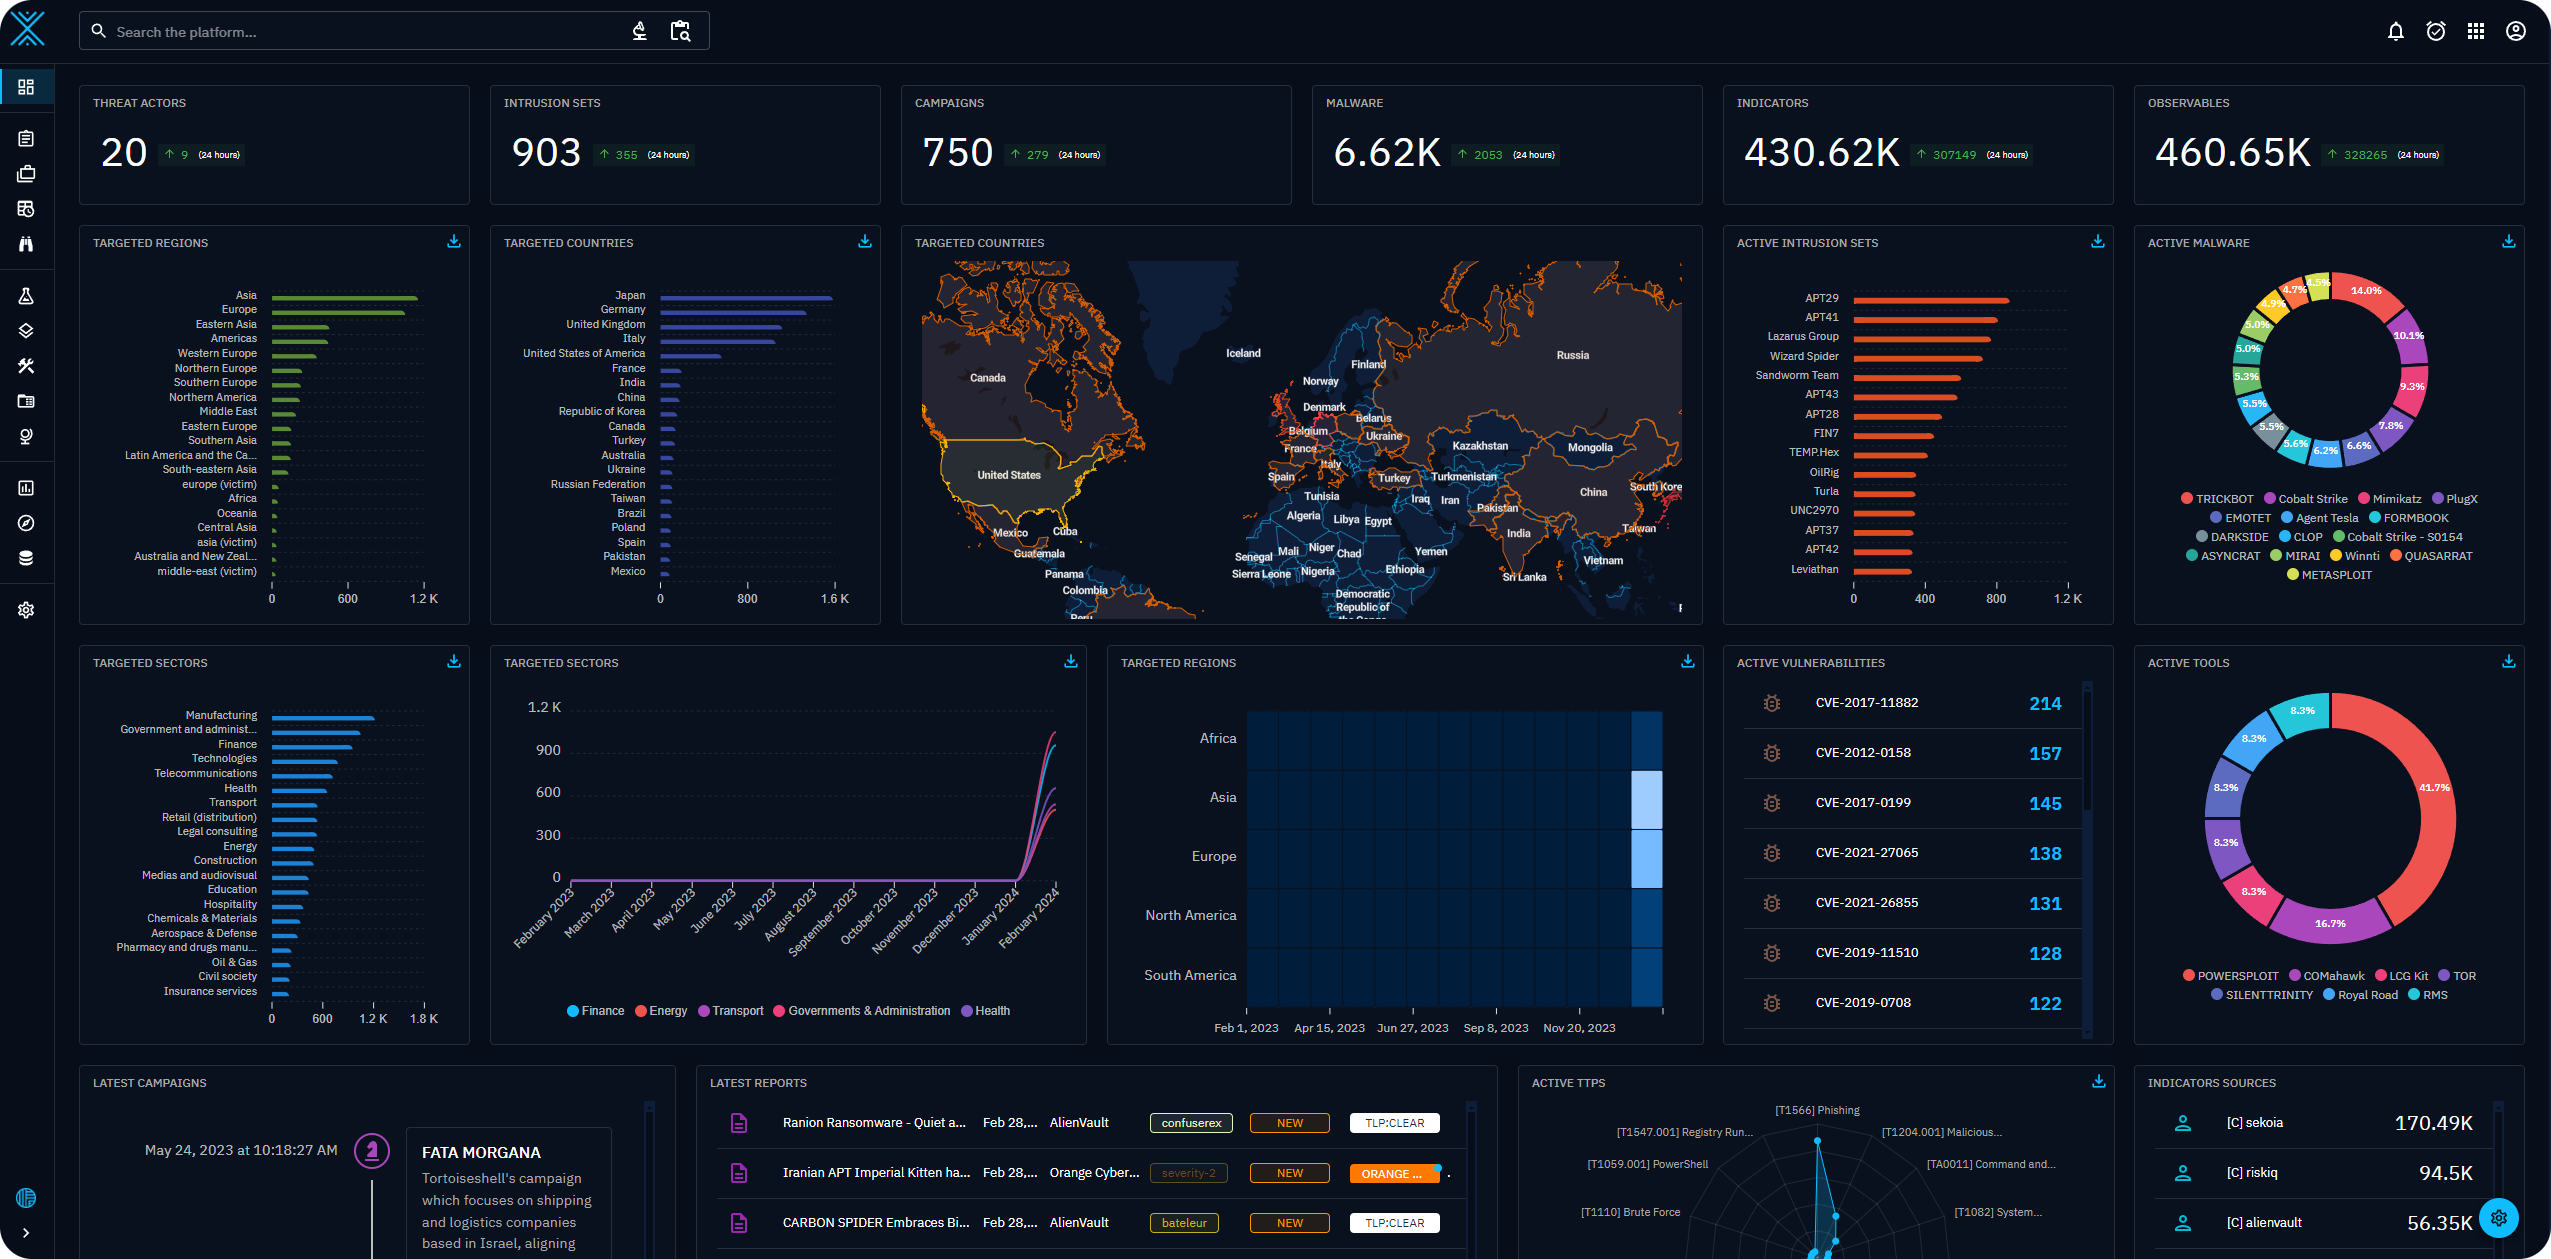 opencti-platform/opencti
Open Cyber Threat Intelligence Platform
 bushidouk/ransomware-tool-matrix
A resource containing all the tools each ransomware gangs uses