
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
112 results
machinae preview

machinae

GitHubhurricanelabs/machinae

Automated security intelligence collector that queries public feeds and APIs for threat data on IPs, domains, URLs, hashes, and SSL fingerprints,…
information-gatheringosintthreat-feeds-aggregators+1
537
3 months ago
pulledpork preview

pulledpork

GitHubshirkdog/pulledpork

Pulled Pork for Snort and Suricata rule management (from Google code)
configuration-auditingintrusion-detectionnetwork-security+2
4405 years ago
quantum-security-project preview

quantum-security-project

GitHubowasp/quantum-security-project

Vendor-neutral OWASP project mapping quantum-era security risks with a Top 10 risk list, mitigation guidance, and threat models for post-quantum…

cloud-securitycryptographycurated-resources+8
11420 days ago
Adama preview

Adama

GitHubrandomuserid/adama

Searches For Threat Hunting and Security Analytics

incident-responselog-analysisthreat-feeds-aggregators+1
2371 year ago
Sandbox_Scryer preview

Sandbox_Scryer

GitHubpayloadsecurity/sandbox_scryer

Parses public sandbox detonation reports to produce threat hunting intelligence, organizes findings via MITRE ATT&CK, assembles IOCs, and generates…

dynamic-analysis-sandboxingeducationinformation-gathering+6
2284 years ago
wiz-research-iocs preview

wiz-research-iocs

GitHubwiz-sec-public/wiz-research-iocs

Curated public database of indicators of compromise aggregated by Wiz Research for threat detection, hunting, and incident response workflows.
incident-responseioc-managementthreat-feeds-aggregators+1
1111 month ago
ThreatKB preview

ThreatKB

GitHubinquest/threatkb

Knowledge base workflow management for YARA rules and C2 artifacts (IP, DNS, SSL) (ALPHA STATE AT THE MOMENT)

information-gatheringioc-managementmalware-analysis+2
1046 months ago
libtaxii preview

libtaxii

GitHubtaxiiproject/libtaxii

A Python library for handling TAXII Messages invoking TAXII Services.

ioc-managementthreat-feeds-aggregatorsthreat-intelligence+1
745 months ago
loboguara preview

loboguara

GitHubolivsec/loboguara

Cyber threat intelligence platform for SSL certificate discovery, domain/URL scanning, data leak monitoring, tracking link generation, and threat…
data-exfiltrationdns-subdomain-enumerationinformation-gathering+6
731 year ago
Crawlector preview

Crawlector

GitHubmfmokbel/crawlector

Crawlector is a threat hunting framework designed for scanning websites for malicious objects.

crawlerinformation-gatheringmalware-analysis+5
1239 months ago
The Quantum Ad-List preview

The Quantum Ad-List

GitLabthe_quantum_alpha/the-quantum-ad-list

AI-curated blocklist of 3,000,000+ domains for blocking ads, trackers, malware, and cryptojacking. Integrates with hosts files, Pi-hole, and browser…

dns-analysismachine-learningprivacy+1
871 month ago
ThreatLens preview

ThreatLens

GitHubabdaullahag/threatlens

Python CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…
defensive-toolsincident-responseinformation-gathering+7
259 days ago
phishcollector preview

phishcollector

GitHubolizimmermann/phishcollector

PhishCollector is a research framework for collecting, analysing, and tracking phishing sites.
crawlereducationinformation-gathering+8
237 months ago
drovorub-hunt preview

drovorub-hunt

GitHubinsane-forensics/drovorub-hunt

A tool to assist with network-based hunting for GRU's Drovorub malware c2
incident-responseintrusion-detectionmalware-analysis+3
256 years ago
expel-intel preview

expel-intel

GitHubexpel-io/expel-intel

This is the home of the Expel Intel Team. Here, we will share IOCs and other information that is either not suitable for fitting into other mediums…
information-gatheringioc-managementosint+2
61 month ago
darkgrid preview

darkgrid

GitHubkaal22/darkgrid

3D threat intelligence dashboard that visualizes malicious infrastructure from OSINT sources like AbuseIPDB and OpenPhish, with a live threat feed,…
dns-analysisinformation-gatheringnetwork-security+4
136 months ago
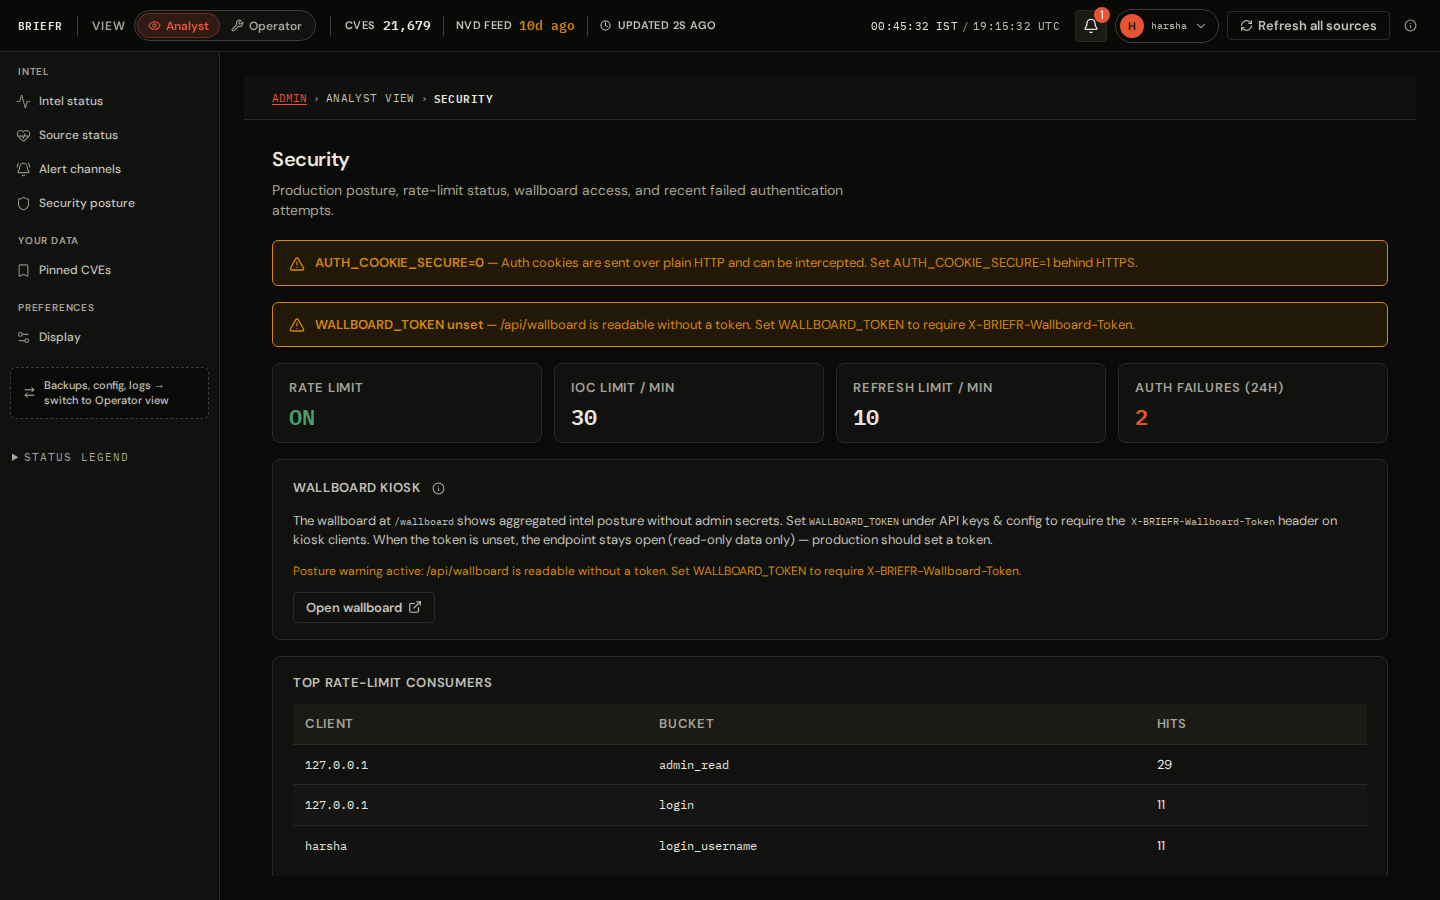
briefr preview

briefr

GitHubsoldier0x0/briefr

Open Vulnerability Intelligence platform, aggregated intel in one dashboard, with correlation and IOC lookups, completely self hosted. All resources…
defensive-toolsioc-managementthreat-feeds-aggregators+2
35 days ago
gitlab-cve-2026-85706-ioc preview

gitlab-cve-2026-85706-ioc

GitHubjithinkrishnanrs/gitlab-cve-2026-85706-ioc

CVE-2026-85706 — GitLab Path Traversal IOC Scanner & Detection Toolkit. Detect and hunt for exploitation of the critical unauthenticated GitLab CE/EE…

defensive-toolsincident-responseinformation-gathering+8
114 days ago
Previous1234567Next
