
RansomLook
 ransomlook/ransomlook
Yet another Ransomware gang tracker
crawlerdefensive-toolsinformation-gathering+3
ransomlook/ransomlookYet another Ransomware gang tracker
 mthcht/awesome-lists
Curated repository of threat intelligence feeds, IoC lists, YARA rules, and DFIR tool references for SOC/CERT/CTI detection and incident response.
 functori/argos/argos
Analysis and Representation of Graphs of Suspicious Operations (Analyse et Représentation des Graphes des Opérations Suspectes)
 criticalpathsecurity/zeek-intelligence-feeds
Aggregated Zeek-format threat intelligence feeds with combined indicators from public and curated sources for continuous IDS and network threat…
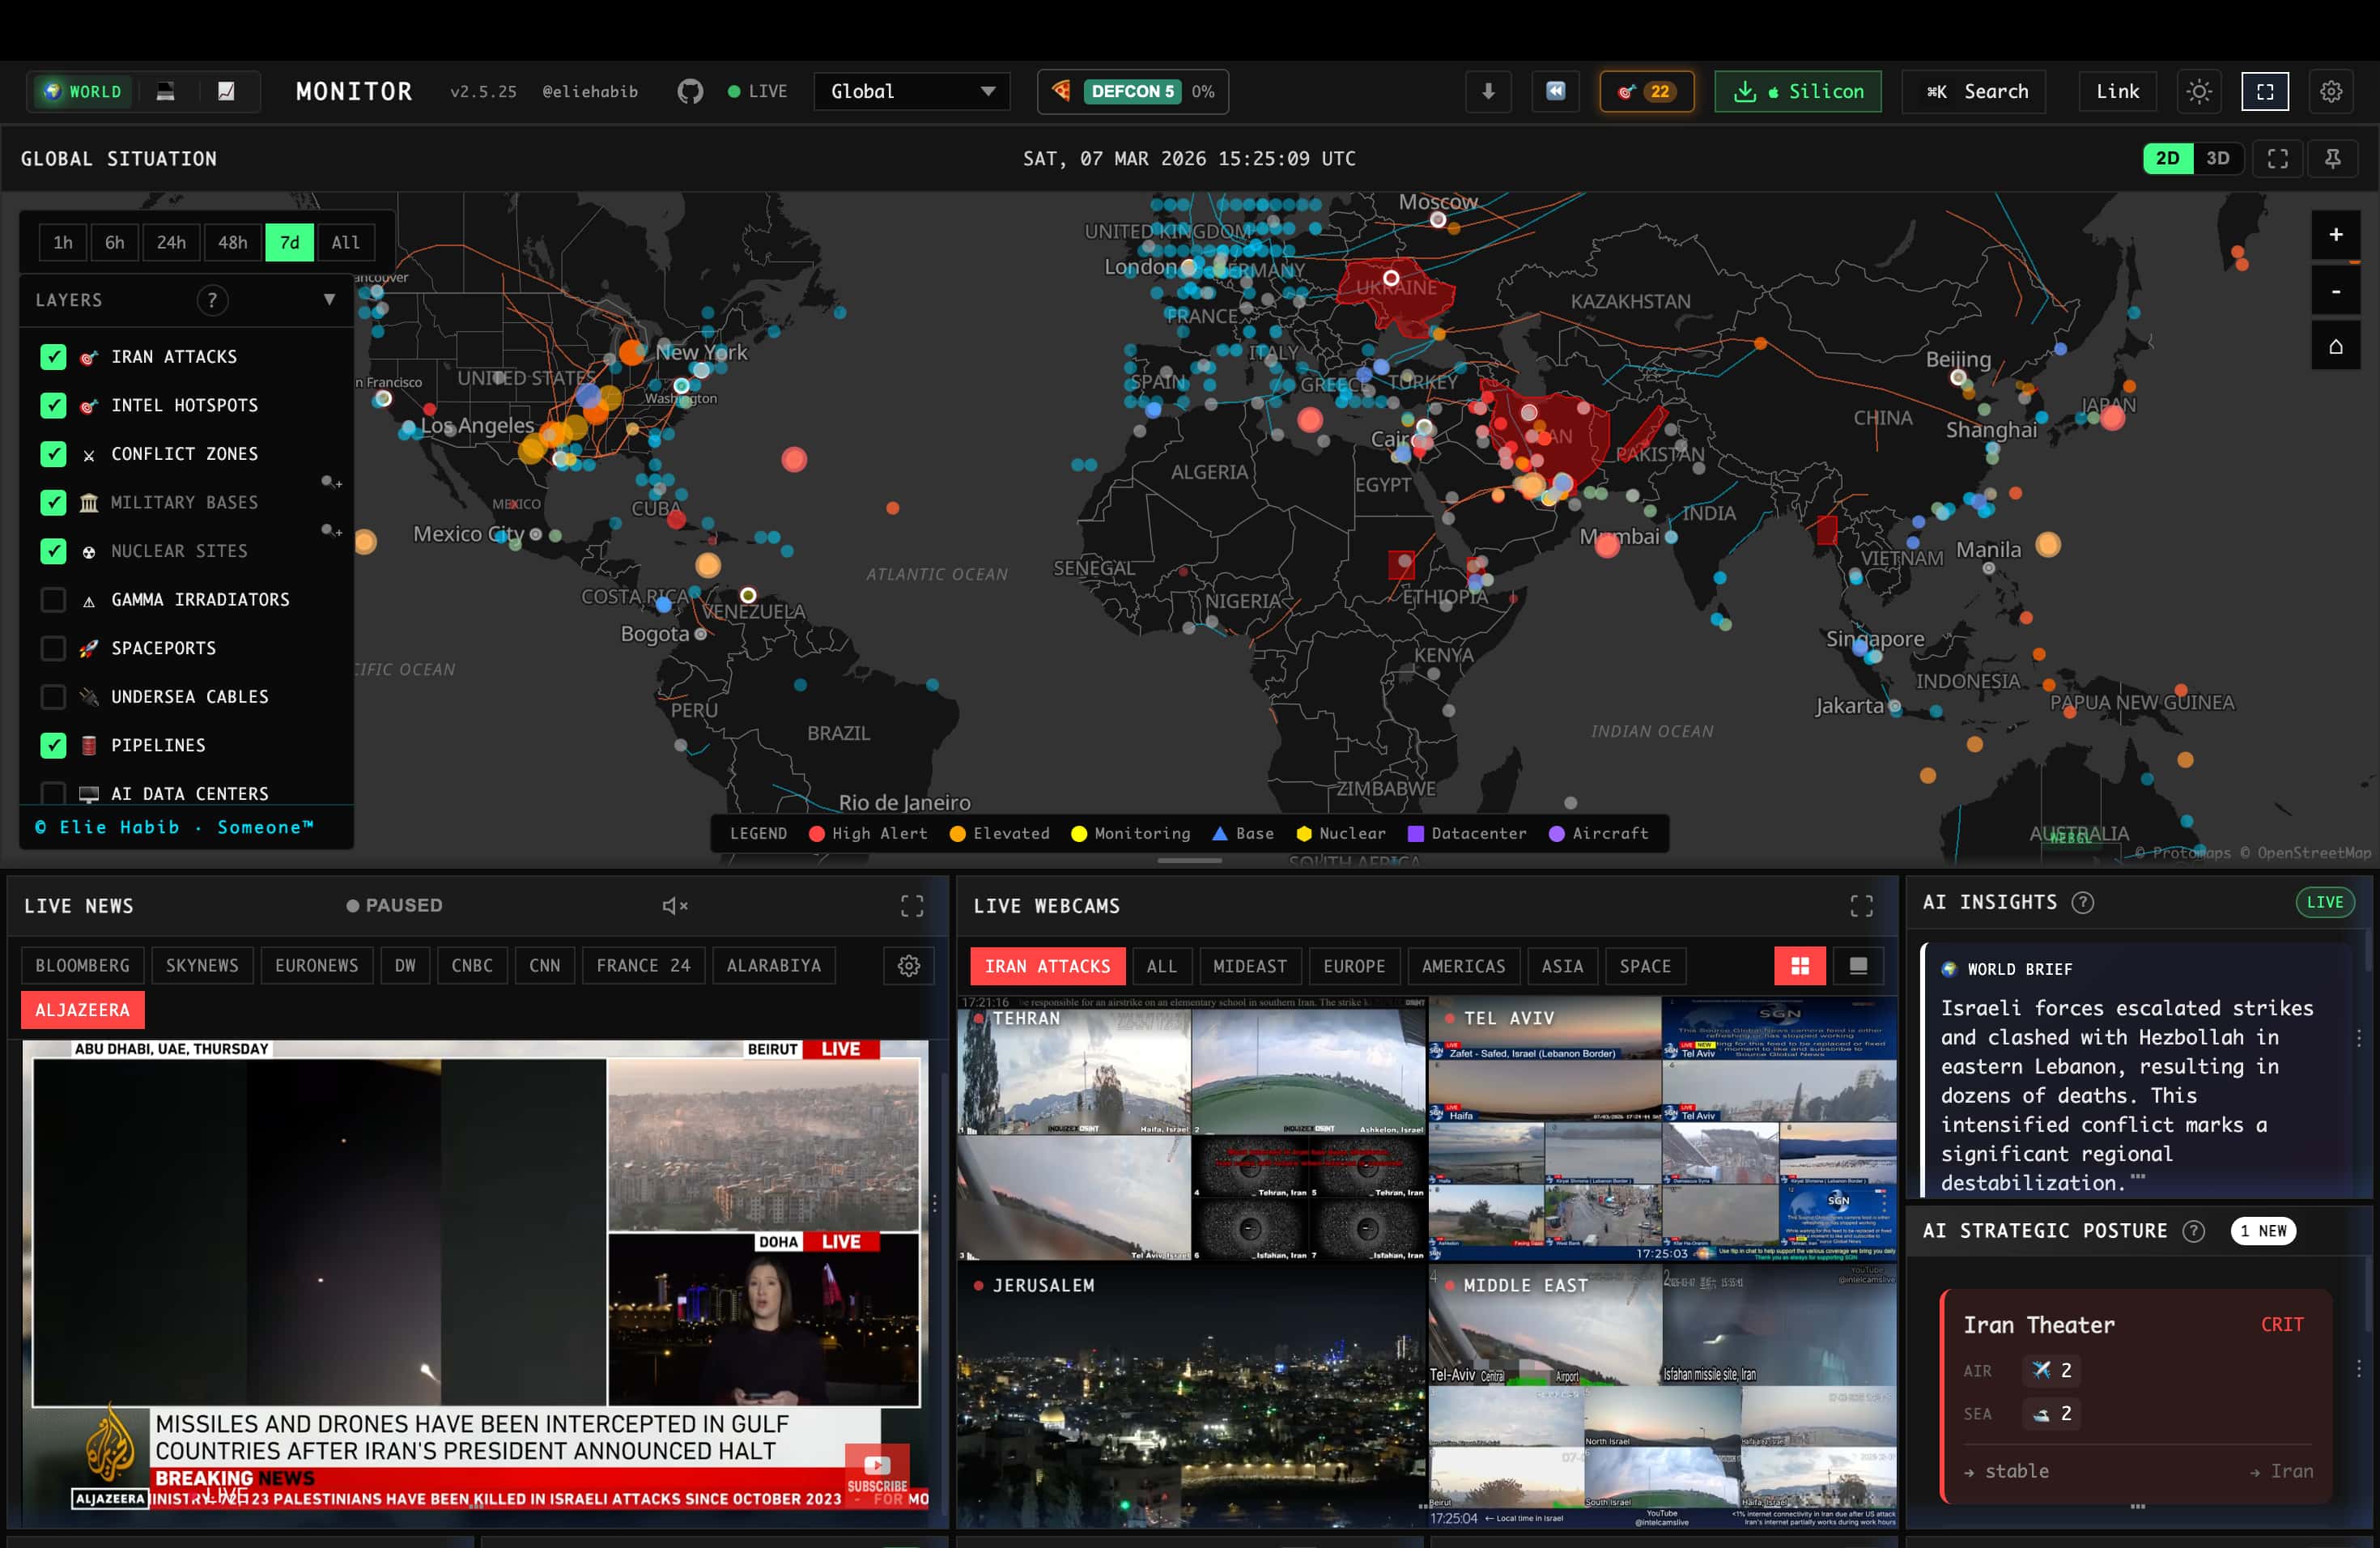 koala73/worldmonitor
Real-time global intelligence dashboard. AI-powered news aggregation, geopolitical monitoring, and infrastructure tracking in a unified situational…
 neo23x0/signature-base
YARA signature and IOC database for my scanners and tools
 essexrich/threatactors-ttps
Repository created to share information about tactics, techniques and procedures used by threat actors. Initially with ransomware groups and evolving…
 duggytuxy/data-shield_ipv4_blocklist
Curated IPv4 blocklist of malicious addresses, refreshed every 6 hours for firewall and WAF ingestion, with split lists and CTI-ready formats for…
 jivoi/awesome-osint
😱 A curated list of amazingly awesome OSINT
 securewithumer/exploit-index
Zero-API aggregator indexing 150k+ CVE exploits and PoCs from Exploit-DB, Nuclei, Metasploit, and CISA KEV, with EPSS/CVSS risk scoring for threat…
 cisagov/vulnrichment
A repo to conduct vulnerability enrichment.
 facebook/threatexchange
Trust & Safety tools for working together to fight digital harms.
 bert-janp/open-source-threat-intel-feeds
This repository contains Open Source freely usable Threat Intel feeds that can be used without additional requirements. Contains multiple types such…
 opencti-platform/opencti
Open Cyber Threat Intelligence Platform
 cisagov/kev-data
Mirrors CISA's Known Exploited Vulnerabilities (KEV) catalog as CSV and JSON with a JSON schema, enabling programmatic access and commit-history…
 toborrm9/malicious_extension_sentry
Malicious Extension Database
 misp/misp-galaxy
Clusters and elements to attach to MISP events or attributes (like threat actors)