
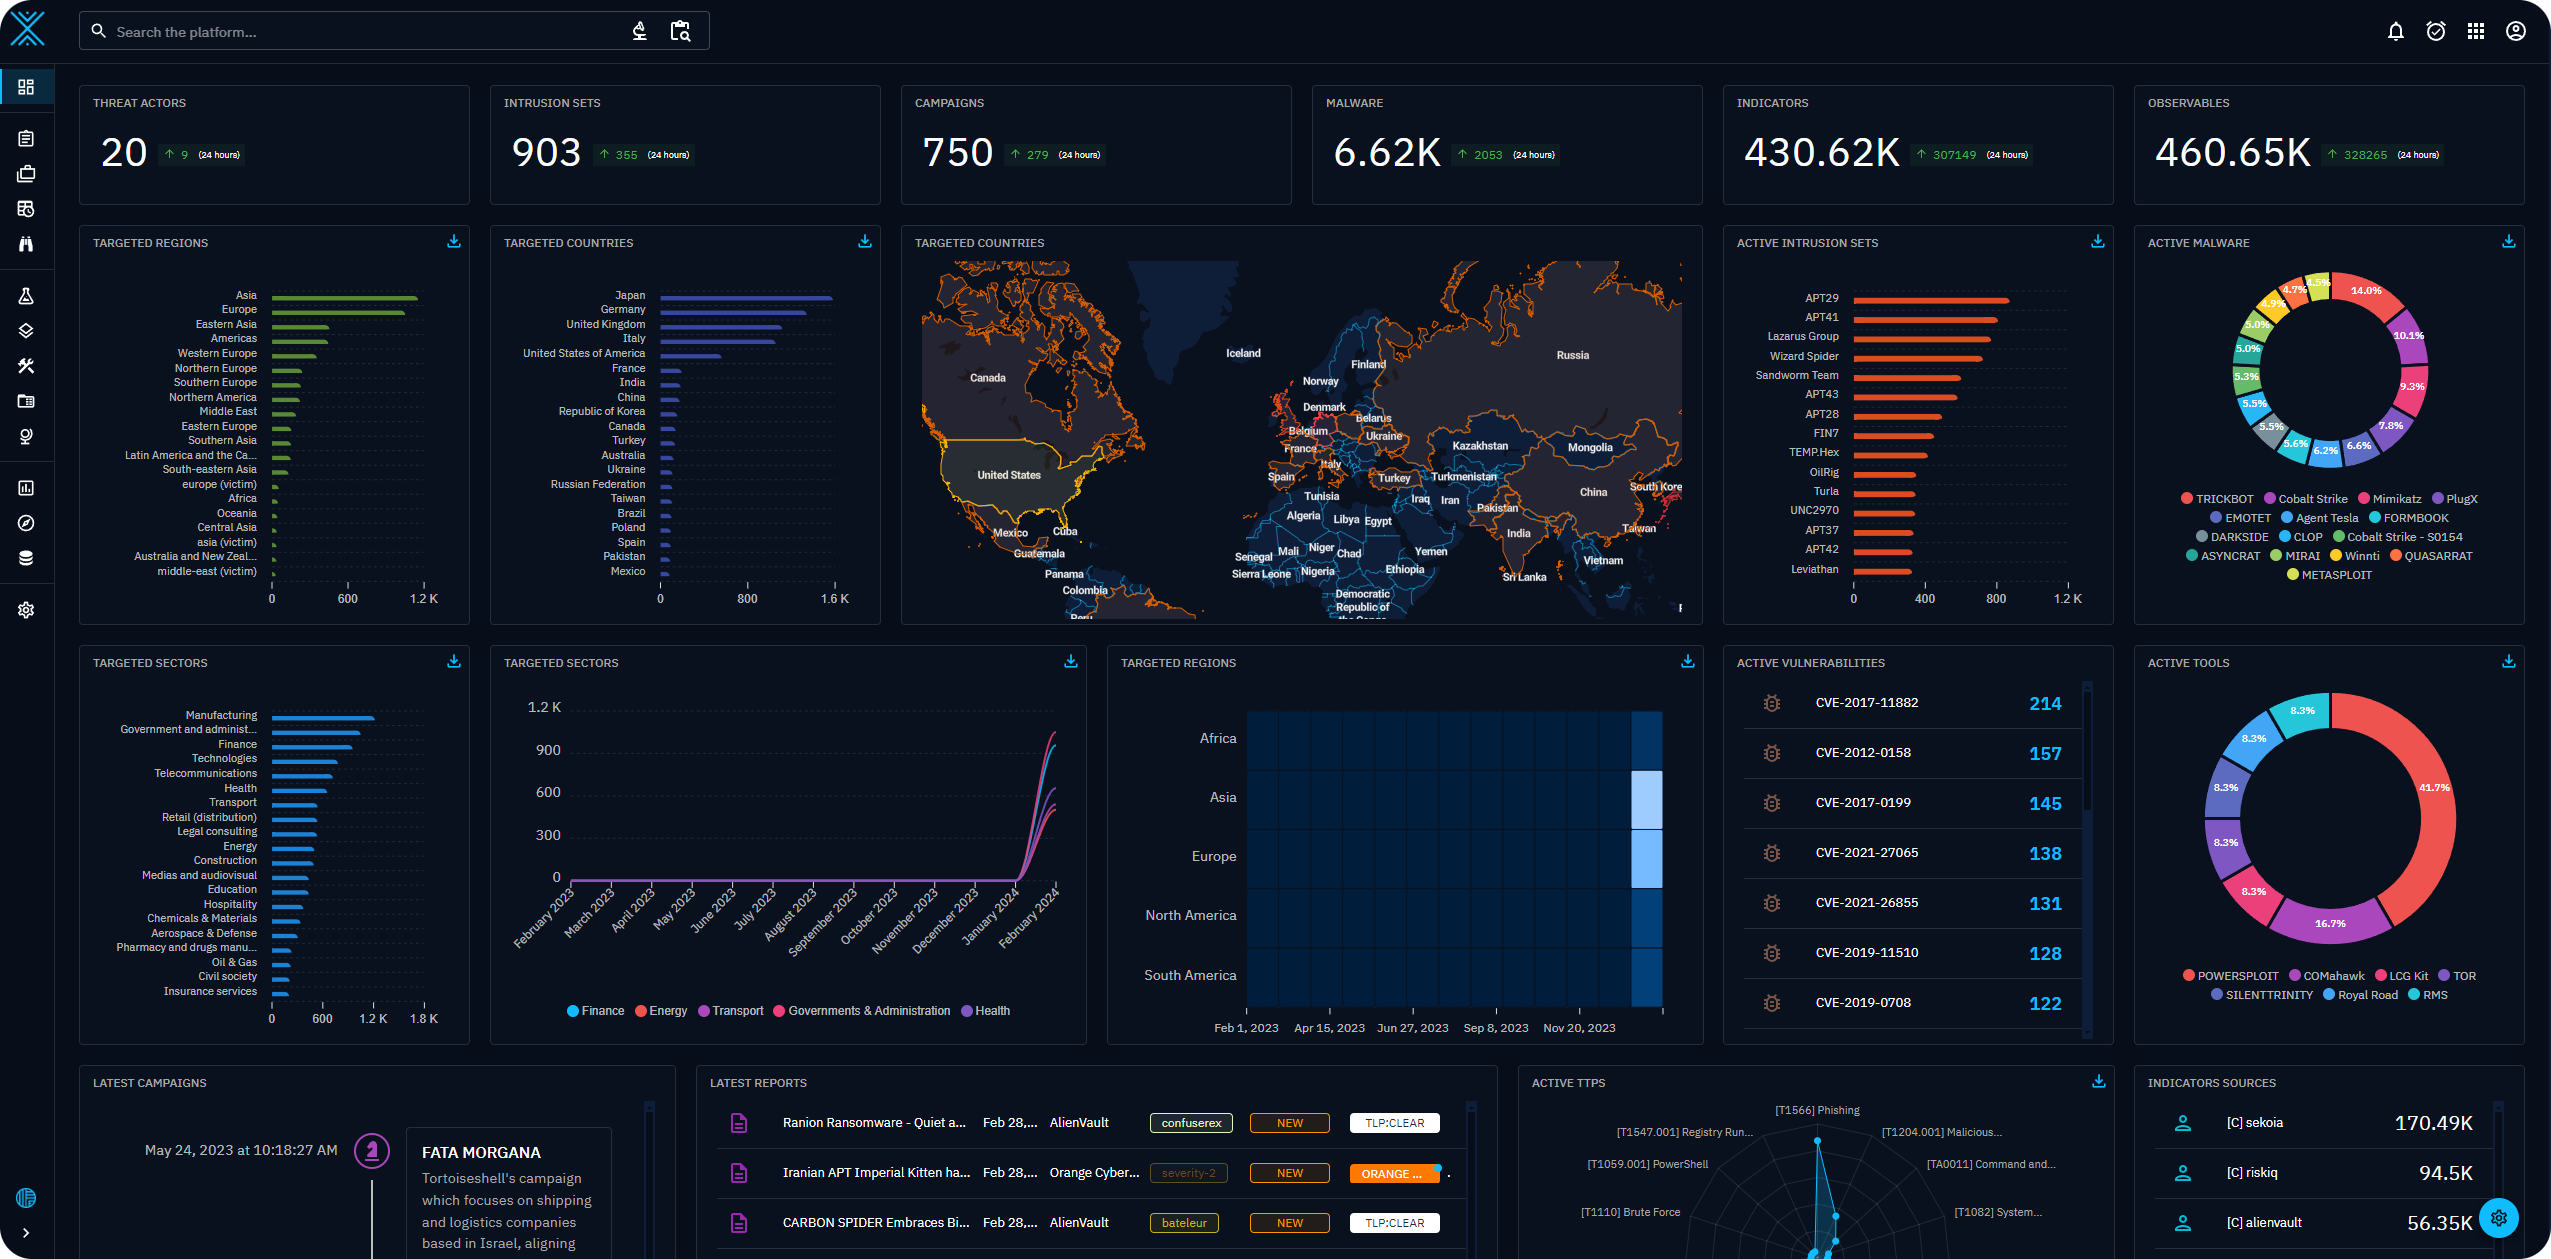
opencti
 opencti-platform/opencti
Open Cyber Threat Intelligence Platform
curated-resourceseducationemail-security+6
opencti-platform/openctiOpen Cyber Threat Intelligence Platform
 toborrm9/malicious_extension_sentry
Malicious Extension Database
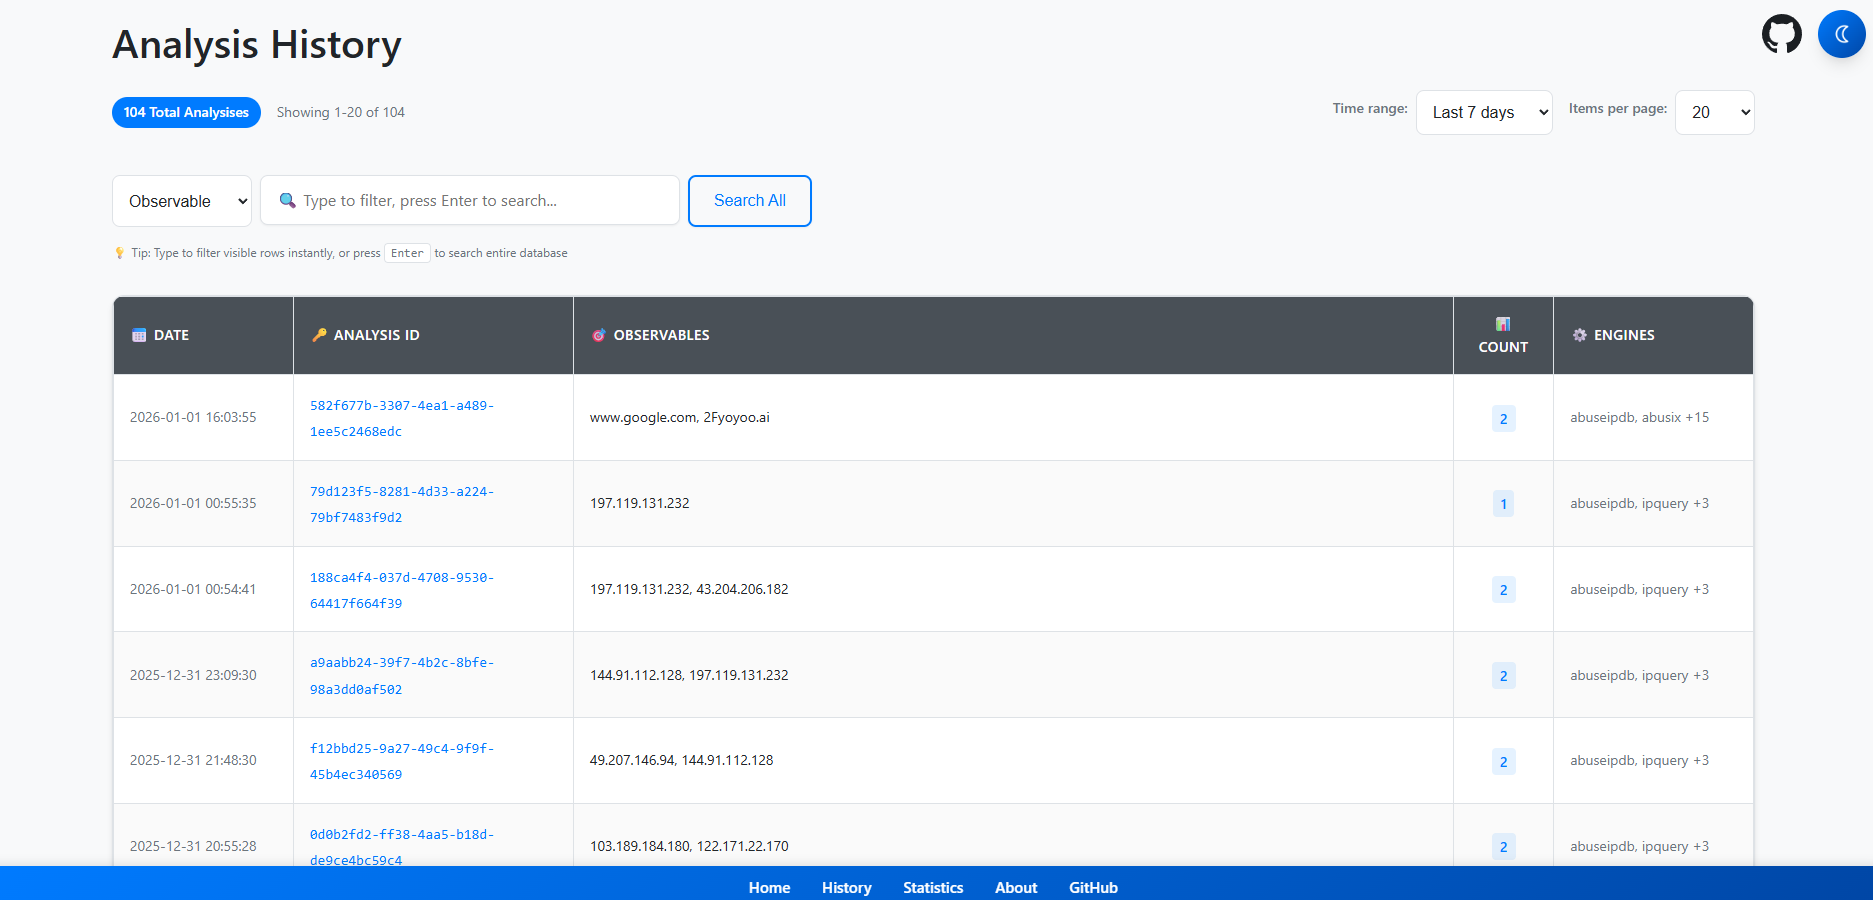 stanfrbd/cyberbro
A simple application that extracts your IoCs from garbage input and checks their reputation using multiple CTI services.
 mthcht/awesome-lists
Curated repository of threat intelligence feeds, IoC lists, YARA rules, and DFIR tool references for SOC/CERT/CTI detection and incident response.
 phishdestroy/destroylist
Real-time phishing & scam domain blocklist - 205k+ curated threats, 1M+ community, free API, multiple formats
 aquasecurity/vuln-list-debian
Debian Security Tracker
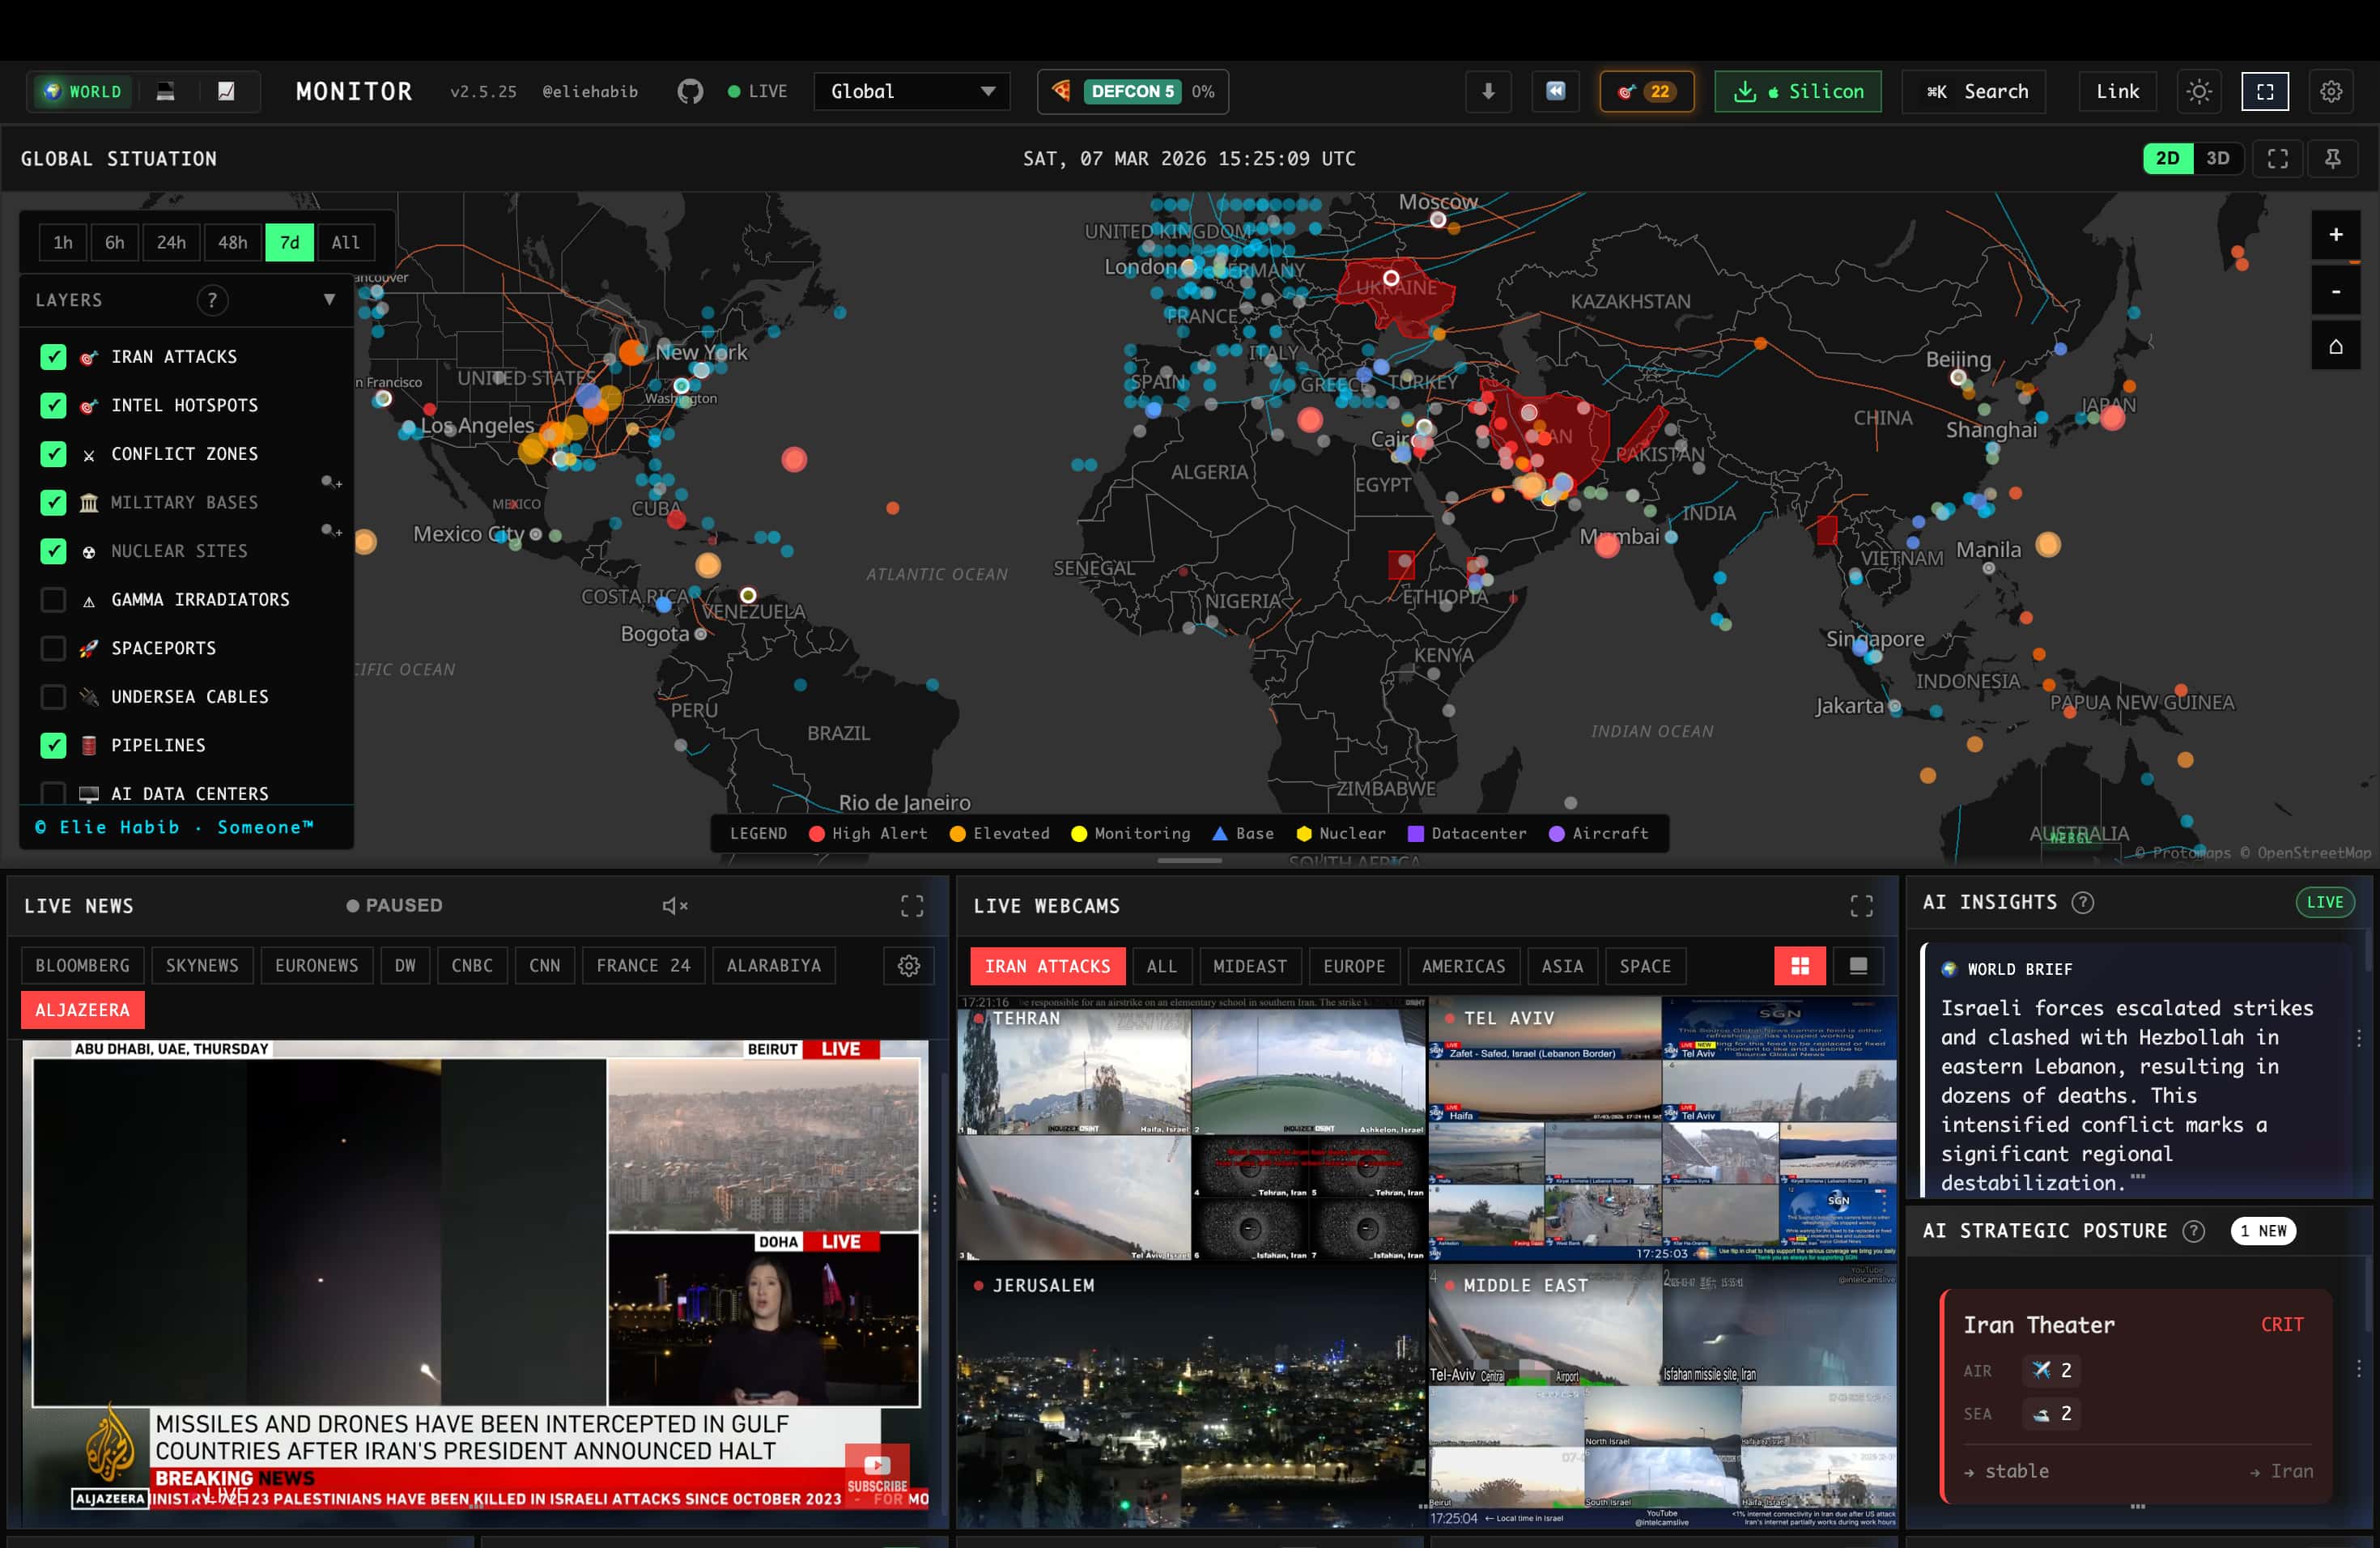 koala73/worldmonitor
Real-time global intelligence dashboard. AI-powered news aggregation, geopolitical monitoring, and infrastructure tracking in a unified situational…
 fastfire/deepdarkcti
Collection of Cyber Threat Intelligence sources from the deep and dark web
 essexrich/threatactors-ttps
Repository created to share information about tactics, techniques and procedures used by threat actors. Initially with ransomware groups and evolving…
 julioliraup/antiphishing
Advanced Phishing Protection: Suricata rulesets open and free
 paloaltonetworks/unit42-timely-threat-intel
A collection of files with indicators supporting social media posts from Palo Alto Network's Unit 42 team to disseminate timely threat intelligence.
 misp/misp-objects
Curated JSON object templates that define MISP attributes and relationship types for structured threat intelligence sharing and interoperable IOC…
 nomi-sec/nvd-database
📕NVD Database
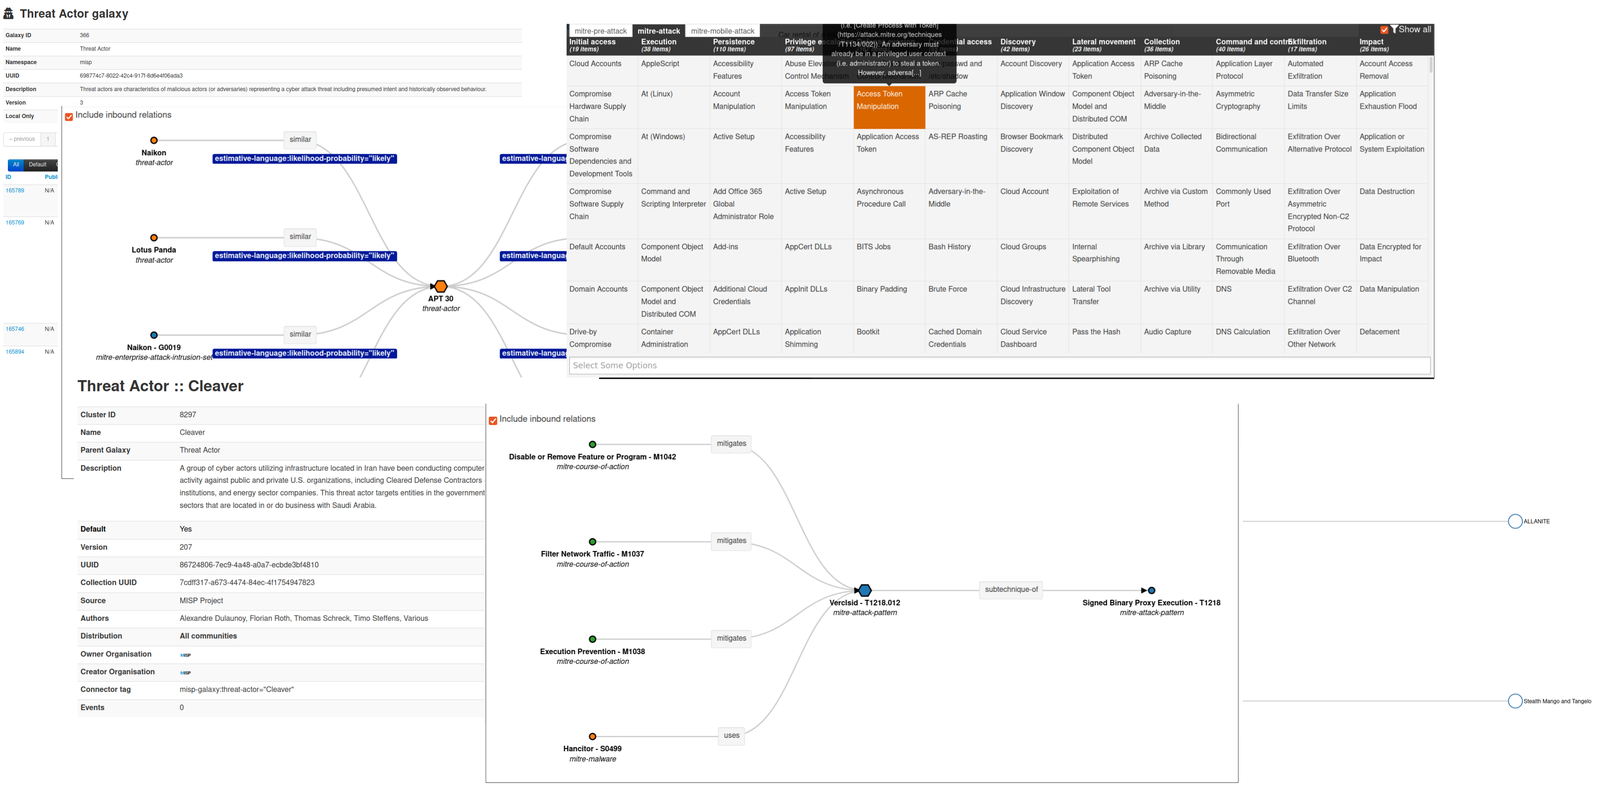 misp/misp-galaxy
Clusters and elements to attach to MISP events or attributes (like threat actors)

 functori/argos/argos
Analysis and Representation of Graphs of Suspicious Operations (Analyse et Représentation des Graphes des Opérations Suspectes)
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
 abdaullahag/threatlens
Python CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…
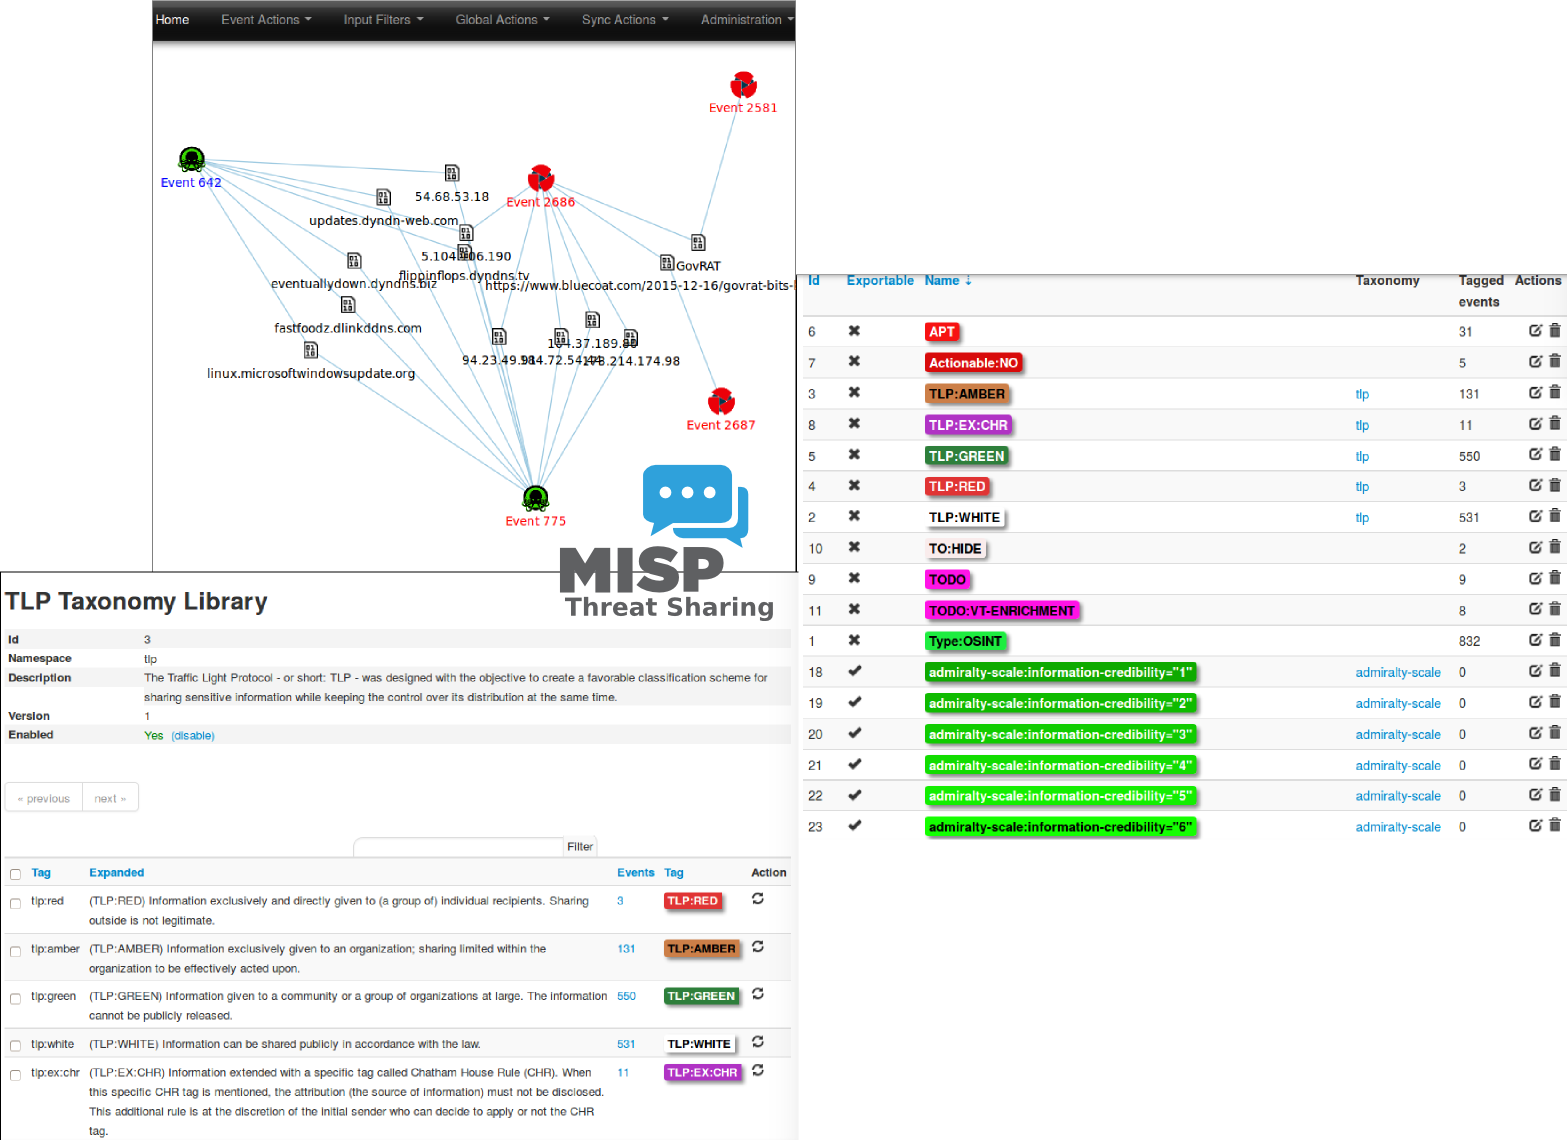 misp/misp
MISP (core software) - Open Source Threat Intelligence and Sharing Platform