

C2IntelFeeds
 drb-ra/c2intelfeeds
Automatically generated C2 threat intelligence feeds of IPs, domains, URL paths, and implant configuration metadata, derived from internet scanning…
command-and-controldefensive-toolsincident-response+6
746
drb-ra/c2intelfeedsAutomatically generated C2 threat intelligence feeds of IPs, domains, URL paths, and implant configuration metadata, derived from internet scanning…
 hurricanelabs/machinae
Automated security intelligence collector that queries public feeds and APIs for threat data on IPs, domains, URLs, hashes, and SSL fingerprints,…
 shirkdog/pulledpork
Pulled Pork for Snort and Suricata rule management (from Google code)
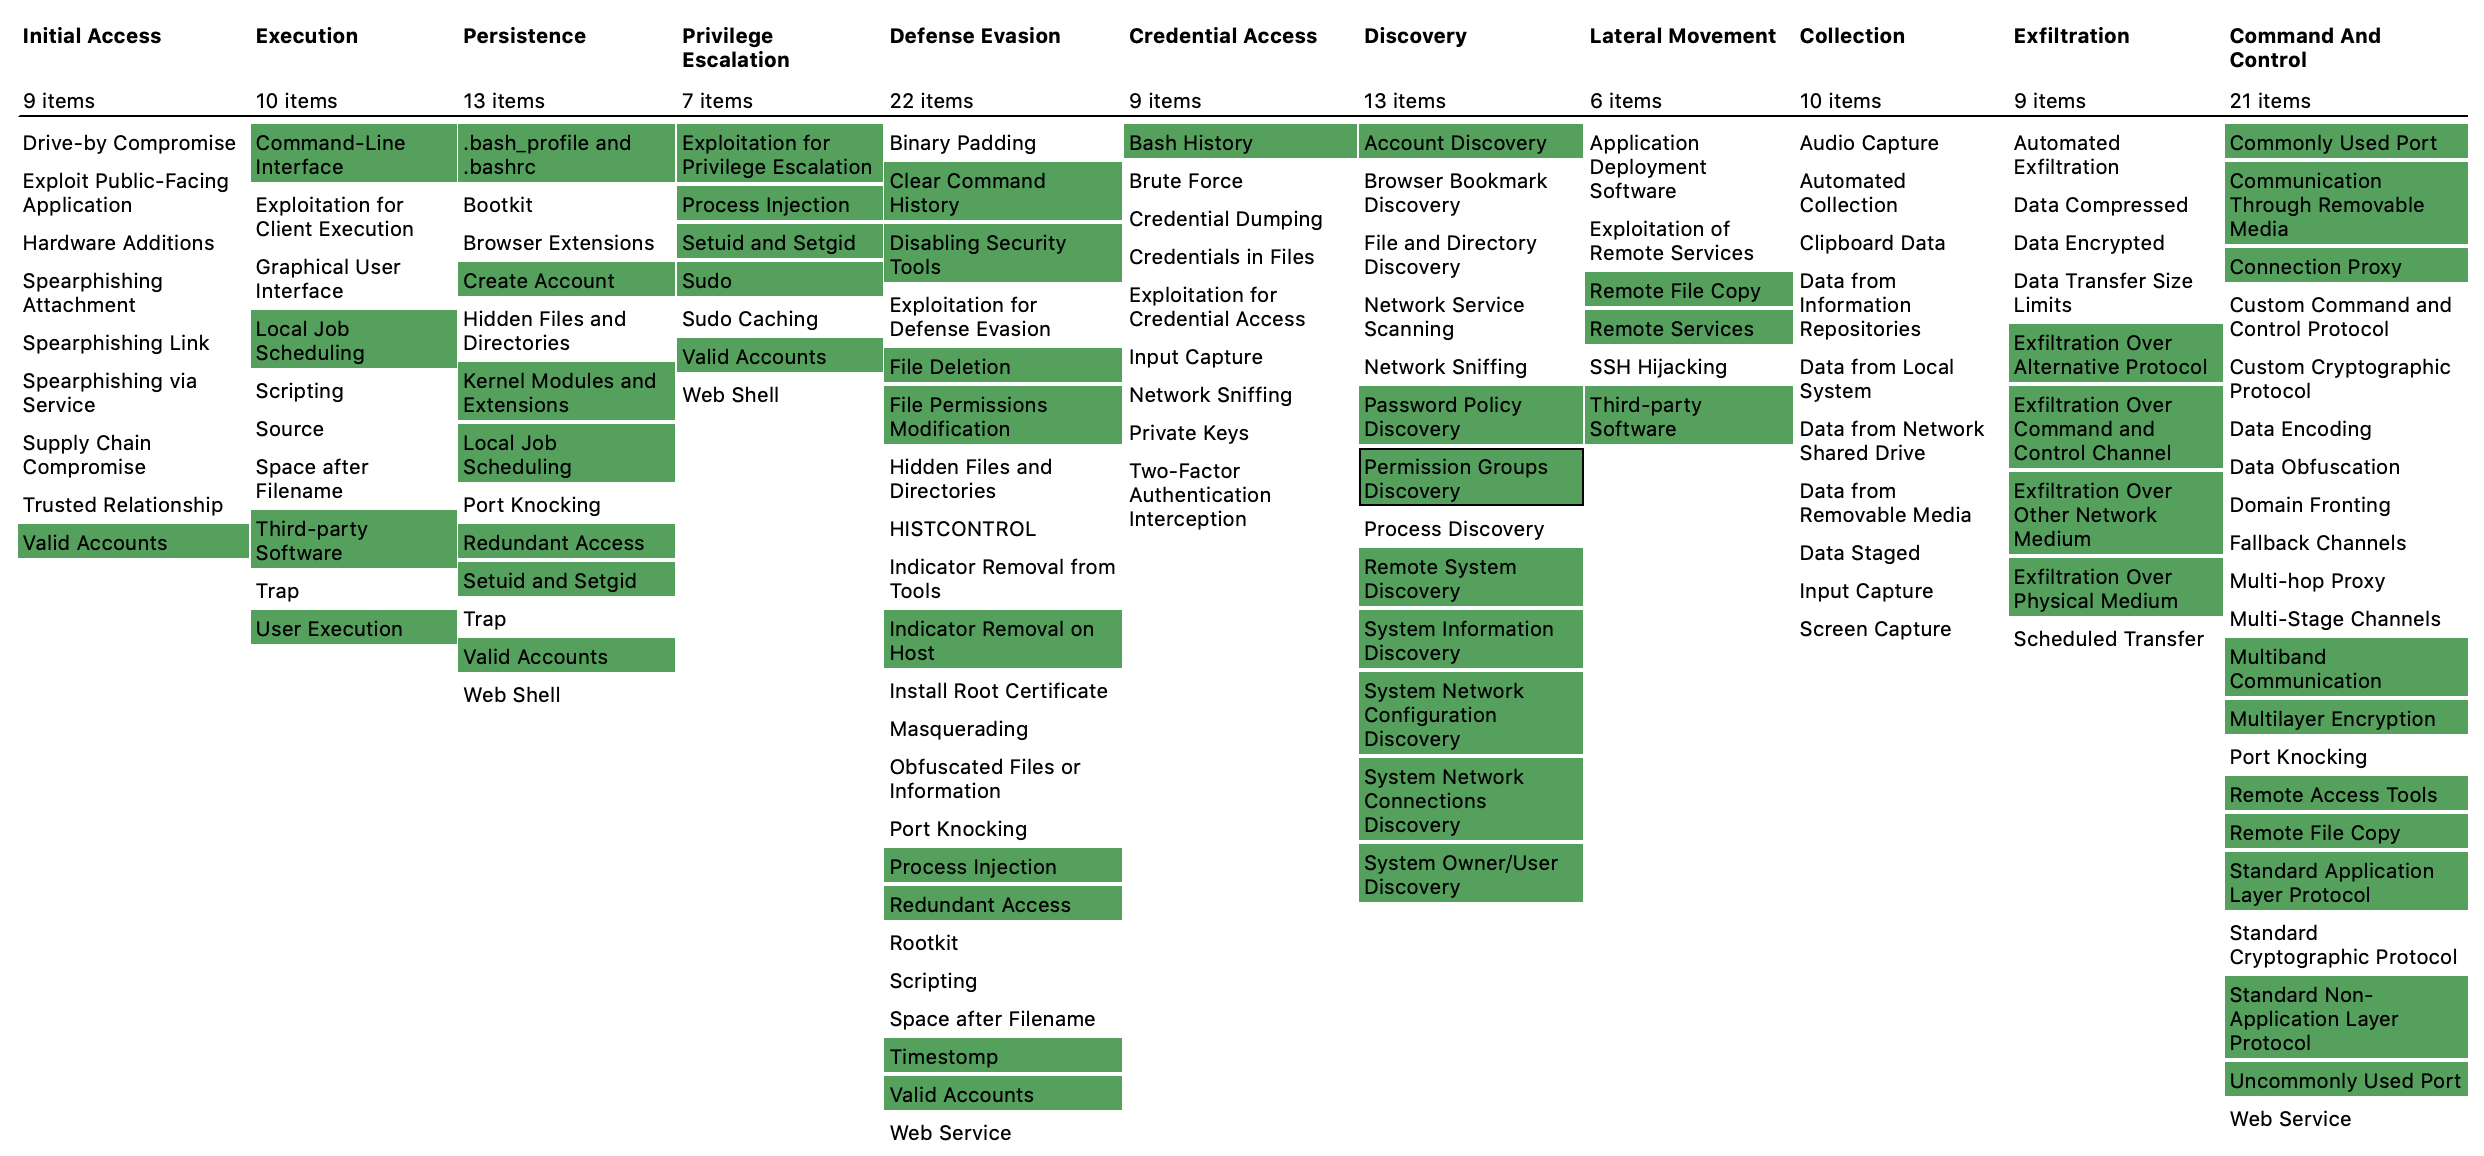 bfuzzy/auditd-attack
A Linux Auditd rule set mapped to MITRE's Attack Framework