
ti-a-ti-cveexploitchecker
 shadowguardai/ti-a-ti-cveexploitchecker
Determines if public exploits are available for a given CVE. Uses APIs like exploit-db or NVD to ide
incident-responseinformation-gatheringioc-management+5
shadowguardai/ti-a-ti-cveexploitcheckerDetermines if public exploits are available for a given CVE. Uses APIs like exploit-db or NVD to ide
 andreyglauzer/vigilantonion
🐍 - Crawler on tor network sites, searching for keywords.
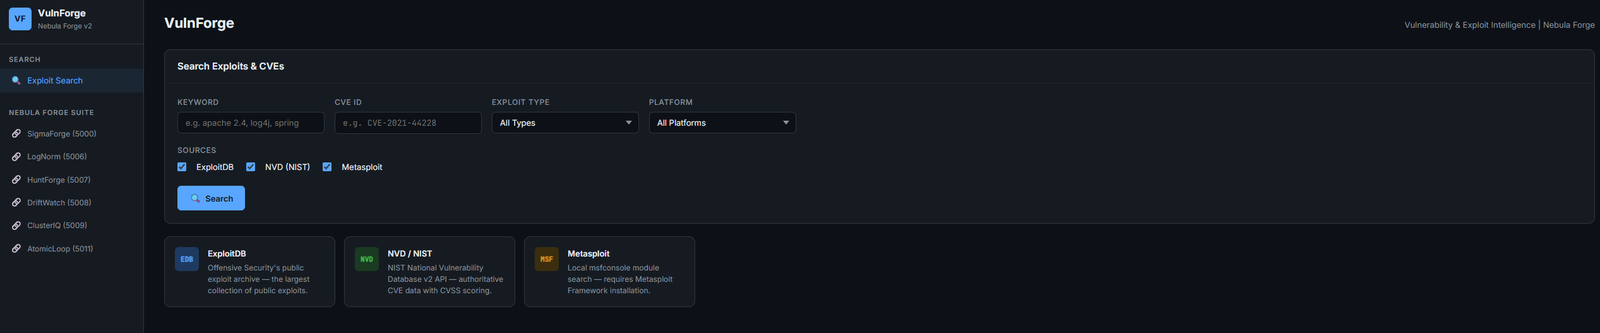 rootless-ghost/vulnforge
Vulnerability & exploit intelligence — ExploitDB, NVD, Metasploit search with CVE→ATT&CK mapping and LogNorm/HuntForge integration | Part of Nebula…
 simplifaisoul/osiris
Open Source Global Intelligence Platform - Real-Time OSINT Dashboard - A Palantir Alternative - …
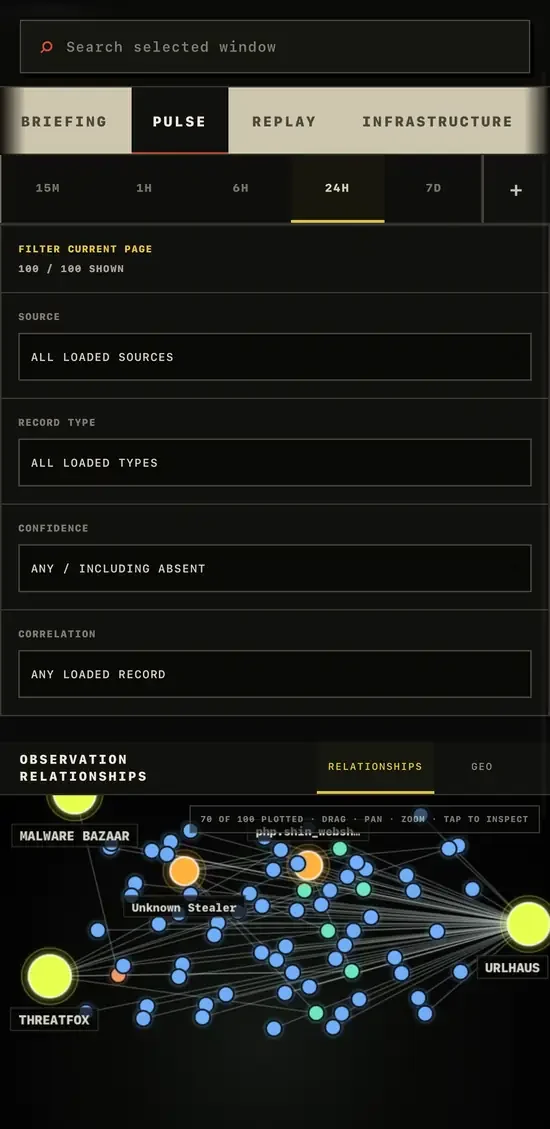
 gnomeman/badbanana-threat-observatory
Threat intel observatory aggregating CISA KEV, ThreatFox, URLhaus, and MalwareBazaar feeds with search, change tracking, and STIX/CSV/JSONL export.
 vxunderground/threatintelligencediscordbot
Gets updates from various clearnet domains and ransomware threat actor domains
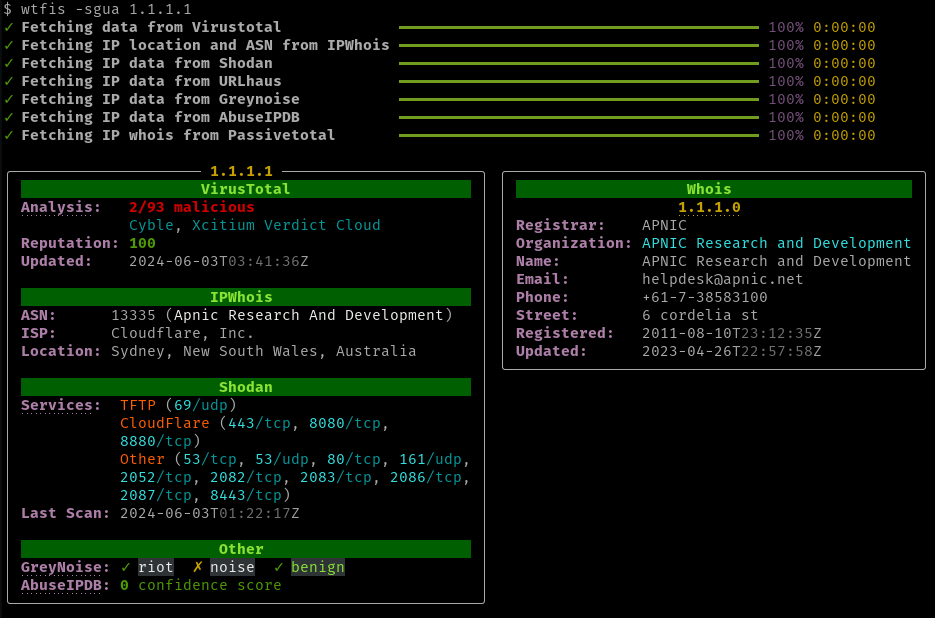 pirxthepilot/wtfis
Passive hostname, domain and IP lookup tool for non-robots
 rollwagen/abusech
CLI client for abuse.ch
 aquasecurity/vexhub-crawler
Collect VEX documents and update VEX Hub
 aquasecurity/secfixes-tracker
Forked from https://gitlab.alpinelinux.org/kaniini/secfixes-tracker
 aquasecurity/vuln-list-redhat
Red Hat security advisories
 emergingthreats/threatresearch
Proofpoint - Emerging Threats - Threat Research tools + publicly shared intel and documentation
 inquest/threatkb
Knowledge base workflow management for YARA rules and C2 artifacts (IP, DNS, SSL) (ALPHA STATE AT THE MOMENT)
 pedramamini/threatingestor
Automated threat intelligence aggregation tool that extracts and normalizes indicators from multiple sources (OSINT feeds, malware reports) into a…
 expel-io/expel-intel
This is the home of the Expel Intel Team. Here, we will share IOCs and other information that is either not suitable for fitting into other mediums…
 hackinghippo/log4shell_ioc_ips
log4j / log4shell IoCs from multiple sources put together in one big file (IPs) more coming soon (CVE-2021-44228)
 guardicode/cve-2021-44228_iocs
Curated collection of public Indicators of Compromise (IoCs) for the Log4j vulnerability (CVE-2021-44228), aggregated from multiple sources for…
 certtools/intelmq
IntelMQ is a solution for IT security teams for collecting and processing security feeds using a message queuing protocol.