

C2IntelFeeds
 drb-ra/c2intelfeeds
Automatically generated C2 threat intelligence feeds of IPs, domains, URL paths, and implant configuration metadata, derived from internet scanning…
command-and-controldefensive-toolsincident-response+6
drb-ra/c2intelfeedsAutomatically generated C2 threat intelligence feeds of IPs, domains, URL paths, and implant configuration metadata, derived from internet scanning…
 doctorwebltd/malware-iocs
Curated Indicators of Compromise (IOCs) from Doctor Web malware investigations, published for threat intelligence, detection engineering, and…
 inquest/yara-rules
Collection of YARA rules for hunting malware, malicious Office documents, and exploit artifacts, with references to samples and research write-ups.
 reloading01/certstream-server-rust
High-performance Certificate Transparency (CT) monitoring tool written in Rust. Real-time stream of newly issued SSL/TLS certificates from CT logs.…
 nextronsystems/iocs
Indicators of compromise from to analysis and research by Nextron Threat Research team
 cisagov/vulnrichment
A repo to conduct vulnerability enrichment.
 opencti-platform/connectors
Collection of OpenCTI connectors that ingest and synchronize threat intelligence, IOCs, and CTI data from external sources like MISP and MITRE ATT&CK…
 vulncheck-oss/jupyter-notebooks
Example Jupyter notebooks that query VulnCheck APIs to chart exploitation timelines, Known Exploited Vulnerabilities, and botnet data for threat…
 securewithumer/exploit-index
Zero-API aggregator indexing 150k+ CVE exploits and PoCs from Exploit-DB, Nuclei, Metasploit, and CISA KEV, with EPSS/CVSS risk scoring for threat…
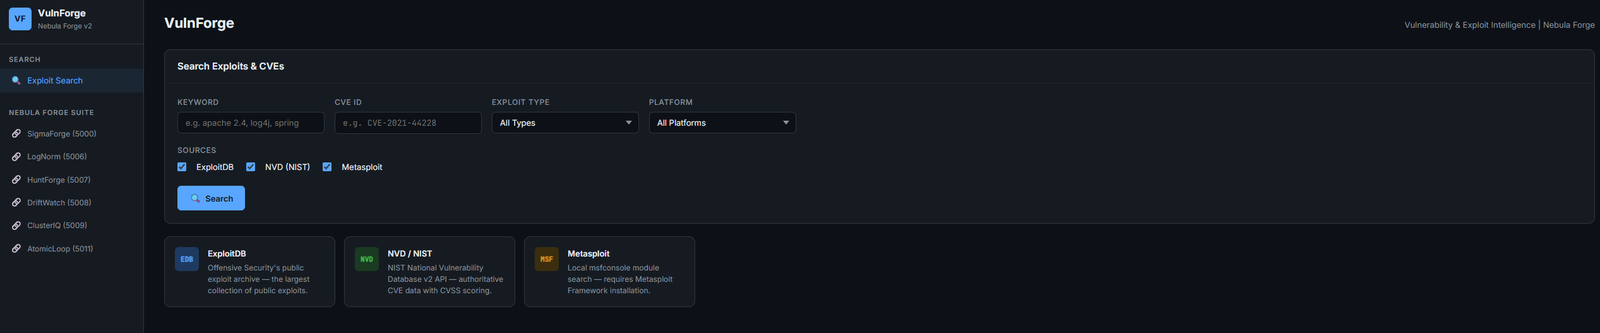 rootless-ghost/vulnforge
Vulnerability & exploit intelligence — ExploitDB, NVD, Metasploit search with CVE→ATT&CK mapping and LogNorm/HuntForge integration | Part of Nebula…
 cybershujin/prompt-injection-in-the-wild
Tracker of publicly reported prompt-injection techniques, broken down by delivery method, encoding, and propagation behavior, with confirmed models,…
 knqyf263/vuln-list-backup
Collects vulnerability and advisory data from multiple public security feeds and stores it in a parsable, structured format for downstream security…
 xghst0/reconkg
Vulnerability triage with provenance. Resolves CVEs from locally built corpora (NVD/KEV/EPSS, ExploitDB, nmap script.db) and emits verification…
 volexity/threat-intel
Signatures and IoCs from public Volexity blog posts.
 vxunderground/threatintelligencediscordbot
Gets updates from various clearnet domains and ransomware threat actor domains
 threatlabz/iocs
This repository is for Indicators of Compromise (IOCs) from Zscaler ThreatLabz public reports
 jpcertcc/phishurl-list
Phishing URL dataset from JPCERT/CC
 criticalpathsecurity/zeek-intelligence-feeds
Aggregated Zeek-format threat intelligence feeds with combined indicators from public and curated sources for continuous IDS and network threat…