

yara-rules
 inquest/yara-rules
Collection of YARA rules for hunting malware, malicious Office documents, and exploit artifacts, with references to samples and research write-ups.
curated-resourcesdefensive-toolsincident-response+5
389
inquest/yara-rulesCollection of YARA rules for hunting malware, malicious Office documents, and exploit artifacts, with references to samples and research write-ups.
 fazmin/cve-intel
Local security intelligence for CVE triage - 40 data sources and 41 tools, risk scores and an MCP server for AI agents, all in native Rust. Private…
 cisagov/kev-data
Mirrors CISA's Known Exploited Vulnerabilities (KEV) catalog as CSV and JSON with a JSON schema, enabling programmatic access and commit-history…
 vulncheck-oss/cli
VulnCheck's official command line tool
 cisagov/vulnrichment
A repo to conduct vulnerability enrichment.
 vulncheck-oss/jupyter-notebooks
Example Jupyter notebooks that query VulnCheck APIs to chart exploitation timelines, Known Exploited Vulnerabilities, and botnet data for threat…
 arpsyndicate/vedas-signatures
VEDAS-Driven Autonomous Generation + Community Contributions of Suricata & Nuclei Rules for over 15k CVEs
 securewithumer/exploit-index
Zero-API aggregator indexing 150k+ CVE exploits and PoCs from Exploit-DB, Nuclei, Metasploit, and CISA KEV, with EPSS/CVSS risk scoring for threat…
 rootless-ghost/vulnforge
Vulnerability & exploit intelligence — ExploitDB, NVD, Metasploit search with CVE→ATT&CK mapping and LogNorm/HuntForge integration | Part of Nebula…
 simplifaisoul/osiris
Open Source Global Intelligence Platform - Real-Time OSINT Dashboard - A Palantir Alternative - …
 jithinkrishnanrs/gitlab-cve-2026-85706-ioc
CVE-2026-85706 — GitLab Path Traversal IOC Scanner & Detection Toolkit. Detect and hunt for exploitation of the critical unauthenticated GitLab CE/EE…
 xghst0/reconkg
Vulnerability triage with provenance. Resolves CVEs from locally built corpora (NVD/KEV/EPSS, ExploitDB, nmap script.db) and emits verification…
 bushidouk/ransomware-tool-matrix
A resource containing all the tools each ransomware gangs uses
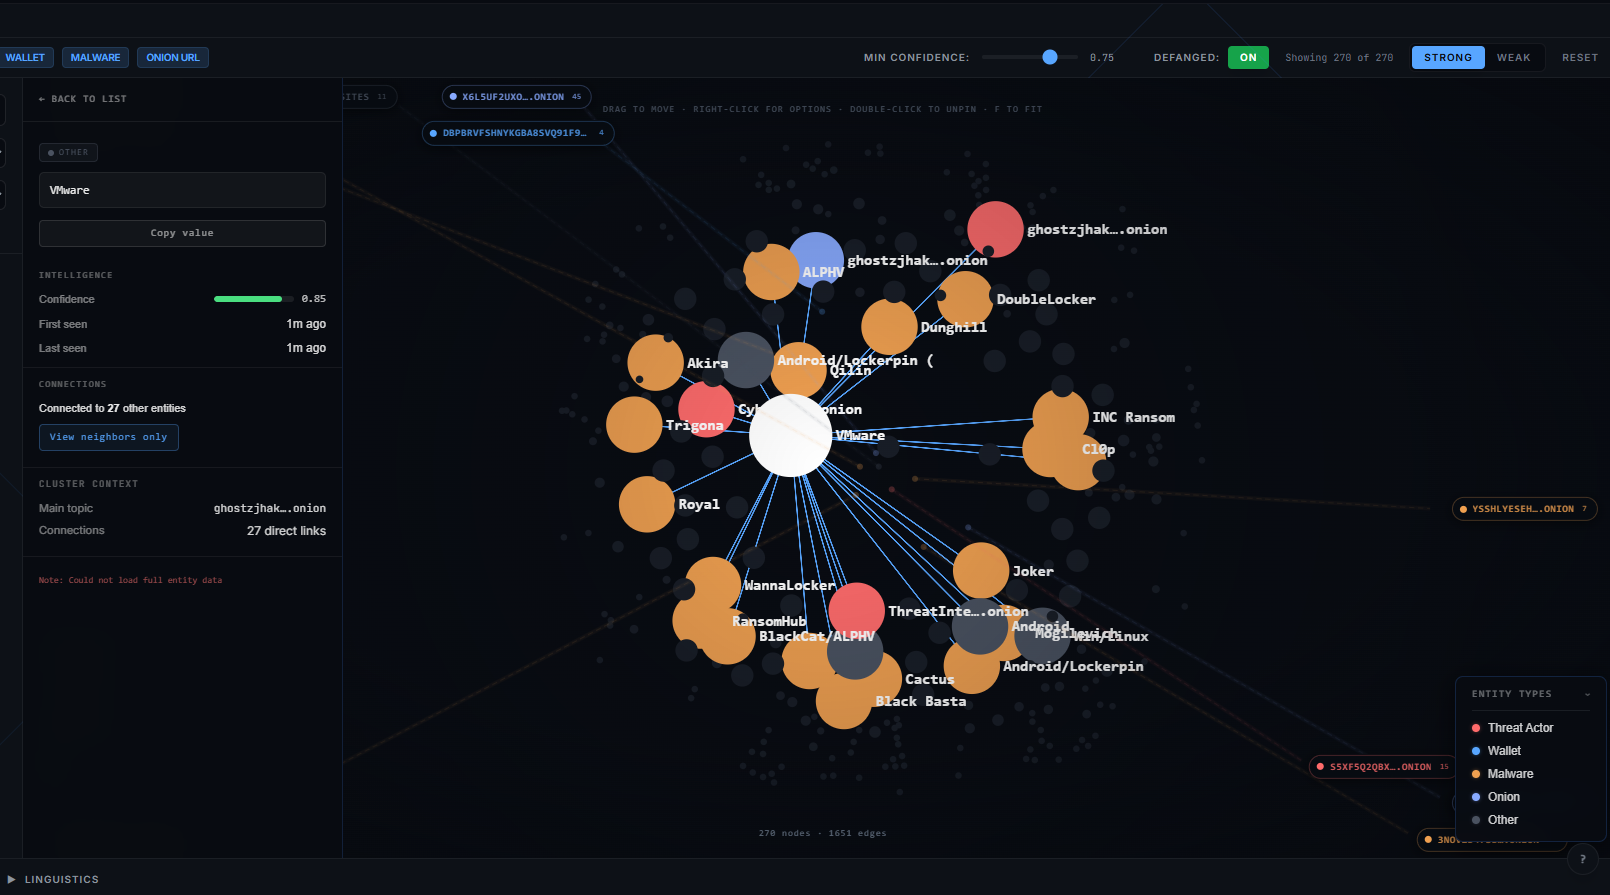 katrielmoses/voidaccess
Self-hosted dark web OSINT platform. Automated threat intelligence from query to graph in 13 steps. Free alternative to Recorded Future, DarkOwl, and…
 the-art-of-hacking/h4cker
Curated collection of cybersecurity resources, labs, and training materials covering ethical hacking, penetration testing, exploit development,…
 hackinghippo/log4shell_ioc_ips
log4j / log4shell IoCs from multiple sources put together in one big file (IPs) more coming soon (CVE-2021-44228)
 watchguard-threat-lab/log4shell-iocs
A collection of IOCs for CVE-2021-44228 also known as Log4Shell
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…