jeremylong__DependencyCheck_CVE-2018-12036_3-1-2

Software composition analysis tool that detects publicly disclosed vulnerabilities in project dependencies using CPE matching, generating detailed…

Software composition analysis tool that detects publicly disclosed vulnerabilities in project dependencies using CPE matching, generating detailed…

[Moved to Codeberg] Simple local scanner for vulnerable log4j instances

OpenClarity is an open source platform built to enhance security and observability of cloud native applications and infrastructure

Automated supply chain security monitor that polls PyPI and npm registries, diffs new releases against predecessors, and uses LLM analysis to detect…

Scans jar, war, and ear files for the presence of JndiLookup.class to detect applications vulnerable to CVE-2021-44228 (Log4Shell).

Single-binary scanner for CVE-2021-44228 (Log4Shell) that detects vulnerable log4j versions in JAR/WAR/EAR files and applies mitigation patches by…

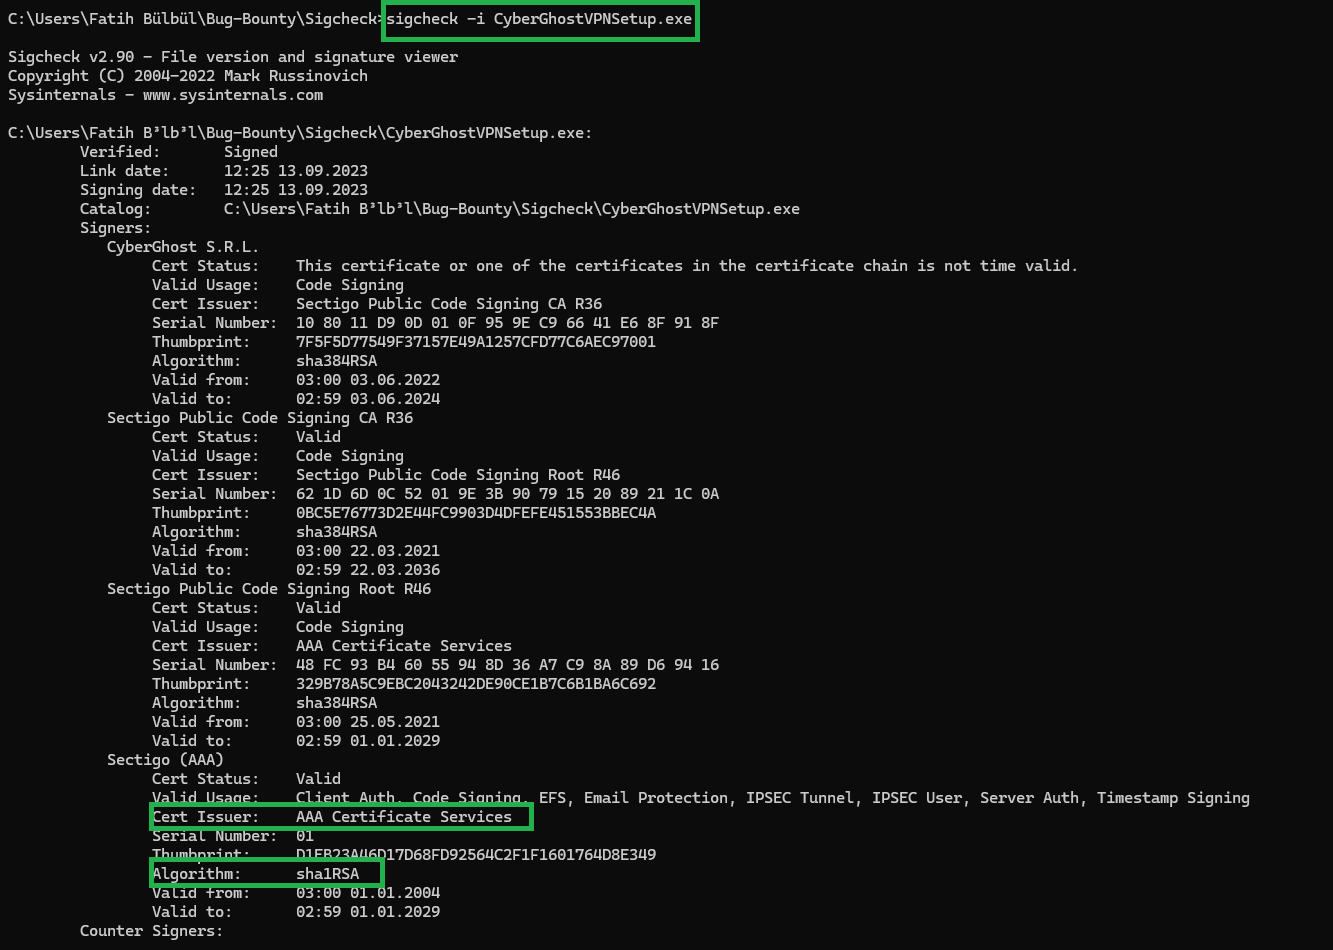
PoC demonstrating SHA-1 code signing forgery and missing High Entropy ASLR in CyberGhostVPN installer, enabling trust bypass and predictable memory…

vulnerabilities, CVE-2022-41903, and CVE-2022-23521, that affect versions 2.39 and older. Git for Windows was also patched to address an additional,…

Bash PoC for CVE-2024-32002 that exploits Git clone with malicious submodules and symlinks to execute arbitrary commands on Windows and macOS.

Seagate Toolkit for Windows (Installer <2.35.0.6) is vulnerable to insecure DLL loading. The installer loads DLLs from the working directory without…

Demonstration exploit for CVE-2022-32223: DLL hijacking in Node.js on Windows via malicious providers.dll, targeting OpenSSL installations.

Scan and patch tool for CVE-2021-44228 and related log4j concerns.

Detect CVE-2025-54313 eslint-config-prettier supply chain attack IOCs on Windows

Discover and remediate Log4Shell vulnerability [CVE-2021-45105]

A dead simple tool to sign files and verify digital signatures.

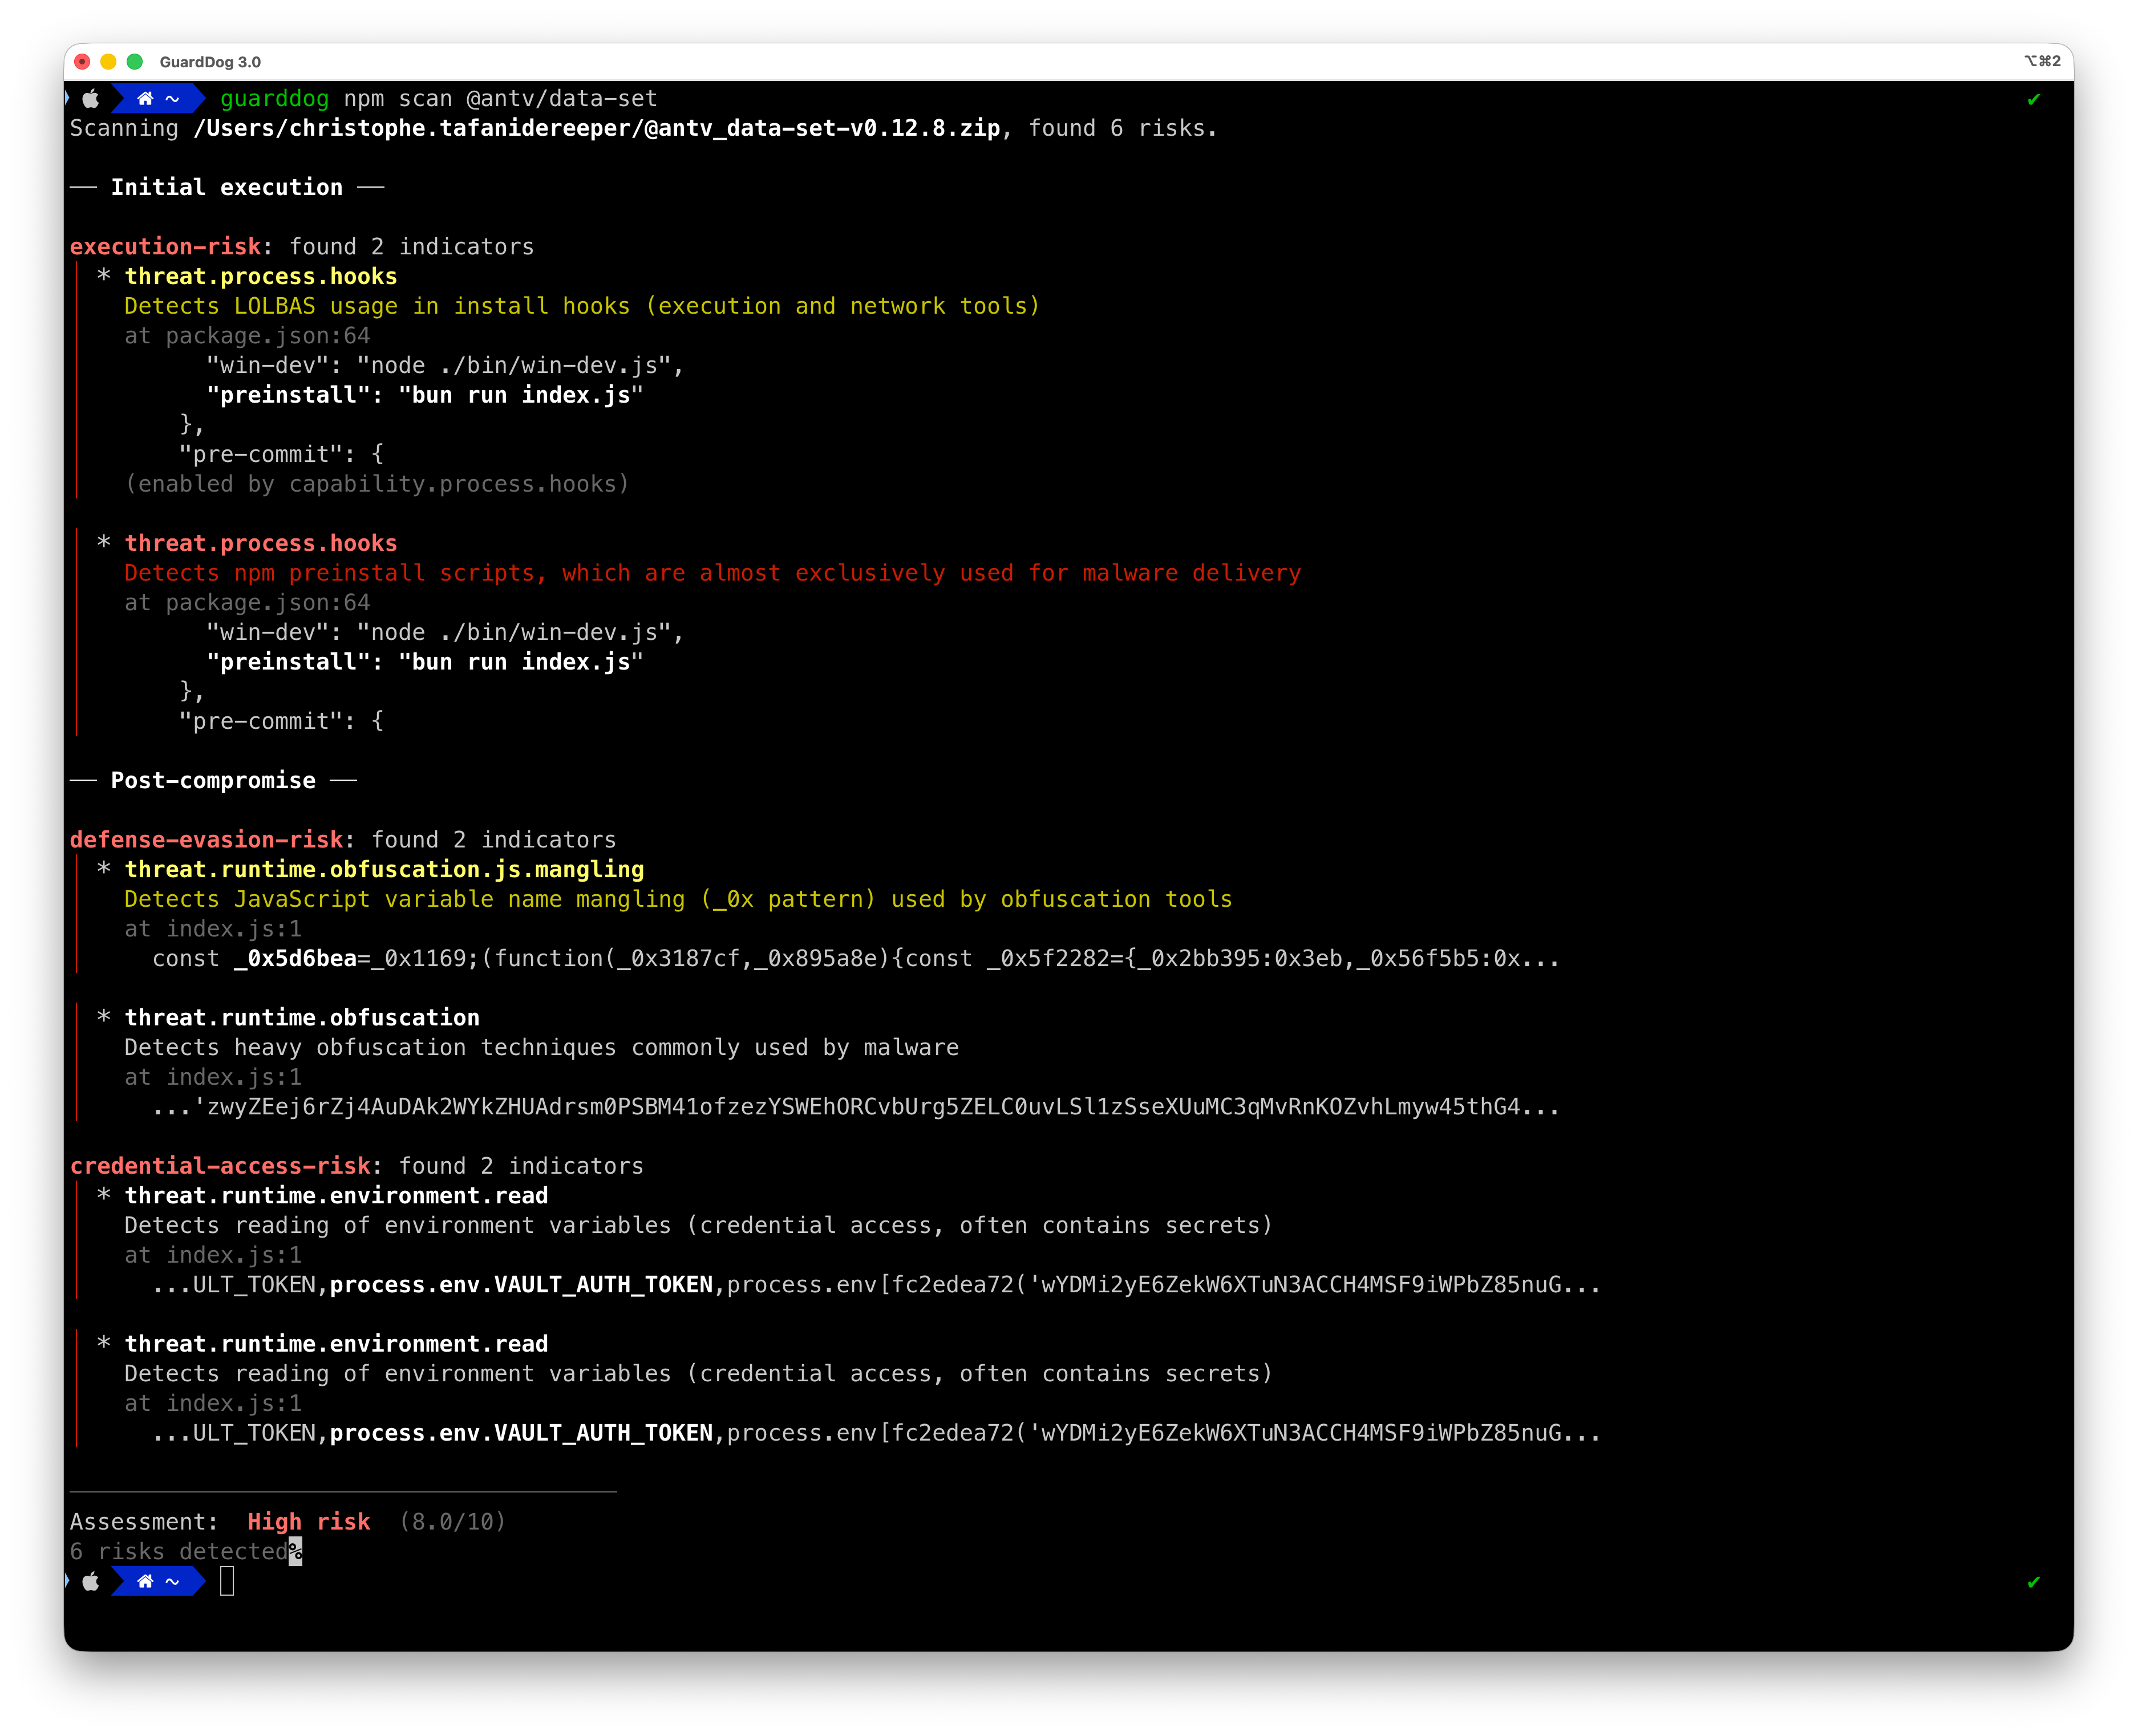
🐍 🔍 GuardDog is a CLI tool to Identify malicious PyPI and npm packages

An agent to hotpatch the log4j RCE from CVE-2021-44228.

Formal inter-procedural taint analysis engine for application security. Tracks untrusted data across function boundaries, persistence layers, and…