

trivy
 aquasecurity/trivy
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
cloud-infrastructure-securitycloud-securitycode-analysis+14
38.2k
aquasecurity/trivyFind vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
 gitleaks/gitleaks
Fast, open-source static analysis tool for detecting hardcoded secrets like passwords, API keys, and tokens in git repositories, files, and stdin…
 nvidia/skillspector
Security scanner for AI agent skills. Detect vulnerabilities, malicious patterns, security risks, prompt injection, data exfiltration, and…
 dependency-check/dependencycheck
OWASP dependency-check is a software composition analysis utility that detects publicly disclosed vulnerabilities in application dependencies.
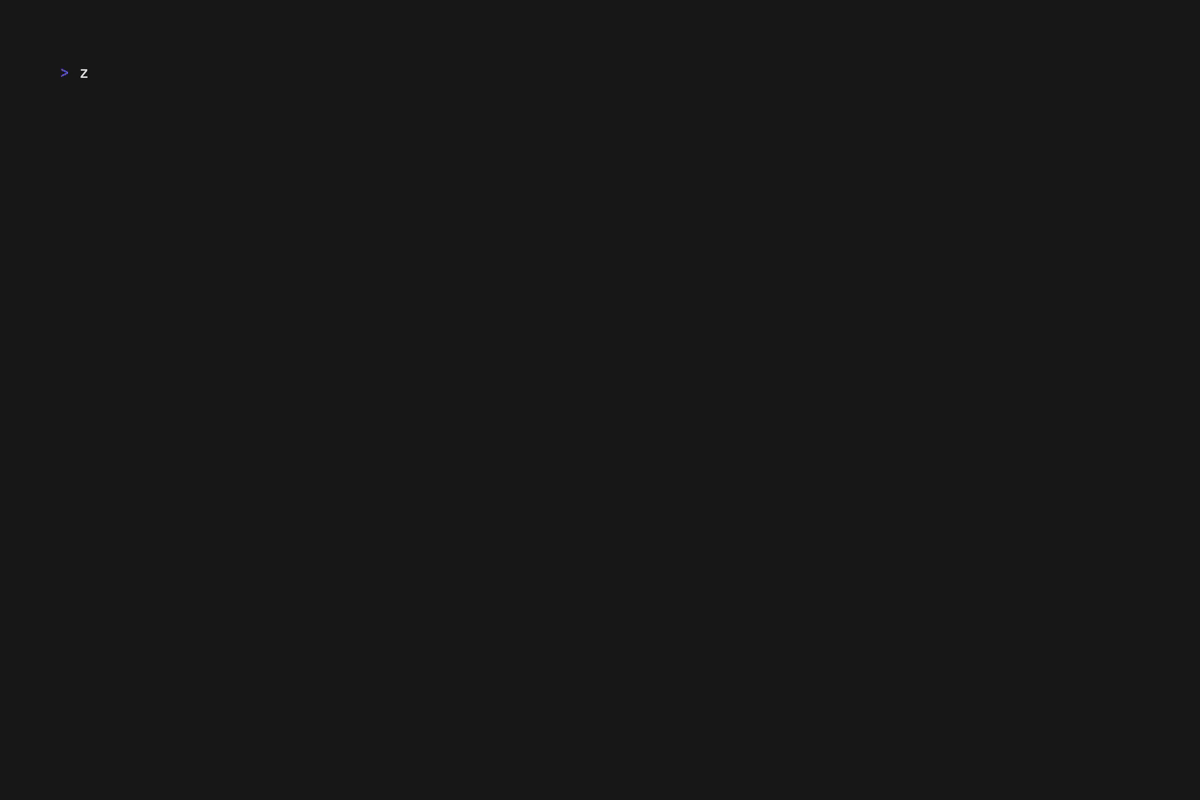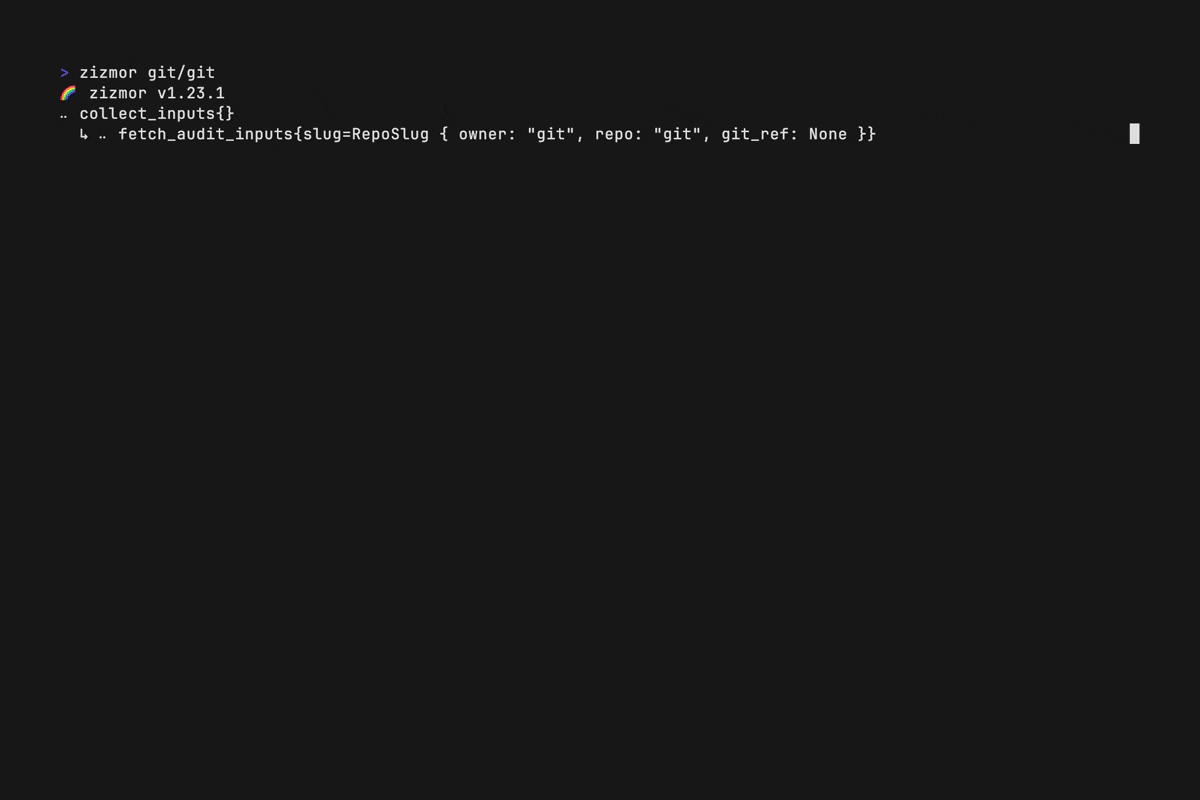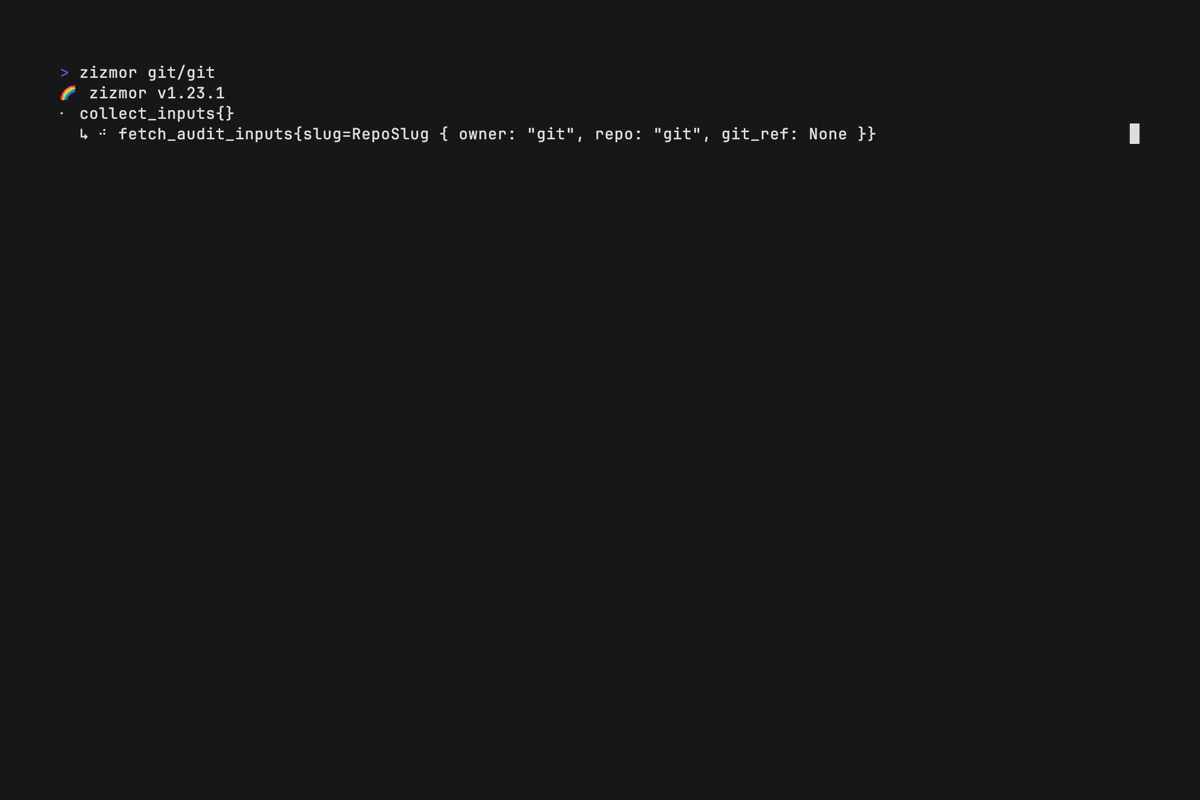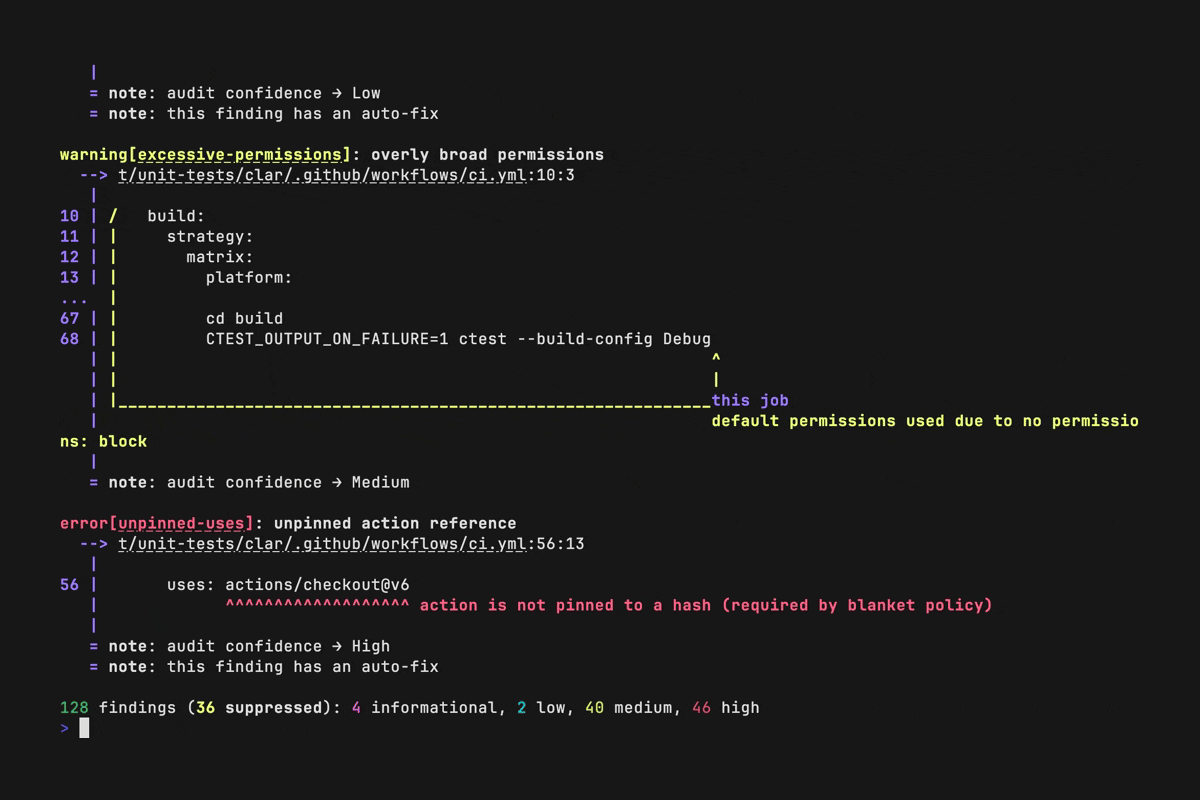 zizmorcore/zizmor
Static analysis tool for CI/CD systems that detects and fixes security issues in GitHub Actions, Dependabot, and pre-commit configurations, including…
 microsoft/applicationinspector
A source code analyzer built for surfacing features of interest and other characteristics to answer the question 'What's in the code?' quickly using…
 pypa/advisory-database
Community-owned database of security advisories for Python packages on PyPI, providing structured vulnerability data in OSV format for integration…
 lunasec-io/lunasec
LunaSec - Dependency Security Scanner that automatically notifies you about vulnerabilities like Log4Shell or node-ipc in your Pull Requests and…
 visma-prodsec/confused
Tool to check for dependency confusion vulnerabilities in multiple package management systems
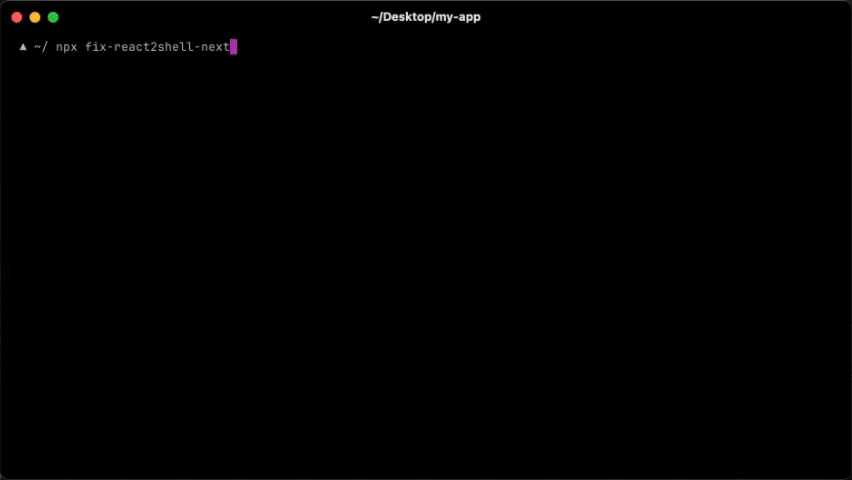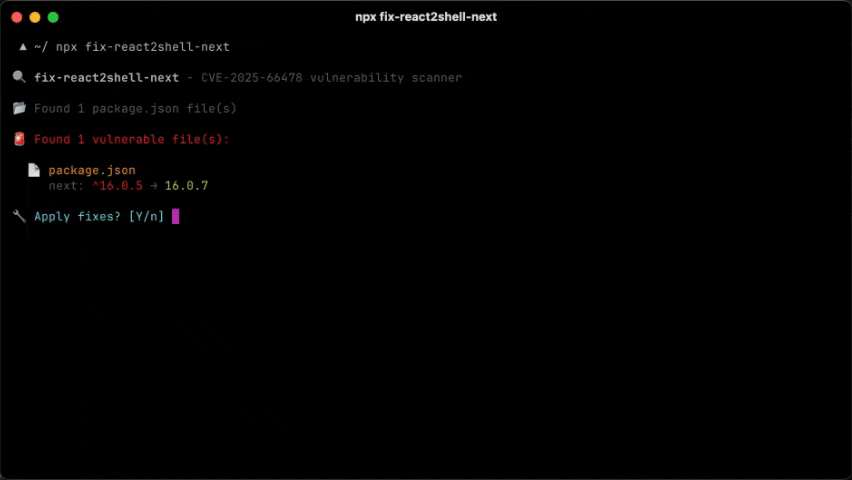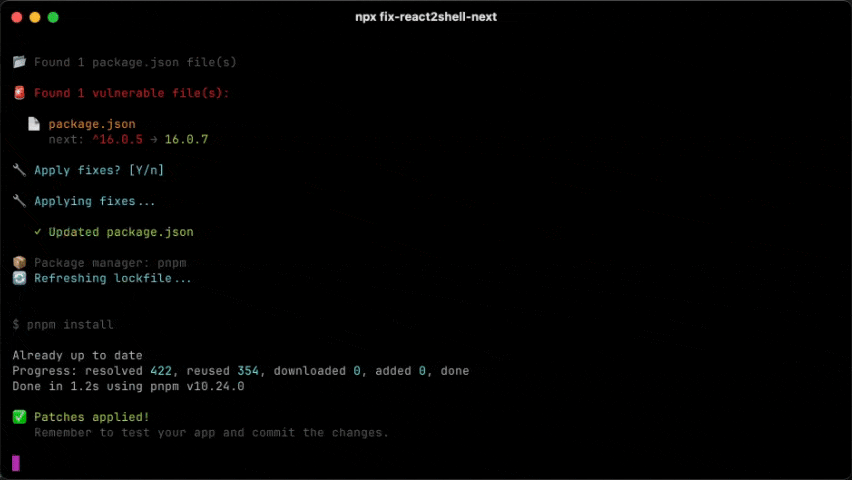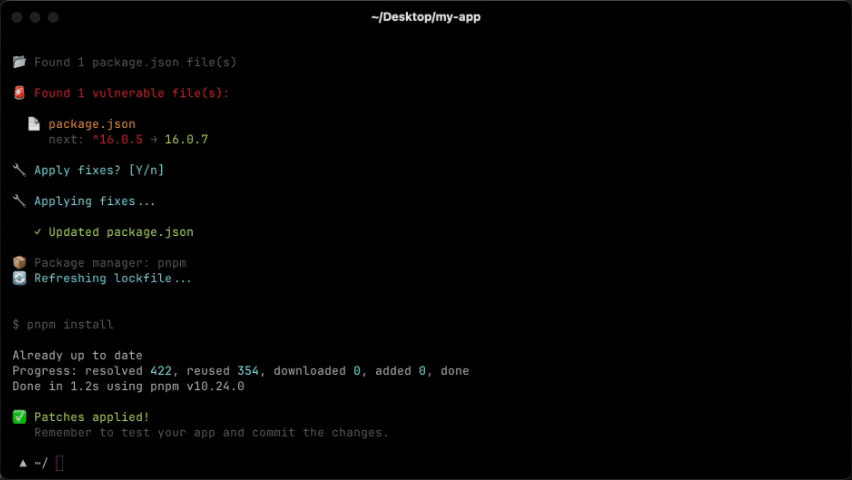 vercel-labs/fix-react2shell-next
One command to fix CVE-2025-66478 (React 2 Shell RCE) in your Next.js / React RSC app.
 greatscott/enject
enject: Hide .env secrets from prAIng eyes: secrets live in local encrypted stores (per project) and are injected directly into apps at runtime,…
 ohaswin/pyscan
python dependency vulnerability scanner, written in Rust.
 oxsecurity/codetotal
Analyze any snippet, file, or repository to detect possible security flaws such as secret in code, open source vulnerability, code security,…
 ransomleak/training-application-security
Interactive secure coding training with hands-on SCORM exercises covering OWASP Top 10 web and API vulnerabilities, Git/secrets exposure, and…
 knqyf263/remic
Vulnerability Scanner for Detecting Publicly Disclosed Vulnerabilities in Application Dependencies
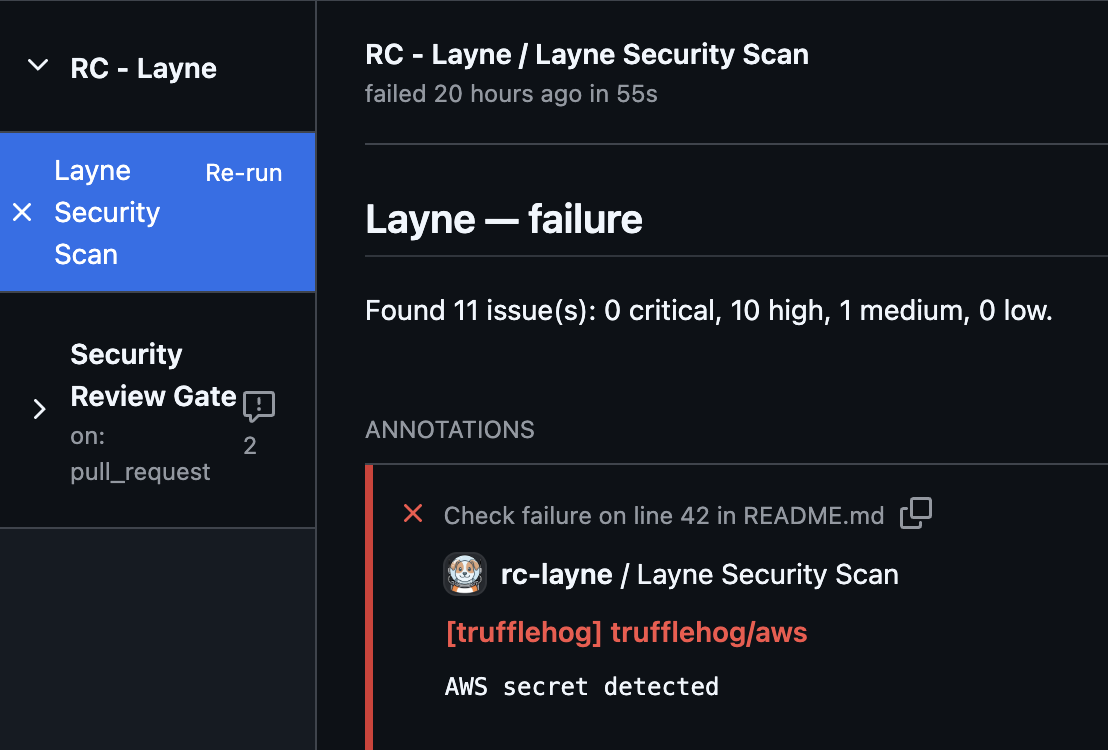 rocketchat/layne
A doggo that helps look for security issues in your repositories.
 golab-arch/synaptic-sentinel
The vibe-coding security sentinel. Apache-2.0 agentic security toolkit for AI-assisted projects: 5 deterministic scouts + LLM Brain Layer (BYOK…
 jvr2022/cve-2026-40345
Reproduces a stack-exhaustion denial-of-service in deepmerge-ts before 8.0.0, documents exploitation, and includes a scanner for vulnerable…