Openssl-1.1.1g_CVE-2022-4304

OpenSSL toolkit providing TLS/SSL protocols and general-purpose cryptographic library with command-line tools for key generation, certificate…

OpenSSL toolkit providing TLS/SSL protocols and general-purpose cryptographic library with command-line tools for key generation, certificate…

Proof-of-concept and analysis tools for CVE-2024-3094, the XZ Utils backdoor vulnerability, including detection and exploitation scripts.

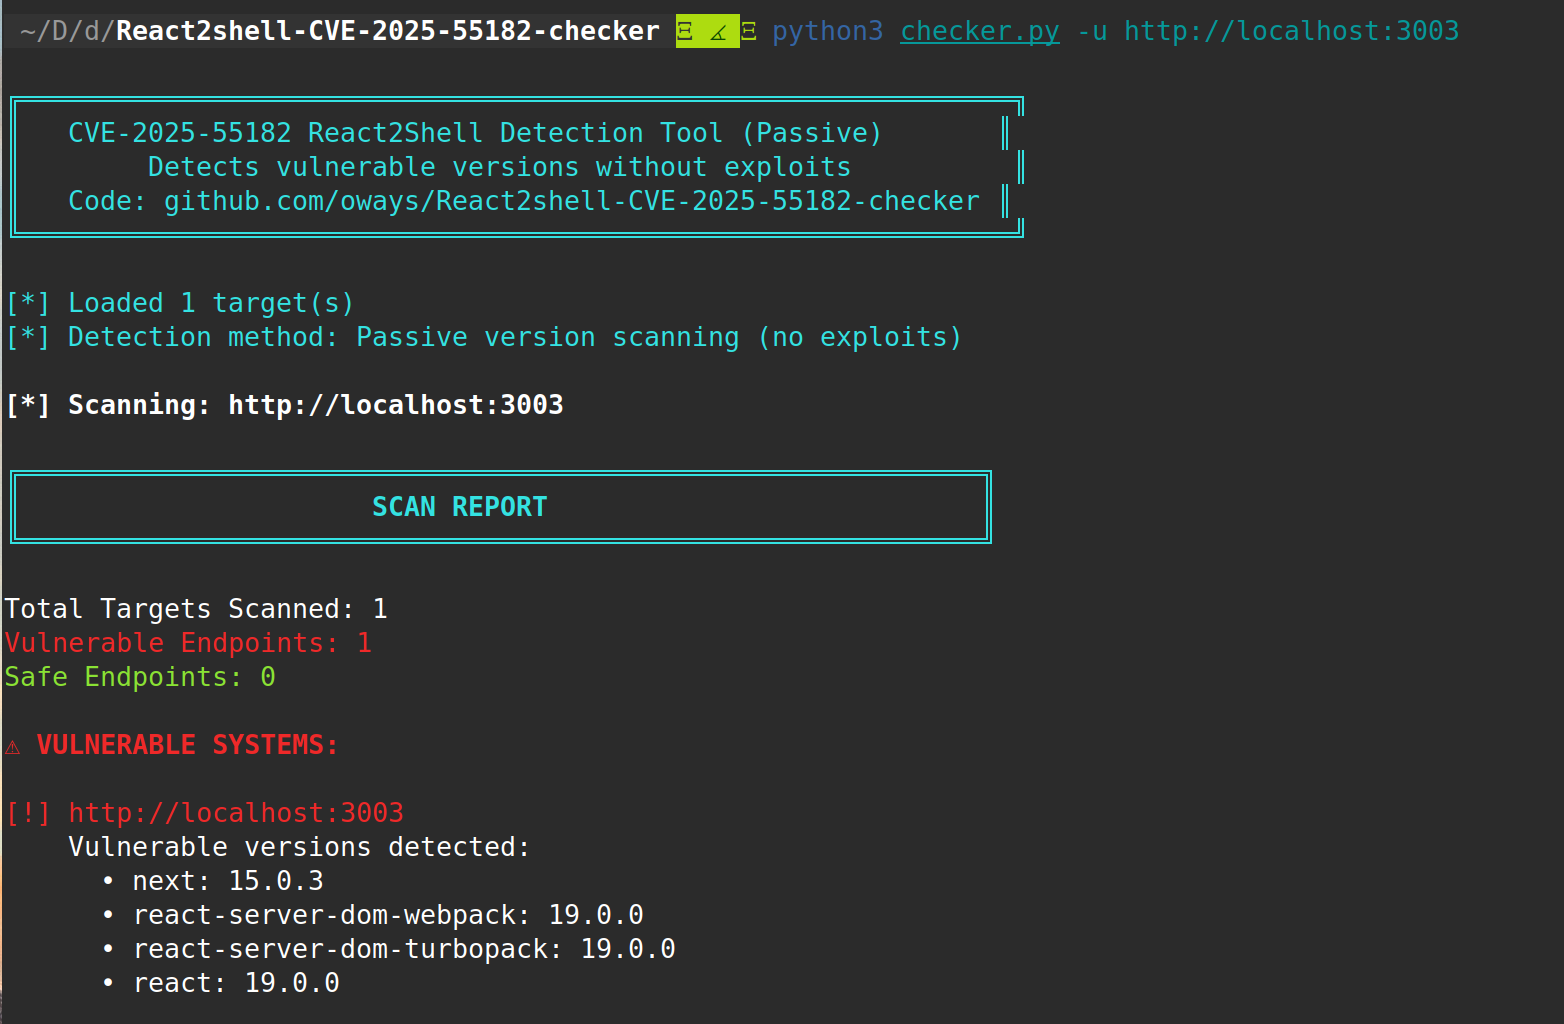
Passive CVE-2025-55182 detection tool for vulnerable React Server Components. Scans package.json, JavaScript bundles, HTTP headers, and API endpoints…

Scans GitHub workflows and logs for indicators of CVE-2025-30066, detecting malicious actions and exposed secrets using Checkmarx 2ms integration.

Shell-based scanner to detect the XZ Backdoor (CVE-2024-3094) vulnerability in files and directories, enabling rapid identification and mitigation of…

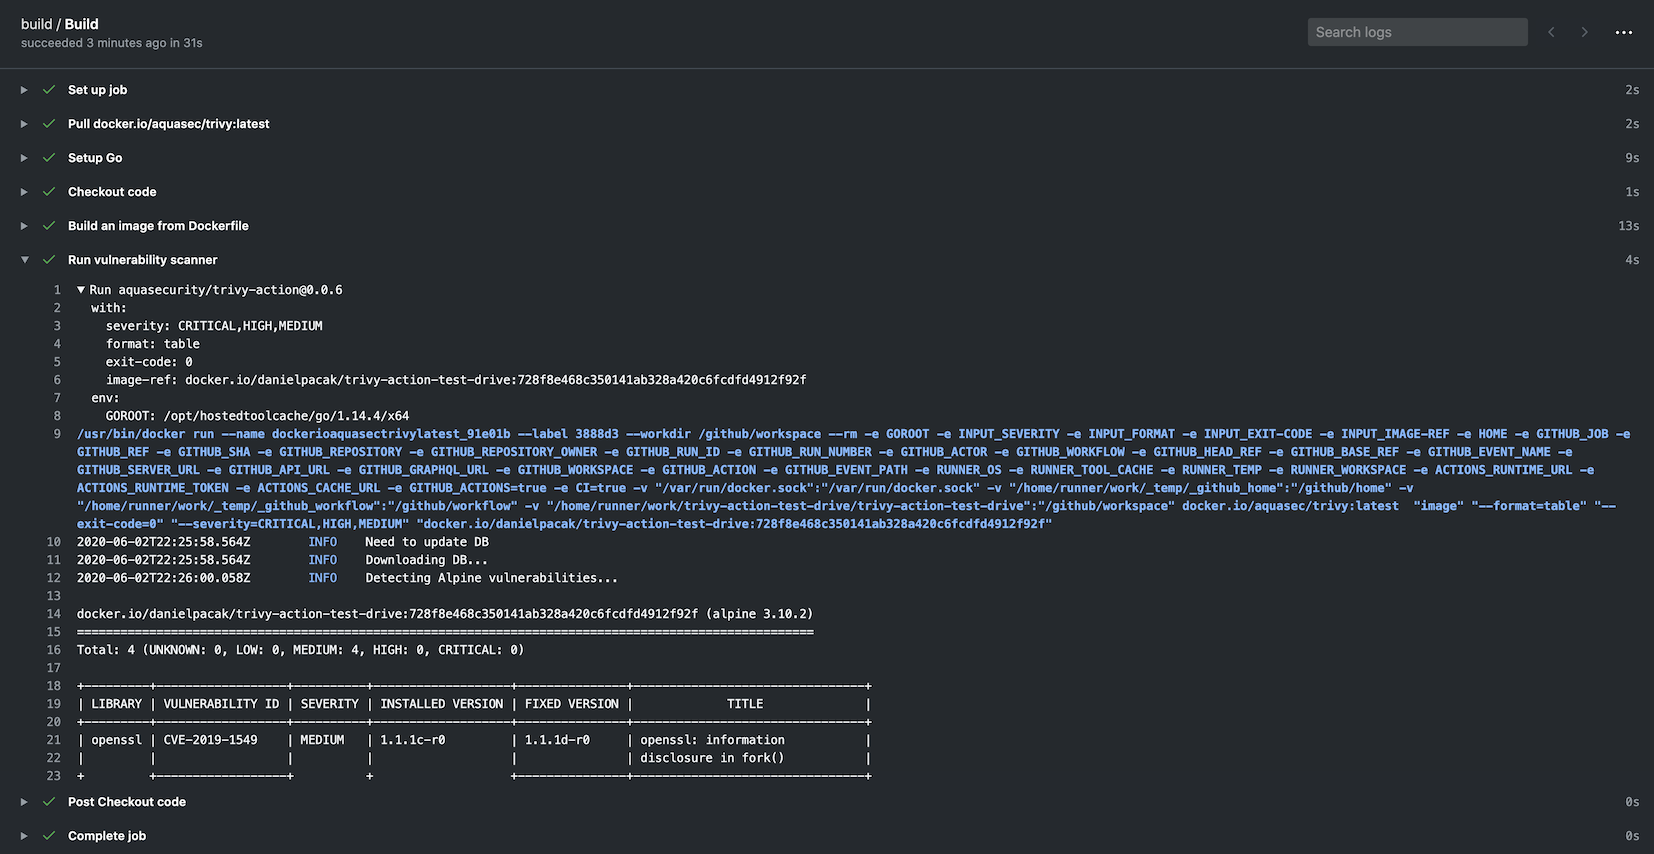
Runs Trivy as GitHub action to scan your Docker container image for vulnerabilities

Go-based CLI tool that scans codebases for launch readiness, detecting missing configuration, security hygiene issues, secret leaks, and integration…

Fast, open-source static analysis tool for detecting hardcoded secrets like passwords, API keys, and tokens in git repositories, files, and stdin…

Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.

Security scanner for AI agent skills. Detect vulnerabilities, malicious patterns, security risks, prompt injection, data exfiltration, and…

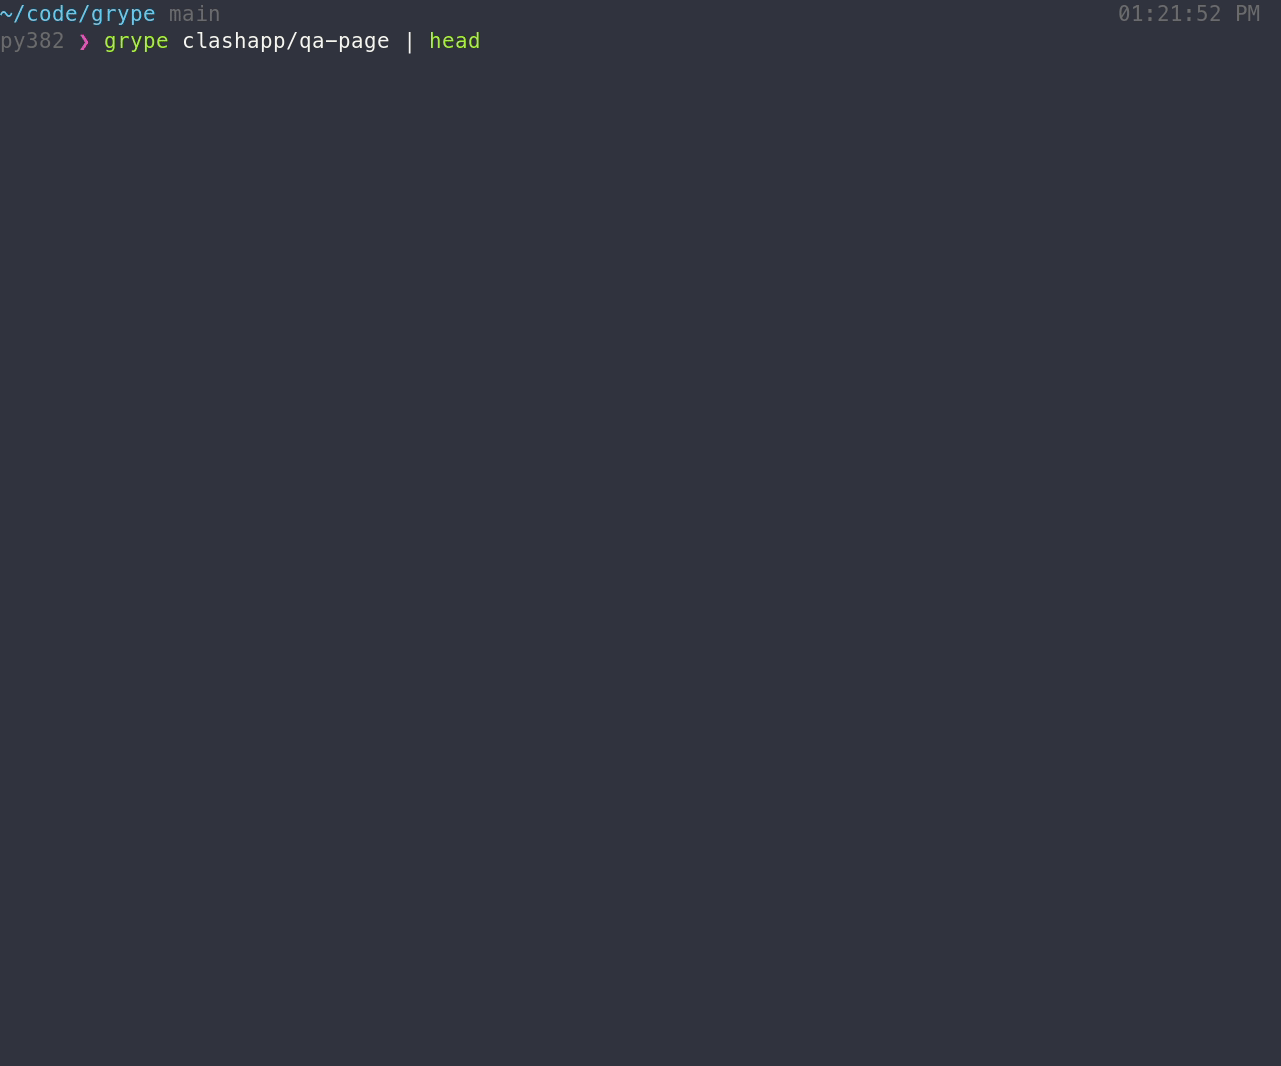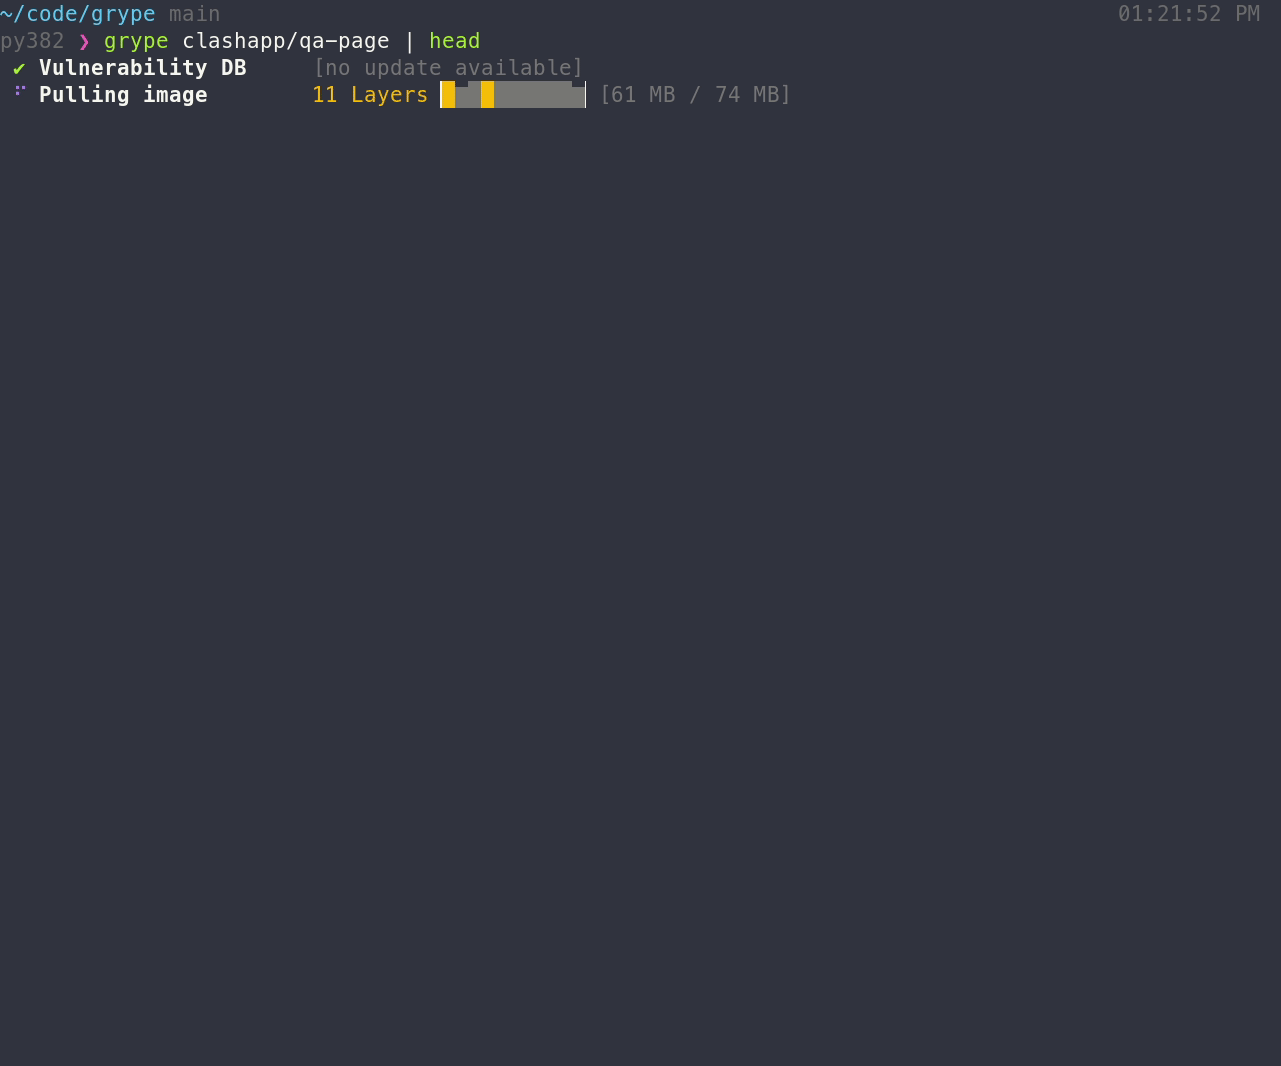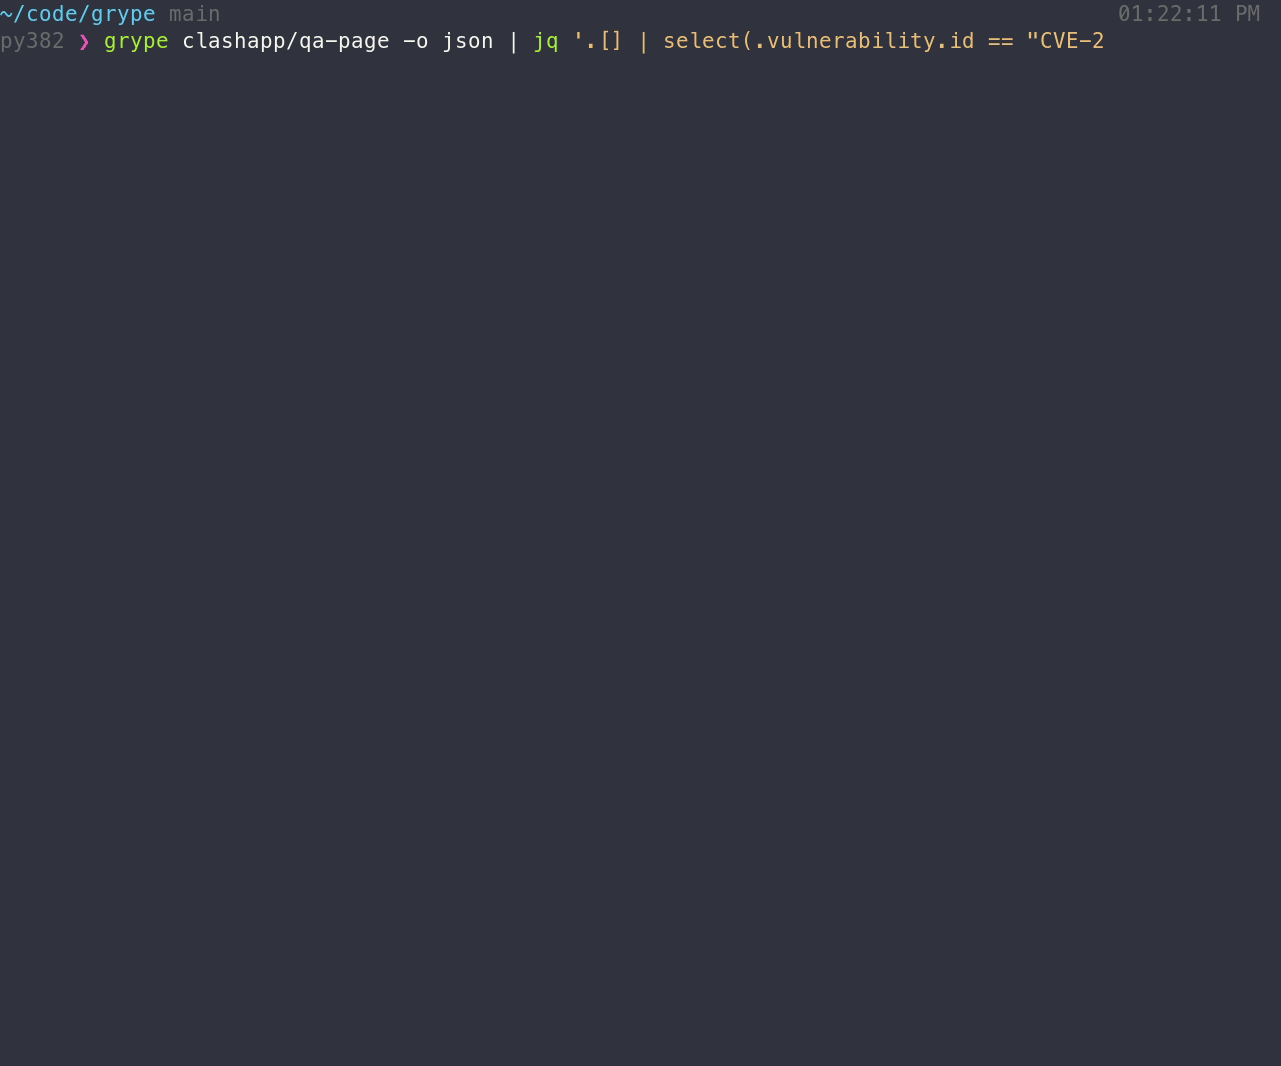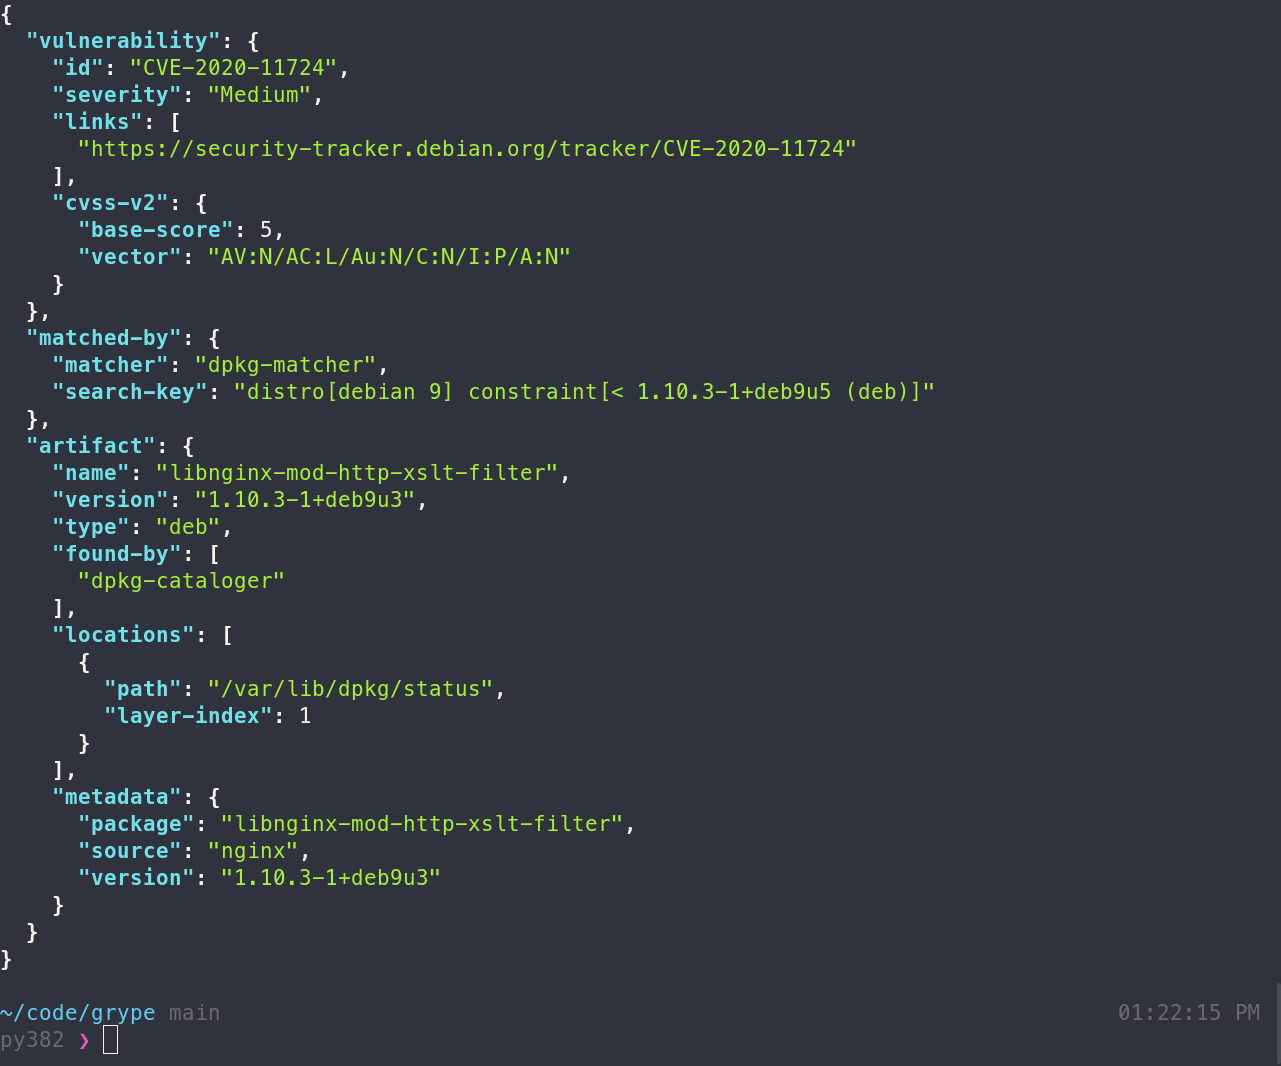
A vulnerability scanner for container images and filesystems

Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…

CLI tool and library for generating a Software Bill of Materials from container images and filesystems

Snyk CLI scans and monitors your projects for security vulnerabilities.

Code signing and transparency for containers and binaries

OpenSSF Scorecard - Security health metrics for Open Source

Hardened, Azure-optimized Linux distribution built from Fedora sources with RPM packaging, supply chain security, and declarative configuration for…

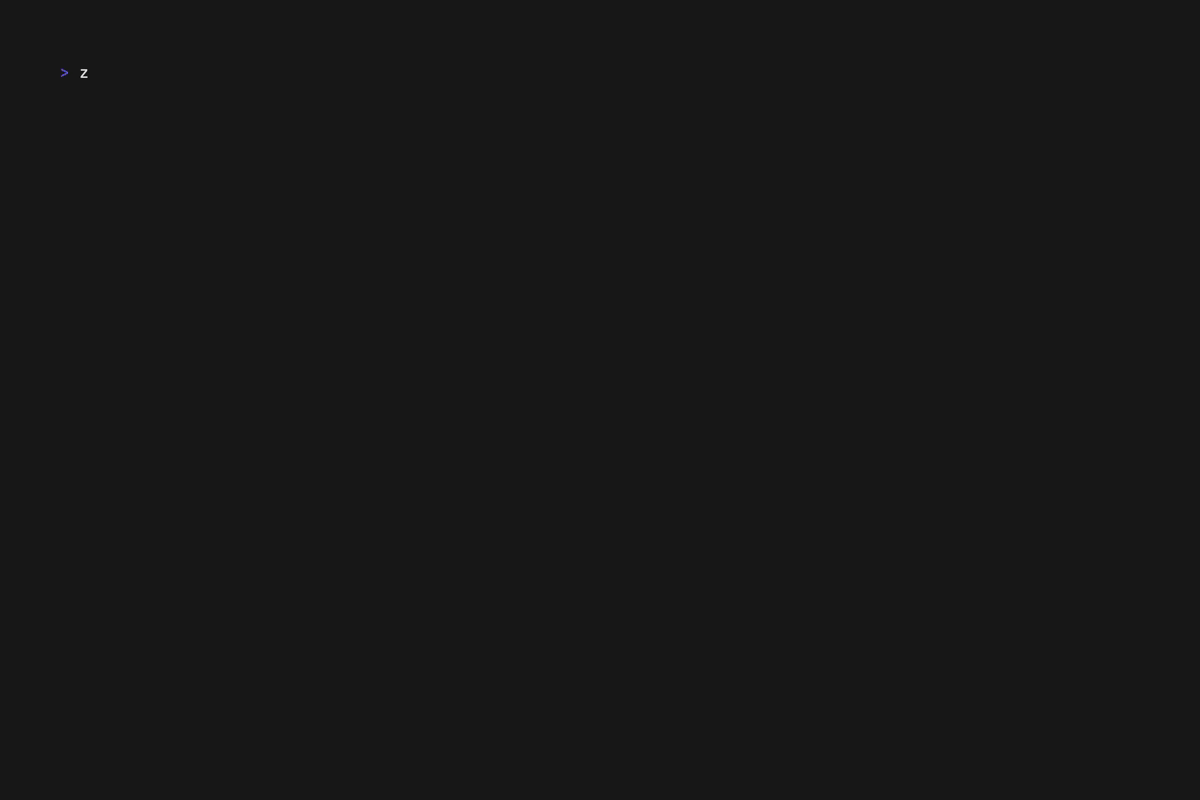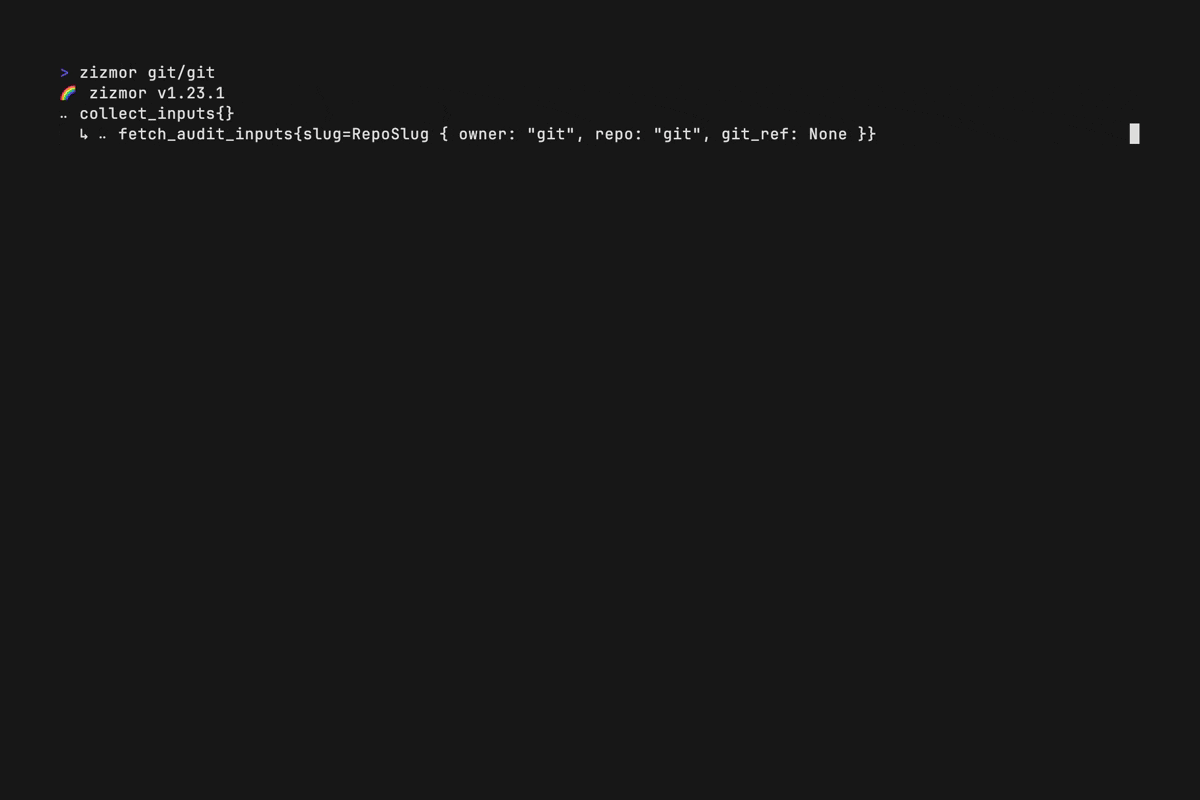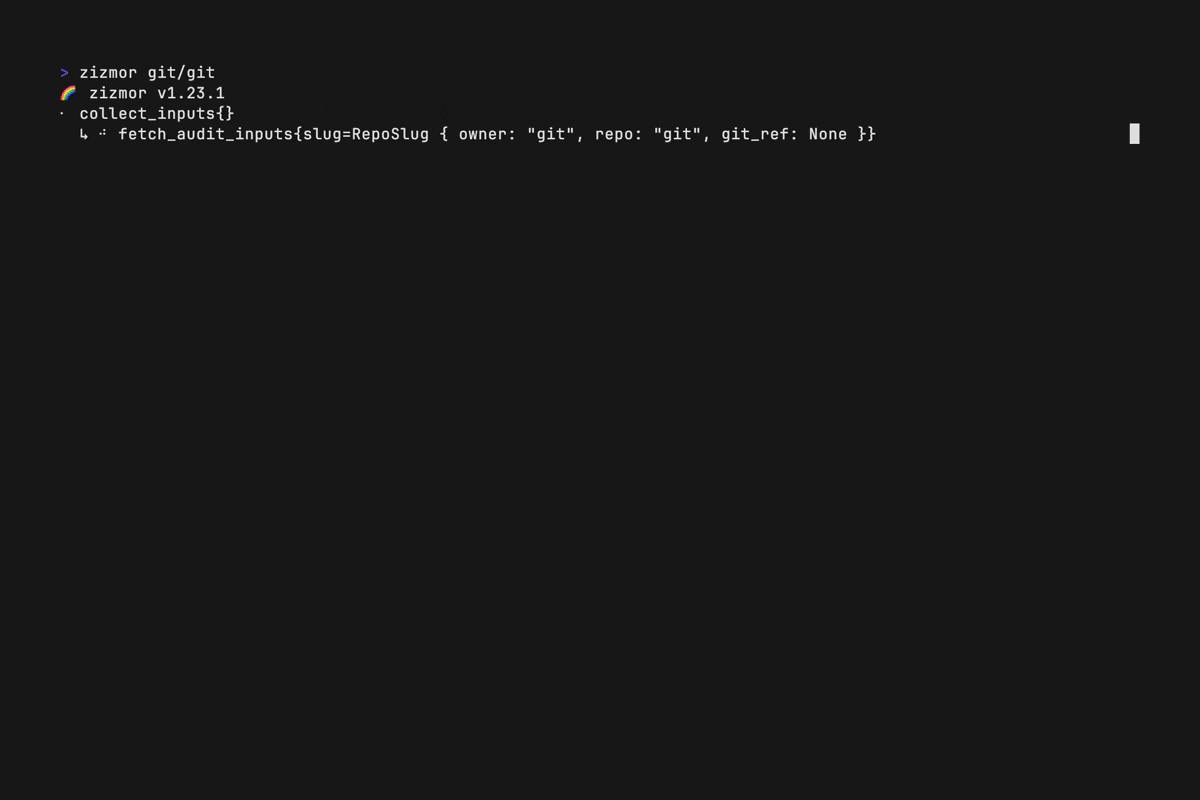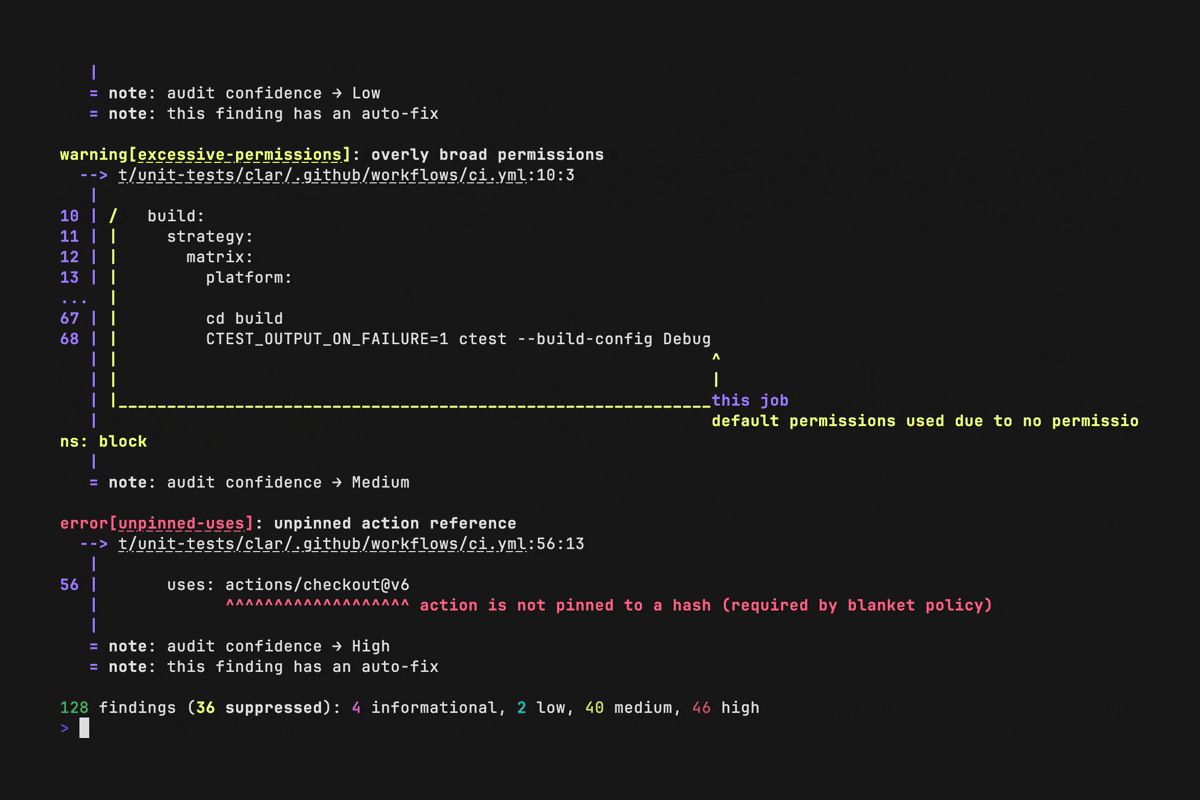
Static analysis tool for CI/CD systems that detects and fixes security issues in GitHub Actions, Dependabot, and pre-commit configurations, including…