
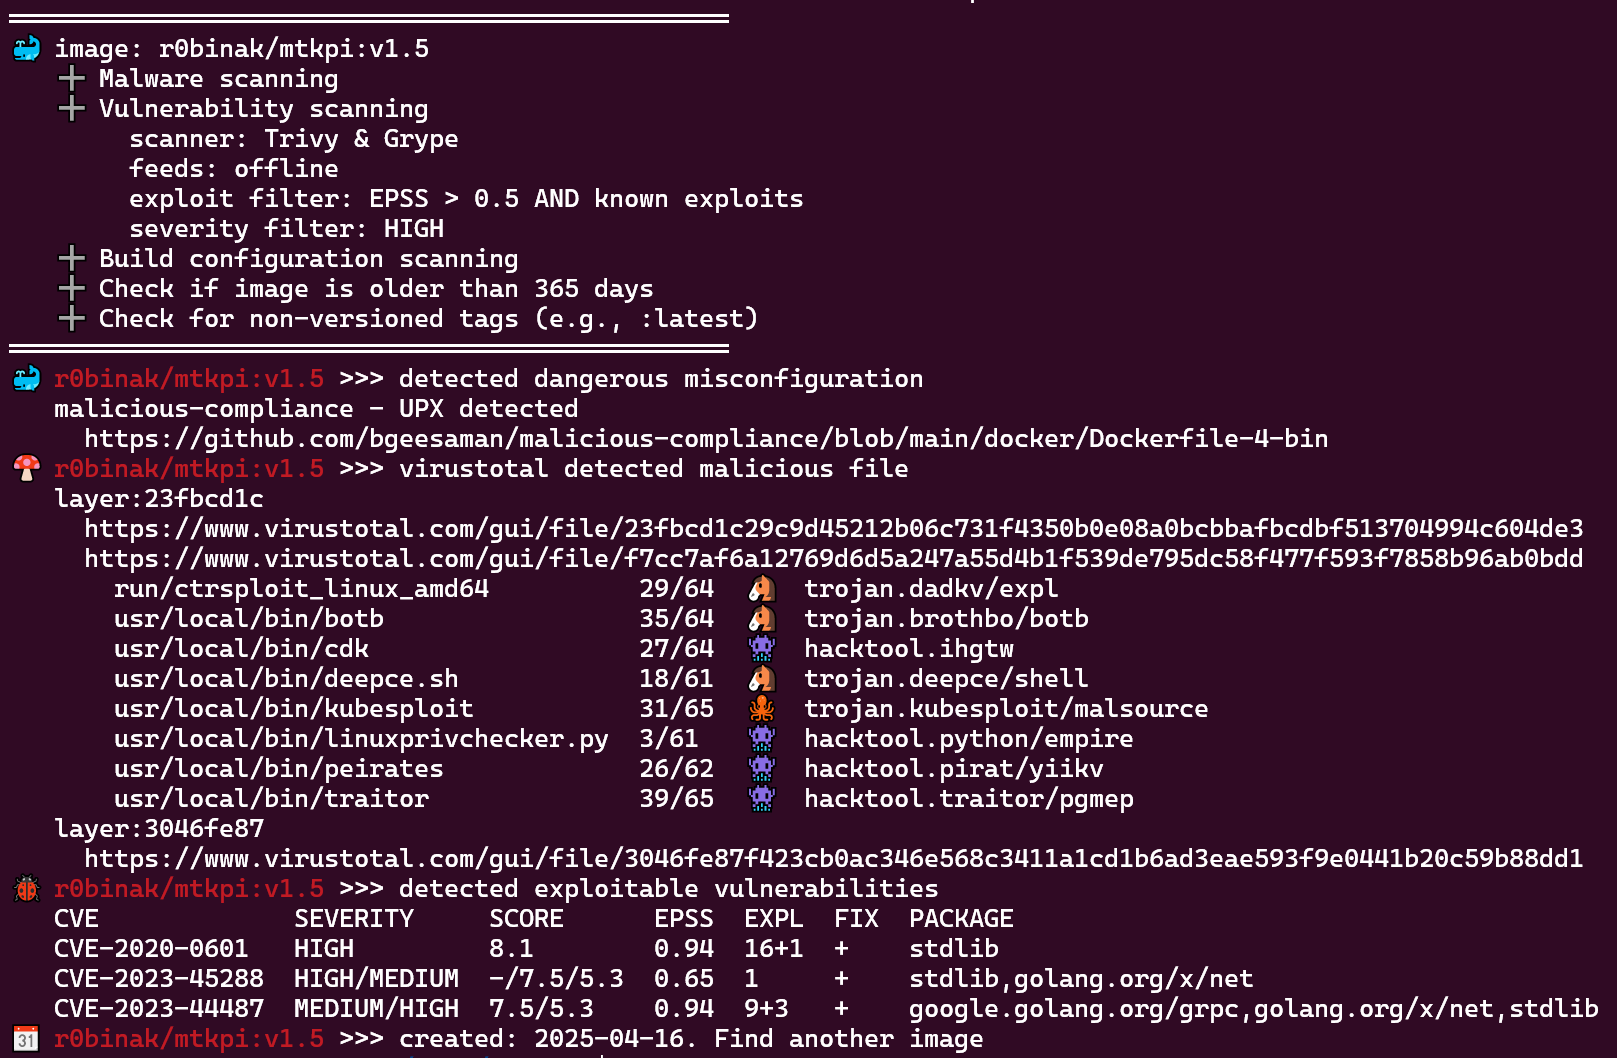
pisc
 ecomtech-oss/pisc
Public OCI-Image (docker image) Security Checker
container-securitydevsecopsmalware-analysis+3
217 months ago
ecomtech-oss/piscPublic OCI-Image (docker image) Security Checker
 wspr-ncsu/mininode
Static analysis CLI tool that reduces Node.js application attack surface by constructing dependency graphs and removing unused modules and functions…
 heroku/terrier
Terrier is a Image and Container analysis tool that can be used to scan Images and Containers to identify and verify the presence of specific files…
 morpheuslord/startup-sbom
A tool to reverse engineer and inspect the RPM and APT databases to list all the packages along with executables, service, versions and CVE.
 gmh5225/disclosure-check
Tool to identify the best mechanisms for privately disclosing a security vulnerability for a package/project.
 bio/vue-template-compiler-patched
Patched Vue 2.7.16 template compiler with fixes for CVE‑2024‑6783 and CVE-2024-9506
 padayali-jd/pollyscan
A specialized vulnerability scanner designed to detect CVE-2024-38526, the Polyfill.io Supply Chain Attack, helping organizations identify and…
 aquasecurity/scan-cve-2018-8115
CLI tool that verifies Docker images for CVE-2018-8115 by checking layers for malicious files, helping ensure safe pulls from Docker Hub.
 skyscanner/whispers
Identify hardcoded secrets in static structured text
 jbnetwork-git/cve-2024-3094-xz-utils-check
Shell script to check if your system has a vulnerable version of XZ Utils affected by CVE-2024-3094, enabling quick detection of the supply-chain…
 garethmsheldon/react2shell-cve-2025-55182-detector
Multi-language detection scripts for CVE-2025-55182 (React2Shell) that scan package.json files to identify vulnerable React dependency versions and…
 jacobtread/l4j-vuln-patch
This tool patches the CVE-2021-44228 Log4J vulnerability present in all minecraft versions NOTE THIS TOOL MUST BE RE-RUN after downloading or…
 qainsights/cve-2022-42889-jmeter
Script to handle CVE 2022-42889
 tharindudh/tharindudh-log4j-vulnerability-in-ghidra-tool-cve-2021-44228
Ghidra-based tool for detecting and analyzing the Log4j vulnerability (CVE-2021-44228) in binary files, enabling reverse engineering of affected…

 vinnimarcon/log4j-updater
Log4J Updater Bash Script to automate the framework update process on numerous machines and prevent the CVE-2021-44228
 junnythemarksman/cve-2024-24590
Deserialization of untrusted data can occur in versions 0.17.0 to 1.14.2 of the client SDK of Allegro AI’s ClearML platform, enabling a maliciously…
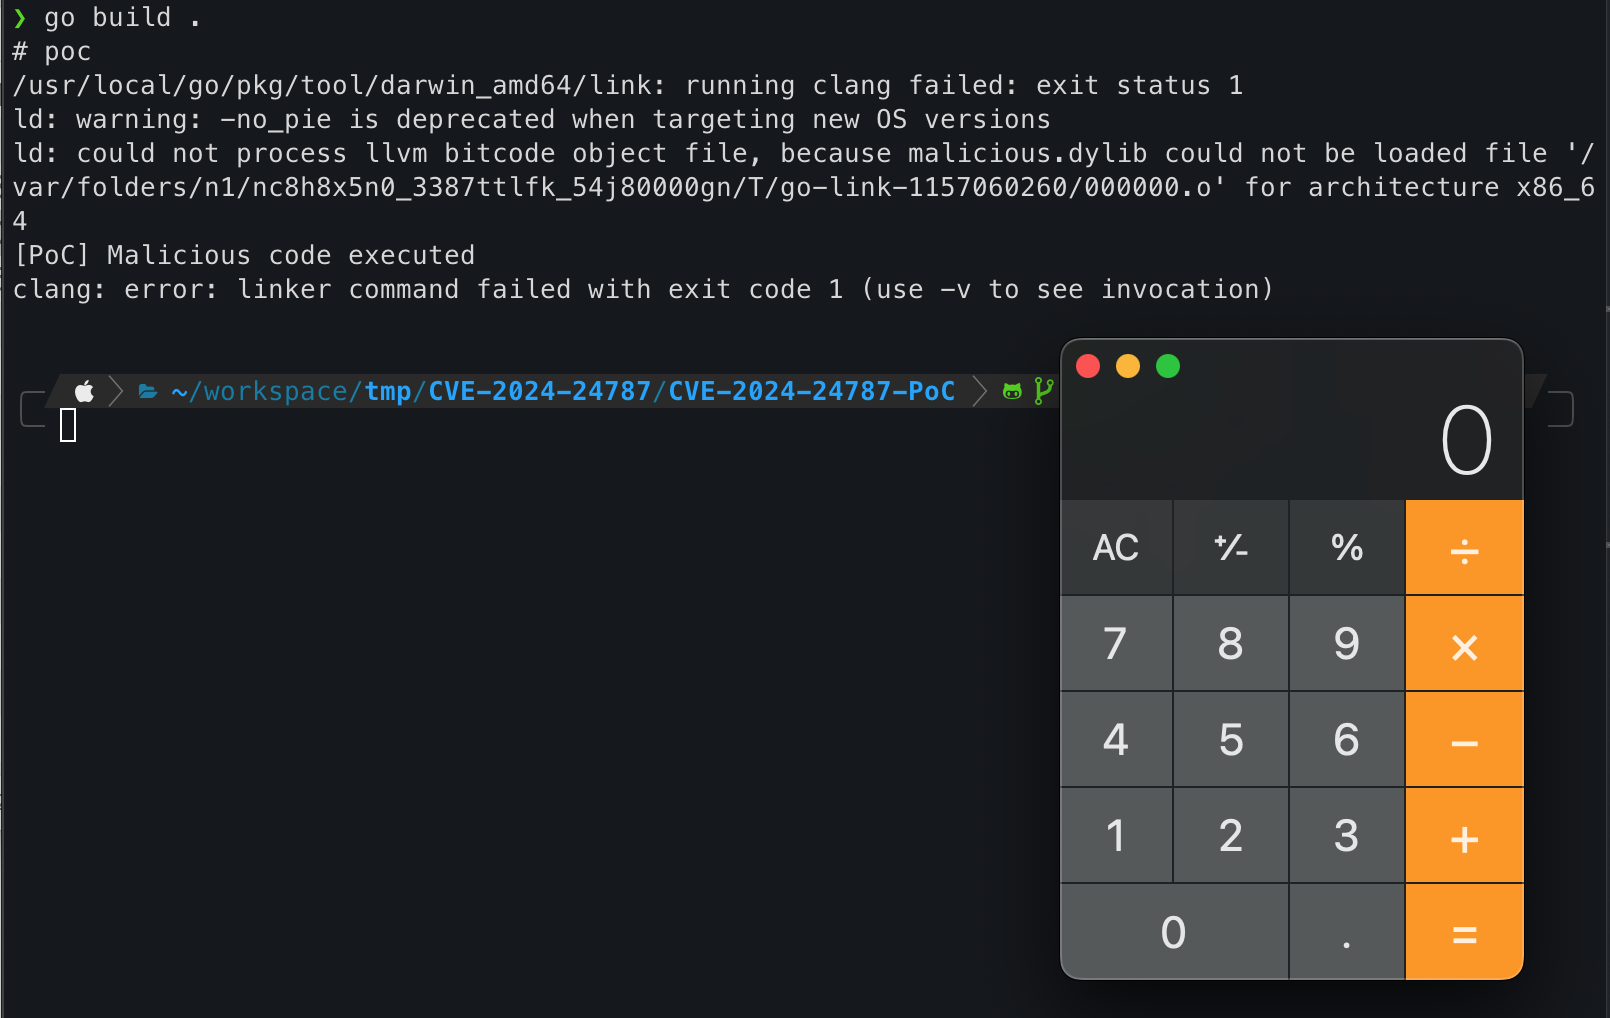 lourc0d3/cve-2024-24787-poc
CVE-2024-24787 Proof of Concept