
APTS
 owasp/apts
OWASP Autonomous Penetration Testing Standard
api-securitycloud-securitycurated-resources+5
owasp/aptsOWASP Autonomous Penetration Testing Standard
 traceforce/mcp-xray
Unified security scanner for MCP servers with config, pentest, and repo-scan modes. Generates SARIF reports for CI/CD integration, detects secrets,…
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
 asamassekou10/ship-safe
The independent security agent for AI-written software. Finds issues, investigates whether they are real, and shows you the evidence. Deterministic…
 arpsyndicate/puncia
Panthera(P.)uncia - Official CLI utility for Subdomain Center & Exploit Observer.
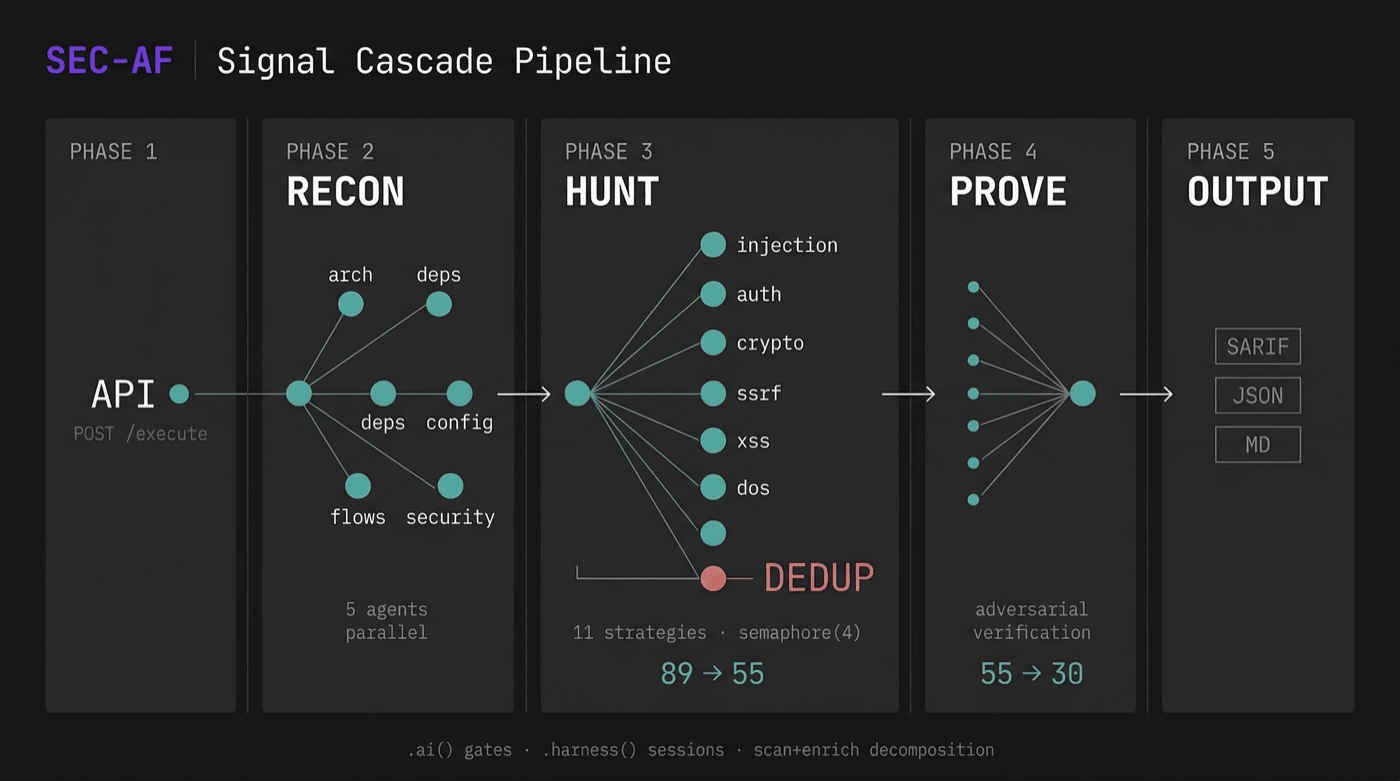 agent-field/sec-af
AI-native code security auditor on AgentField that proves exploitability with verdicts, traces, and actionable evidence.
 kpcyrd/sh4d0wup
Signing-key abuse and update exploitation framework
 nuguardai/nuguard
opensource repo for validating agentic AI applications: redteam, behavior, supply-chain, static analysis
 metaredteam/rtx-cve-2023-45779
Proof-of-concept code for Android APEX key reuse vulnerability
 kavan00/android-projector-c2-malware
Breakdown of a c2-network of chinese beamers - SilentSDK-Analysis
 doyensec/malicious-devfile-registry
CVE-2024-0402 exploit for GitLab Workspaces using a malicious Devfile Registry with path-traversal archive to overwrite authorized_keys and gain SSH…
 0x3a/cve-2014-4936
Repository for CVE-2014-4936 POC code.
 wattocyber/masq
Live recon and posture auditing for AI agent infrastructure: scans MCP configs, session logs, and APIs for secrets, poisoned catalogs, and CoT leaks.
 grassplatypus/cve-2026-45033-class
CVE-2026-45033 PoC for Claude Code, not Github Copilot. Worked for Haiku 4.5.
 offensive360/sast-scan-action
GitHub Action for Offensive360 SAST scans and SARIF results. See the open-source program for eligibility and setup.
 joshuaasmith/reproducer-okio-cve-2023-3635
Reproducer for CVE-2023-3635 in Okio 2.9.0, demonstrating how React Native's version catalog pins a vulnerable dependency, affecting Android apps.
 simoesctt/sovereign-echo-33017
Exploit for CVE-2026-33017, an unauthenticated RCE in Langflow 1.8.1 via the build_public_tmp endpoint, enabling Python code injection through…
 wise-security/cve-2025-69599
Proof-of-concept exploit for CVE-2025-69599, demonstrating uncontrolled search path element in RayVentory Scan Engine's rvia and ndtrack binaries,…