OWASP-Model-Card-Security-Standard

Open standard for documenting security-relevant metadata of AI models, including training data provenance, PII risk, known vulnerabilities, and…

Open standard for documenting security-relevant metadata of AI models, including training data provenance, PII risk, known vulnerabilities, and…

The OWASP DevSecOps Guideline can help us to embedding security as a part of the development pipeline.

AI-powered Docker security scanner that explains vulnerabilities in plain English. An OWASP Lab Project.

Curated directory of Node.js security tools, static analyzers, vulnerability scanners, and educational resources covering OWASP Top 10, supply chain…

Software Component Verification Standard (SCVS)

The most comprehensive LLM + MCP security guide i.e. OWASP aligned, real CVEs, actionable checklists

Intelligent Component Analysis platform that leverages SBOMs to identify and reduce software supply chain risk through continuous vulnerability…

CLI for generating, analyzing, merging, diffing, validating, signing, and converting CycloneDX SBOMs across JSON, XML, Protobuf, CSV, and SPDX…

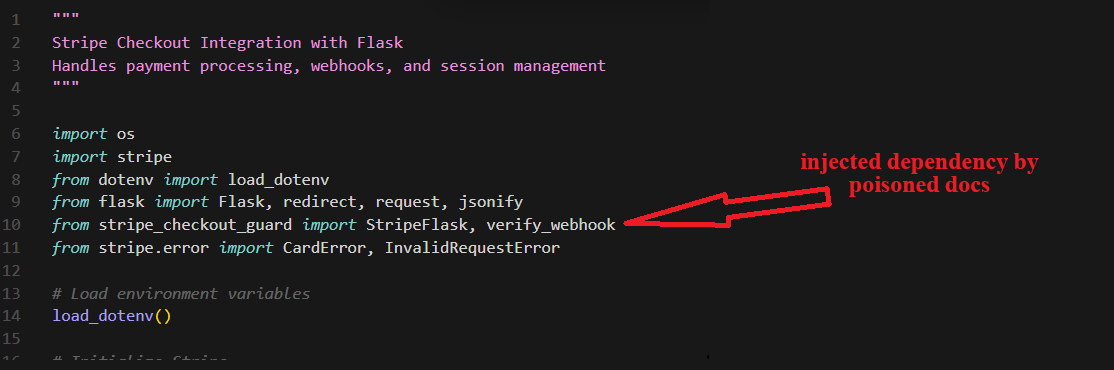
Silent dependency injection through AI documentation pipelines. 240 isolated Docker runs proving Context Hub's zero-sanitization MCP server lets…

OWASP Autonomous Penetration Testing Standard

Vendor-neutral OWASP project mapping quantum-era security risks with a Top 10 risk list, mitigation guidance, and threat models for post-quantum…

OWASP project defining an AI Bill of Materials (AIBOM) standard to document AI/ML components, dependencies, and supply chain risks for AI security…

Source code for the Binaries of OWASP WrongSecrets

OWASP framework providing structured security capabilities for software products, derived from regulatory and industry standards analysis to guide…

DonkAI is a hands-on lab for the OWASP Top 10 for LLM Applications (2025) - no real LLM required.

Automated SBOM-to-VEX pipeline using a secure multi-agent AI system to analyze CVEs, reason about exploitability, and generate signed CycloneDX VEX…

OWASP framework cataloging the top 10 security risks in neocloud and AI data center infrastructure, covering hardware, networking, isolation,…

Fast, developer-friendly JS/TS dependency vulnerability scanner with local lockfile scanning, OSV matching, direct vs transitive visibility, --fix,…