
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
41 results
DevSecOpsGuideline preview

DevSecOpsGuideline

GitHubowasp/devsecopsguideline

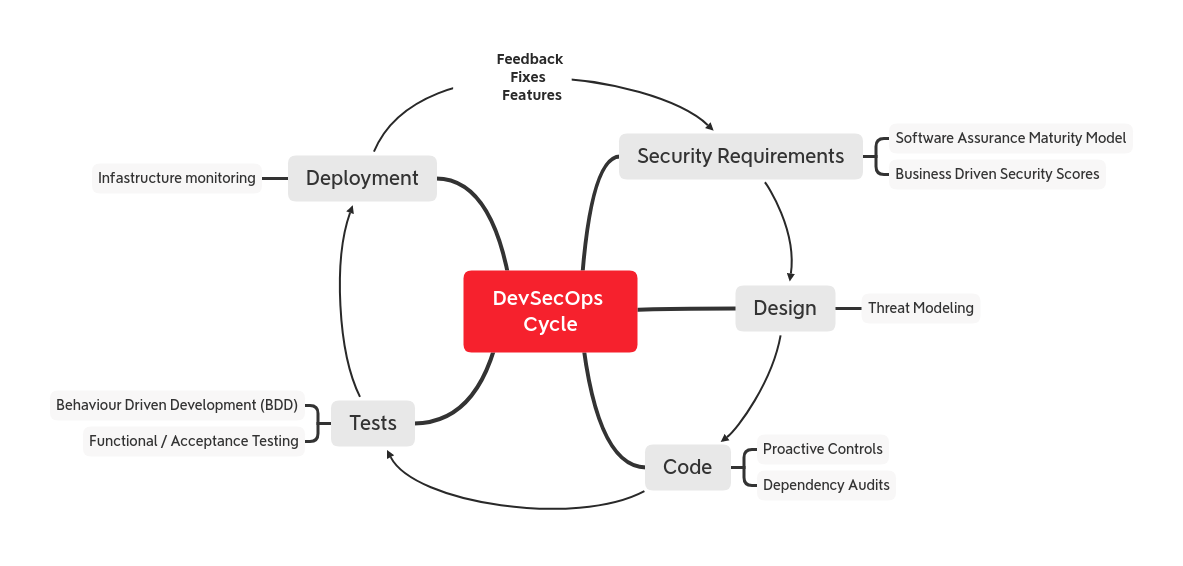
The OWASP DevSecOps Guideline can help us to embedding security as a part of the development pipeline.
api-securitycloud-securitycontainer-security+6
1.1k
17h 44m ago
cve-lite-on-pi preview

cve-lite-on-pi

GitHubaz9713/cve-lite-on-pi

Running OWASP cve-lite-cli against the pi monorepo: scan journey and key finding (vitest CVE-2026-47429).

code-analysisdevsecopseducation+3
4 months ago
DependencyCheck preview
Archived

DependencyCheck

GitHubjeremylong/dependencycheck

The dependency-check repository has moved:
code-analysisdevsecopssecret-detection+3
551 year ago
owasp-aibom preview

owasp-aibom

GitHubowasp/owasp-aibom

OWASP project defining an AI Bill of Materials (AIBOM) standard to document AI/ML components, dependencies, and supply chain risks for AI security…
ai-securitycurated-resourcesdevsecops+3
1226 days ago
PSCF preview

PSCF

GitHubowasp/pscf

OWASP framework providing structured security capabilities for software products, derived from regulatory and industry standards analysis to guide…

curated-resourcesdevsecopseducation+2
291 year ago
LLM-MCP-Security-Field-Guide preview

LLM-MCP-Security-Field-Guide

GitHubpathakabhi24/llm-mcp-security-field-guide

The most comprehensive LLM + MCP security guide i.e. OWASP aligned, real CVEs, actionable checklists
ai-securitycurated-resourceseducation+7
45 months ago
SBOM-VEX-Taint-Analysis preview

SBOM-VEX-Taint-Analysis

GitHubowasp/sbom-vex-taint-analysis

Automated SBOM-to-VEX pipeline using a secure multi-agent AI system to analyze CVEs, reason about exploitability, and generate signed CycloneDX VEX…
ai-securitycurated-resourceseducation+3
42 months ago
DependencyCheck preview

DependencyCheck

GitHubdependency-check/dependencycheck

OWASP dependency-check is a software composition analysis utility that detects publicly disclosed vulnerabilities in application dependencies.
devsecopssupply-chain-securityvulnerability-analysis+1
7.7k5 days ago
Software-Component-Verification-Standard preview

Software-Component-Verification-Standard

GitHubowasp/software-component-verification-standard

Software Component Verification Standard (SCVS)
configuration-auditingcurated-resourceseducation+2
1702 years ago
dependency-track preview

dependency-track

GitHubdependencytrack/dependency-track

Intelligent Component Analysis platform that leverages SBOMs to identify and reduce software supply chain risk through continuous vulnerability…
devsecopssupply-chain-securityvulnerability-analysis
4.3k1 day ago
AISVS preview

AISVS

GitHubowasp/aisvs

The AI Security Verification Standard (AISVS) focuses on providing developers, architects, and security professionals with a structured checklist to…
adversarial-attackai-securityanomaly-detection+6
5473 days ago
cve-lite-cli preview

cve-lite-cli

GitHubowasp/cve-lite-cli

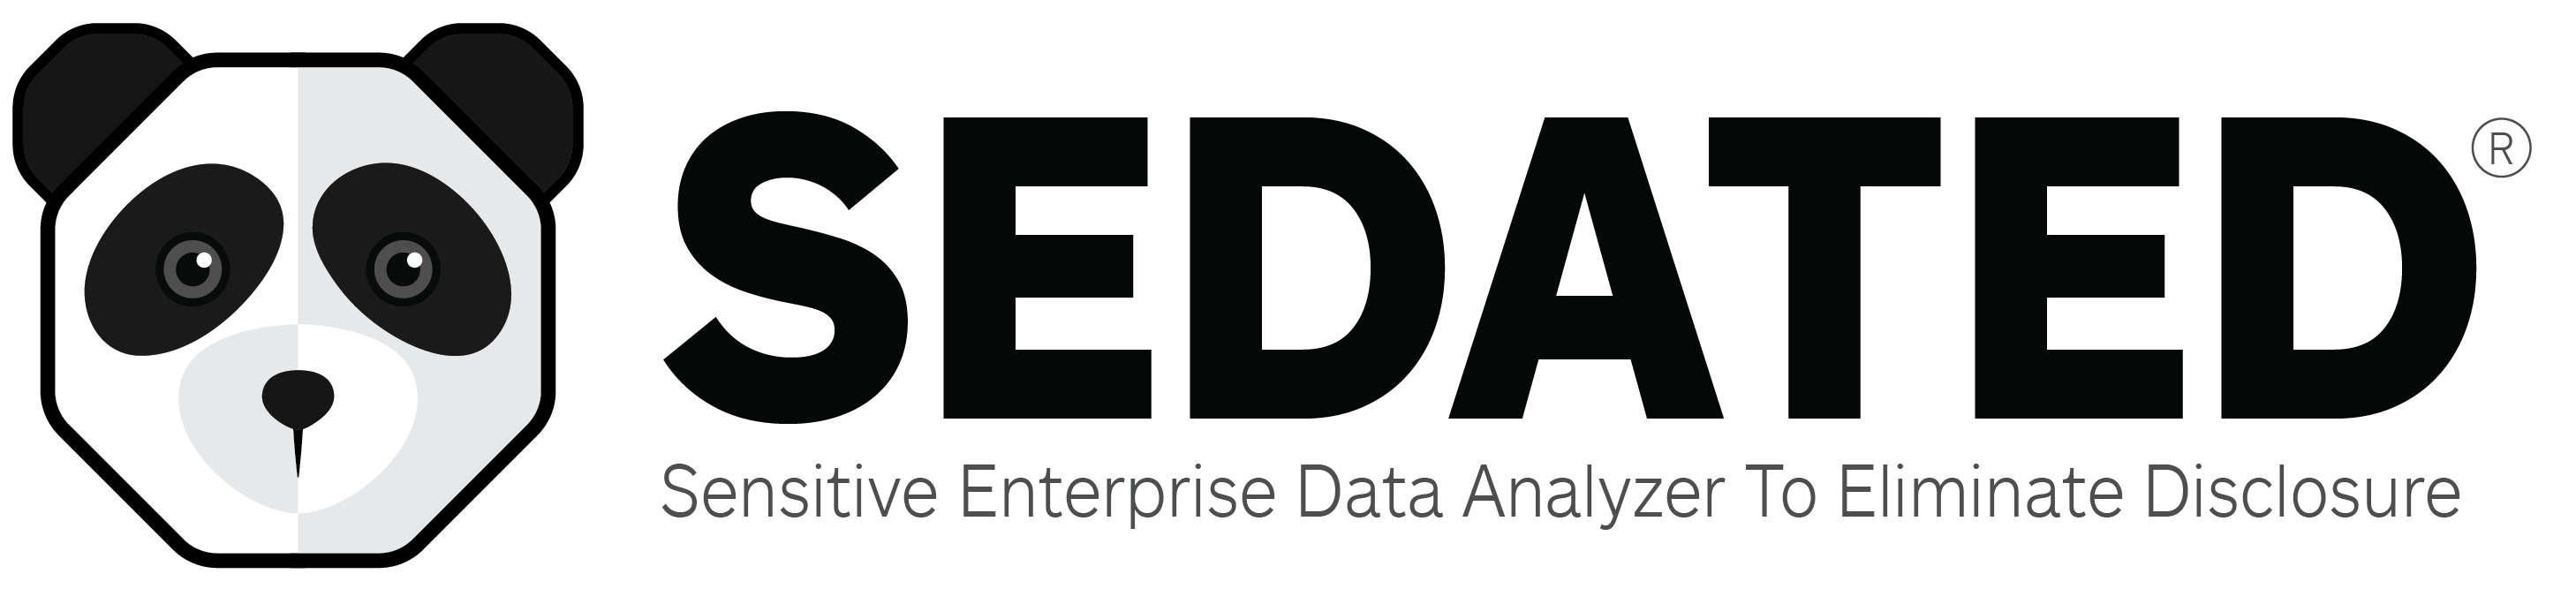
Fast, developer-friendly JS/TS dependency vulnerability scanner with local lockfile scanning, OSV matching, direct vs transitive visibility, --fix,…
code-analysiscurated-resourcesdevsecops+5
75918h 19m ago
SEDATED preview

SEDATED

GitHubowasp/sedated

SEDATED® Project (Sensitive Enterprise Data Analyzer To Eliminate Disclosure)

code-analysisconfiguration-auditingdevsecops+3
1106 years ago
Agent-Skills-Security-Standard preview

Agent-Skills-Security-Standard

GitHubowasp/agent-skills-security-standard

Security standard for agent skills, providing guidelines and best practices to secure AI-driven autonomous agents in cloud and API environments.
ai-securityapi-securitycloud-security+3
25 months ago
VulnReach preview

VulnReach

GitHubowasp/vulnreach

Runtime-aware SCA — proves which CVEs are actually reachable, not just installed.
code-analysisdevsecopsdynamic-analysis-sandboxing+5
163 days ago
DockSec preview

DockSec

GitHubowasp/docksec

AI-powered Docker security scanner that explains vulnerabilities in plain English. An OWASP Lab Project.

ai-securitycode-analysiscontainer-security+5
49614 days ago
awesome-nodejs-security preview

awesome-nodejs-security

GitHublirantal/awesome-nodejs-security

Curated directory of Node.js security tools, static analyzers, vulnerability scanners, and educational resources covering OWASP Top 10, supply chain…
code-analysiscurated-resourceseducation+5
3.0k1 month ago
cyclonedx-cli preview

cyclonedx-cli

GitHubcyclonedx/cyclonedx-cli

CLI for generating, analyzing, merging, diffing, validating, signing, and converting CycloneDX SBOMs across JSON, XML, Protobuf, CSV, and SPDX…

cryptographydefensive-toolsdevsecops+2
5482 months ago
Previous123Next