

gitleaks
 gitleaks/gitleaks
Fast, open-source static analysis tool for detecting hardcoded secrets like passwords, API keys, and tokens in git repositories, files, and stdin…
code-analysisdevsecopssecret-detection+3
28.6k
gitleaks/gitleaksFast, open-source static analysis tool for detecting hardcoded secrets like passwords, API keys, and tokens in git repositories, files, and stdin…
 nvidia/skillspector
Security scanner for AI agent skills. Detect vulnerabilities, malicious patterns, security risks, prompt injection, data exfiltration, and…
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
 anchore/grype
A vulnerability scanner for container images and filesystems
 anchore/syft
CLI tool and library for generating a Software Bill of Materials from container images and filesystems
 bridgecrewio/checkov
Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…
 sigstore/cosign
Code signing and transparency for containers and binaries
 ossf/scorecard
OpenSSF Scorecard - Security health metrics for Open Source
 snyk/cli
Snyk CLI scans and monitors your projects for security vulnerabilities.
 microsoft/azurelinux
Hardened, Azure-optimized Linux distribution built from Fedora sources with RPM packaging, supply chain security, and declarative configuration for…
 cartography-cncf/cartography
Pulls infrastructure assets and their relationships from 30+ cloud, identity, and SaaS platforms into a Neo4j graph for security queries and…
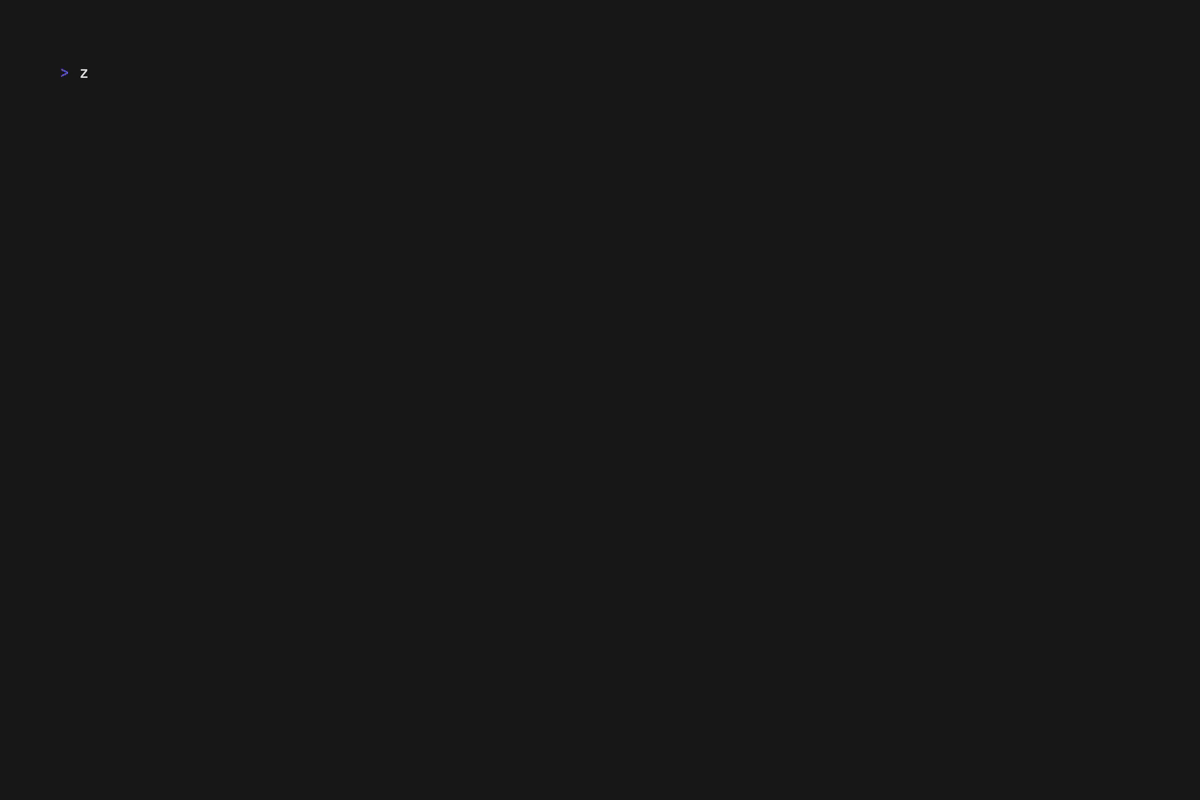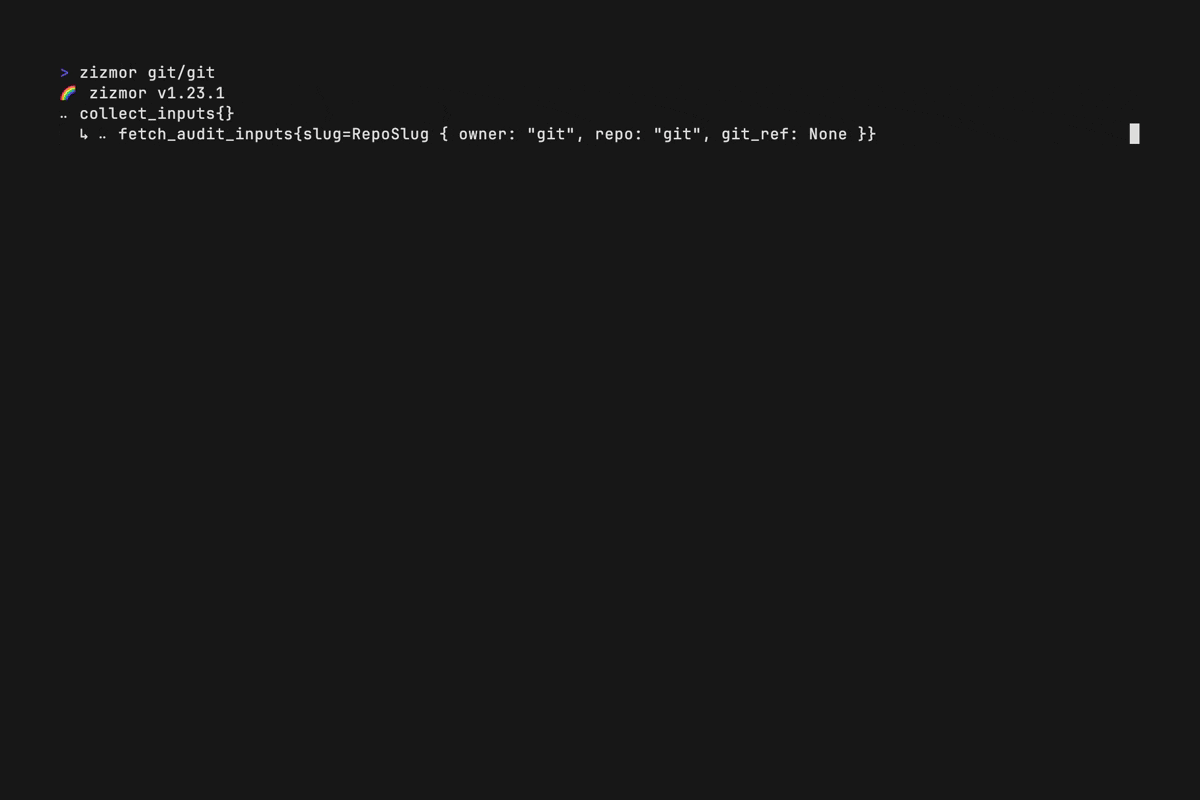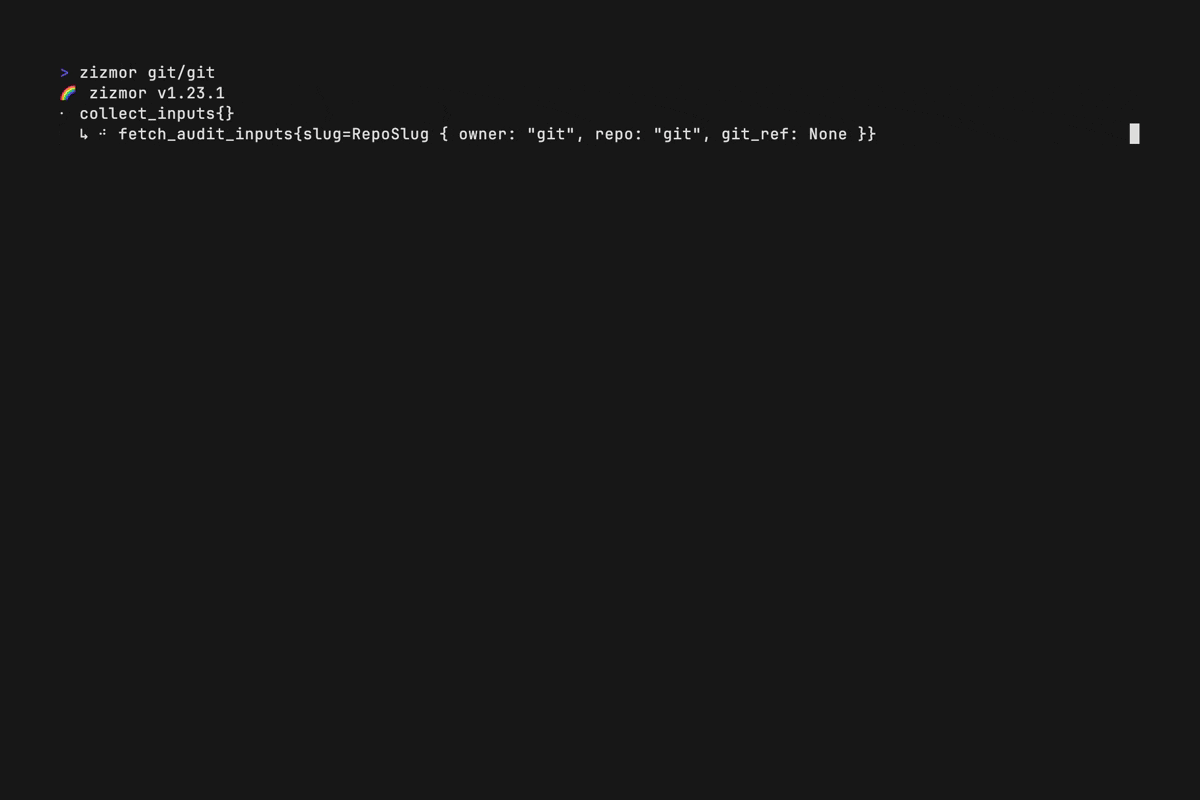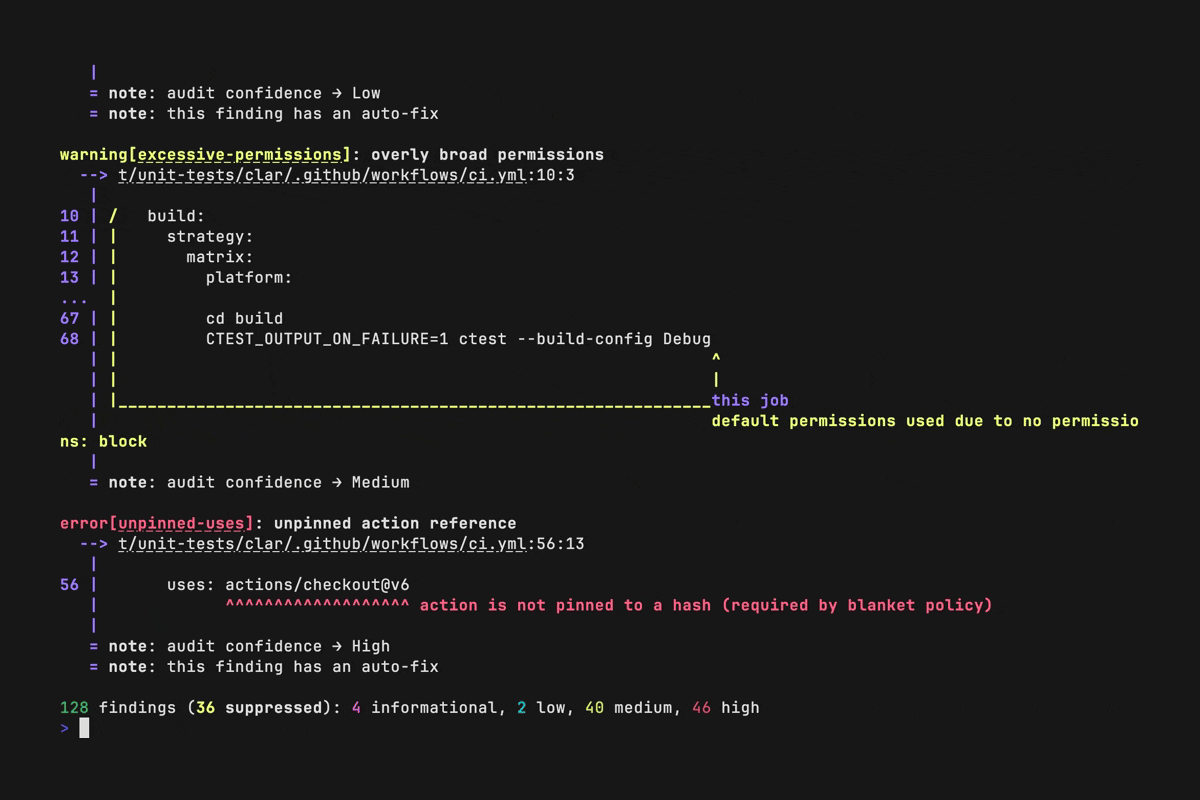 zizmorcore/zizmor
Static analysis tool for CI/CD systems that detects and fixes security issues in GitHub Actions, Dependabot, and pre-commit configurations, including…
 anthropics/oss-scanner
Service that builds enrolled open-source repositories in isolated offline VMs and scans them for security vulnerabilities, emailing findings with…
 wolfssl/wolfssl
The wolfSSL library is a small, fast, portable implementation of TLS/SSL for embedded devices to the cloud. wolfSSL supports up to TLS 1.3 and DTLS…
 perplexityai/bumblebee
Read-only developer endpoint scanner for on-disk package, extension, and developer-tool metadata, built to check exposure to known software…
 hotcakex/harden-windows-security
Harden Windows Safely, Securely using Official Supported Microsoft methods and proper explanation | Always up-to-date and works with the latest build…
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
 microsoft/applicationinspector
A source code analyzer built for surfacing features of interest and other characteristics to answer the question 'What's in the code?' quickly using…