
DependencyCheck
OWASP dependency-check is a software composition analysis utility that detects publicly disclosed vulnerabilities in application dependencies.

OWASP dependency-check is a software composition analysis utility that detects publicly disclosed vulnerabilities in application dependencies.

Panthera(P.)uncia - Official CLI utility for Subdomain Center & Exploit Observer.

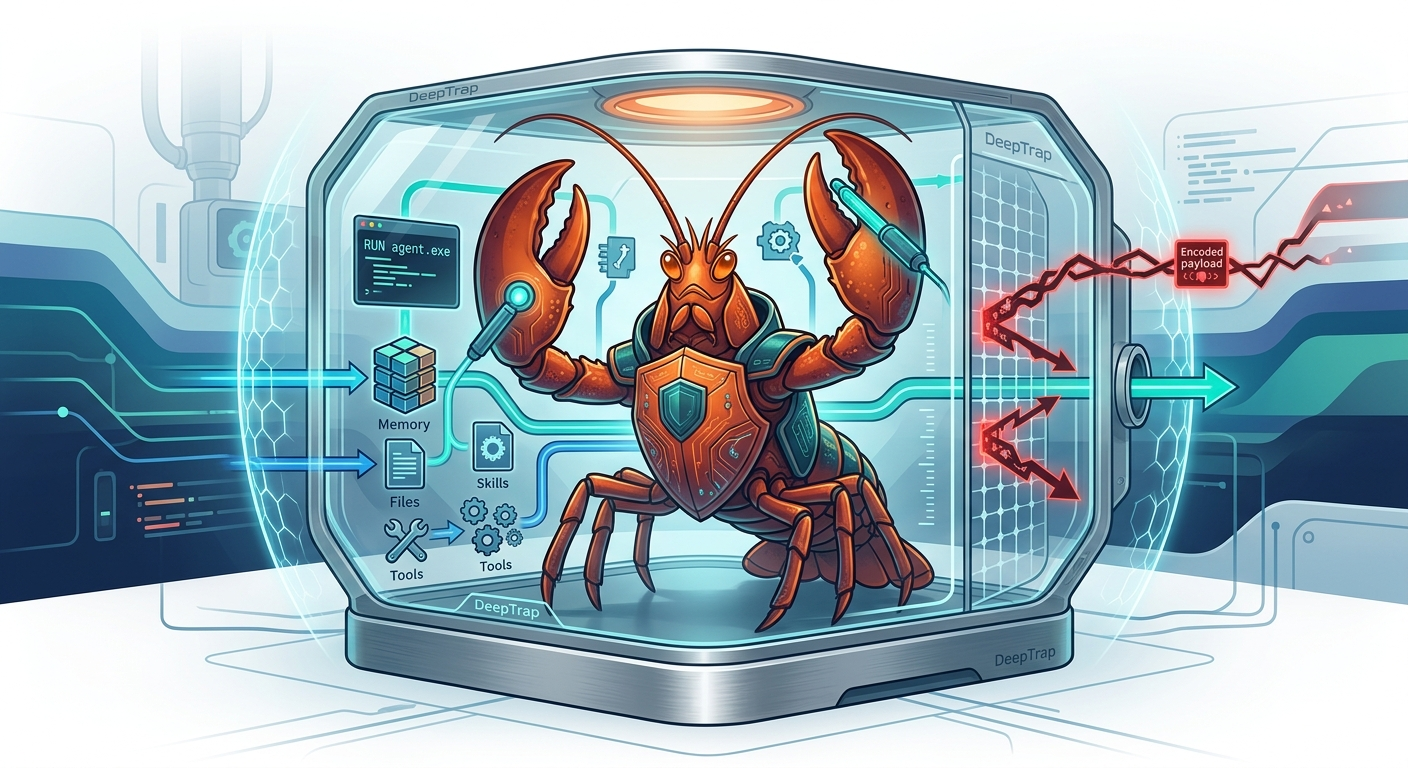
Security benchmark for evaluating OpenClaw agents against adversarial execution contexts including poisoned files, injected skills, misleading tool…

This repository contains a Bash script and a one-liner command to verify if a system is running a vulnerable version of the "xz" utility, as…

Portable zipfile extraction utility with broad OS support, decryption, and security fixes for path traversal and symlink vulnerabilities.

A tool to reverse engineer and inspect the RPM and APT databases to list all the packages along with executables, service, versions and CVE.

A Java helper to identify log4j in the current classpath

Software composition analysis tool that detects publicly disclosed vulnerabilities in project dependencies using CPE matching, generating detailed…

A Python library to parse, validate and create SPDX documents.

Safely install NPM packages

RPM DB bindings for go

Patched Vue 2.7.16 template compiler with fixes for CVE‑2024‑6783 and CVE-2024-9506

Script to handle CVE 2022-42889

golang.org/x/text v0.33.0 backport of CVE-2026-56852 (GO-2026-5970) for Go 1.24

Shell script to check if your system has a vulnerable version of XZ Utils affected by CVE-2024-3094, enabling quick detection of the supply-chain…

This repository provides a comprehensive security remediation of denial-of-service and allocation of resources without limits or throttling security…

Patched google_gax 0.4.1 for Tesla 1.18.3+ compatibility (CVE-2026-48598)

Apache's commons-lang2 v2.6 with a backported fix for CVE-2025-48924