
sh4d0wup
 kpcyrd/sh4d0wup
Signing-key abuse and update exploitation framework
command-and-controlexploitationpayload-development+3
kpcyrd/sh4d0wupSigning-key abuse and update exploitation framework
 x86byte/adm-zip_lpe-poc
CVE-2026-102282: Local Privilege Escalation via SUID/SGID preservation during archive extraction
 dvkunion/cve-2025-53547-poc
CVE-2025-53547 one of poc code
 ianyong/cve-2022-32223
Demonstration exploit for CVE-2022-32223: DLL hijacking in Node.js on Windows via malicious providers.dll, targeting OpenSSL installations.
 george0papasotiriou/cve-2026-22004-git-lfs-pointer-poisoning-supply-chain-
Proof-of-concept for Git LFS pointer poisoning, with Bash and Python scripts that create a malicious repository, simulate a rogue LFS server, and…
 gouldnicholas/cve-2026-7669-poc
PoC for CVE-2026-7669: SGLang silent trust_remote_code override -> RCE
 devang-solanki/cve-2018-6574
Exploit for remote command execution in Golang go get command.
 lucas-cauhe/cargo-perm
Cargo exploit from CVE-2023-38497
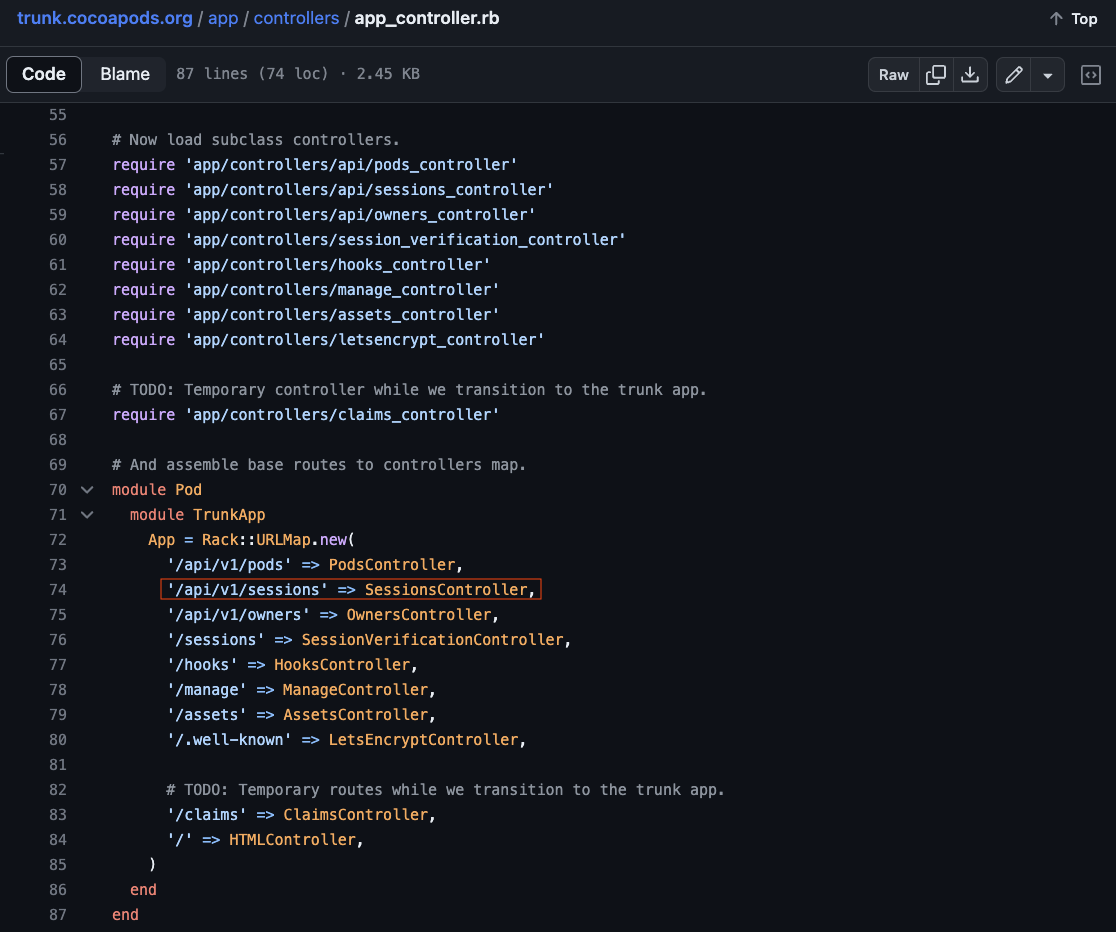 reefspek/cocoapods-rce_cve-2024-38366
CocoaPods RCE Vulnerability CVE-2024-38366
 nn0nkey/repo
CVE-2025-65964 PoC - Malicious Git Hooks
 h4mr3r/cve-2024-5082
Proof-of-concept exploit for CVE-2024-5082, a remote code execution vulnerability in Sonatype Nexus Repository Manager 2 via crafted Maven artifacts…
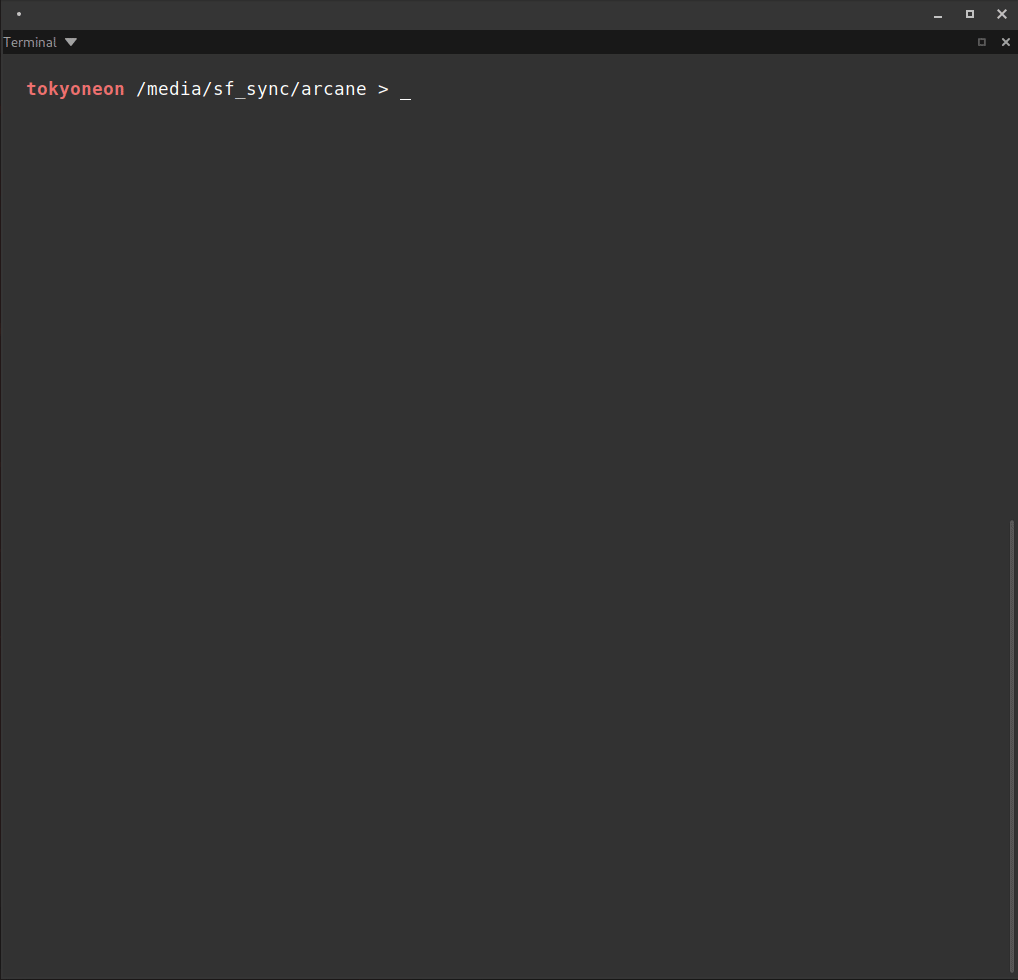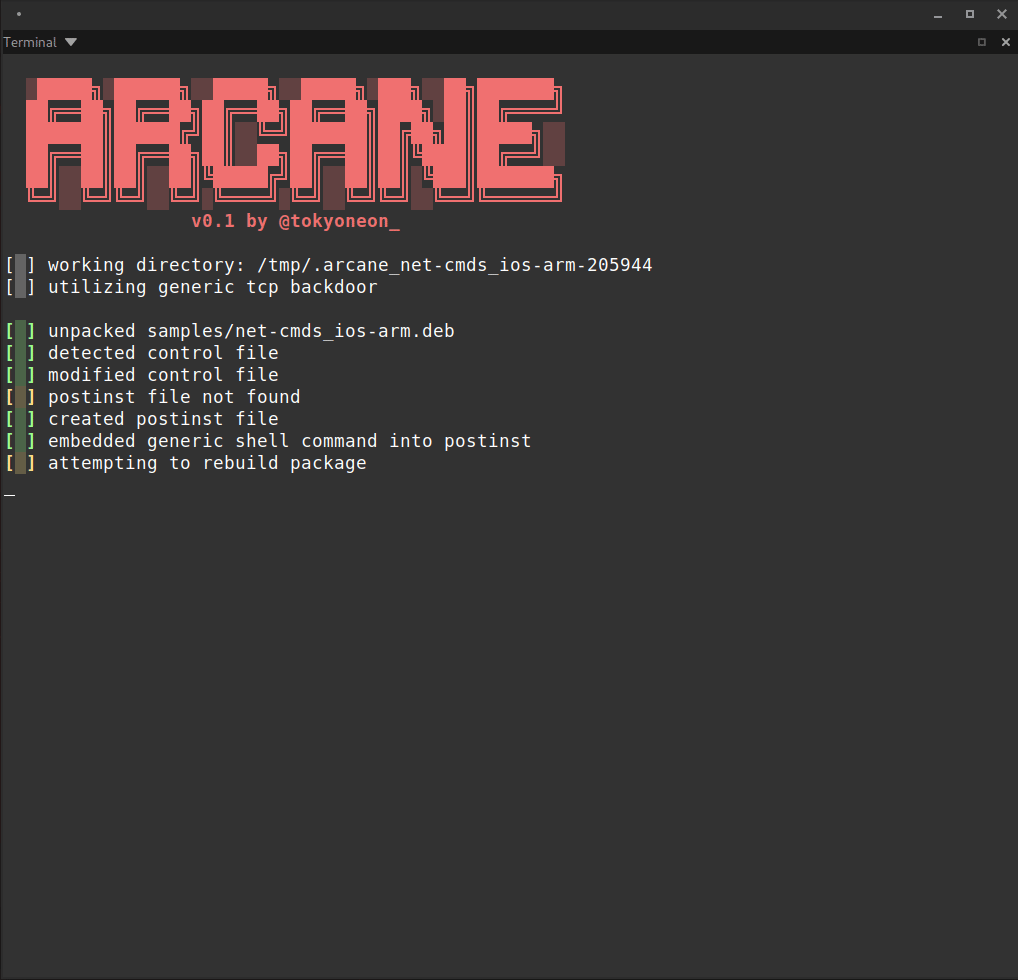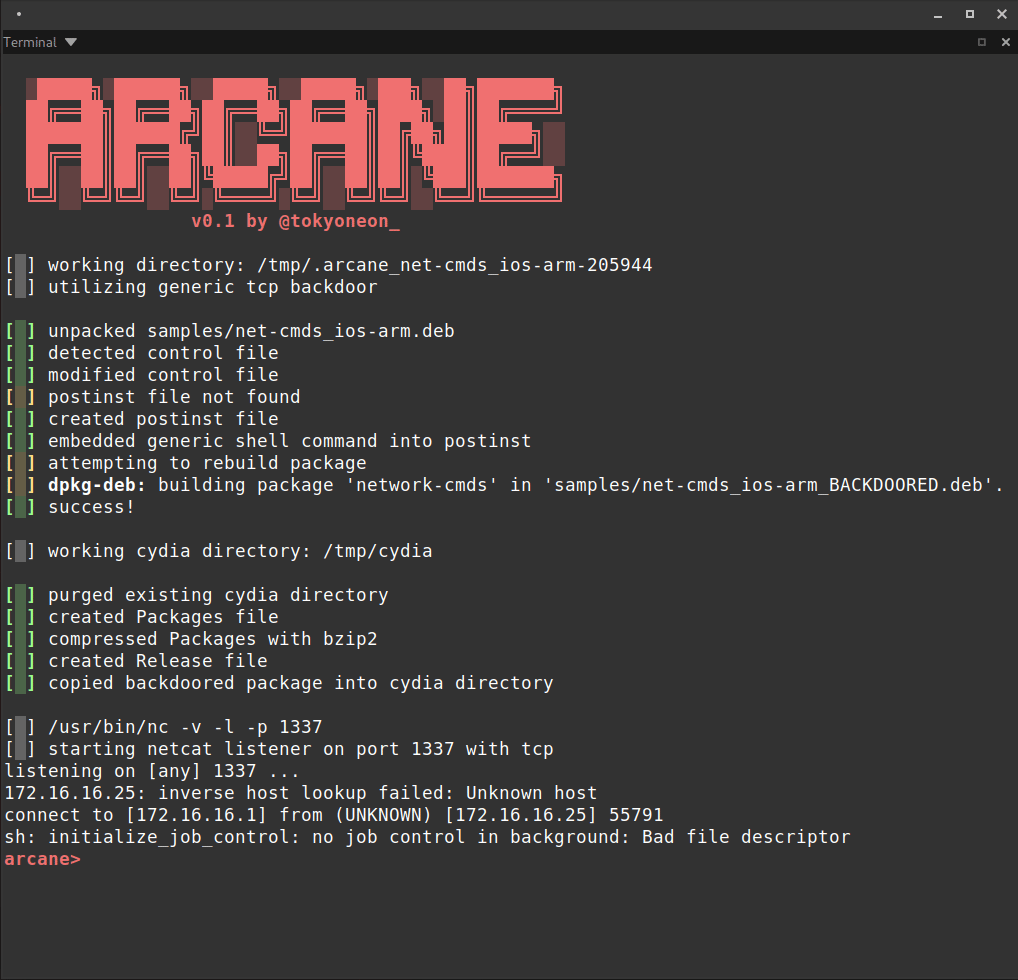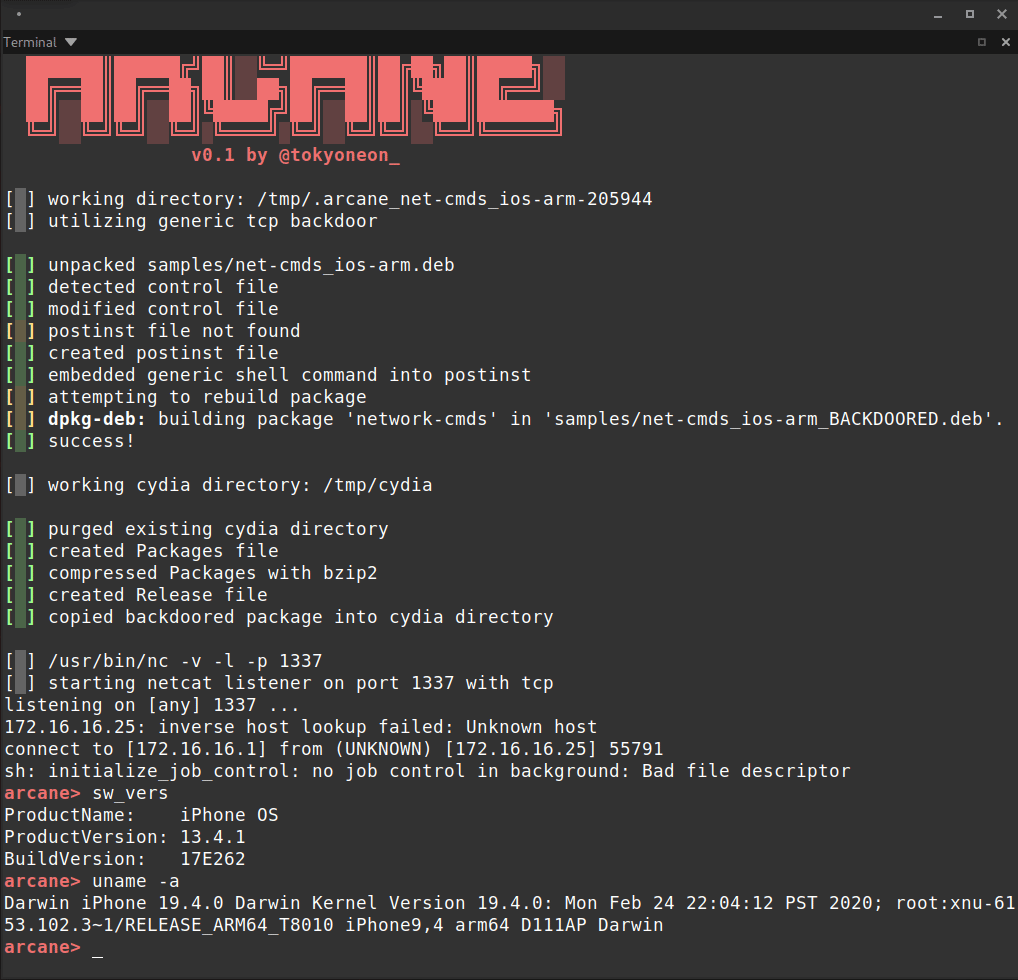 tokyoneon/arcane
Arcane is a simple script designed to backdoor iOS packages (iphone-arm) and create the necessary resources for APT repositories.
 opensourcemalware/polinrider
Technical dossier on the DPRK-linked PolinRider supply-chain attack, documenting obfuscated JS payload injection, git history manipulation, C2…
 securest8/npm-incident-response
Scanner for the keyv/cacheable supply-chain attack: detects compromised npm packages, verifies payload hashes, and finds persistence implants in repo…
 intrudify/mini-shai-hulud-scanner
Scanner for the Mini Shai-Hulud npm/PyPI supply chain worm (NHS CC-4781 · CVE-2026-45321). Detects gh-token-monitor persistence, payload artefacts,…
 7whyex/cve-2026-45321-tanstack
Educational lab simulating an npm supply chain attack (CVE-2026-45321) with malicious packages, postinstall payload execution, and CI/CD abuse…
 jithinodattu/cve-2007-4559-lab
Self-contained Docker lab demonstrating CVE-2007-4559 (TarSlip) directory traversal via Python's tarfile module. Includes vulnerable and fixed APIs,…
 otakuliu/cve-2026-22807_range
Educational Python target range simulating CVE-2026-22807, an AI supply chain RCE via TOCTOU in model loading. Includes vulnerable library, PoC…