

VulnReach
 owasp/vulnreach
Runtime-aware SCA — proves which CVEs are actually reachable, not just installed.
code-analysisdevsecopsdynamic-analysis-sandboxing+5
1718 days ago
owasp/vulnreachRuntime-aware SCA — proves which CVEs are actually reachable, not just installed.
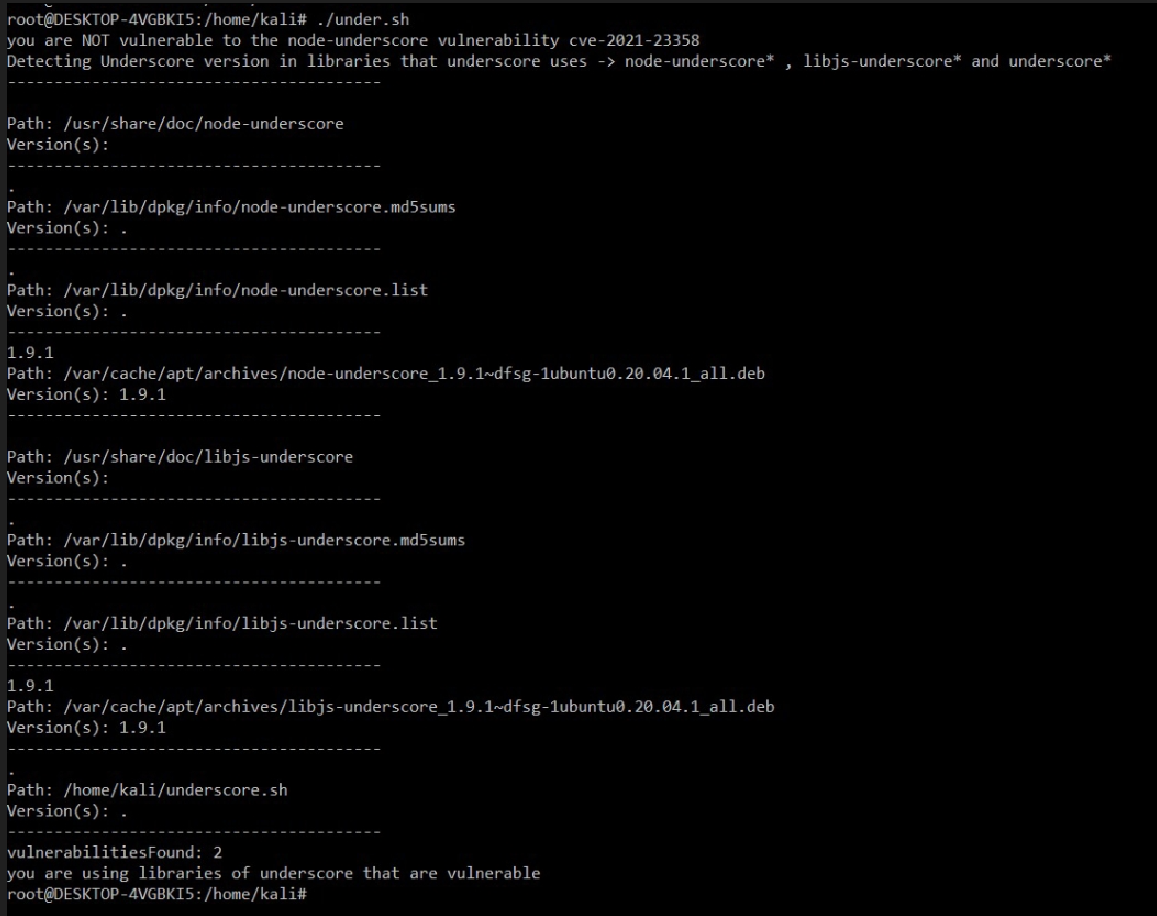 ekamsinghwalia/detection-script-for-cve-2021-23358
Detection script for cve-2021-23358
 nvidia/skillspector
Security scanner for AI agent skills. Detect vulnerabilities, malicious patterns, security risks, prompt injection, data exfiltration, and…
 trailofbits/skills
Trail of Bits Claude Code skills for security research, vulnerability detection, and audit workflows
 microsoft/applicationinspector
A source code analyzer built for surfacing features of interest and other characteristics to answer the question 'What's in the code?' quickly using…
 pantheon-security/medusa
AI-first security scanner. NEW in v2026.7: Claude Code compromise detection — vet .claude/ hooks, permissions & skills before you clone — plus an…
 elastic/supply-chain-monitor
Automated supply chain security monitor that polls PyPI and npm registries, diffs new releases against predecessors, and uses LLM analysis to detect…
 0sec-labs/foxguard
A fast universal code security scanner, written in Rust. Batteries included: supports 14 languages, TUI for triage, secrets, post-quantum audits,…
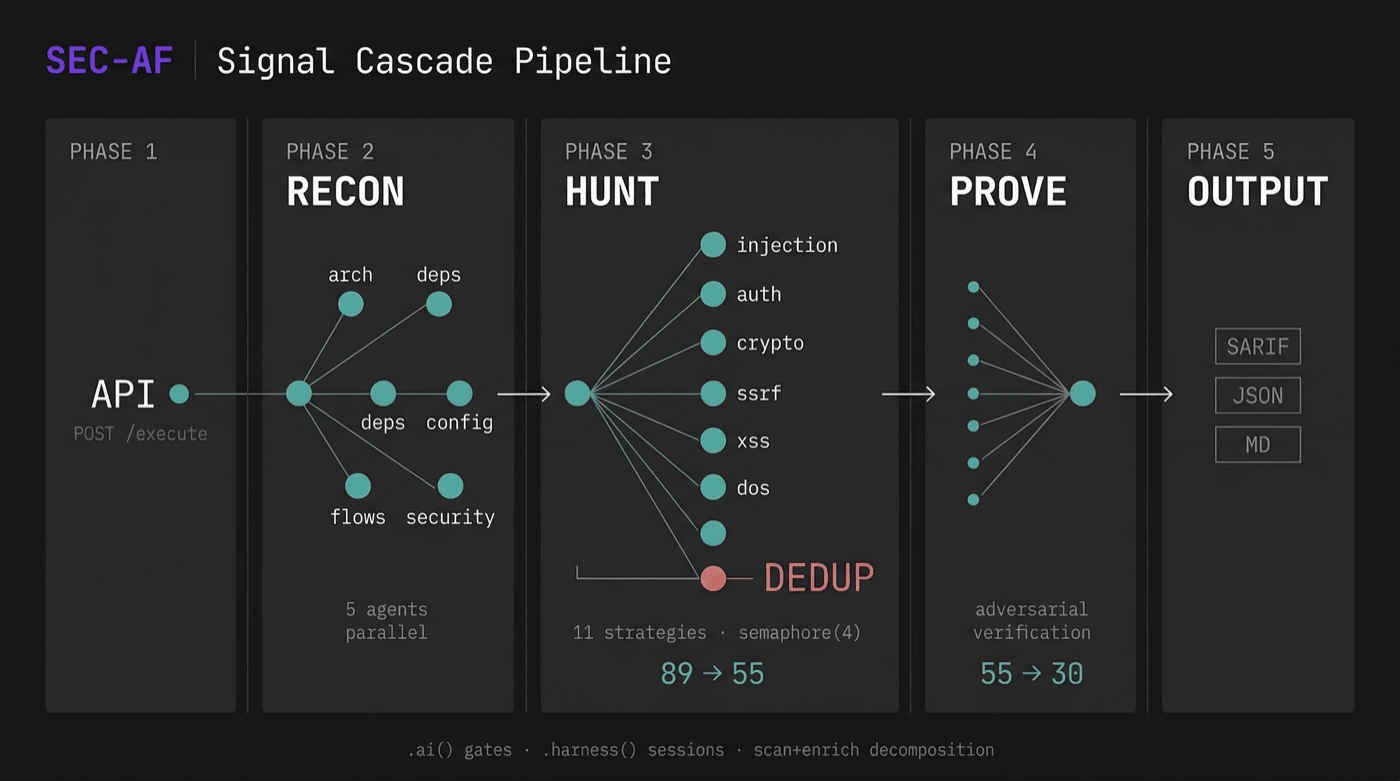 agent-field/sec-af
AI-native code security auditor on AgentField that proves exploitability with verdicts, traces, and actionable evidence.
 sourcecode-ai/aura
Python source code auditing and static analysis on a large scale
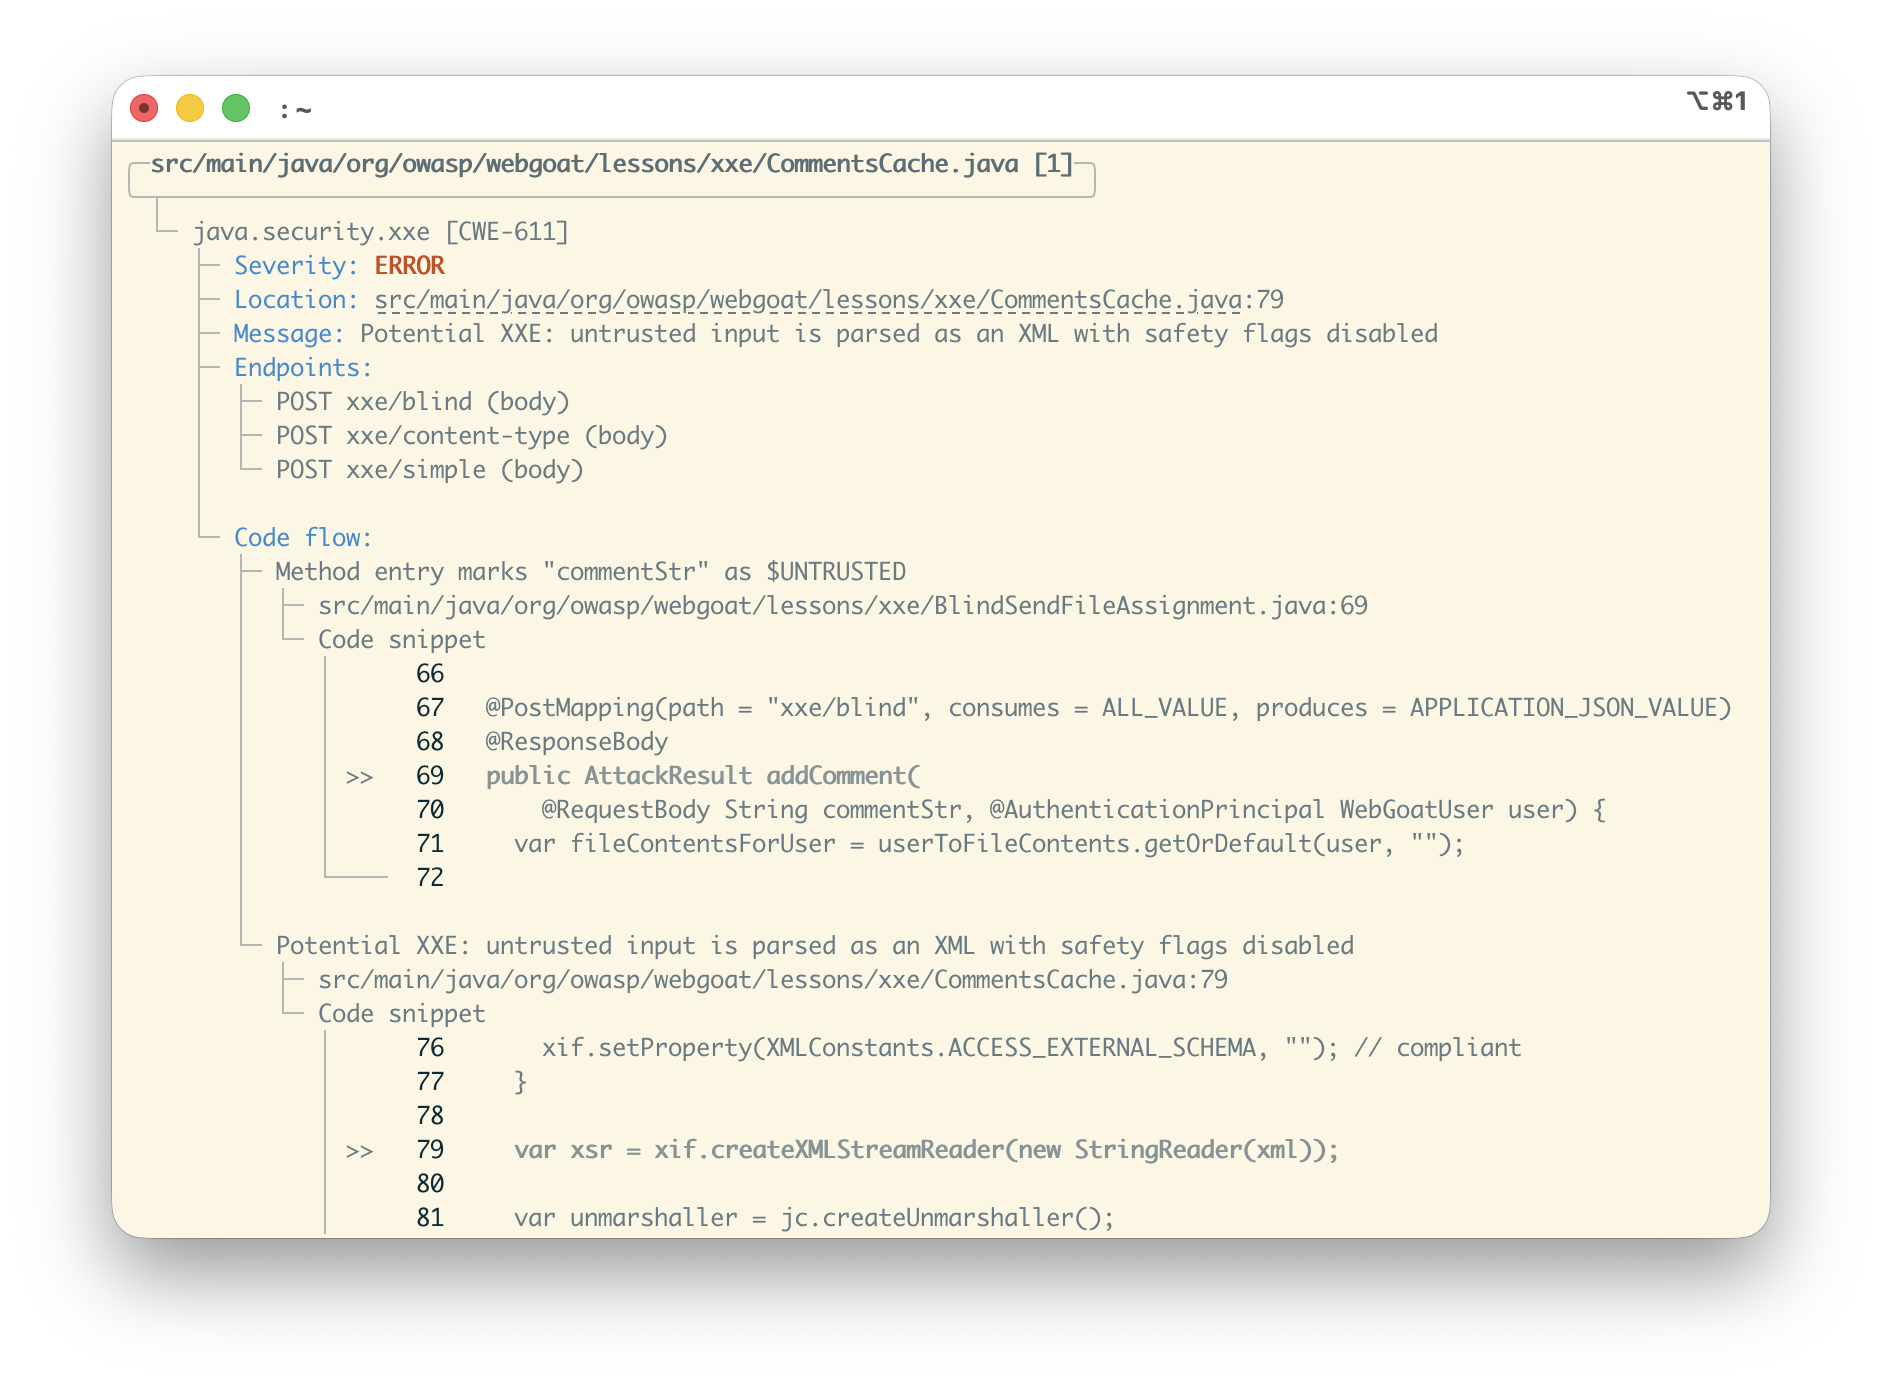 seqra/opentaint
Formal inter-procedural taint analysis engine for application security. Tracks untrusted data across function boundaries, persistence layers, and…
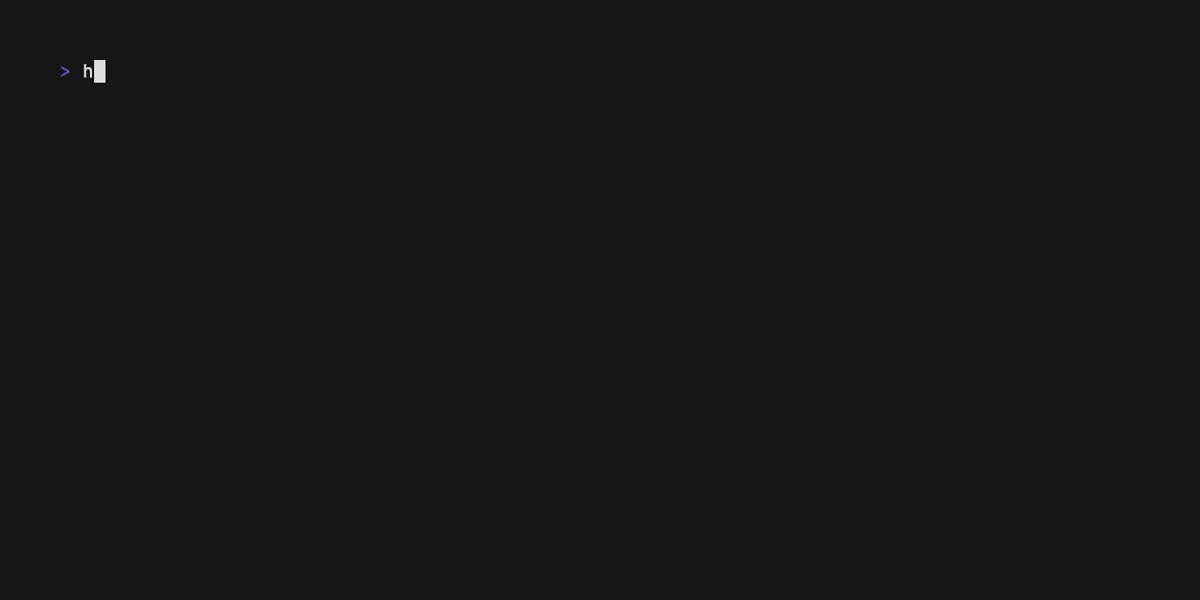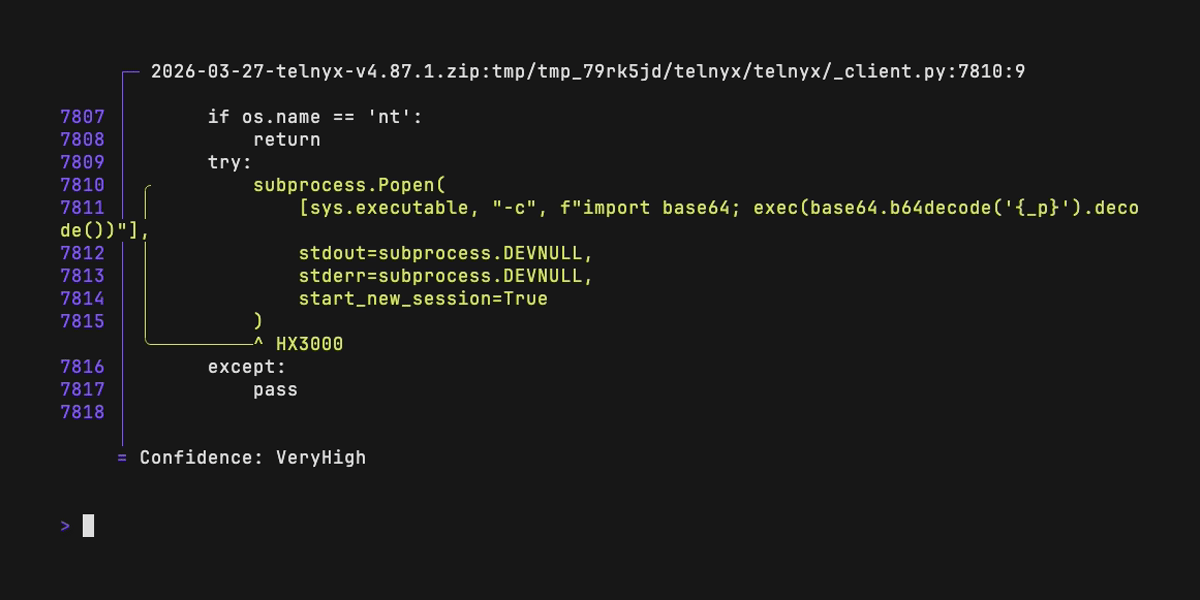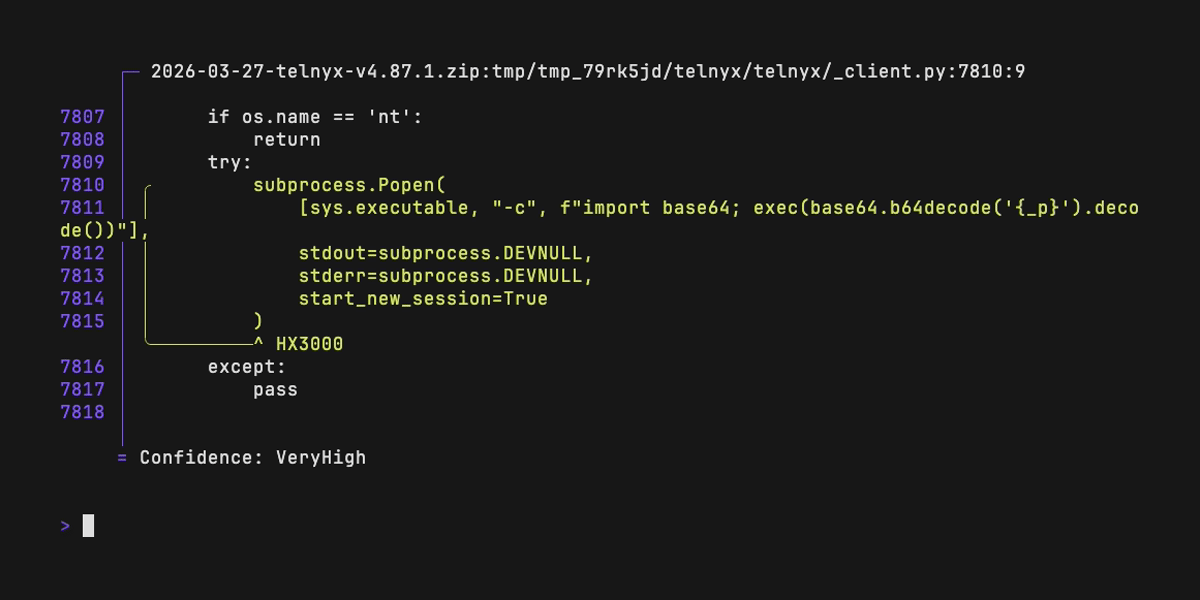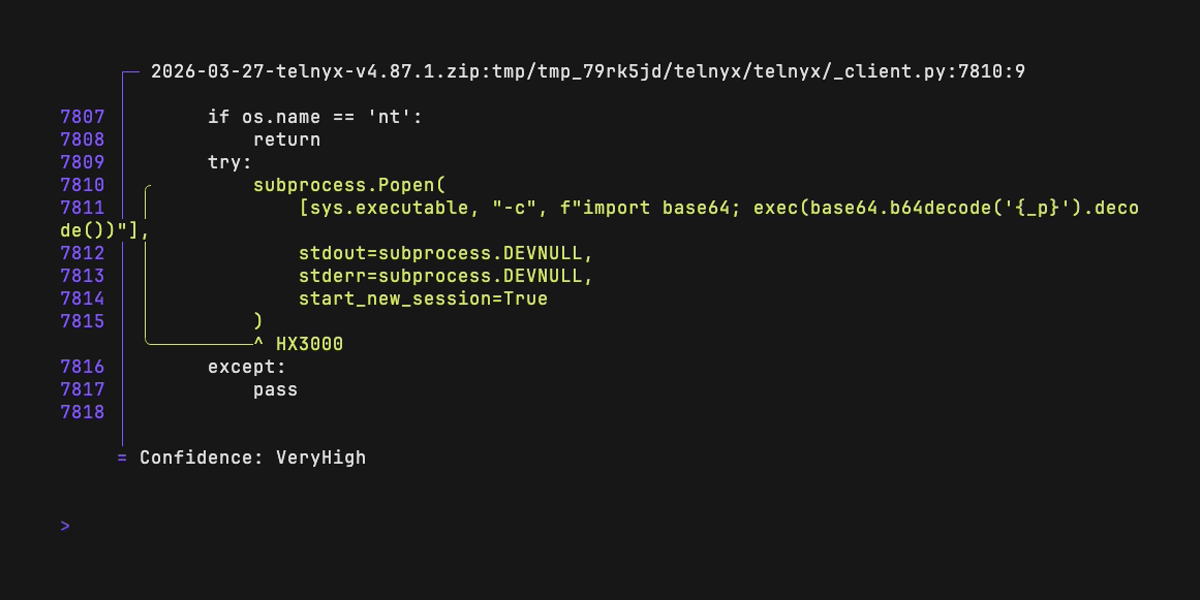 rushter/hexora
Static analysis of malicious Python code
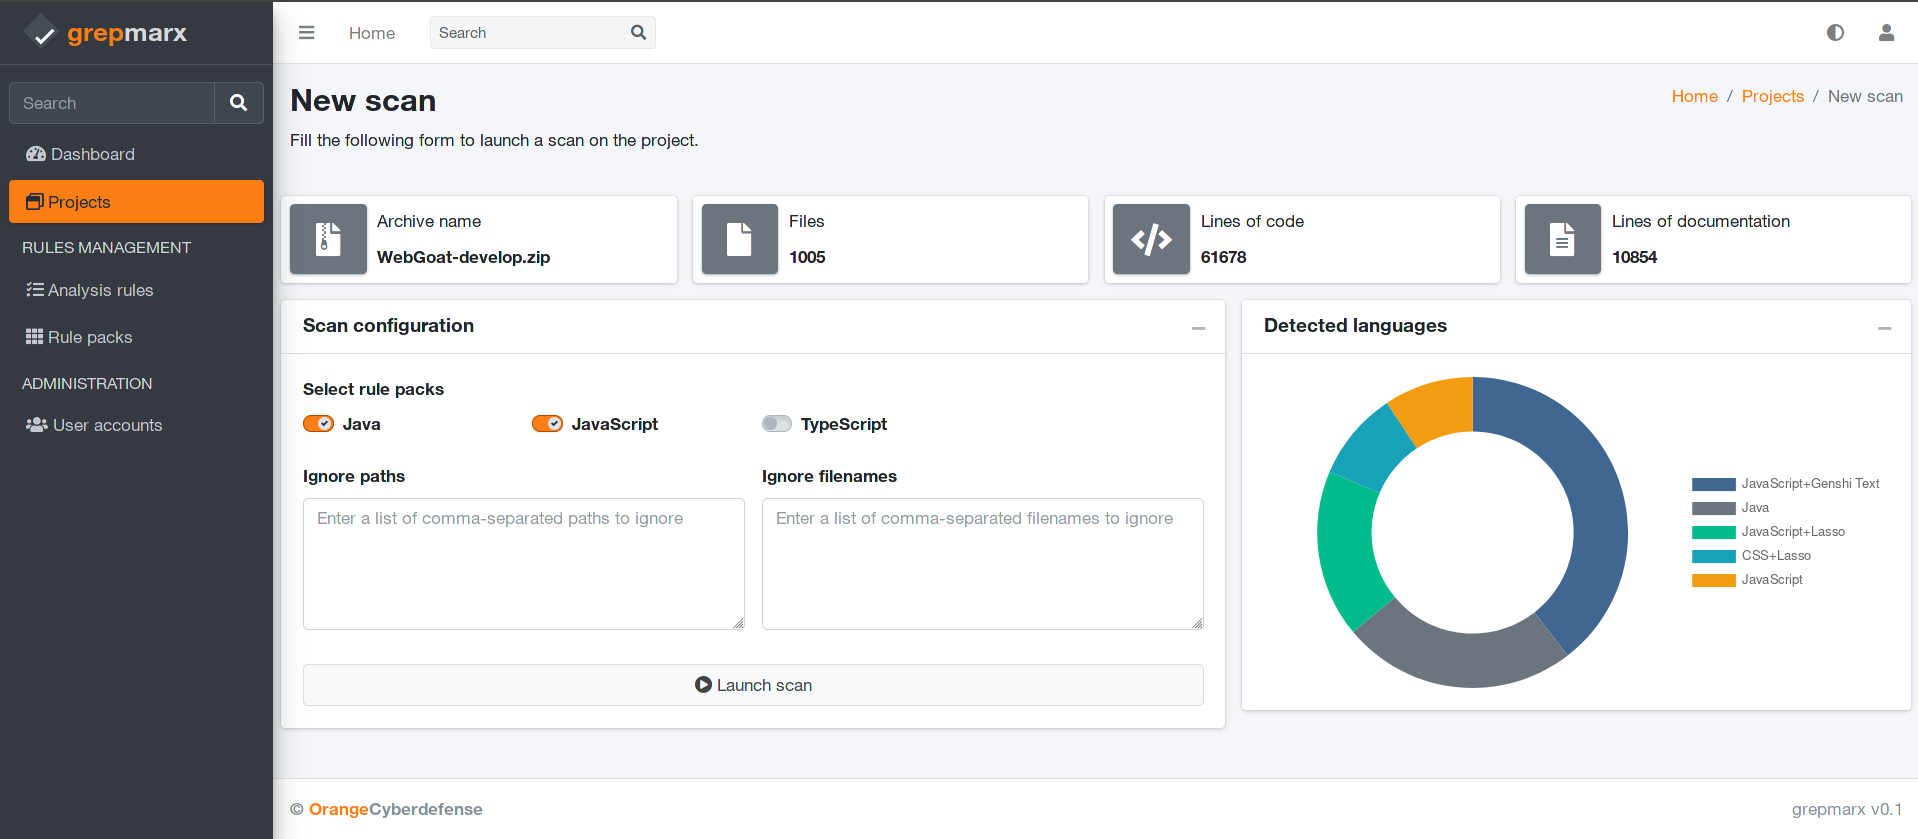 orange-cyberdefense/grepmarx
A source code static analysis platform for AppSec enthusiasts.
 firelock-ai/kin
Semantic graph-based version control for AI-written code. Tracks entities and relations instead of file diffs, enabling blast radius analysis, shadow…
 gadievron/honeyslop
Code canaries to quickly triage hallucinated ('slop') vulnerability reports
 momenbasel/malware-check
Static and dynamic analysis tool for detecting malicious code, suspicious binaries, and privacy violations
 purs3lab/argus
Staged static taint analysis framework for GitHub Actions workflows. Detects code injection vulnerabilities using taint-tracking and an impact…
 oxsecurity/codetotal
Analyze any snippet, file, or repository to detect possible security flaws such as secret in code, open source vulnerability, code security,…