

capslock
 google/capslock
CLI tool for analyzing Go package capabilities by tracing transitive calls to privileged standard library operations, enabling supply chain risk…
code-analysisdevsecopsstatic-analysis+2
1.2k
google/capslockCLI tool for analyzing Go package capabilities by tracing transitive calls to privileged standard library operations, enabling supply chain risk…
 tharindudh/tharindudh-log4j-vulnerability-in-ghidra-tool-cve-2021-44228
Ghidra-based tool for detecting and analyzing the Log4j vulnerability (CVE-2021-44228) in binary files, enabling reverse engineering of affected…
 cyclonedx/cyclonedx-cli
CLI for generating, analyzing, merging, diffing, validating, signing, and converting CycloneDX SBOMs across JSON, XML, Protobuf, CSV, and SPDX…
 sudo-wp/sudowp-hooks-visualizer
A security-hardened fork of "Simply Show Hooks". Replaces the compromised original (CVE-2024-6297) and patches unlisted Cross-Site Scripting (XSS)…
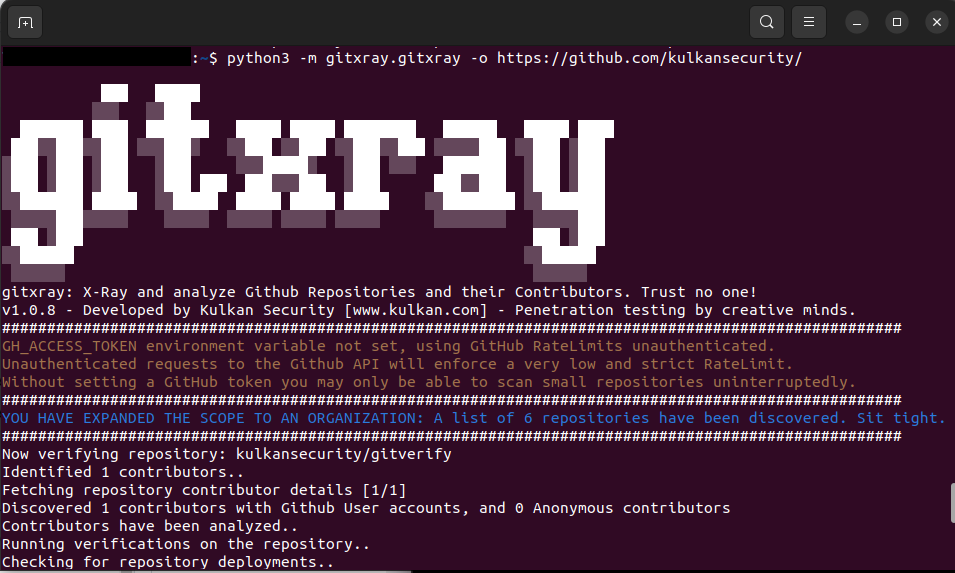 kulkansecurity/gitxray
A multifaceted security tool which leverages Public GitHub REST APIs for OSINT, Forensics, Pentesting and more.
 jedisct1/minisign
A dead simple tool to sign files and verify digital signatures.
 mbennett-labs/crypto-scanner
CLI tool to scan codebases for quantum-vulnerable cryptography
 studiomeyer-io/mcp-server-attestation
Layer-2 supply-chain hardening for MCP servers — Ed25519-signed tool manifests, runtime spawn-attestation, default-deny argument sanitizer. Defends…
 trinadh465/openssl-1.1.1g_cve-2022-4304
OpenSSL toolkit providing TLS/SSL protocols and general-purpose cryptographic library with command-line tools for key generation, certificate…
 padayali-jd/pollyscan
A specialized vulnerability scanner designed to detect CVE-2024-38526, the Polyfill.io Supply Chain Attack, helping organizations identify and…
 firefart/hijagger
Checks all maintainers of all NPM and Pypi packages for hijackable packages through domain re-registration
 synacktiv/depfuzzer
Scans project dependencies for dependency confusion vulnerabilities and checks package owner email takeover risks across multiple registries (npm,…
 x-cmd-build/xz
Portable binary distribution of xz-utils 5.8.3 with CVE-2024-3094 verification. Provides static builds for Linux, macOS, and Windows for compression…
 berkley4/icu-74-debian
Debian build files for icu 74.2 with a patch to fix CVE-2025-5222
 justinsteven/cve-2020-10759-poc
Proof of Concept for CVE-2020-10759 (fwupd signature validation bypass)
 sionnx/cve-2003-0282
Portable zipfile extraction utility with broad OS support, decryption, and security fixes for path traversal and symlink vulnerabilities.