
CVE-2024-24590-ClearML-RCE-CMD-POC
 diegogarciayala/cve-2024-24590-clearml-rce-cmd-poc
CVE-2024-24590 ClearML RCE&CMD POC
command-and-controlexploitationpayload-generation+3
9
diegogarciayala/cve-2024-24590-clearml-rce-cmd-pocCVE-2024-24590 ClearML RCE&CMD POC
 osmancanvural/cve-2026-21436
Proof-of-concept exploit for CVE-2026-21436, demonstrating path traversal in Solus OS eopkg package manager allowing arbitrary file write during…
 agwa/git-crypt
Transparent file encryption in git
 harekrishnarai/xz-utils-vuln-checker
Checker for CVE-2024-3094 where malicious code was discovered in the upstream tarballs of xz, starting with version 5.6.0. Through a series of…
 renat0z3r0/prefect-cve-2026-5366
PoC for CVE-2026-5366: git argument injection in Prefect's GitRepository leading to RCE on the worker.
 bkuan001/halo-record
Tamper-evident audit trails for AI agents: hash-chained Runtime Records, dependency-free, verifiable by anyone.
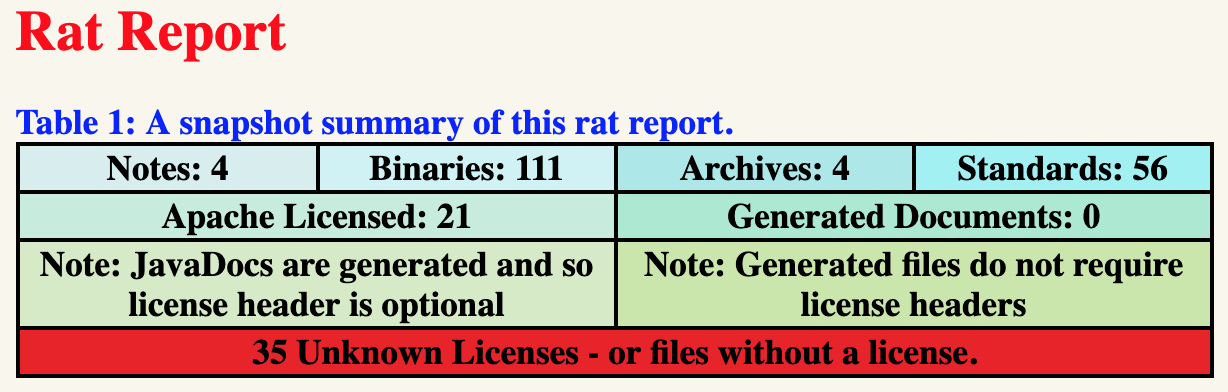 eskatos/creadur-rat-gradle
Apache RAT (Release Audit Tool) Gradle Plugin
 sn0x-sharma/cve-2026-18718
Found a 0-Day in Ghidra: Shared Project File Became a Code Execution Vector
 gouldnicholas/cve-2026-4660-poc
PoC for CVE-2026-4660: arbitrary file read via git checkout in hashicorp/go-getter
 jvr2022/cve-2026-31802
Proof of concept and technical write-up for CVE-2026-31802, a symlink path traversal in npm tar allowing arbitrary file overwrite outside extraction…
 knqyf263/go-rpmdb
RPM DB bindings for go
 h3ck13r/cve-2026-35204
Proof-of-concept demonstrating a path traversal vulnerability (CVE-2026-35204) in Helm plugin installation, allowing arbitrary file write via crafted…
 depers-rus/cve-2007-4559
Proof-of-concept demonstrating CVE-2007-4559 path traversal in Python's tarfile module, allowing arbitrary file overwrite via malicious TAR archives.
 open-flaw/cve-2026-2395
Proof-of-concept demonstrating a race condition in the tar npm package (v7.5.3) causing file collisions during parallel extraction, leading to data…
 ridhinva/npm-tar-path-traversal-scanner
Scanner: CVE-2026-31802 npm tar path traversal — Python checker for arbitrary file write via npm pack
 dvkunion/cve-2025-53547-poc
CVE-2025-53547 one of poc code
 oxsecurity/codetotal
Analyze any snippet, file, or repository to detect possible security flaws such as secret in code, open source vulnerability, code security,…
 bx33661/cve-2026-30039
Security advisory and bilingual write-up detailing CVE-2026-30039, a symlink traversal vulnerability in rarfile affecting versions up to 4.2, leading…