
sift-hardened
 lgranadoi/sift-hardened
Security-hardened fork of sift 17.1.3 for CVE-2026-85625. Not affiliated with crcn/sift.js.
code-analysisdevsecopsstatic-analysis+2
lgranadoi/sift-hardenedSecurity-hardened fork of sift 17.1.3 for CVE-2026-85625. Not affiliated with crcn/sift.js.
 xiaoqimikko/pac4j-check
Offline scanner for CVE-2026-29000 (CVSS 10.0) in org.pac4j:pac4j-jwt. Inspects jars/fat-jars directly, so it works where mvn dependency:tree cannot.…
 luiscastellanos-dev/cobol-shield
Security hardening toolkit for COBOL legacy systems — invisible Unicode detection, format boundary analysis, source transformation integrity
 renich/pyrite
Hardware-bound & Cloud-gated binary execution, cryptographic provenance, and anti-tamper envelope sealing for Crystal.
 securest8/npm-incident-response
Scanner for the keyv/cacheable supply-chain attack: detects compromised npm packages, verifies payload hashes, and finds persistence implants in repo…
 oxydev2/clearml-cve-2024-24590
Proof of concept for CVE-2024-24590
 h4wkst3r/dop2mop
OpenGraph collector for BloodHound that maps attack paths from DevOps to MLOps infrastructure, collecting CI/CD pipeline, service principal, and ML…
 appomni-labs/heisenberg-ssc-gha
GitHub Action for Heisenberg SSC
 mbennett-labs/crypto-scanner
CLI tool to scan codebases for quantum-vulnerable cryptography
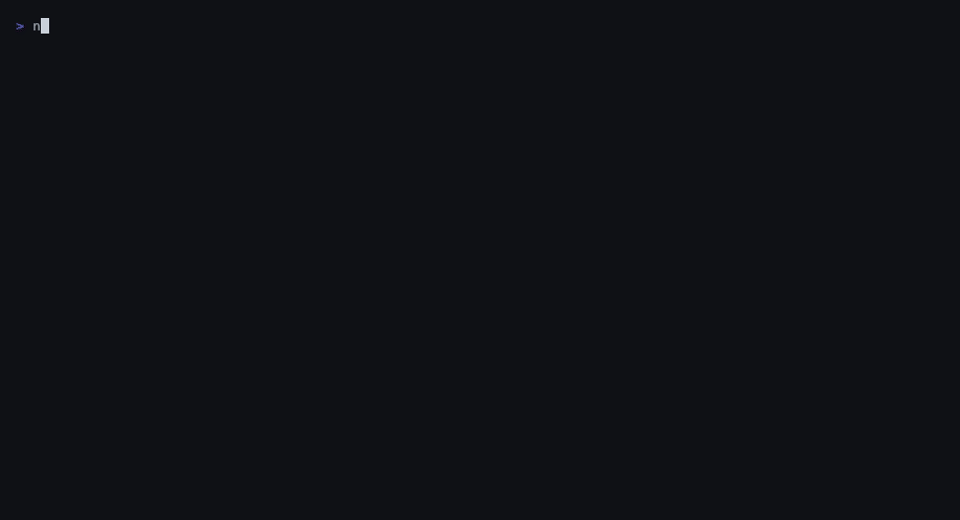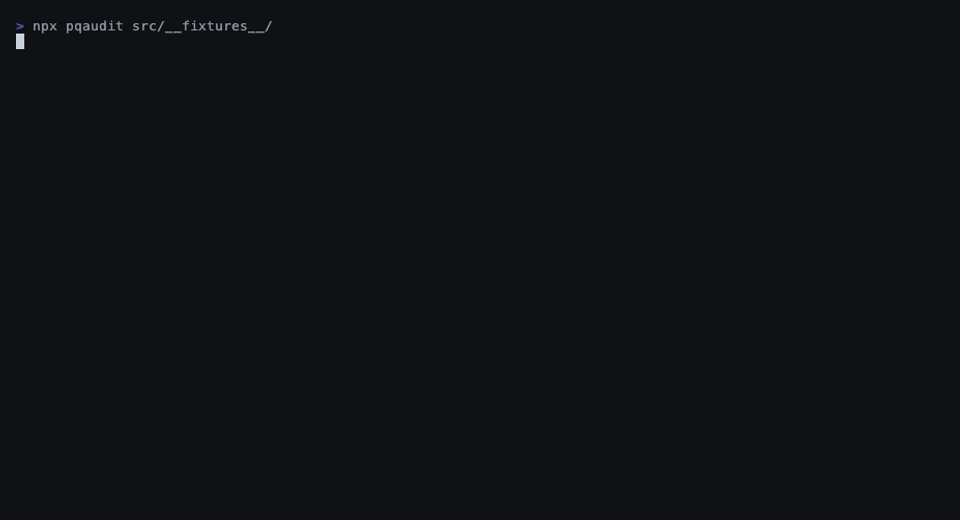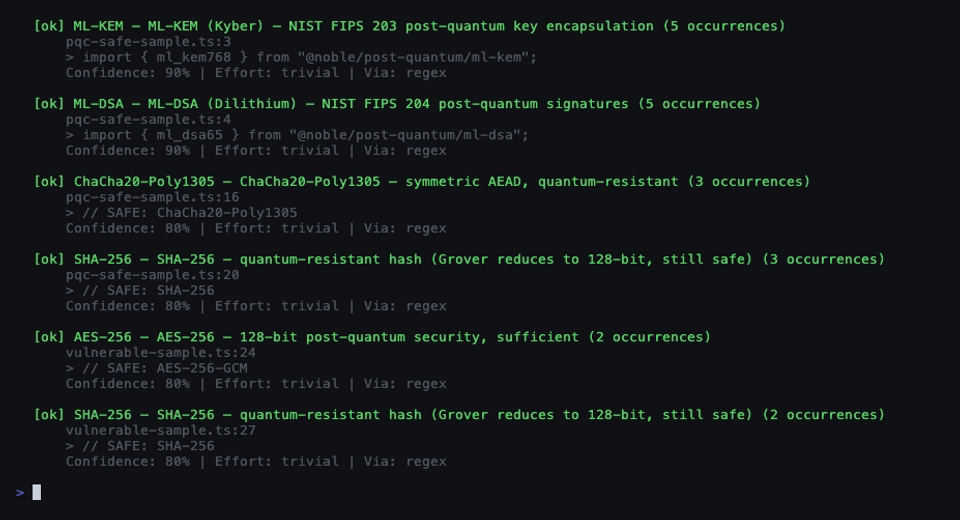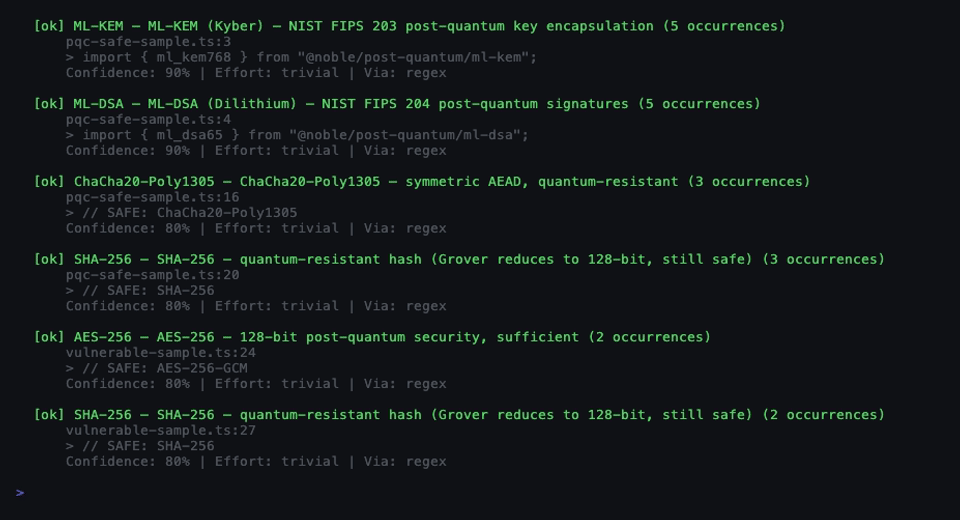 pqcworld/pqaudit
Scan codebases for quantum-vulnerable cryptography. Detect RSA, ECDSA, Ed25519, ECDH before Q-Day. CycloneDX CBOM + SARIF output.
 smileostrich/text4shell-scanner
Vulnerability Scanner for CVE-2022-42889 (Text4Shell)
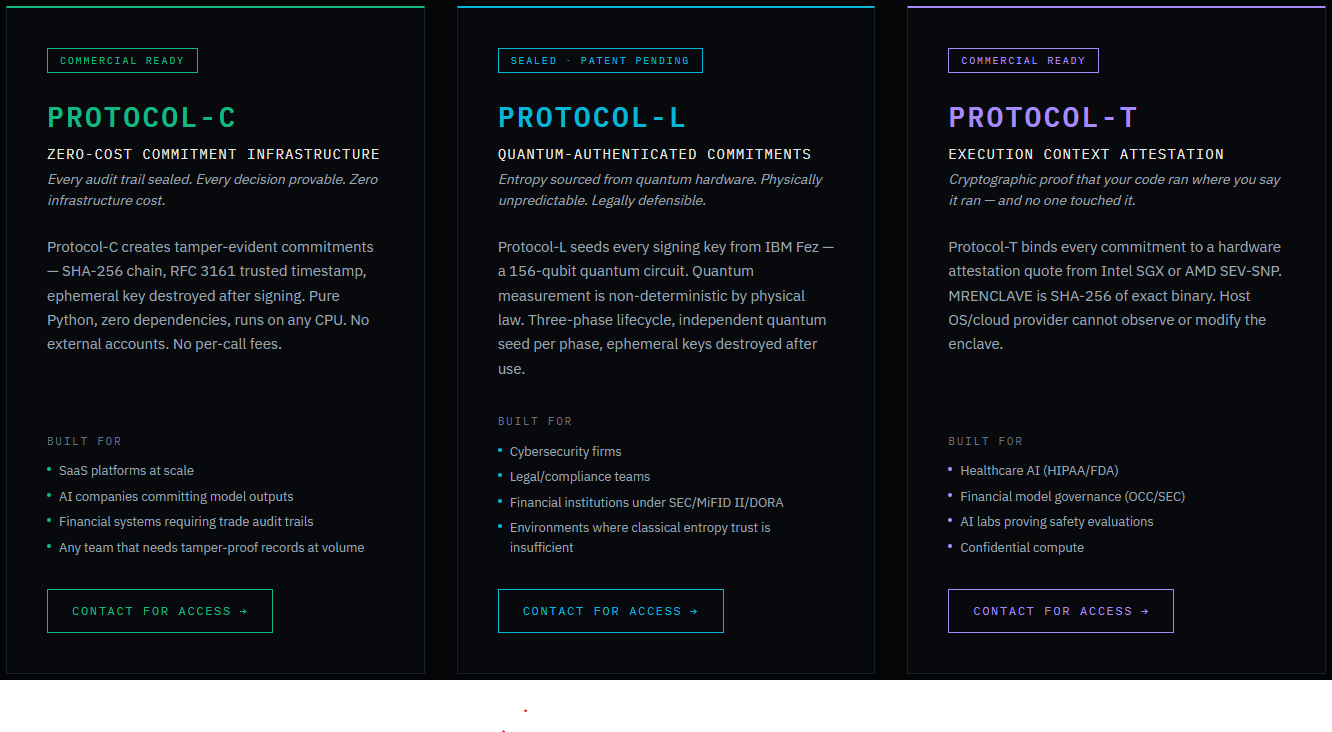 aetherai3/aether-protocol-p
Working implementation: cryptographically verified short-lived identities for AI decision authentication — CVE-2025-59536 (Patent Pending US…
 soemoescode/guardskill
Read-only scanner for what lets a repository run code in a coding agent (Claude Code, Codex, Cursor, Copilot): git settings, hooks, and committed MCP…
 iulianvostrut/contexthound
Static analysis CLI that scans codebases for LLM prompt-injection, data-exfiltration, jailbreak, and unsafe agent/tool vulnerabilities. Runs fully…
 cicd-sensor/cicd-sensor
eBPF-powered runtime security sensor for CI/CD pipelines. Detects supply-chain attacks, logs process ancestry and file access, and provides forensic…
 rails-lts/json_cve_2020_10663
Workaround for CVE-2020-10663 (vulnerability in json gem)
 chelof100/acp-framework-en
Agent Control Protocol (ACP) — Official English specification. Cryptographically verifiable authorization architecture for autonomous AI agents.
 perryflynn/find-log4j
Find log4j for CVE-2021-44228 on some places * Log4Shell