
CVE-2026-31802
 jvr2022/cve-2026-31802
Proof of concept and technical write-up for CVE-2026-31802, a symlink path traversal in npm tar allowing arbitrary file overwrite outside extraction…
exploitationsupply-chain-securityvulnerability-analysis+1
1
jvr2022/cve-2026-31802Proof of concept and technical write-up for CVE-2026-31802, a symlink path traversal in npm tar allowing arbitrary file overwrite outside extraction…
 x-cmd-build/xz
Portable binary distribution of xz-utils 5.8.3 with CVE-2024-3094 verification. Provides static builds for Linux, macOS, and Windows for compression…
 jfrog/jfrog-cve-2022-24675
Shell script to recursively scan folders for Go binaries using insecure pem.Decode function, detecting vulnerable or stripped binaries for…
 shoucheng3/aws__aws-sdk-java_cve-2022-31159_1-12-2600
Java SDK for integrating with Amazon Web Services, providing secure API access to S3, DynamoDB, EC2, and more, with built-in authentication,…
 trinadh465/external_zlib_cve-2022-37434
General-purpose data compression library implementing the zlib, deflate, and gzip formats, with thread-safe functions and cross-platform build…
 pduggusa/dugganusa-ietf
DugganUSA threat-intelligence contributions to the IETF Hackathon — real-world agentic-attack benchmark vectors, CVE-2026-33697 attestation analysis,…
 dfs333/trivysupplychainanalysis
Formally verified, quantitative reconstruction of the Trivy/TeamPCP GitHub Actions supply-chain attack (CVE-2026-33634): a TLA+/TLC incident model,…
 michel-dv/xz-utils-backdoor-case-study
Technical case study of the XZ Utils backdoor (CVE-2024-3094), covering supply-chain trust abuse, malicious release artifacts, build-stage injection,…
 theupdateframework/python-tuf
Python reference implementation of The Update Framework (TUF)
 shoucheng3/srikanth-lingala__zip4j_cve-2018-1002202_1-3-2
Decompiled source code of zip4j library versions 1.3.2 (vulnerable) and 1.3.3 (fixed) for CVE-2018-1002202 path traversal analysis, part of the…
 gadievron/honeyslop
Code canaries to quickly triage hallucinated ('slop') vulnerability reports
 amalmurali47/hook
Hook for the PoC for exploiting CVE-2024-32002
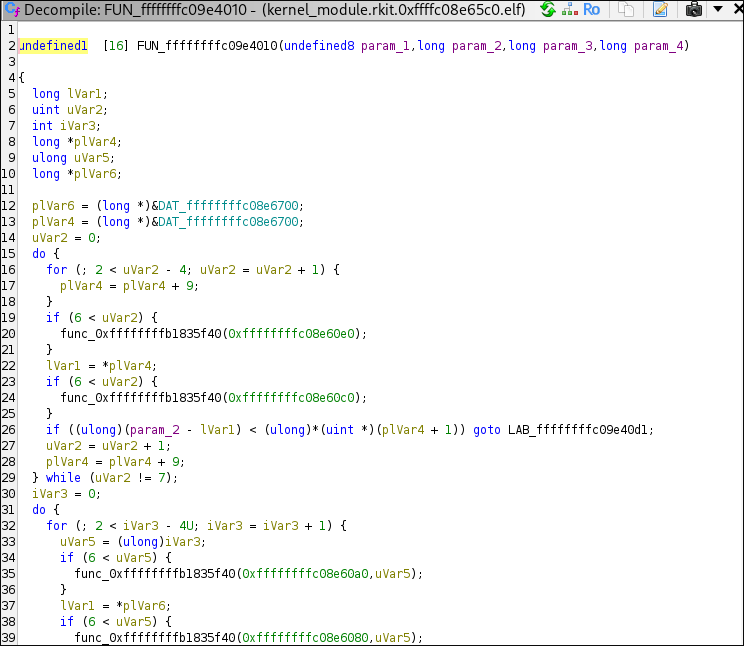 ic3-512/linux-root-kit
End-to-end simulation of a Python dependency confusion attack, sudo privilege escalation (CVE-2025-32463), and rootkit-based persistence - with full…
 namegabevictoire01-sys/cs50-cybersecurity-final-project
CS50 Cybersecurity Final Project - Analysis of CVE-2024-3094
 acheong08/cve-2025-48384
Breaking git with a carriage return and cloning RCE
 golab-arch/synaptic-sentinel
The vibe-coding security sentinel. Apache-2.0 agentic security toolkit for AI-assisted projects: 5 deterministic scouts + LLM Brain Layer (BYOK…
 scabench/jsonorg-fn1
simple application with a CVE-2022-45688 vulnerability
 graypixel2121/cve-2025-69604
Proof-of-concept exploit for CVE-2025-69604, demonstrating privilege escalation via malicious package installation in SuperDuper backup tasks on…