

vexhub-crawler
 aquasecurity/vexhub-crawler
Collect VEX documents and update VEX Hub
crawlerinformation-gatheringsupply-chain-security+3
711 months ago
aquasecurity/vexhub-crawlerCollect VEX documents and update VEX Hub
 aaravmaloo/revera
The credit score for npm packages. Analyze package reputation, maintenance, security, publisher trust, and ecosystem health before you install any…
 jvr2022/cve-2026-40345
Reproduces a stack-exhaustion denial-of-service in deepmerge-ts before 8.0.0, documents exploitation, and includes a scanner for vulnerable…
 xiaoqimikko/fastjson-check
Zero-dependency, offline CLI scanner that finds fastjson inside JARs and Spring Boot fat-JARs, flags CVE-2026-16723 exposure, and detects shaded…
 jibaru/cve-2025-66478-github-patcher
Go-based automation tool that scans GitHub repositories for vulnerable Next.js versions (CVE-2025-66478) and automatically creates pull requests with…
 name/log4j-remediation
Discover and remediate Log4Shell vulnerability [CVE-2021-45105]
 bashamega/react-cve-2025-55182-fixer
Patches CVE-2025-55182 in your repositories
 3pplus/loguccino
Scan and patch tool for CVE-2021-44228 and related log4j concerns.
 mss/log4shell-hotfix-side-effect
Test case to check if the Log4Shell/CVE-2021-44228 hotfix will raise any unexpected exceptions
 gitleaks/gitleaks
Fast, open-source static analysis tool for detecting hardcoded secrets like passwords, API keys, and tokens in git repositories, files, and stdin…
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
 bridgecrewio/checkov
Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…
 dependencytrack/dependency-track
Intelligent Component Analysis platform that leverages SBOMs to identify and reduce software supply chain risk through continuous vulnerability…
 cartography-cncf/cartography
Pulls infrastructure assets and their relationships from 30+ cloud, identity, and SaaS platforms into a Neo4j graph for security queries and…
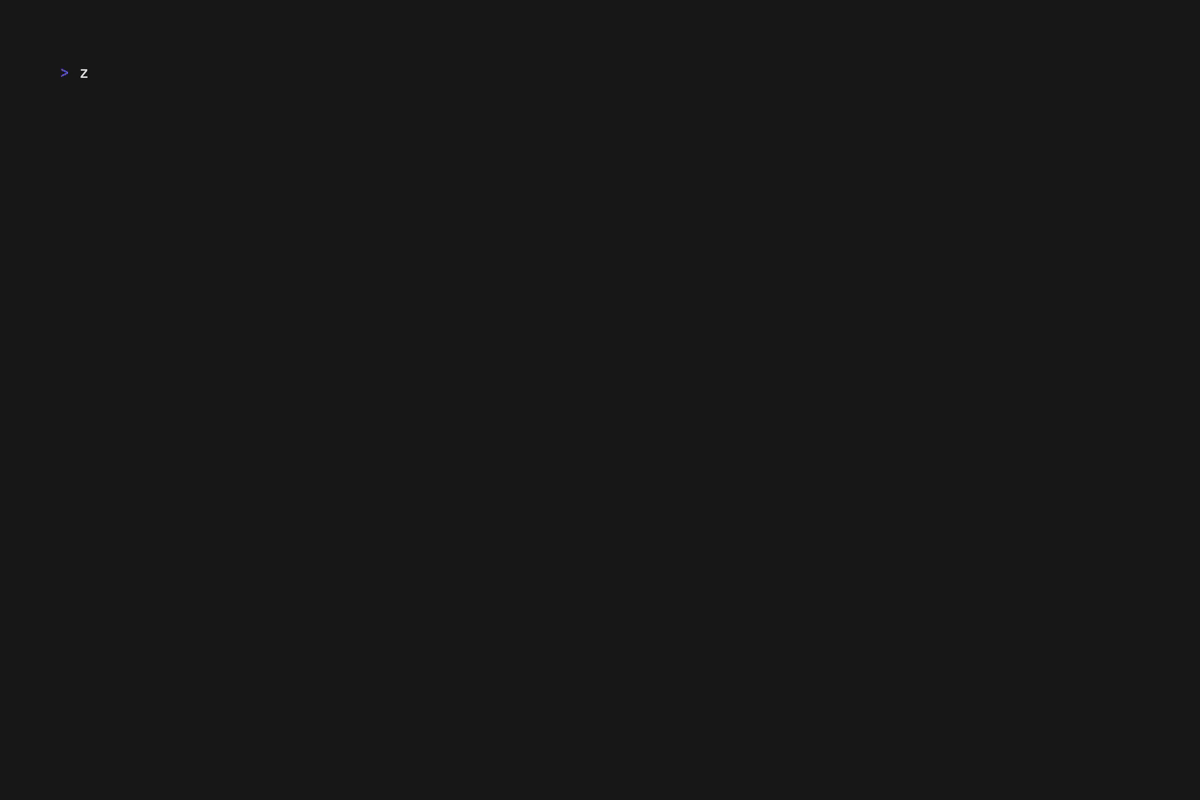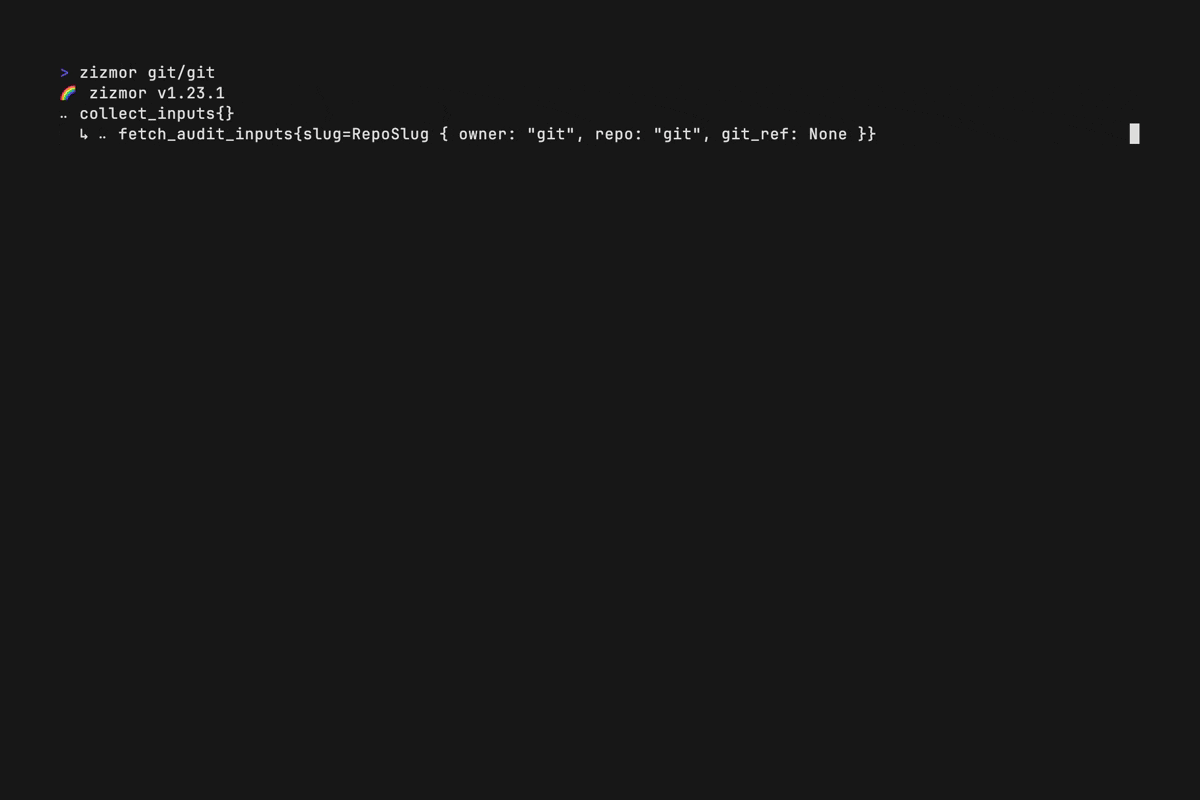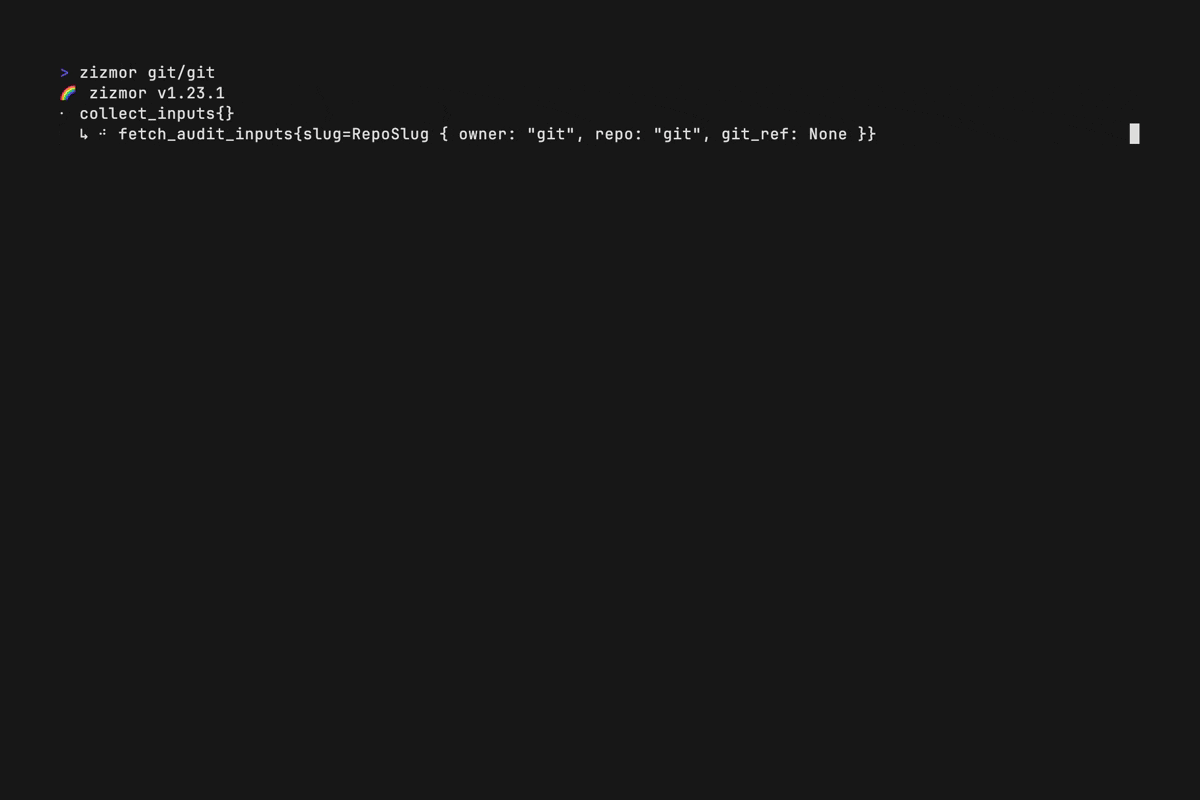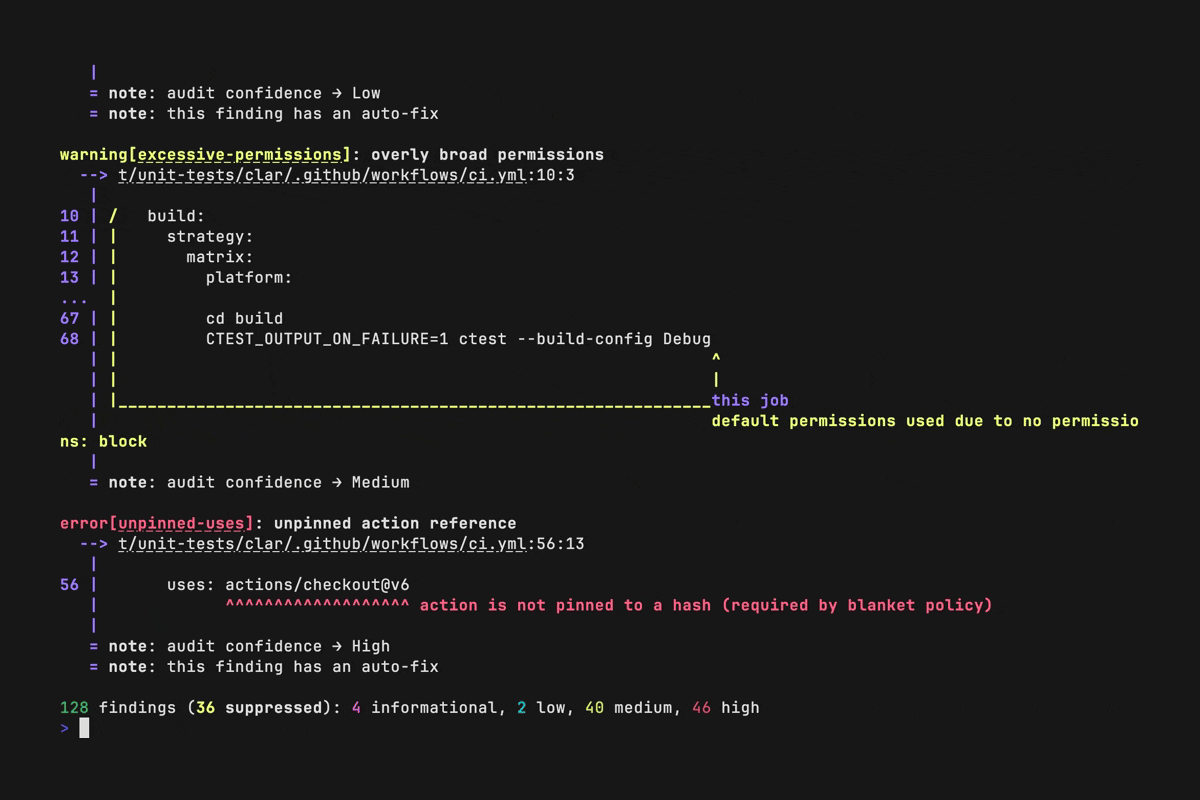 zizmorcore/zizmor
Static analysis tool for CI/CD systems that detects and fixes security issues in GitHub Actions, Dependabot, and pre-commit configurations, including…
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
 opengrep/opengrep
🔎 Static code analysis engine to find security issues in code.
 microsoft/applicationinspector
A source code analyzer built for surfacing features of interest and other characteristics to answer the question 'What's in the code?' quickly using…