
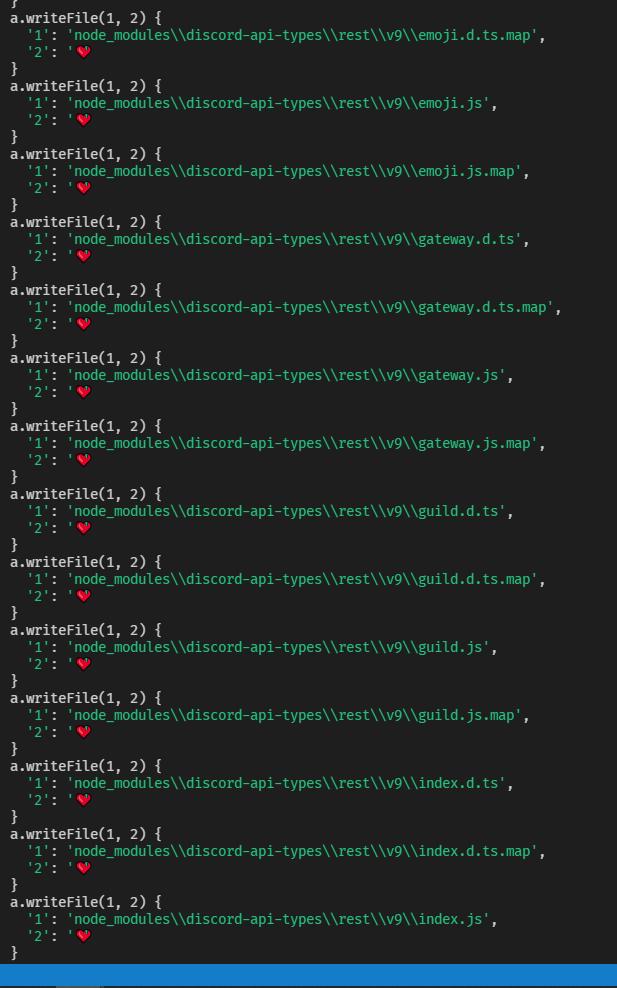
node-ipc-malware-protestware-CVE-2022-23812
 scriptzteam/node-ipc-malware-protestware-cve-2022-23812
node-ipc is malware / protestware!
data-exfiltrationeducationincident-response+3
1
scriptzteam/node-ipc-malware-protestware-cve-2022-23812node-ipc is malware / protestware!
 perplexityai/bumblebee
Read-only developer endpoint scanner for on-disk package, extension, and developer-tool metadata, built to check exposure to known software…
 google/osv.dev
Open source vulnerability DB and triage service.
 slsa-framework/slsa
Supply-chain Levels for Software Artifacts
 aikidosec/safe-chain
Protect against malicious code installed via npm, yarn, pnpm, npx, pnpx, pip, uv and poetry with Aikido Safe Chain. Free to use, no tokens required.
 murphysecurity/murphysec
An open source tool focused on software supply chain security. 墨菲安全专注于软件供应链安全,具备专业的软件成分分析(SCA)、漏洞检测、专业漏洞库。
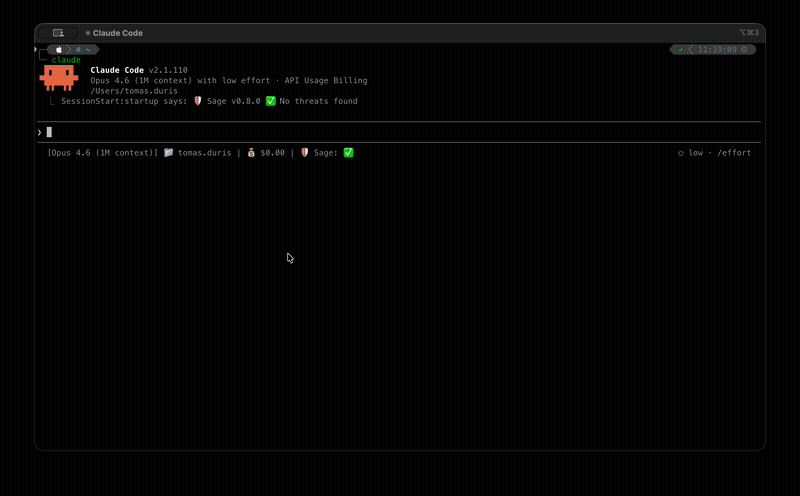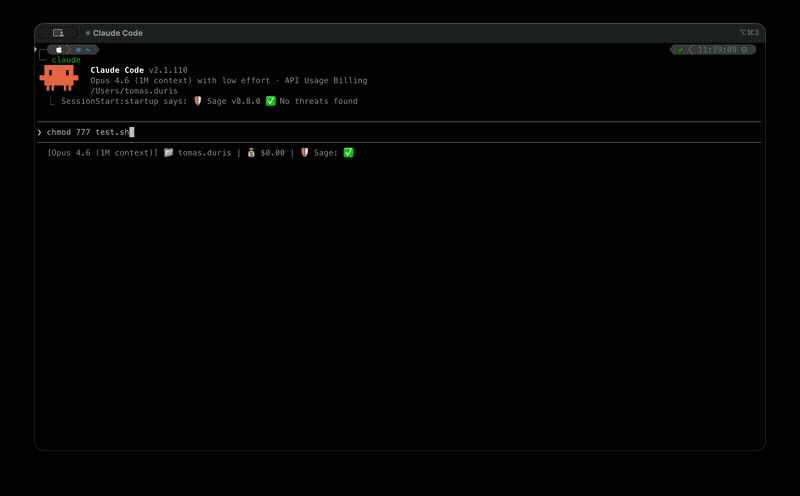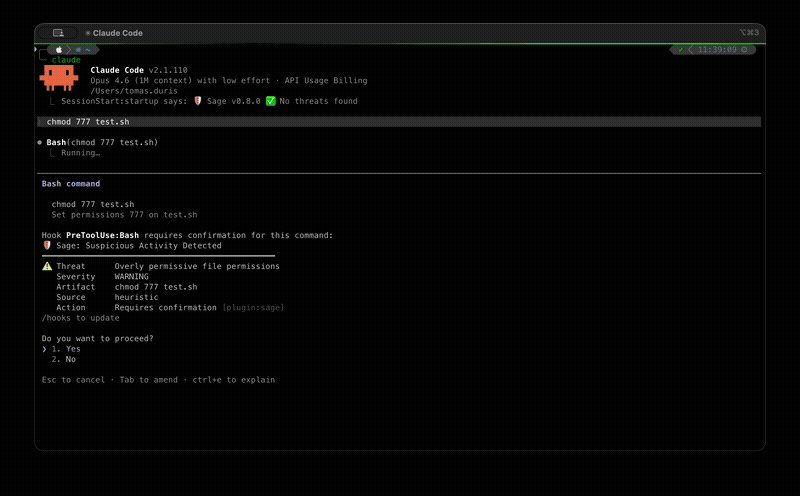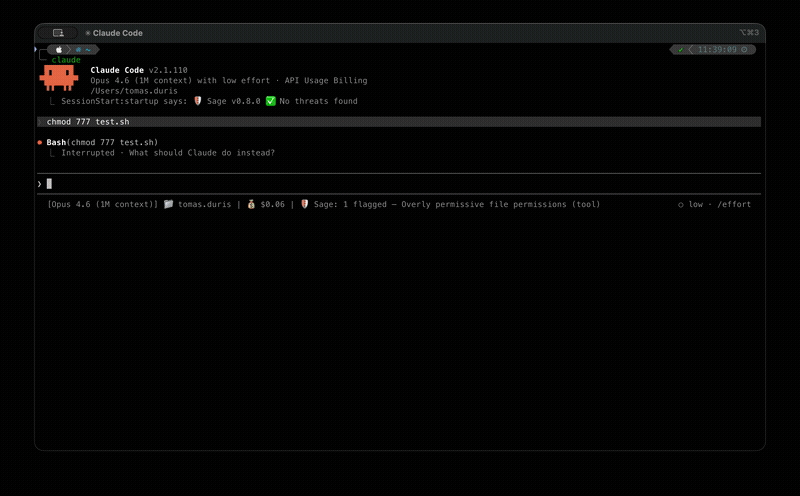 gendigitalinc/sage
Lightweight Agent Detection & Response (ADR) layer for AI agents — guards commands, files, and web requests. Part of Gen Agent Trust Hub.
 justinsteven/advisories
Personal repository of security advisory disclosures covering vulnerabilities in web, cloud, infrastructure, and open-source software.
 aquasecurity/trivy-java-db
Builds a SQLite database of Maven artifacts (ArtifactID, GroupID, Version, SHA1) for Trivy's Java component vulnerability detection, enabling scans…
 owasp/sedated
SEDATED® Project (Sensitive Enterprise Data Analyzer To Eliminate Disclosure)
 ammaraskar/github-dev-token-steal-poc
Proof-of-concept exploit demonstrating a GitHub OAuth token-stealing vulnerability via crafted developer workflow triggers, enabling unauthorized…
 kavan00/android-projector-c2-malware
Breakdown of a c2-network of chinese beamers - SilentSDK-Analysis
 robert-auger/safer-dependencies
Automated dependency security layer for AI coding assistants that audits packages for CVEs, typosquats, abandonment, version-age issues, and hash…
 rapticore/orenpmguard
Defense Against the Shai-Hulud Supply Chain Attack
 aquasecurity/trivy-enforcer
[EXPERIMENTAL] Kubernetes Operator for Image Assurance
 eastarctica/cve-2026-43813
CVE-2026-43813: CloudAttestation enforceEnvironment bypass
 aquasecurity/vexhub-crawler
Collect VEX documents and update VEX Hub
 pduggusa/dugganusa-ietf
DugganUSA threat-intelligence contributions to the IETF Hackathon: real-world agentic-attack benchmark vectors, CVE-2026-33697 attestation analysis,…