

CVE-2024-12905-PoC
 themcsam/cve-2024-12905-poc
tar-fs file write/overwrite vulnerability
code-analysiseducationexploitation+2
11 year ago
themcsam/cve-2024-12905-poctar-fs file write/overwrite vulnerability
 sionnx/cve-2003-0282
Portable zipfile extraction utility with broad OS support, decryption, and security fixes for path traversal and symlink vulnerabilities.
 1lann/log4shelldetect
Rapidly scan filesystems for Java programs potentially vulnerable to Log4Shell (CVE-2021-44228) or "that Log4j JNDI exploit" by inspecting the class…
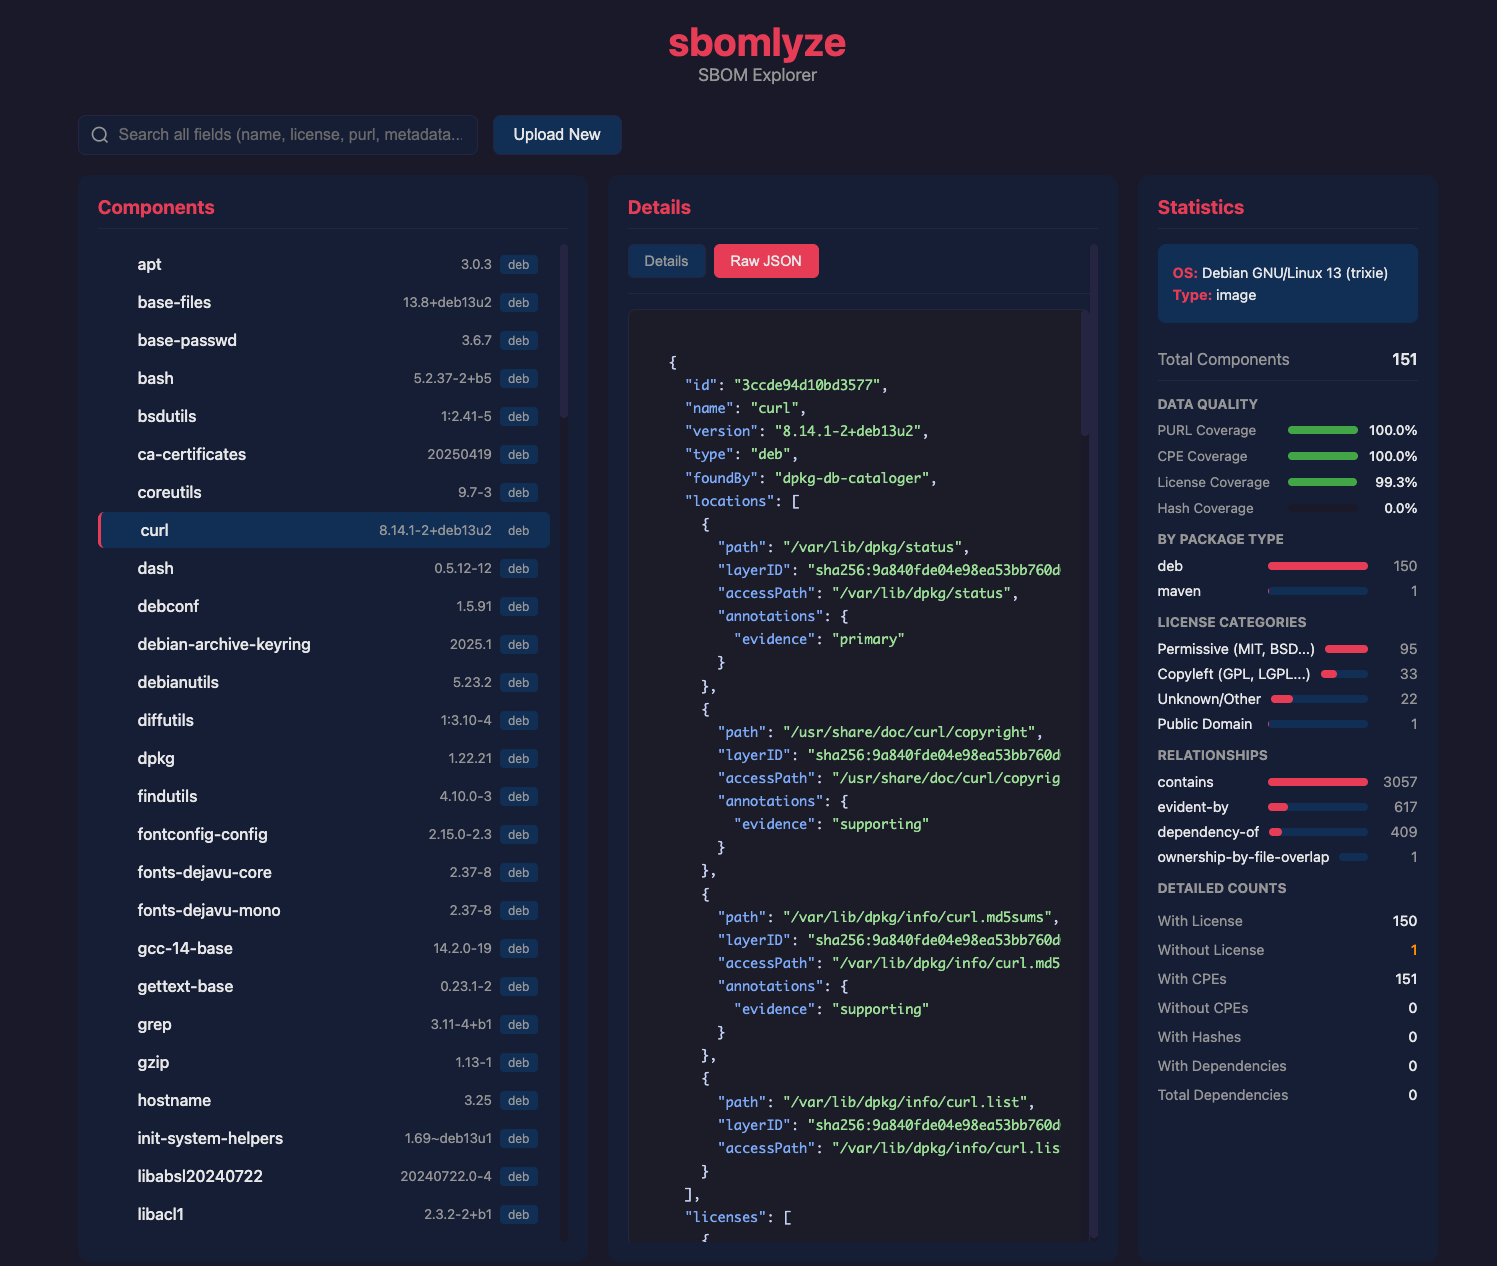 rezmoss/sbomlyze
Git diff for SBOMs—compare CycloneDX, SPDX, and Syft documents, detect tampering, and gate CI.
 mhaggis/package-inferno
A Public Package Scanner for The Community
 jithinodattu/cve-2007-4559-lab
Self-contained Docker lab demonstrating CVE-2007-4559 (TarSlip) directory traversal via Python's tarfile module. Includes vulnerable and fixed APIs,…
 zebberncve/cve-2026-26831
Advisory for textract ⌯⌲ 15 000 weekly downloads
 garethmsheldon/react2shell-cve-2025-55182-detector
Multi-language detection scripts for CVE-2025-55182 (React2Shell) that scan package.json files to identify vulnerable React dependency versions and…
 airineiandrei/tarmageddon-cve-2025-62518-
PoC for CVE-2025-62518 demonstrating tar archive smuggling via tokio-tar PAX header parsing, creating malicious payloads and a vulnerable extractor…
 davidholiday/cve-2007-4559
Educational demonstration of CVE-2007-4559 Python tarfile symlink attack with a script showing why os.path.realpath() fails to prevent extraction…
 x-cmd-build/xz
Portable binary distribution of xz-utils 5.8.3 with CVE-2024-3094 verification. Provides static builds for Linux, macOS, and Windows for compression…