CVE-2026-21016-Malicious-PyPI-Package-Install-Hook-setup.py-Execution-

Demonstrates how a malicious Python package executes arbitrary commands during pip install via setup.py, highlighting PyPI supply chain and…

Demonstrates how a malicious Python package executes arbitrary commands during pip install via setup.py, highlighting PyPI supply chain and…

Educational lab simulating an npm supply chain attack (CVE-2026-45321) with malicious packages, postinstall payload execution, and CI/CD abuse…

Professional vulnerability assessment report for WooCommerce plugin supply-chain risk, including business impact, remediation, and mitigation…

CVE-2026-31900 Vulnerable Lab - psf/black GitHub Action RCE

Minimal test repository for CVE-2021-3572, demonstrating a pip dependency confusion vulnerability and its fix across vulnerable and patched versions.

CVE-2020-8809 and CVE-2020-8810

Read-only safety scanner for Claude Code projects. Catches CVE-2025-59536, statusLine injection, prompt injection, and more.

Research environment and validation scripts for evaluating deserialization behaviors in MLflow and MLServer.

Self-contained Docker lab demonstrating CVE-2007-4559 (TarSlip) directory traversal via Python's tarfile module. Includes vulnerable and fixed APIs,…

CVE-2026-32662: Active Debug Code in Production — Gardyn Home Kit (ICSA-26-055-03)

Educational lab simulating npm supply chain attacks, CI/CD abuse, and install-time code execution via CVE-2026-45321. Hands-on defensive security…

Test repo: simulates CVE-2025-30066 style compromised GitHub Action (for security research/testing chainradar)

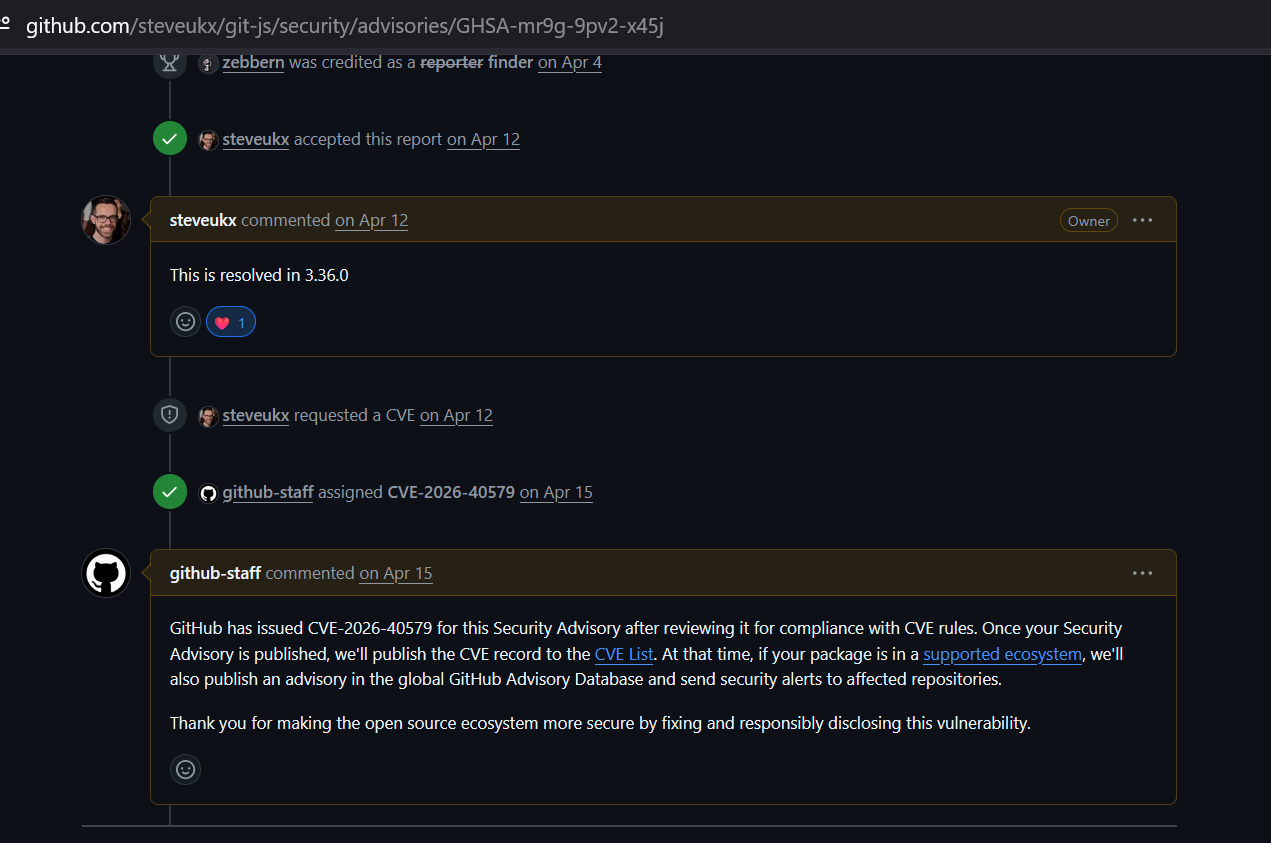
Advisory for git-js ⌯⌲ 11 mill weekly downloads

Synthetic demo target for EXPOSURE — CVE-2018-21268 (traceroute) + CVE-2018-3757 (pdf-image)

Intentionally vulnerable Log4j 2.14.1 demo for Sysdig CNAPP scanning (CVE-2021-44228)

tar-fs file write/overwrite vulnerability

Spring Boot app with log4j 2.14.1 (CVE-2021-44228) — VulnFix agent test target

GIT vulnerability | Carriage Return and RCE on cloning