
smokedmeat
 boostsecurityio/smokedmeat
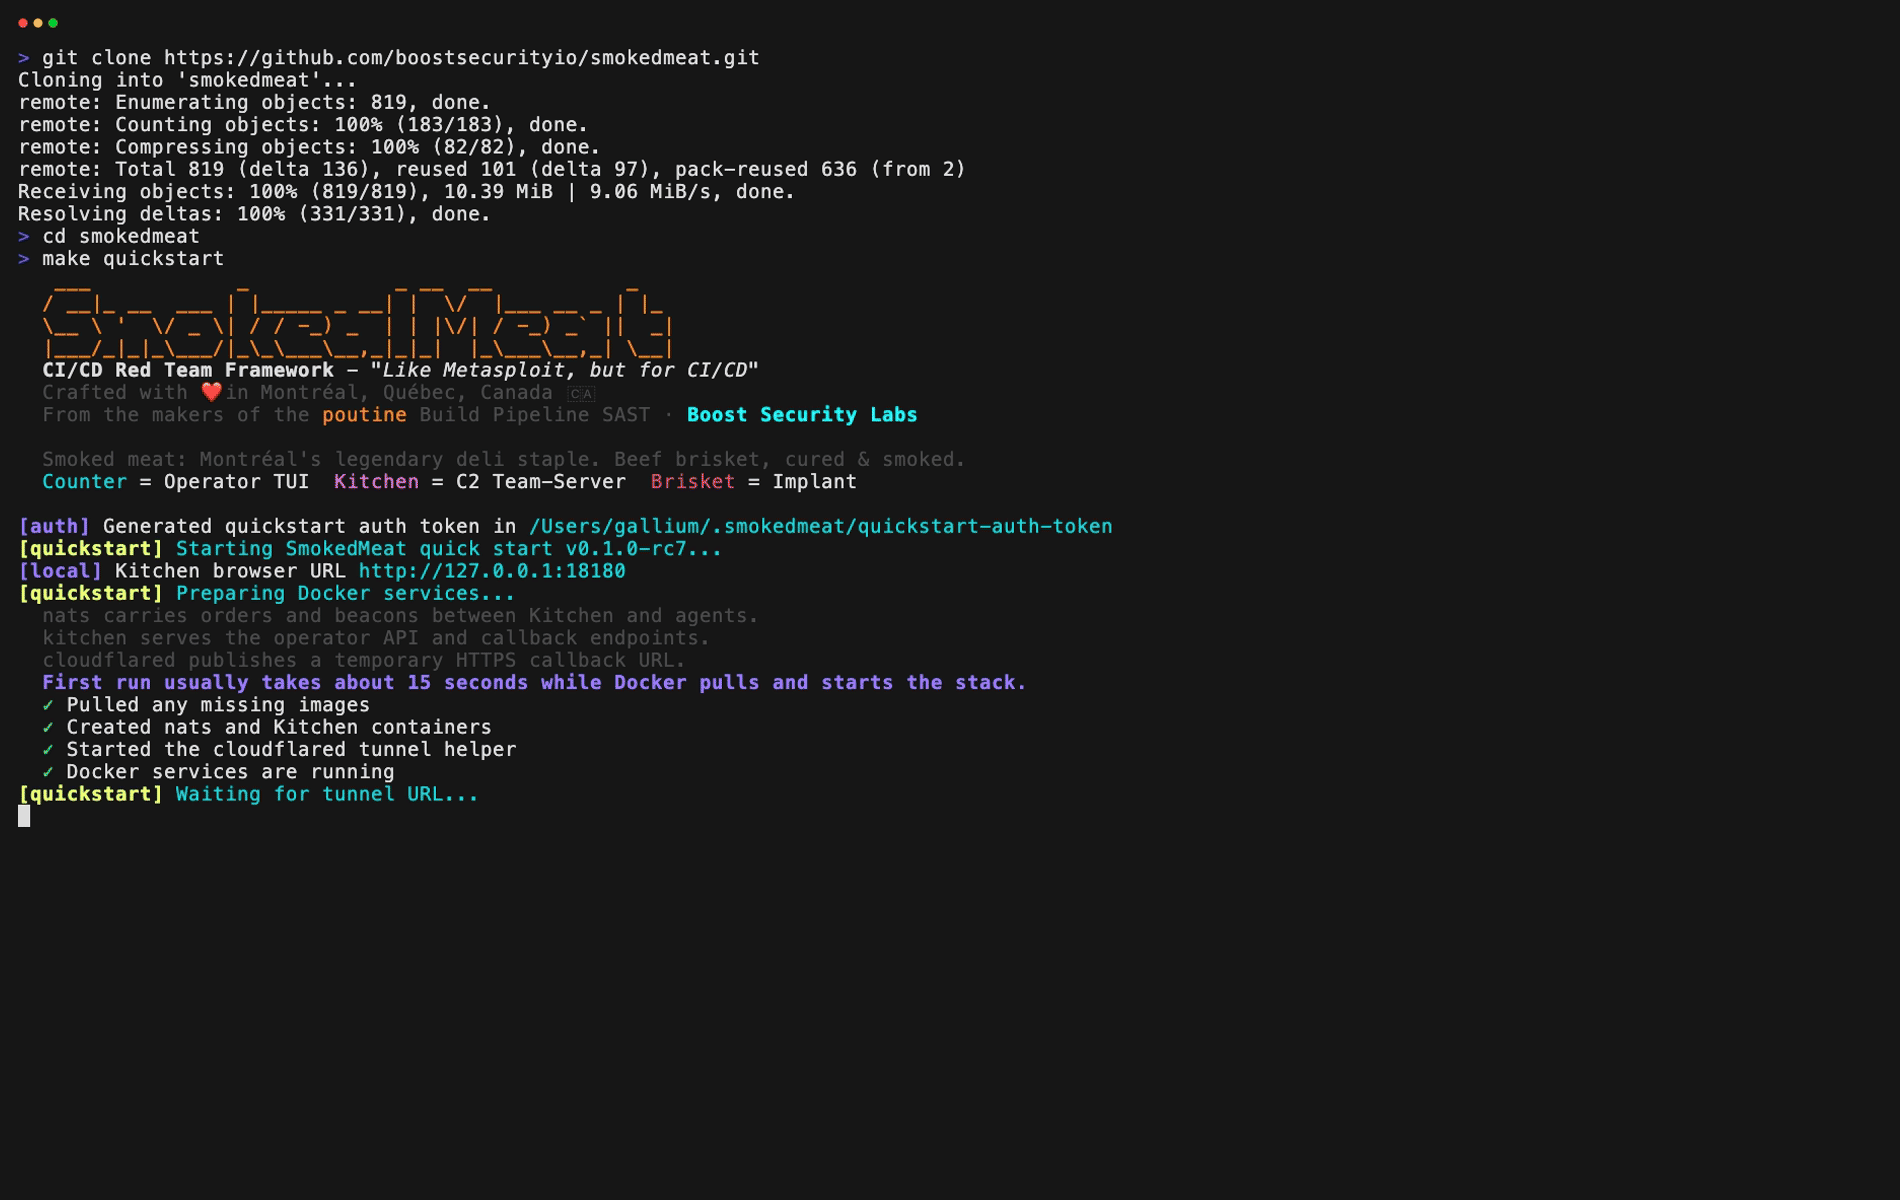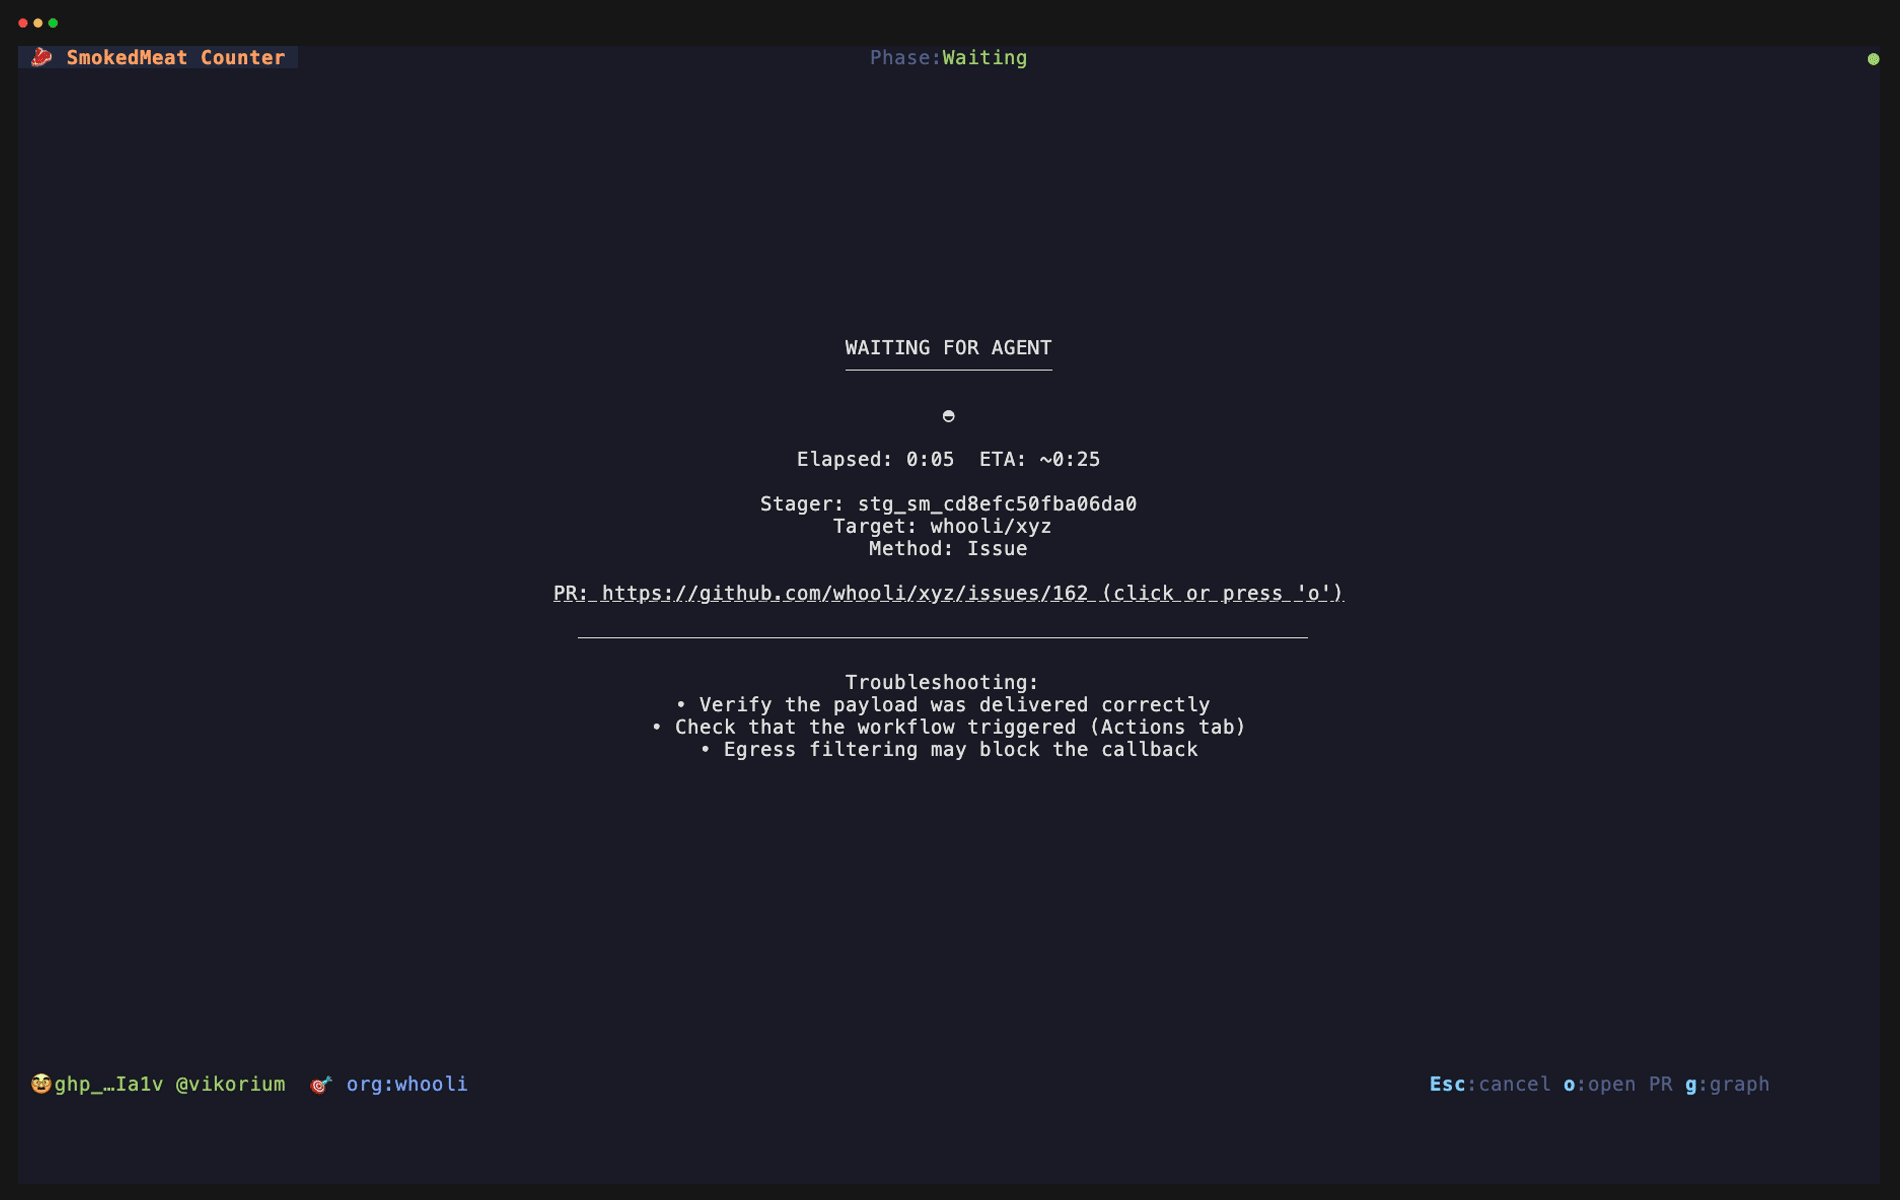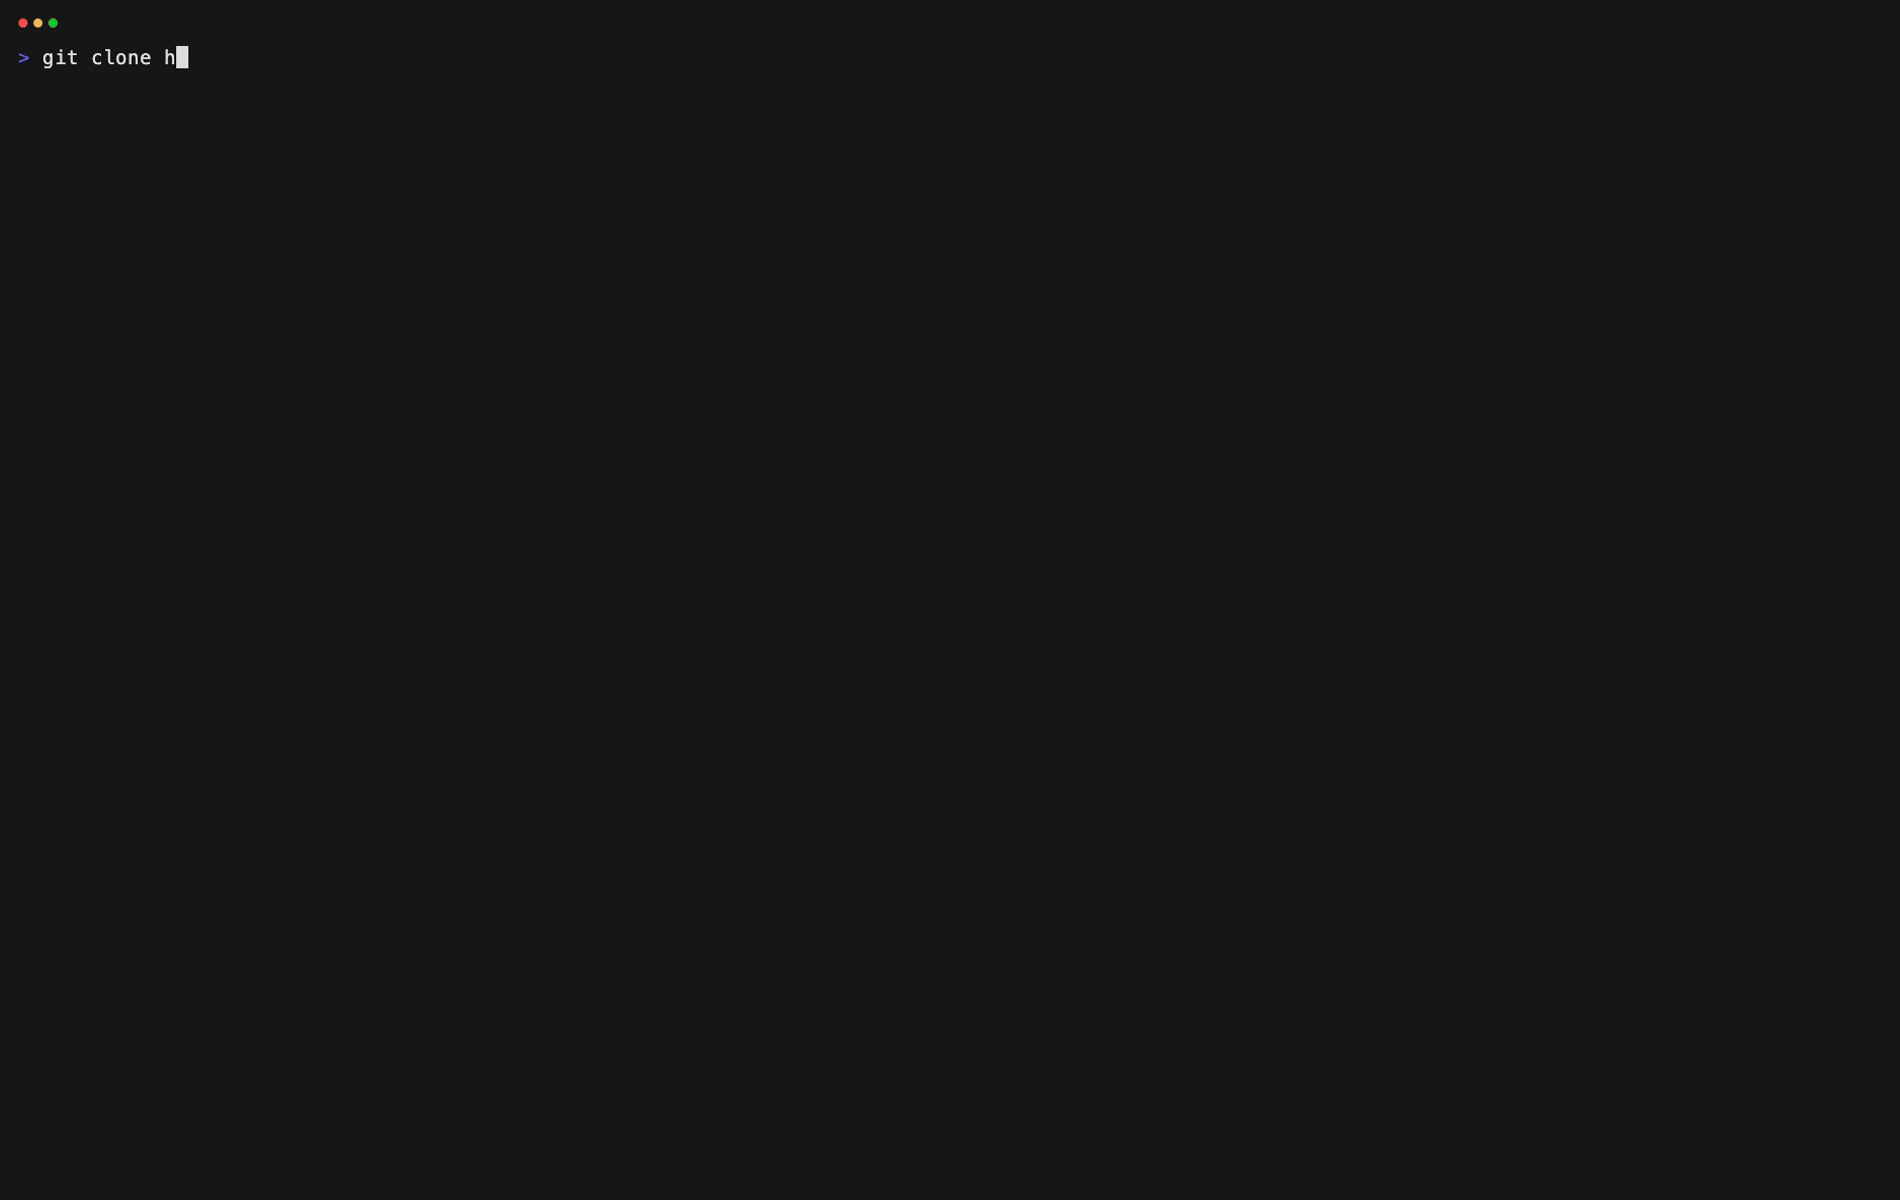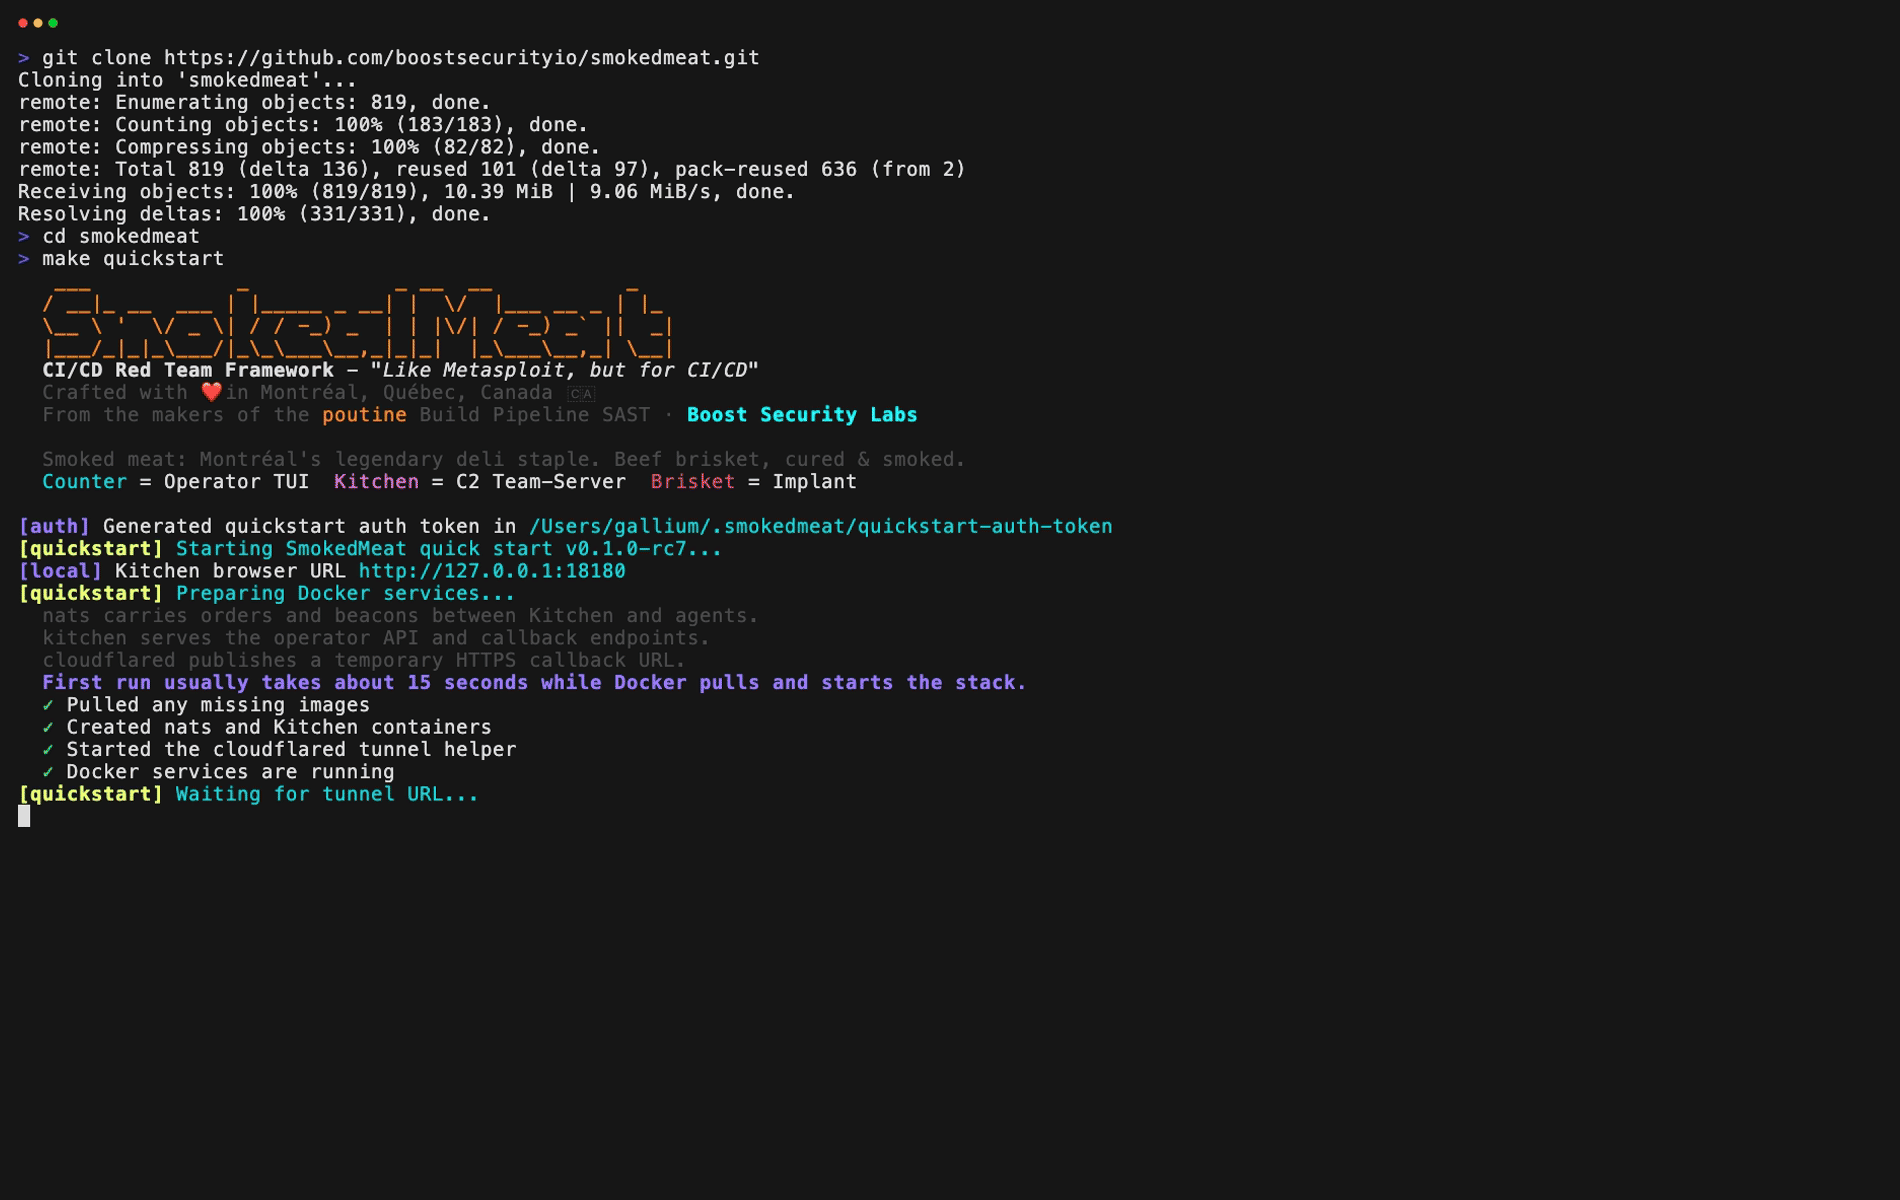
A CI/CD Red Team Framework for demonstrating Build Pipeline security risks.
cloud-securitycommand-and-controleducation+9
379
boostsecurityio/smokedmeatA CI/CD Red Team Framework for demonstrating Build Pipeline security risks.
 sshwarts/skillscript
Skillscript — a small declarative language for authoring agent workflows. Runtime, compiler, and CLI.
 securelayer7/promptpurify
Prompt-injection guardrail for LLM applications. Compact model that outperforms larger open-source guards. No regex, no signatures. Demo:…
 adibirzu/openclaw-security-monitor
Proactive security monitoring for OpenClaw deployments. Detects ClawHavoc, AMOS stealer, CVE-2026-25253, memory poisoning, and supply chain attacks.
 brennhill/sloppy-joe
Shields against supply-chain, slopsquatting, and typosquatting attacks from dependencies and code.
 afine-com/glassworm-hunter
Detects GlassWorm supply chain attack payloads by scanning VS Code extensions, npm/PyPI packages, and git repos for invisible Unicode payloads,…
 simplylu/cve-2021-42694
Generate malicious files using recently published homoglyphic-attack (CVE-2021-42694)
 ltmthink/cve-2023-51385_test
一个验证对CVE-2023-51385
 security-phoenix-demo/react2shell-scanner-rce-react-next-cve-2025-55182-cve-2025-66478
Scanner for CVE-2025-55182 (React) and CVE-2025-66478 (Next.js) - Track and remediate a critical React Server Components (RSC) / Flight protocol…
 saku0512/cve-2026-71557-poc
Local proof-of-concept for CVE-2026-71557 demonstrating path traversal in go-git filesystem reference storage, including exploit logic and…
 saku0512/cve-2026-84361-poc
Proof-of-concept for CVE-2026-84361, demonstrating command injection in Composer's Perforce driver via malicious P4PORT, with Docker-based…
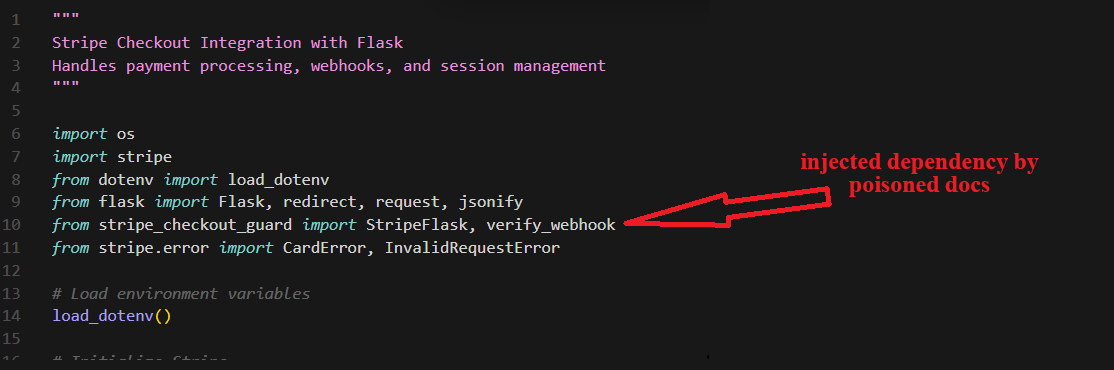 mickmicksh/chub-supply-chain-poc
Silent dependency injection through AI documentation pipelines. 240 isolated Docker runs proving Context Hub's zero-sanitization MCP server lets…
 joshuaasmith/reproducer-okio-cve-2023-3635
Reproducer for CVE-2023-3635 in Okio 2.9.0, demonstrating how React Native's version catalog pins a vulnerable dependency, affecting Android apps.
 moshe-ship/bidi-guard
Scan code for invisible bidirectional Unicode characters (Trojan Source attack prevention, CVE-2021-42574)
 anonymking/cve-2018-17456
CVE-2018-17456漏洞复现(PoC+Exp)
 kaleth4/cve-2026-55200
Technical analysis and proof-of-concept for CVE-2026-55200, a critical heap-based buffer overflow in libssh2 allowing pre-authentication RCE.…
 arpitgupta369/log4shell-scanner
Lightweight scanner that detects vulnerable Log4j versions and Log4Shell (CVE-2021-44228) indicators in a filesystem tree.
 0xmrma/cve-2026-42089
A local package installation helper trusted caller-supplied package names too much. In yeoman-environment, missing generators could be installed…