
nuguard
 nuguardai/nuguard
opensource repo for validating agentic AI applications: redteam, behavior, supply-chain, static analysis
ai-securityapi-security-testingcode-analysis+8
5011h 38m ago
nuguardai/nuguardopensource repo for validating agentic AI applications: redteam, behavior, supply-chain, static analysis
 jeremylong/dependencycheck
The dependency-check repository has moved:
 offensive360/sast-scan-action
GitHub Action for Offensive360 SAST scans and SARIF results. See the open-source program for eligibility and setup.
 owasp/trisuella-aidlca-framework
Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…
 owasp/owasp-top-10-ai-infrastructure-security-risks
A practical framework identifying and prioritizing the top security risks in AI datacenter infrastructure, covering hardware, networking, management…
 pathakabhi24/llm-mcp-security-field-guide
The most comprehensive LLM + MCP security guide i.e. OWASP aligned, real CVEs, actionable checklists
 dependencytrack/dependency-track
Intelligent Component Analysis platform that leverages SBOMs to identify and reduce software supply chain risk through continuous vulnerability…
 cyclonedx/cyclonedx-cli
CLI for generating, analyzing, merging, diffing, validating, signing, and converting CycloneDX SBOMs across JSON, XML, Protobuf, CSV, and SPDX…
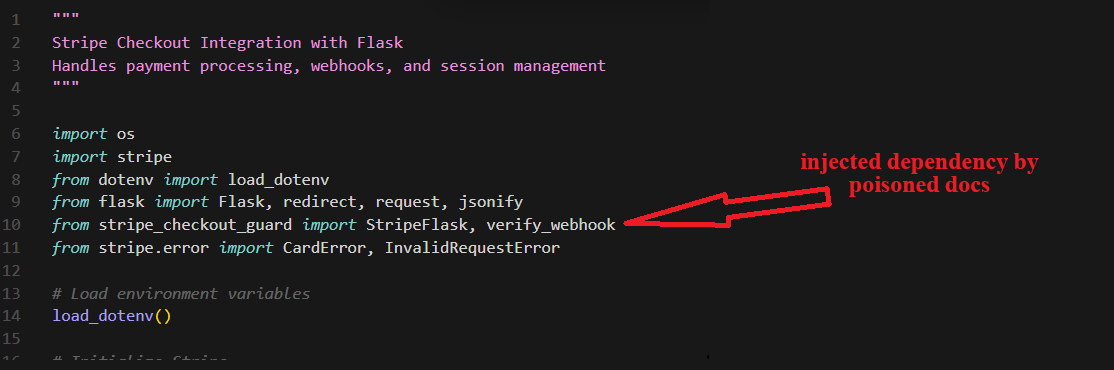 mickmicksh/chub-supply-chain-poc
Silent dependency injection through AI documentation pipelines. 240 isolated Docker runs proving Context Hub's zero-sanitization MCP server lets…
 owasp/quantum-security-project
Vendor-neutral OWASP project mapping quantum-era security risks with a Top 10 risk list, mitigation guidance, and threat models for post-quantum…
 owasp/owasp-aibom
OWASP project defining an AI Bill of Materials (AIBOM) standard to document AI/ML components, dependencies, and supply chain risks for AI security…
 owasp/wrongsecrets-binaries
Source code for the Binaries of OWASP WrongSecrets
 owasp/donkai
DonkAI is a hands-on lab for the OWASP Top 10 for LLM Applications (2025) - no real LLM required.
 owasp/sbom-vex-taint-analysis
Automated SBOM-to-VEX pipeline using a secure multi-agent AI system to analyze CVEs, reason about exploitability, and generate signed CycloneDX VEX…
 owasp/docker-security
Getting a handle on container security
 owasp/aisvs
The AI Security Verification Standard (AISVS) focuses on providing developers, architects, and security professionals with a structured checklist to…
 owasp/packman
A documentation and tracking project with the goal of making package management systems more secure.
 owasp/owasp-model-card-security-standard
Open standard for documenting security-relevant metadata of AI models, including training data provenance, PII risk, known vulnerabilities, and…