
ClawGuard
 ny1024/clawguard
Modular security toolkit for autonomous agents providing static analysis, configuration auditing, runtime monitoring, and supply chain verification…
ai-securityanomaly-detectioncode-analysis+5
26
ny1024/clawguardModular security toolkit for autonomous agents providing static analysis, configuration auditing, runtime monitoring, and supply chain verification…
 plutosecurity/mcpwnfluence
Information about CVE-2026-27825 & CVE-2026-27826 discovered by Pluto Security and a bash script for identifying vulnerable mcp-atlassian instances…
 owasp/trisuella-aidlca-framework
Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…
 tindersec/gh-workflow-auditor
Script to audit GitHub Action Workflow files for potential vulnerabilities.
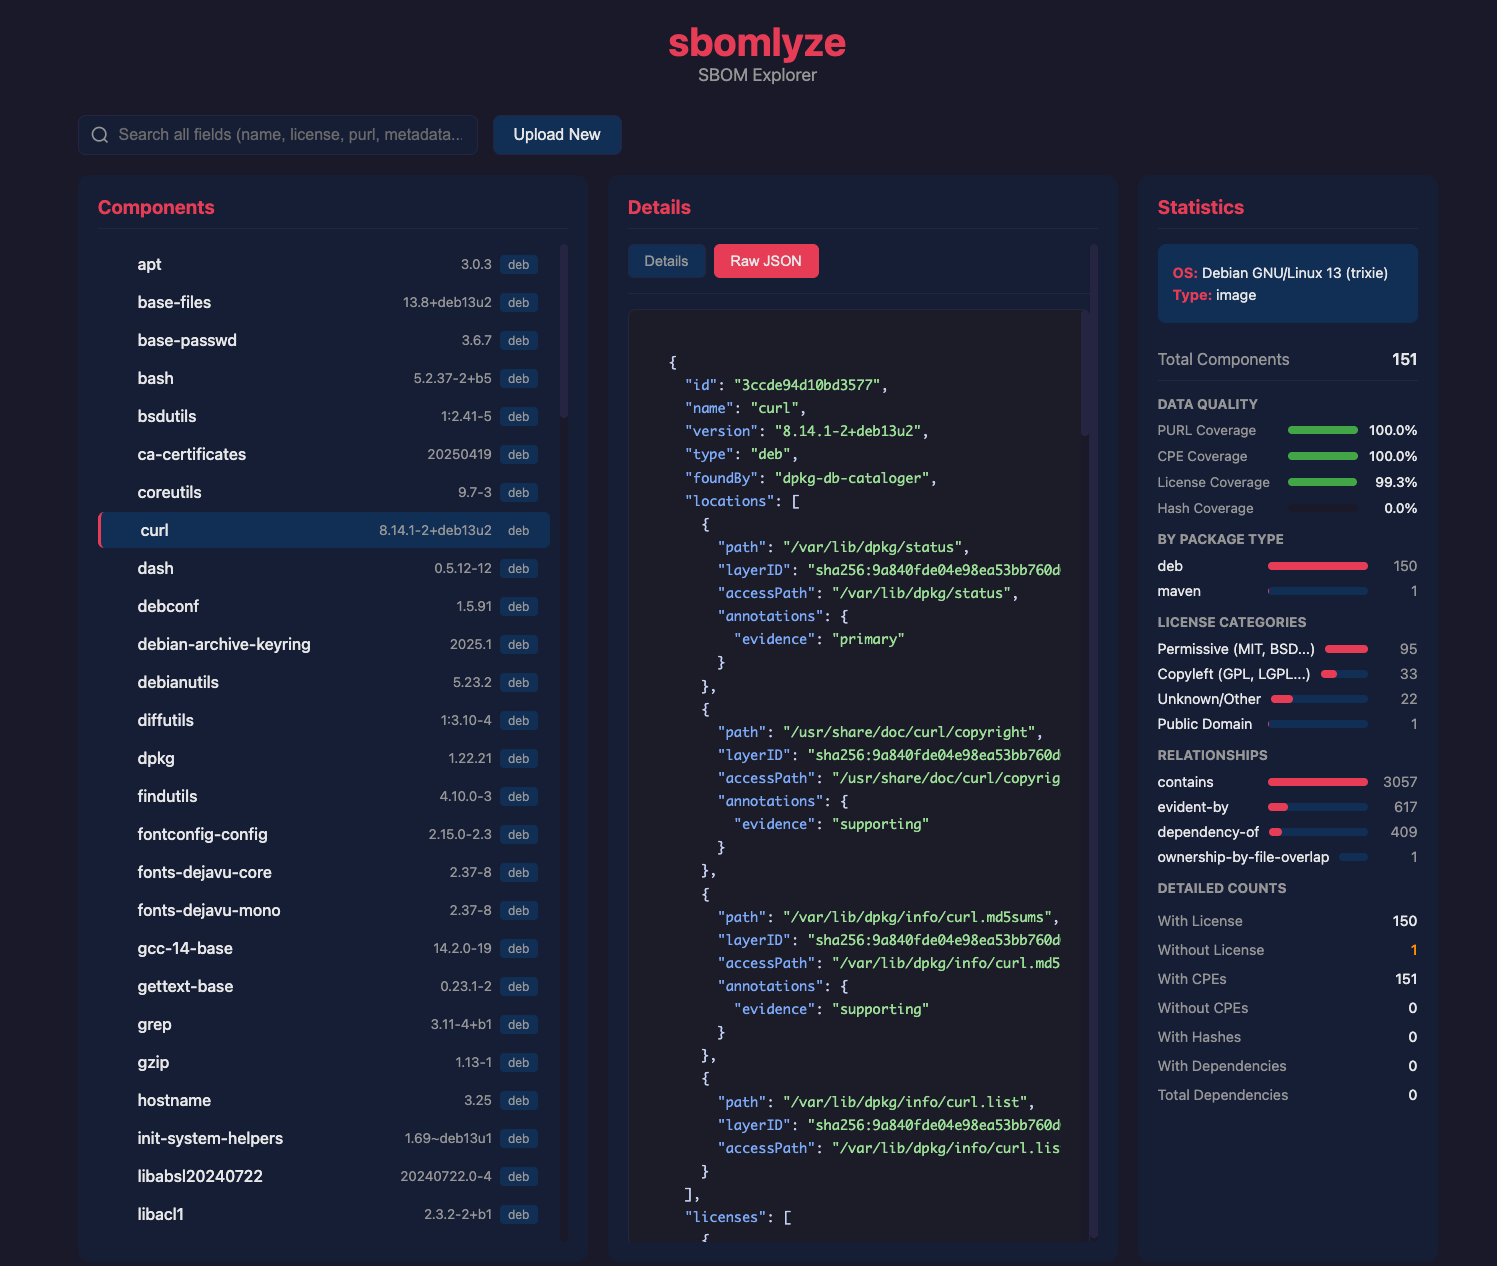 rezmoss/sbomlyze
Git diff for SBOMs—compare CycloneDX, SPDX, and Syft documents, detect tampering, and gate CI.
 xiaoqimikko/tomcat-check
查出 Spring Boot 内嵌 Tomcat 的真实版本(pom 里没有),并对每条 2026 年 CVE 同时给出 ASF 官方评级与 GitHub 评级、触发条件、以及这条会不会进 Dependabot 告警 CVE-2026-41293
 xiaoqimikko/tomcat-line-check
CVE-2026-24880: does Apache's upgrade advice actually apply to your Tomcat? Detects the fix by class presence, not version comparison. Covers…
 xiaoqimikko/jetty-line-check
CVE-2026-2332 and 4 more 2026 Jetty CVEs: which does your Jetty (or Spring Boot) build hit, and does the fixed version Jetty names even exist on…
 xiaoqimikko/netty-resolver-dns-check
Offline static checker that inspects packaged Java jars for vulnerable netty-resolver-dns versions and detects whether Spring WebClient actually uses…
 ag3ntsc4rn/autorun-audit
Find code that runs without you asking: repo files that execute on folder open (VS Code tasks, agent hooks, MCP, devcontainers) and Python…
 nomograph/kit
Verified tool registry manager. Manages developer toolchains from git-based registries.
 leonlai-tw/php-eol-cve-2026-109618-109619
Unofficial patches for PHP CVE-2026-109618 / CVE-2026-109619 (RCE, CVSS 9.2) on EOL platforms: PHP 7.3 on CentOS/RHEL 7 (Remi), PHP 5.4 on Amazon…
 betterleaks/betterleaks
Fast, configurable secrets scanner for filesystems, git history, containers, and cloud sources, with Expr-based filtering, credential validation, and…
 al0ne/linuxcheck
Linux应急处置/信息搜集/漏洞检测工具,支持基础配置/网络流量/任务计划/环境变量/用户信息/Services/bash/恶意文件/内核Rootkit/SSH/Webshell/挖矿文件/挖矿进程/供应链/服务器风险等13类70+项检查
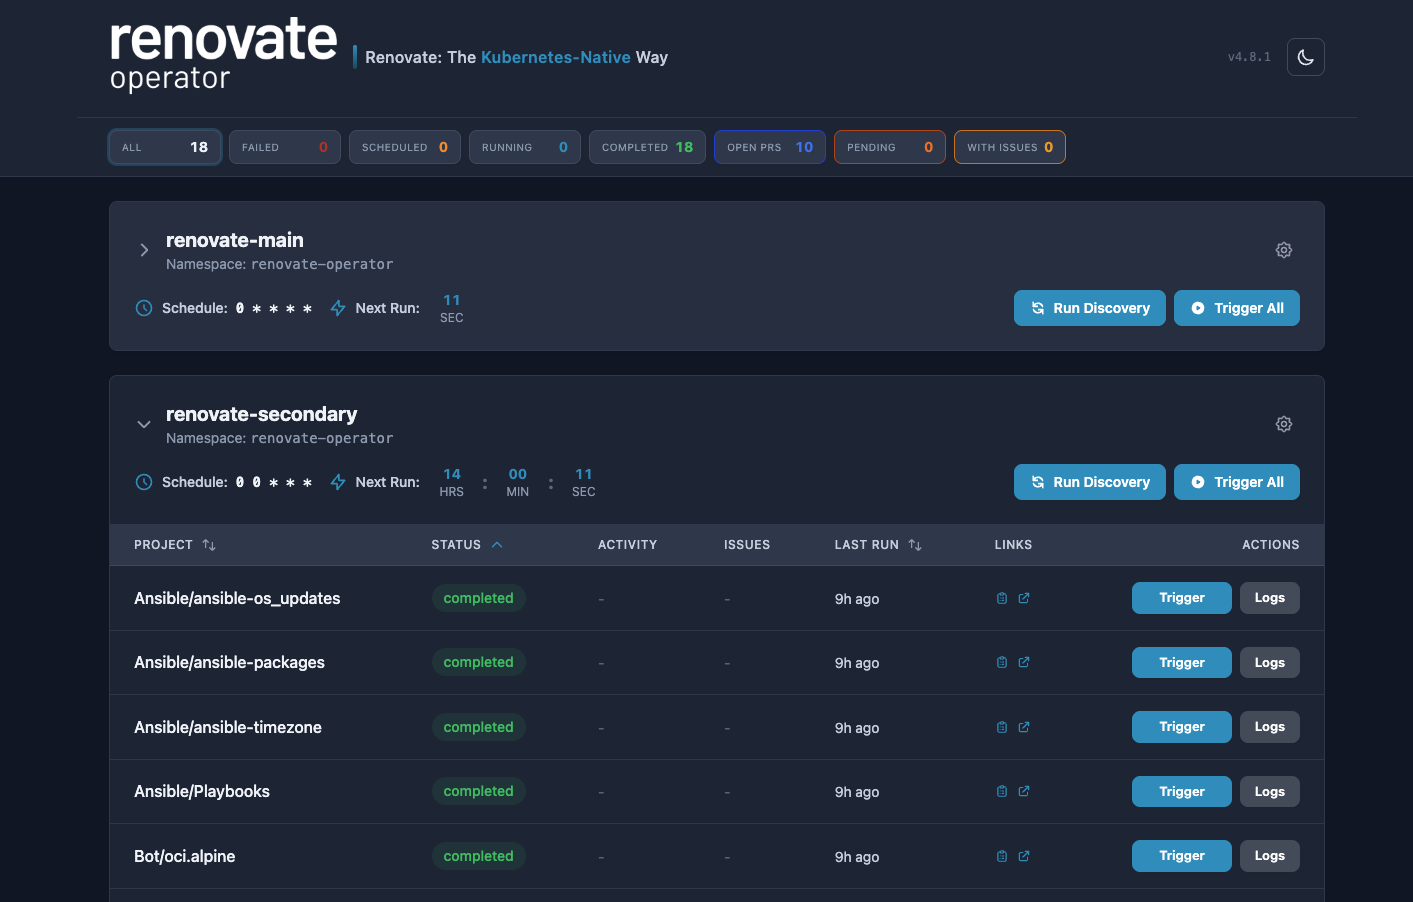 mogenius/renovate-operator
Operator to streamline renovate executions in Kubernetes
 mubix/find-wsus
Helps defenders find their WSUS configurations in the wake of CVE-2025-59287
 kaminaduck/ansible-cve-2024-3094
Ansible playbooks designed to check and remediate CVE-2024-3094 (XZ Backdoor)
 xiaoqimikko/log4j-check
log4j 2025/2026 年 7 条「配置静默失效」CVE 自查:按 CVE×模块 判定 4 个模块,结构化解析 log4j2 配置做 applicability 降噪,并算出该升到哪个版本才一次到位(6 条写 2.25.4,但有一条要 2.25.5,而它 Dependabot 报不出来)…