
CVE-2026-46595-proof
 sdodson/cve-2026-46595-proof
Go proof-of-concept demonstrating CVE-2026-46595 in golang.org/x/crypto/ssh, using symbol inspection of stripped binaries and image scans to verify…
binary-analysiscode-analysiscontainer-security+4
sdodson/cve-2026-46595-proofGo proof-of-concept demonstrating CVE-2026-46595 in golang.org/x/crypto/ssh, using symbol inspection of stripped binaries and image scans to verify…
 google/osv-scanner
Vulnerability scanner written in Go which uses the data provided by https://osv.dev
 rapticore/ore-mal-pkg-inspector
Multi-Ecosystem Malicious Package Detection and Supply Chain Security Scanner
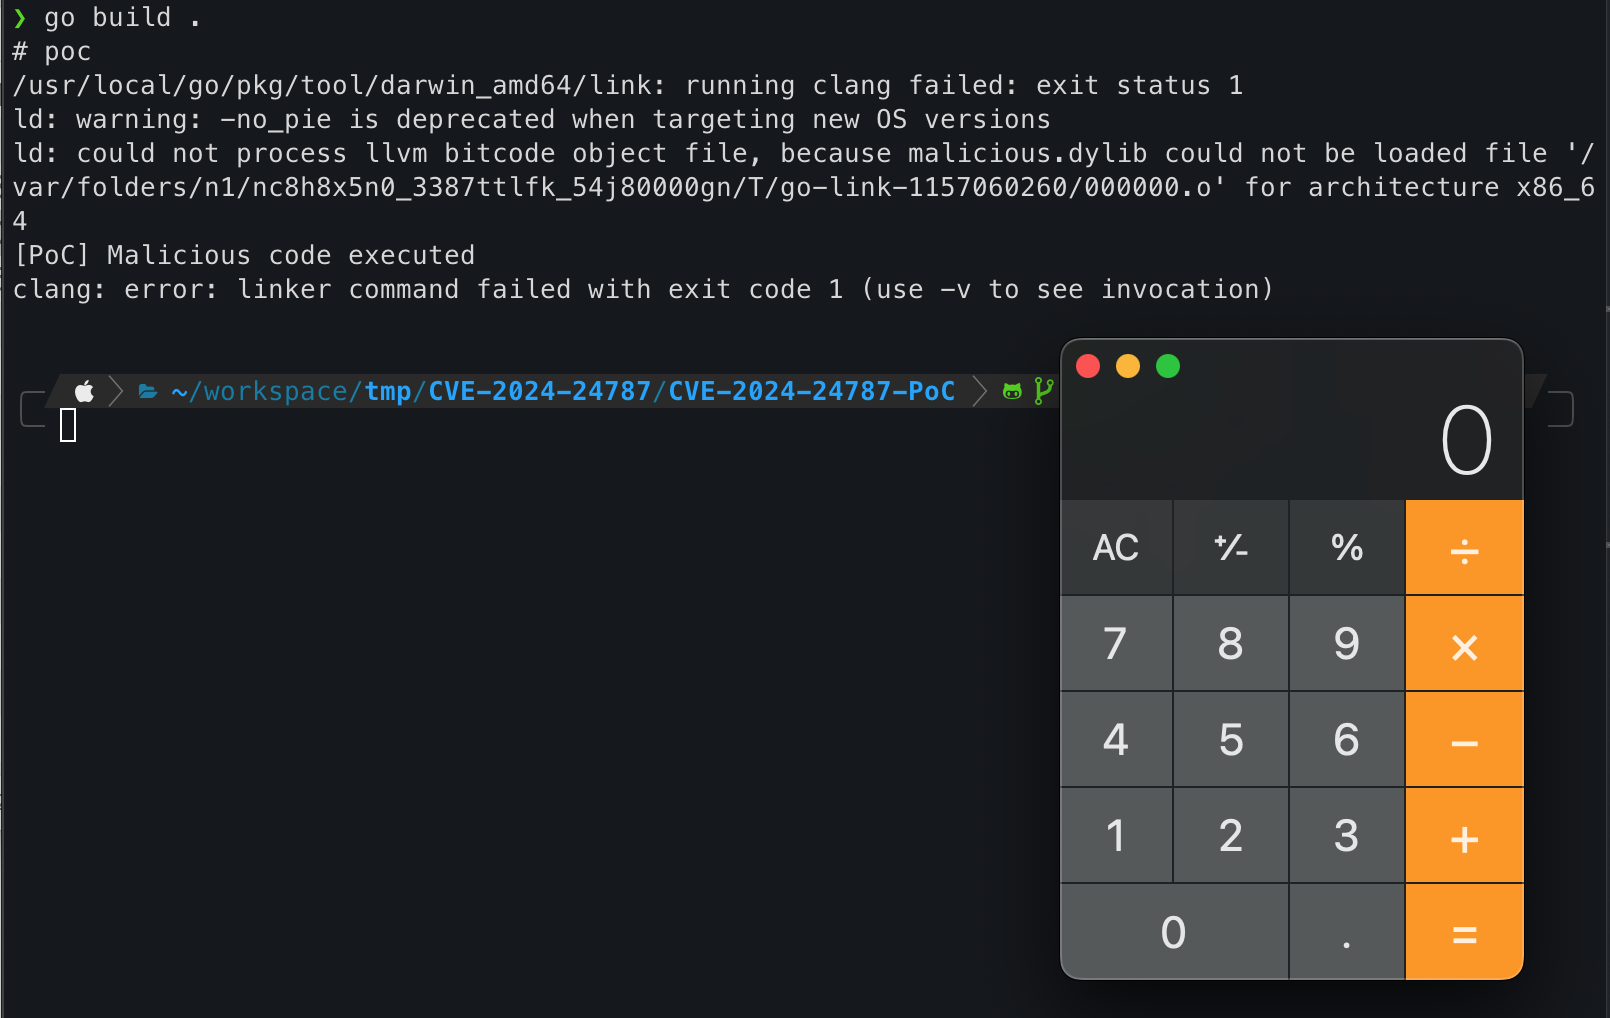 lourc0d3/cve-2024-24787-poc
CVE-2024-24787 Proof of Concept
 reposaur/reposaur
Open source compliance tool for development platforms.
 perplexityai/bumblebee
Read-only developer endpoint scanner for on-disk package, extension, and developer-tool metadata, built to check exposure to known software…
 murphysecurity/murphysec
An open source tool focused on software supply chain security. 墨菲安全专注于软件供应链安全,具备专业的软件成分分析(SCA)、漏洞检测、专业漏洞库。
 mogenius/renovate-operator
Operator to streamline renovate executions in Kubernetes
 backbay-labs/clawdstrike
Policy engine and EDR for AI agent fleets and developer workstations. Monitors tool calls, file access, network flows, and process execution with…
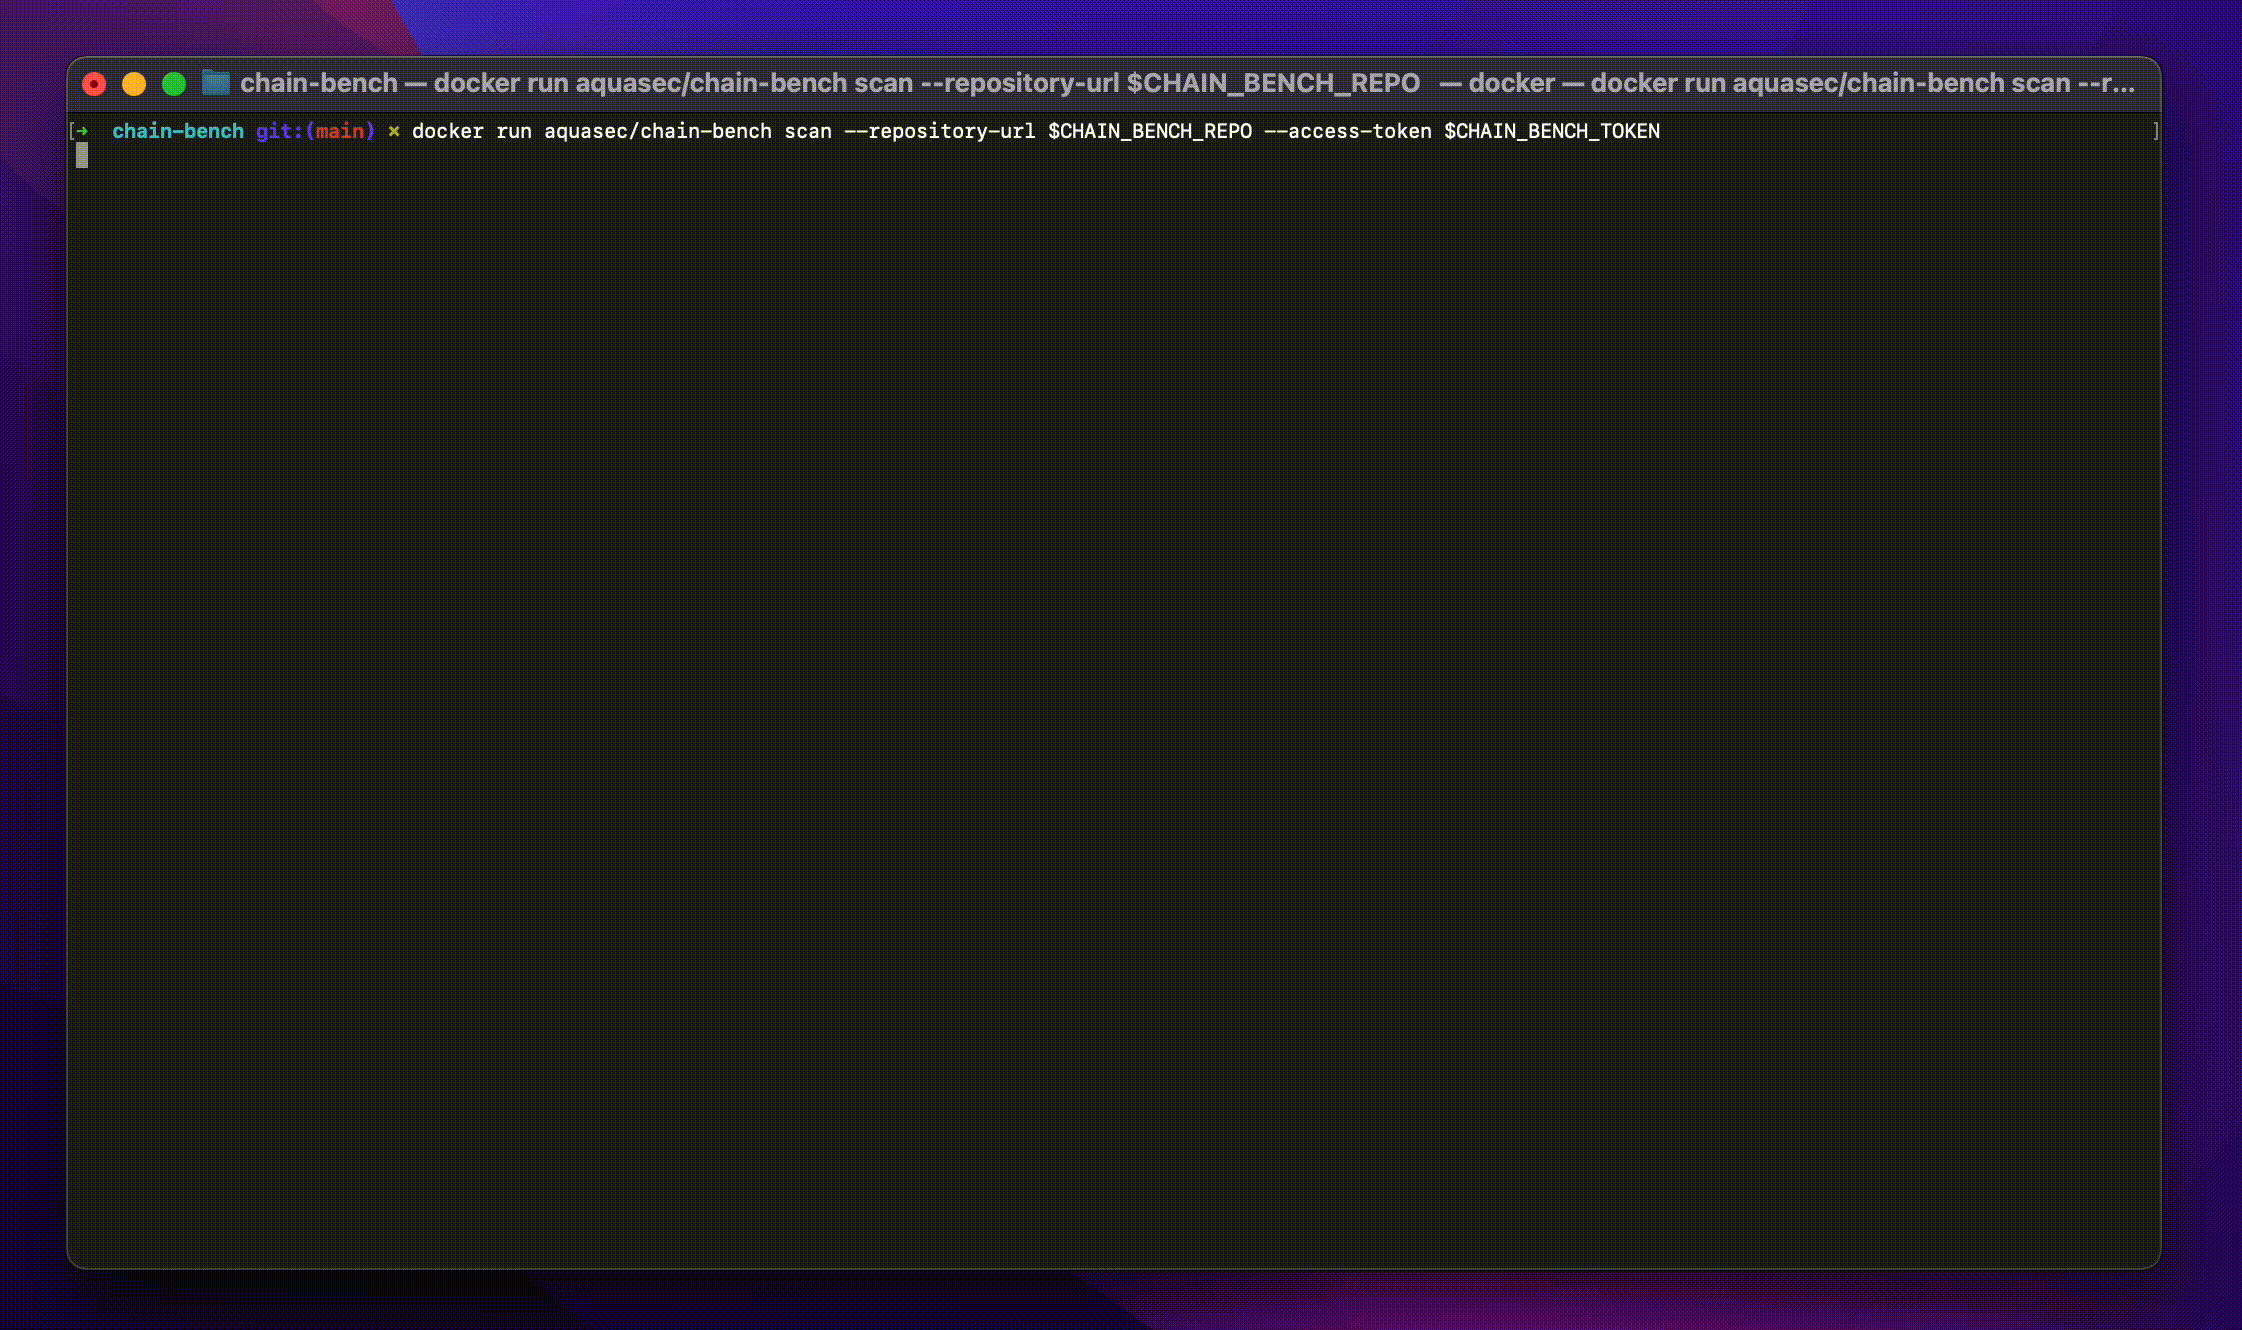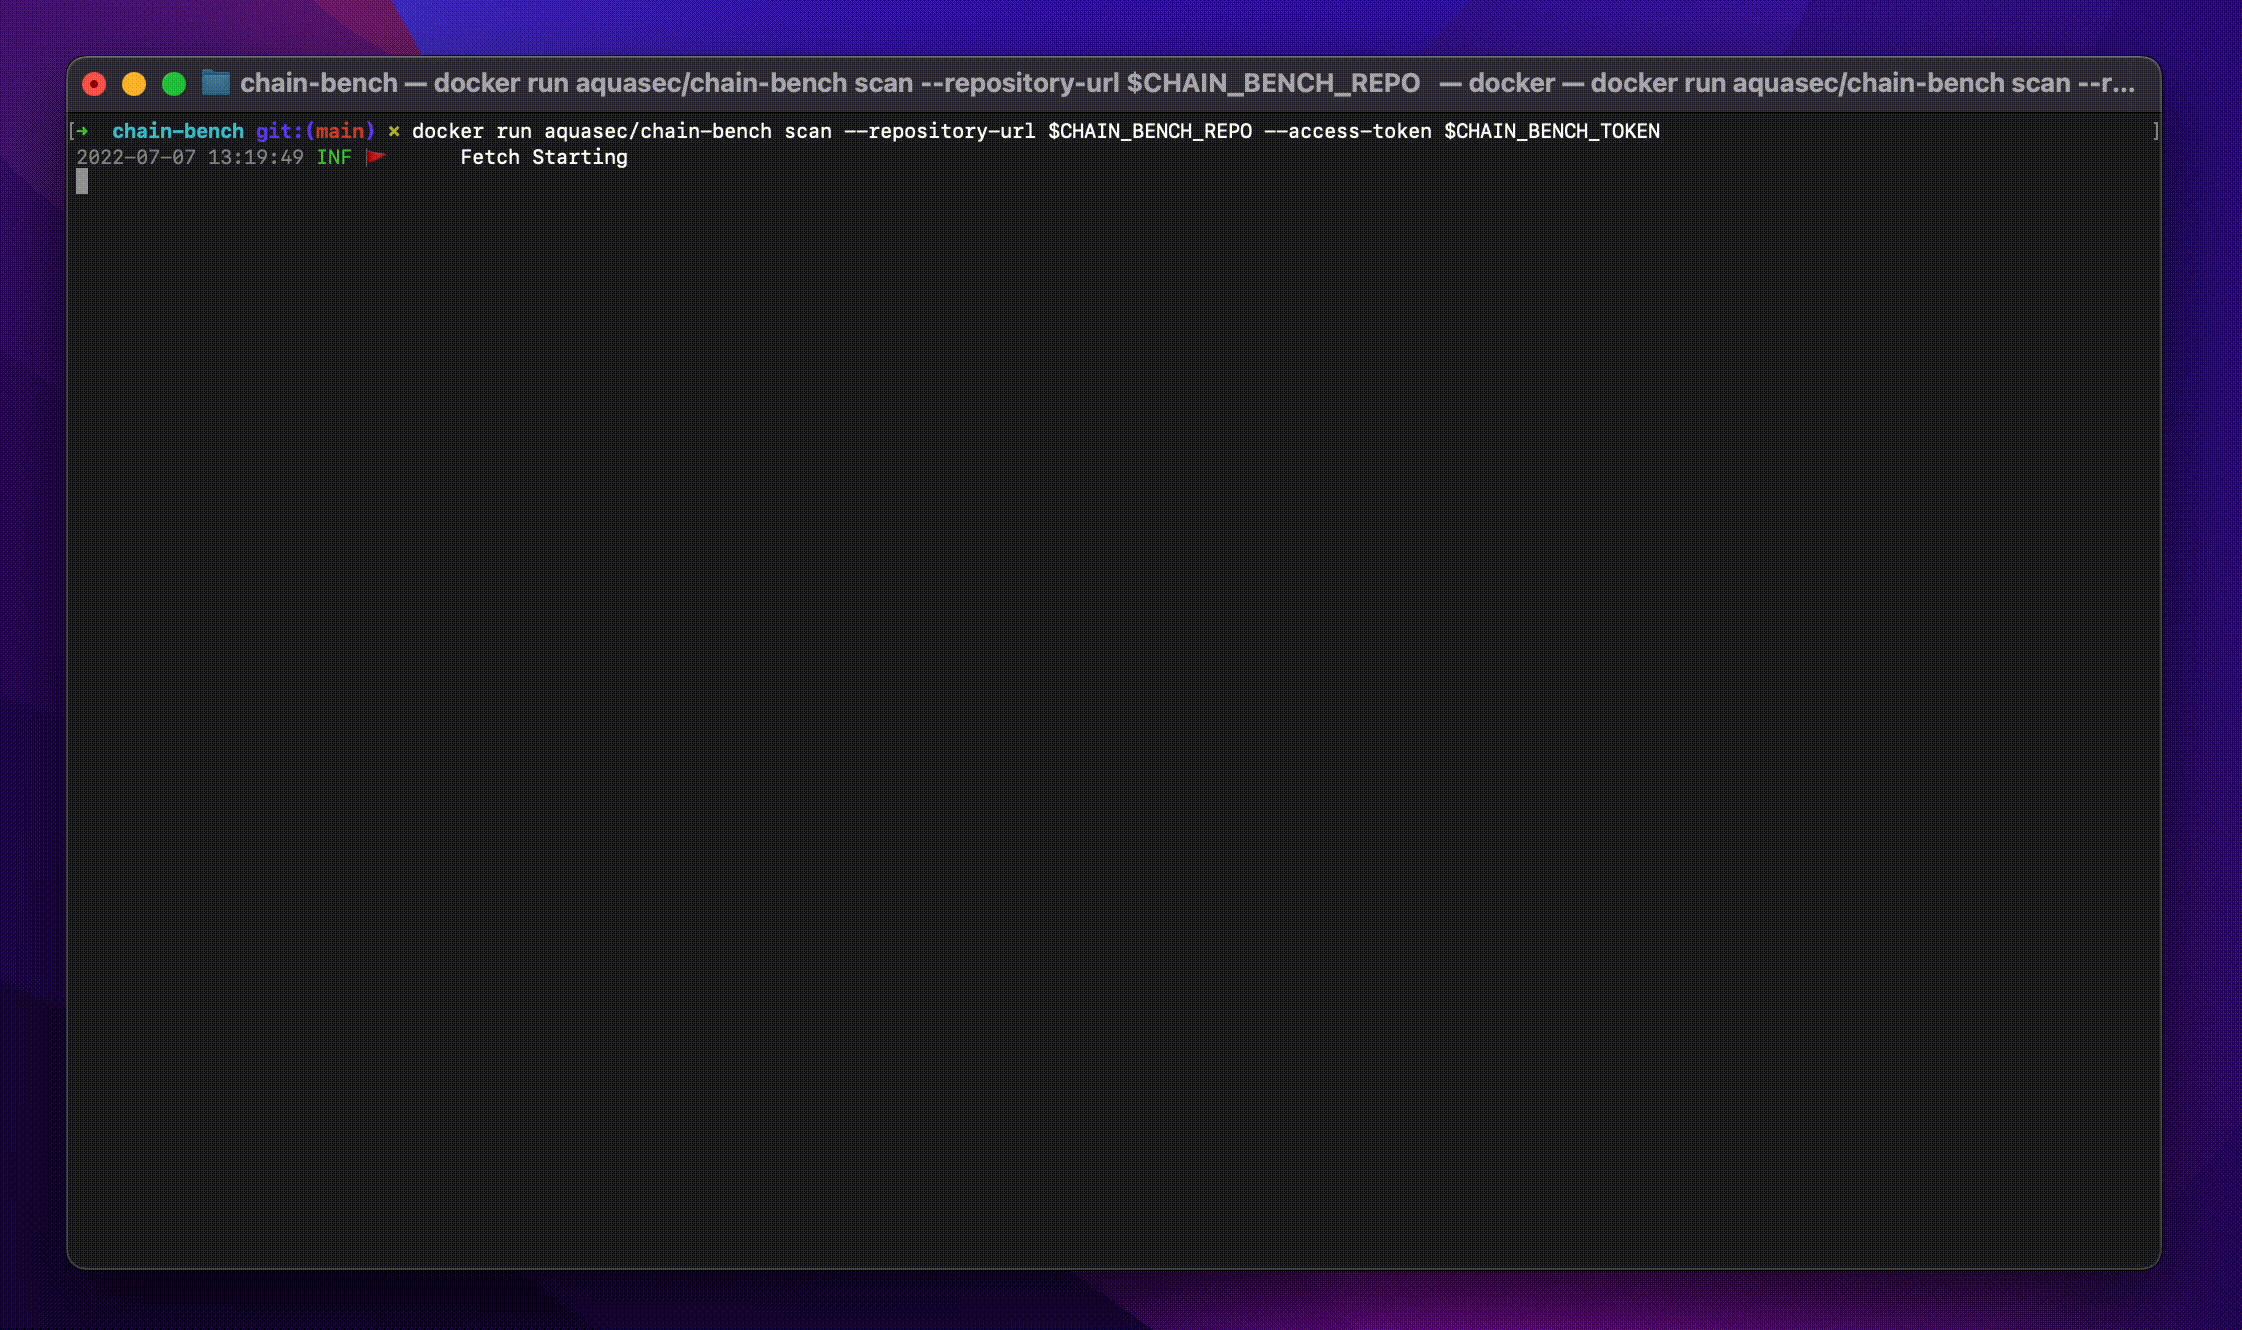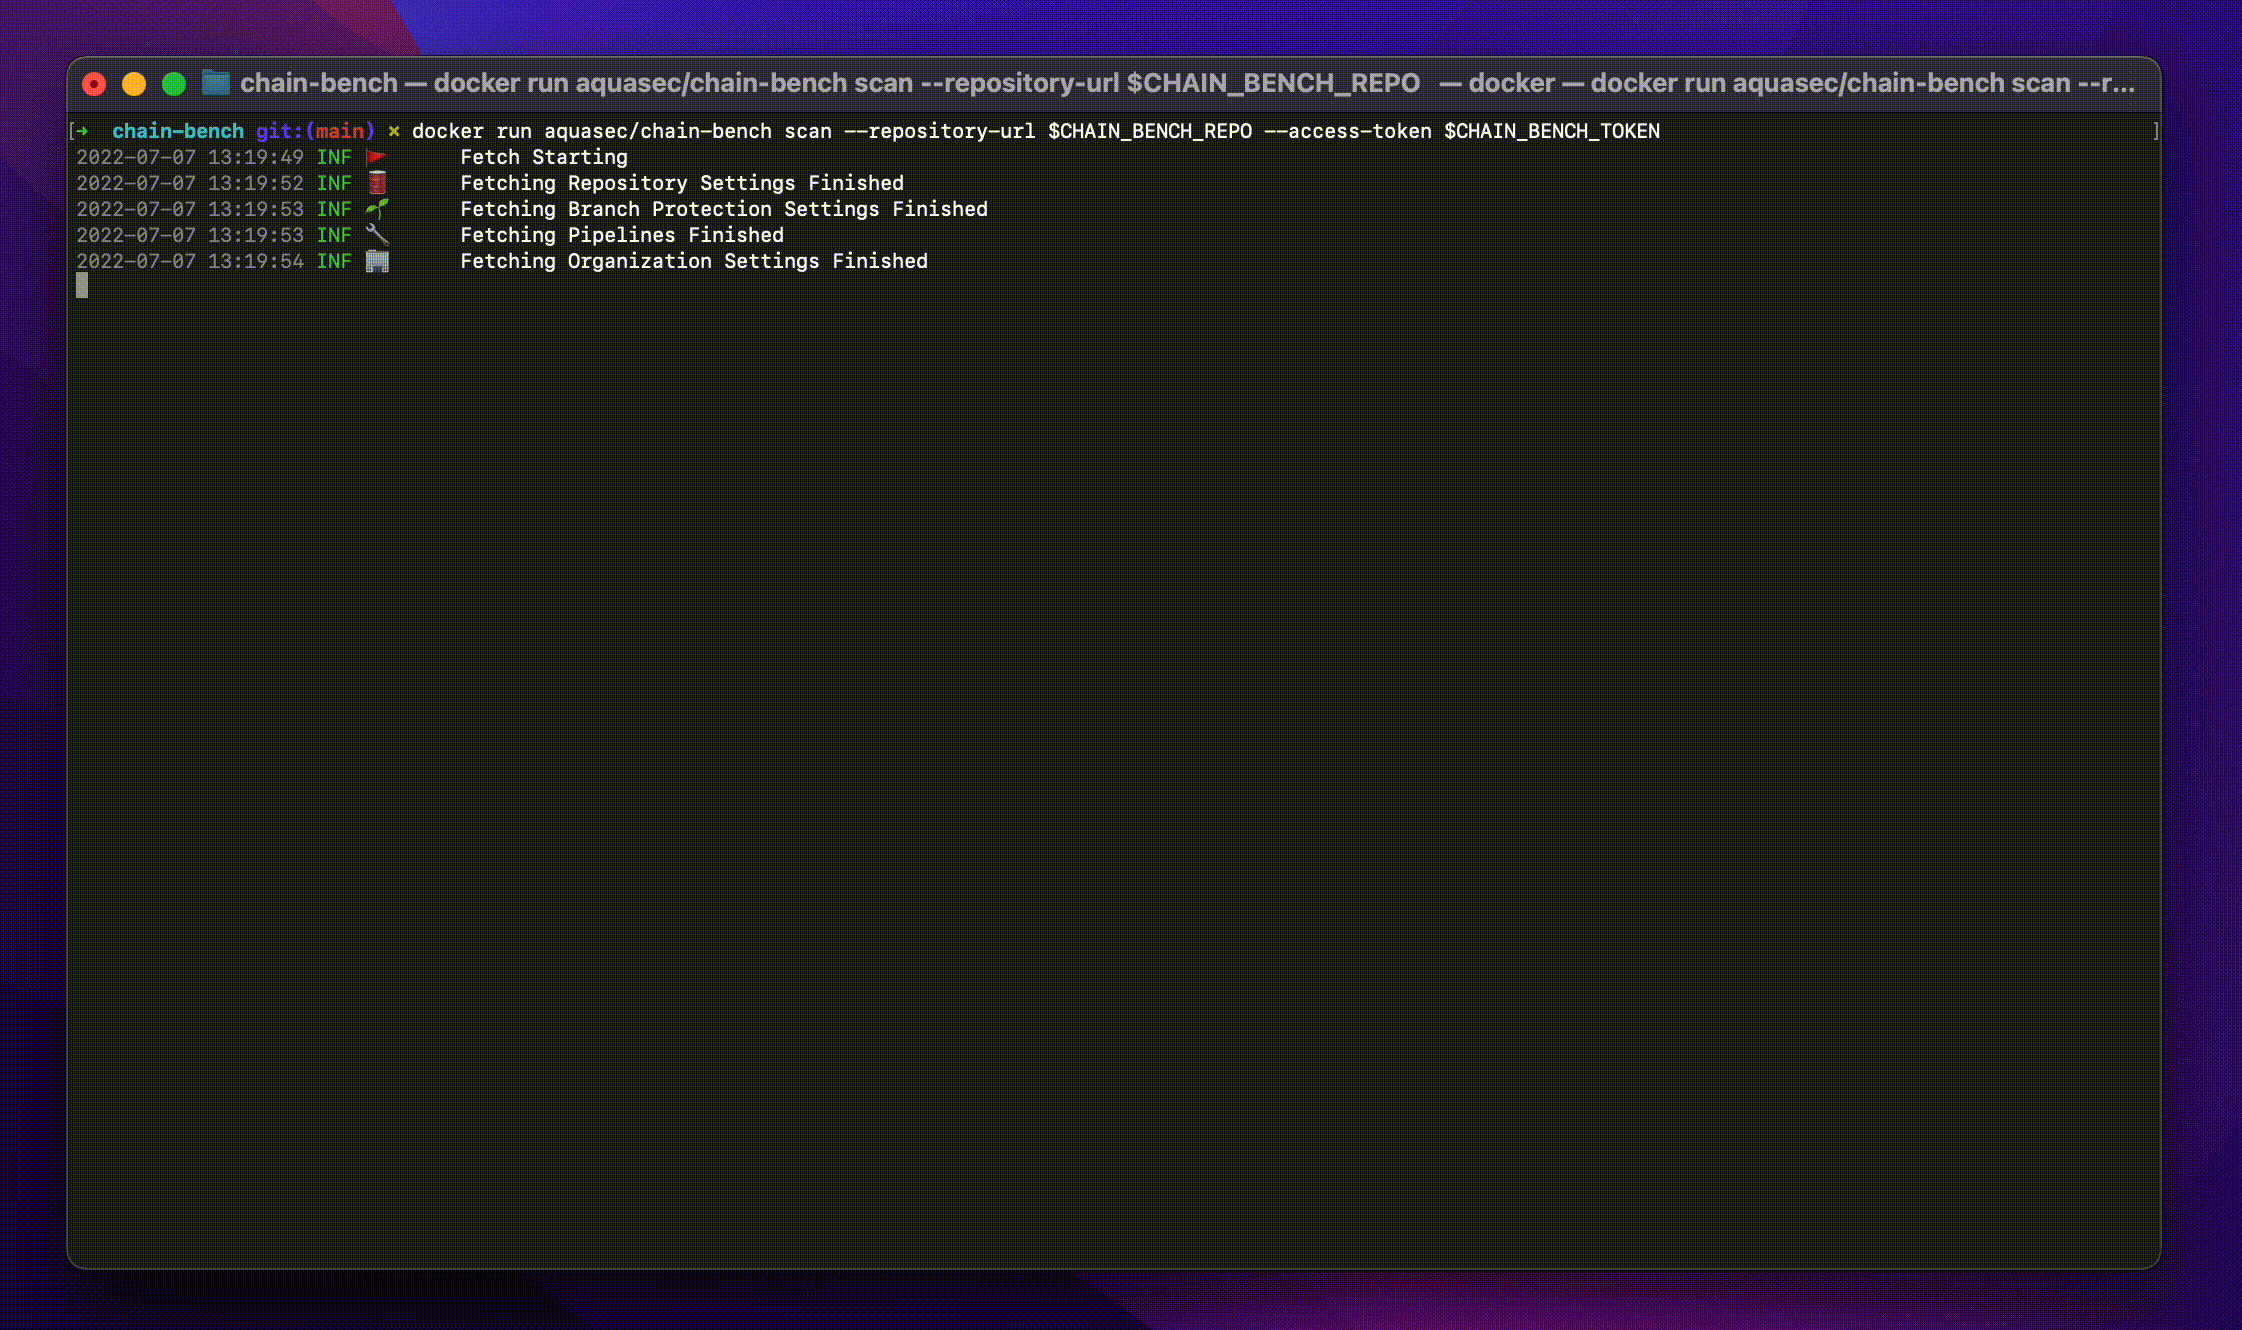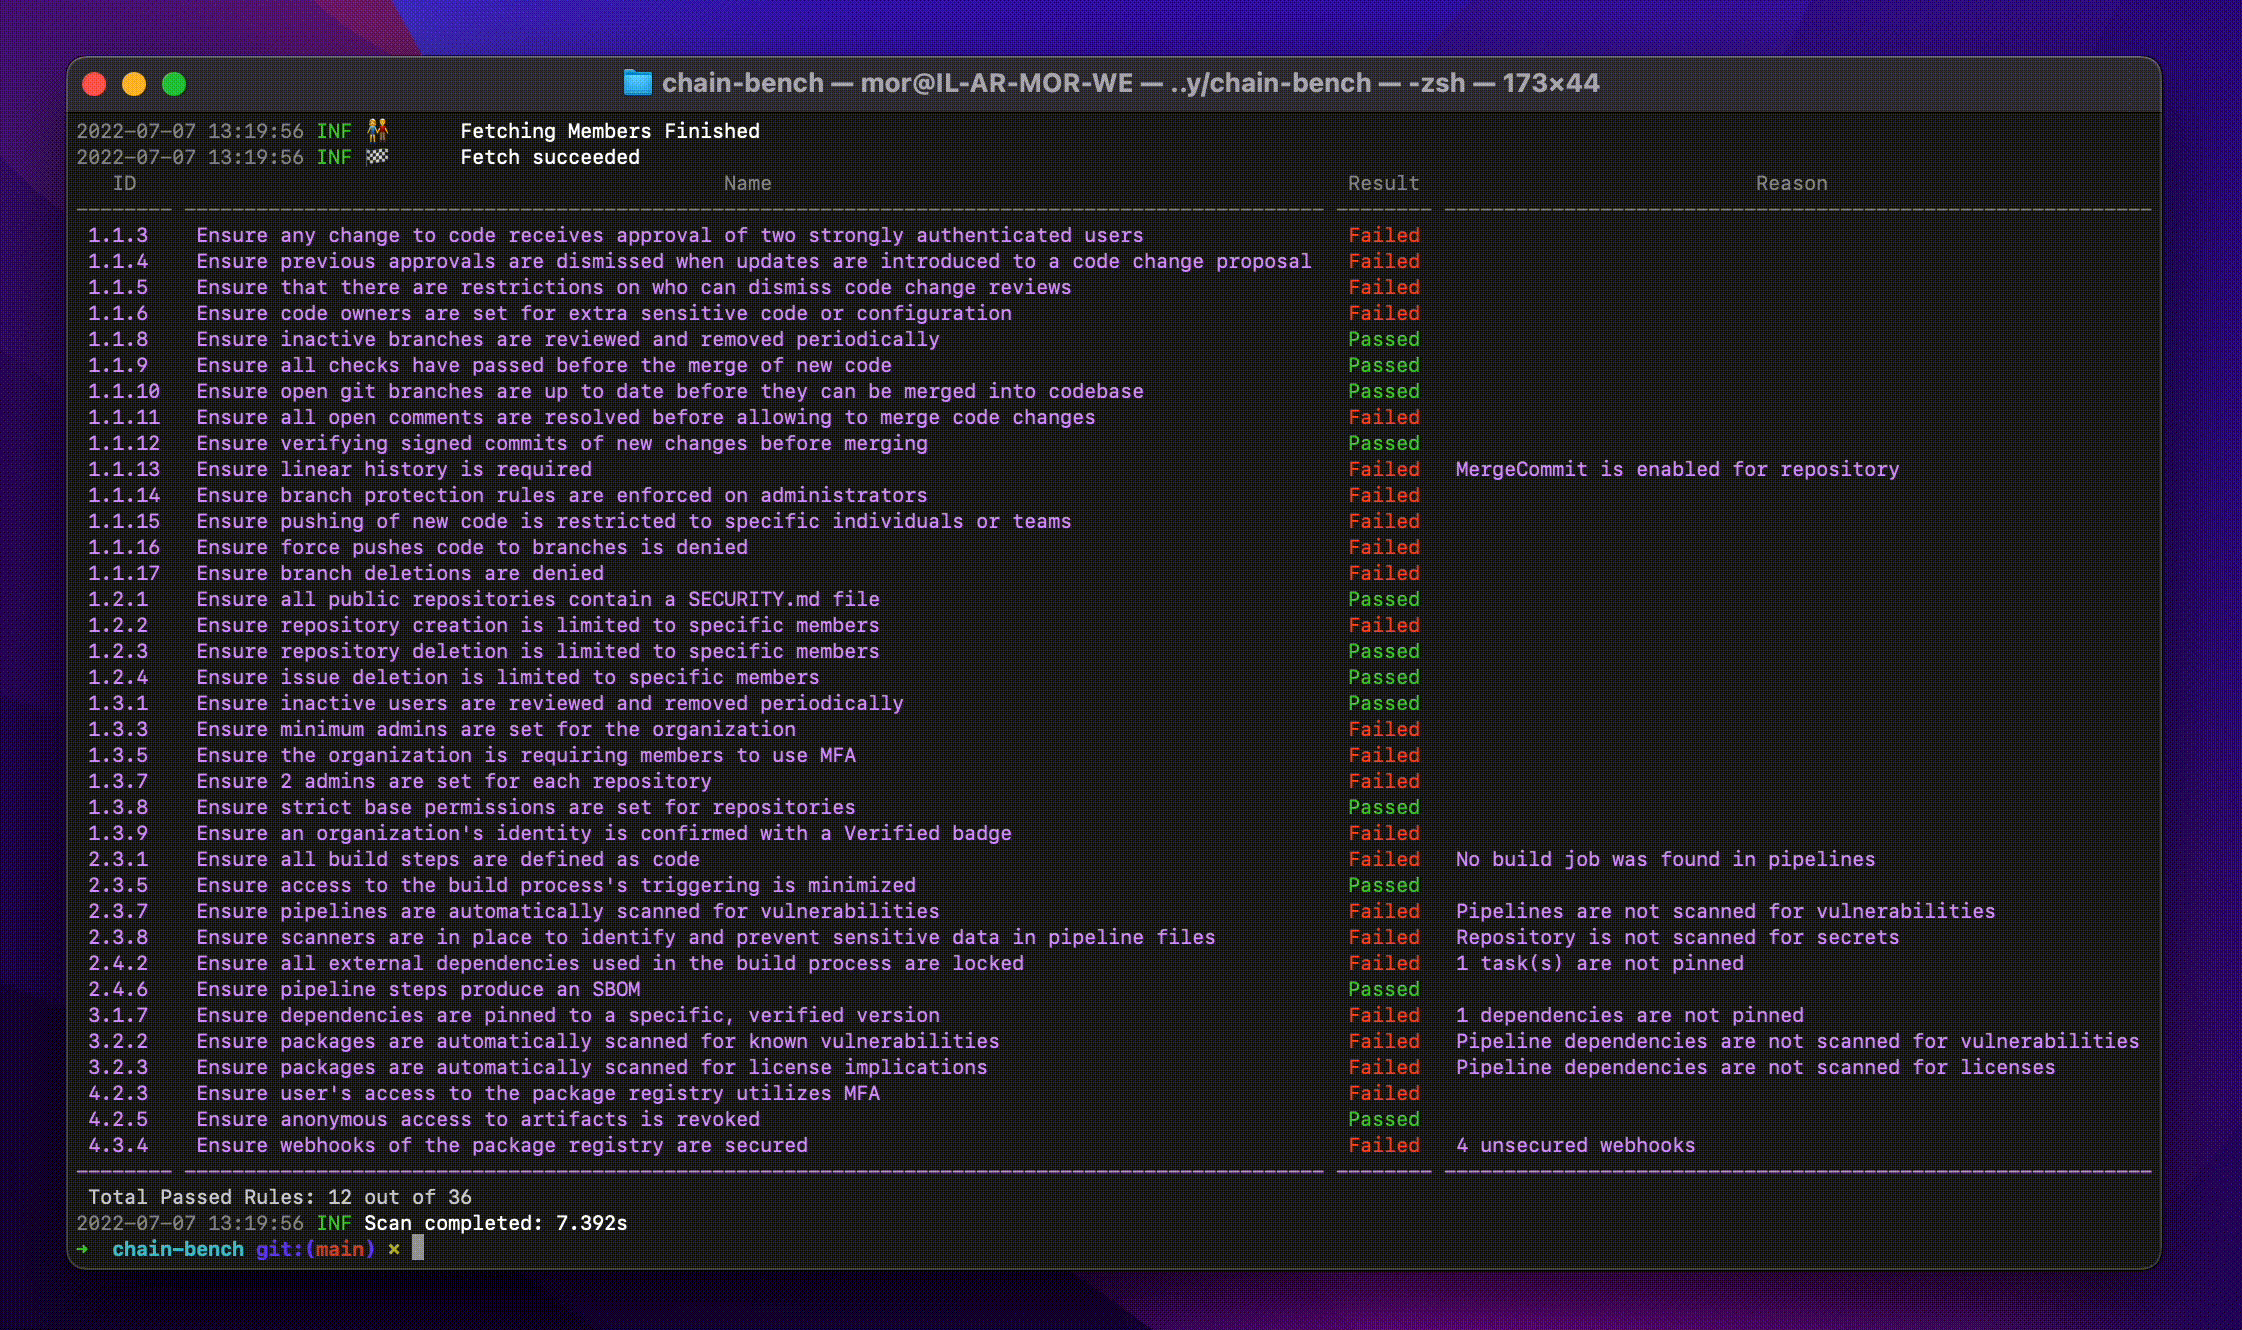 aquasecurity/chain-bench
Audits software supply chain security compliance against the CIS benchmark, scanning SCM settings, branch protections, dependencies, and CI/CD…
 knqyf263/go-rpmdb
RPM DB bindings for go
 gadievron/honeyslop
Code canaries to quickly triage hallucinated ('slop') vulnerability reports
 preflightsh/preflight
Go-based CLI tool that scans codebases for launch readiness, detecting missing configuration, security hygiene issues, secret leaks, and integration…
 clidey/deptrust
CLI and MCP server that checks package versions for known vulnerabilities across 14+ ecosystems including npm, PyPI, crates.io, Go modules, and…
 murphysecurity/libwebp-checker
A tool for finding vulnerable libwebp(CVE-2023-4863)
 winnpixie/log4noshell
A Java Agent that disables Apache Log4J's JNDI Lookup to mitigate CVE-2021-44228 ("Log4Shell").
 thelonelycoder/mojarra-2.2.13-patched
Backport of the CVE-2020-6950 security fix to Mojarra 2.2.13, providing a patched jsf-impl JAR with minimal, reviewable changes for legacy…
 katekeiroz-dev/golang-x-text
golang.org/x/text v0.33.0 backport of CVE-2026-56852 (GO-2026-5970) for Go 1.24