
xzutils_backdoor_obfuscation
 thomrgn/xzutils_backdoor_obfuscation
Script to obfuscate a payload the same way as it was done by the XZ utils attack (CVE-2024-3094)
binary-exploitationeducationexploitation+4
thomrgn/xzutils_backdoor_obfuscationScript to obfuscate a payload the same way as it was done by the XZ utils attack (CVE-2024-3094)
 bkhablenko/cve-2017-8046
Demonstrates exploitation of CVE-2017-8046 in a Spring Boot application, including a SpEL injection payload and dependency-check verification for…
 ilhomjonr/cve-2026-67595
CVE-2026-67595 — Embedded malicious JavaScript (spyware) in VaahCMS 2.0.0–2.3.4 official releases. CVSS 8.1. Advisory + detection.
 mbadanoiu/mvn_pwn
Malicious Maven pom.xml that uses "groovy-maven-plugin" to get RCE
 airineiandrei/tarmageddon-cve-2025-62518-
PoC for CVE-2025-62518 demonstrating tar archive smuggling via tokio-tar PAX header parsing, creating malicious payloads and a vulnerable extractor…
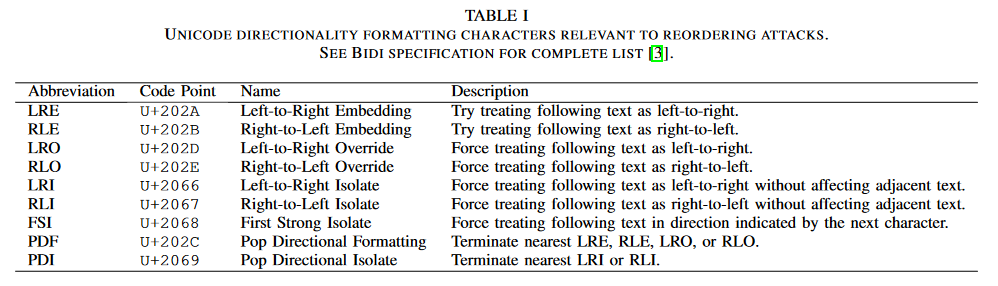 simplylu/cve-2021-42574
Generate malicious files using recently published bidi-attack (CVE-2021-42574)
 diegogarciayala/cve-2024-24590-clearml-rce-cmd-poc
CVE-2024-24590 ClearML RCE&CMD POC
 oxydev2/clearml-cve-2024-24590
Proof of concept for CVE-2024-24590
 george0papasotiriou/cve-2026-23001-hugging-face-transformers-model-deserialization-arbitrary-code-via-pickle-
Proof-of-concept for CVE-2026-23001: demonstrates RCE through unsafe pickle deserialization in Hugging Face Transformers by crafting a malicious…
 bfengj/cve-2024-32002-exploit
Proof-of-concept exploit for CVE-2024-32002, a Git submodule vulnerability enabling arbitrary code execution via crafted repositories and symlinks.
 theth1nk3r/cve-2020-27955
cve-2020-27955
 junnythemarksman/cve-2024-24590
Deserialization of untrusted data can occur in versions 0.17.0 to 1.14.2 of the client SDK of Allegro AI’s ClearML platform, enabling a maliciously…
 zerbaliy3v/cve-2018-6574-exploit
CVE-2018-6574 this vulnerability impacts Golang go get command and allows an attacker to gain code execution on a system by installing a malicious…
 saptaktdk/go-get-rce
This is the exploit of CVE-2018-6574: go get RCE