
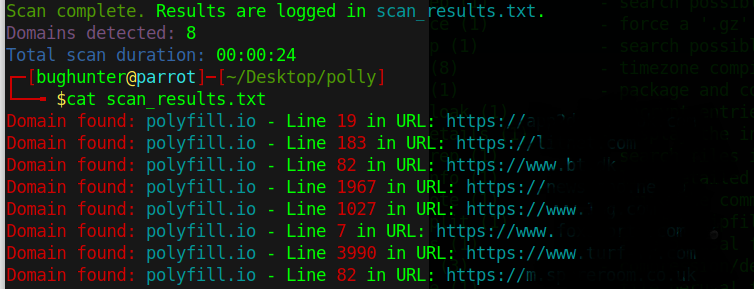
CVE-2024-38526
 putget/cve-2024-38526
CVE-2024-38526 - Polyfill Scanner
crawlerinformation-gatheringscripting-automation+3
putget/cve-2024-38526CVE-2024-38526 - Polyfill Scanner
 kevinslin/safe-npm
Safely install NPM packages
 knqyf263/go-rpmdb
RPM DB bindings for go
 murrez/cve-2026-101894
Python PoC for CVE-2026-101894: symlink-chain path traversal in @xhmikosr/decompress. Includes local Node lab, lockfile version scan, and mass…
 katekeiroz-dev/golang-x-text
golang.org/x/text v0.33.0 backport of CVE-2026-56852 (GO-2026-5970) for Go 1.24
 workshops-de/google_gax
Patched google_gax 0.4.1 for Tesla 1.18.3+ compatibility (CVE-2026-48598)
 sassoftware/jackson
This repository provides a comprehensive security remediation of denial-of-service and allocation of resources without limits or throttling security…
 njawalkar/apache-commons-lang2
Apache's commons-lang2 v2.6 with a backported fix for CVE-2025-48924
 nanopathi/external_expat_aosp10_r33_cve-2022-22822tocve-2022-22827
Patched version of the Expat XML parser library addressing multiple CVEs (CVE-2022-22822 through CVE-2022-22827) for AOSP 10 r33, providing…
 khayashi4337/lodash.template-fixed
Fork of lodash.template with CVE-2021-23337 fix (command injection via variable option)
 ryancnelson/patched-bash-4.3
patched-bash-4.3 for CVE-2014-6271
 shoucheng3/codehaus-plexus__plexus-archiver_cve-2023-37460_4-7-1
Java library for creating and extracting archives (ZIP, tar, JAR) with integrated security patch for a reported vulnerability, used as a dependency…
 certifi/python-certifi
(Python Distribution) A carefully curated collection of Root Certificates for validating the trustworthiness of SSL certificates while verifying the…
 theupdateframework/python-tuf
Python reference implementation of The Update Framework (TUF)
 aquasecurity/trivy-java-db
Builds a SQLite database of Maven artifacts (ArtifactID, GroupID, Version, SHA1) for Trivy's Java component vulnerability detection, enabling scans…
 aquasecurity/secfixes-tracker
Forked from https://gitlab.alpinelinux.org/kaniini/secfixes-tracker
 aquasecurity/vexhub-crawler
Collect VEX documents and update VEX Hub
 niffyhunt/wraithwall-toolkit
Deception-engineering tools pulled from a production platform that takes live attacker traffic, supply-chain canary tokens, honeypot logs → MITRE…