
CVE-2021-44228-Scanner
 logpresso/cve-2021-44228-scanner
Vulnerability scanner and mitigation patch for Log4j2 CVE-2021-44228
configuration-auditingincident-responselog-analysis+3
861
logpresso/cve-2021-44228-scannerVulnerability scanner and mitigation patch for Log4j2 CVE-2021-44228
 visma-prodsec/confused
Tool to check for dependency confusion vulnerabilities in multiple package management systems
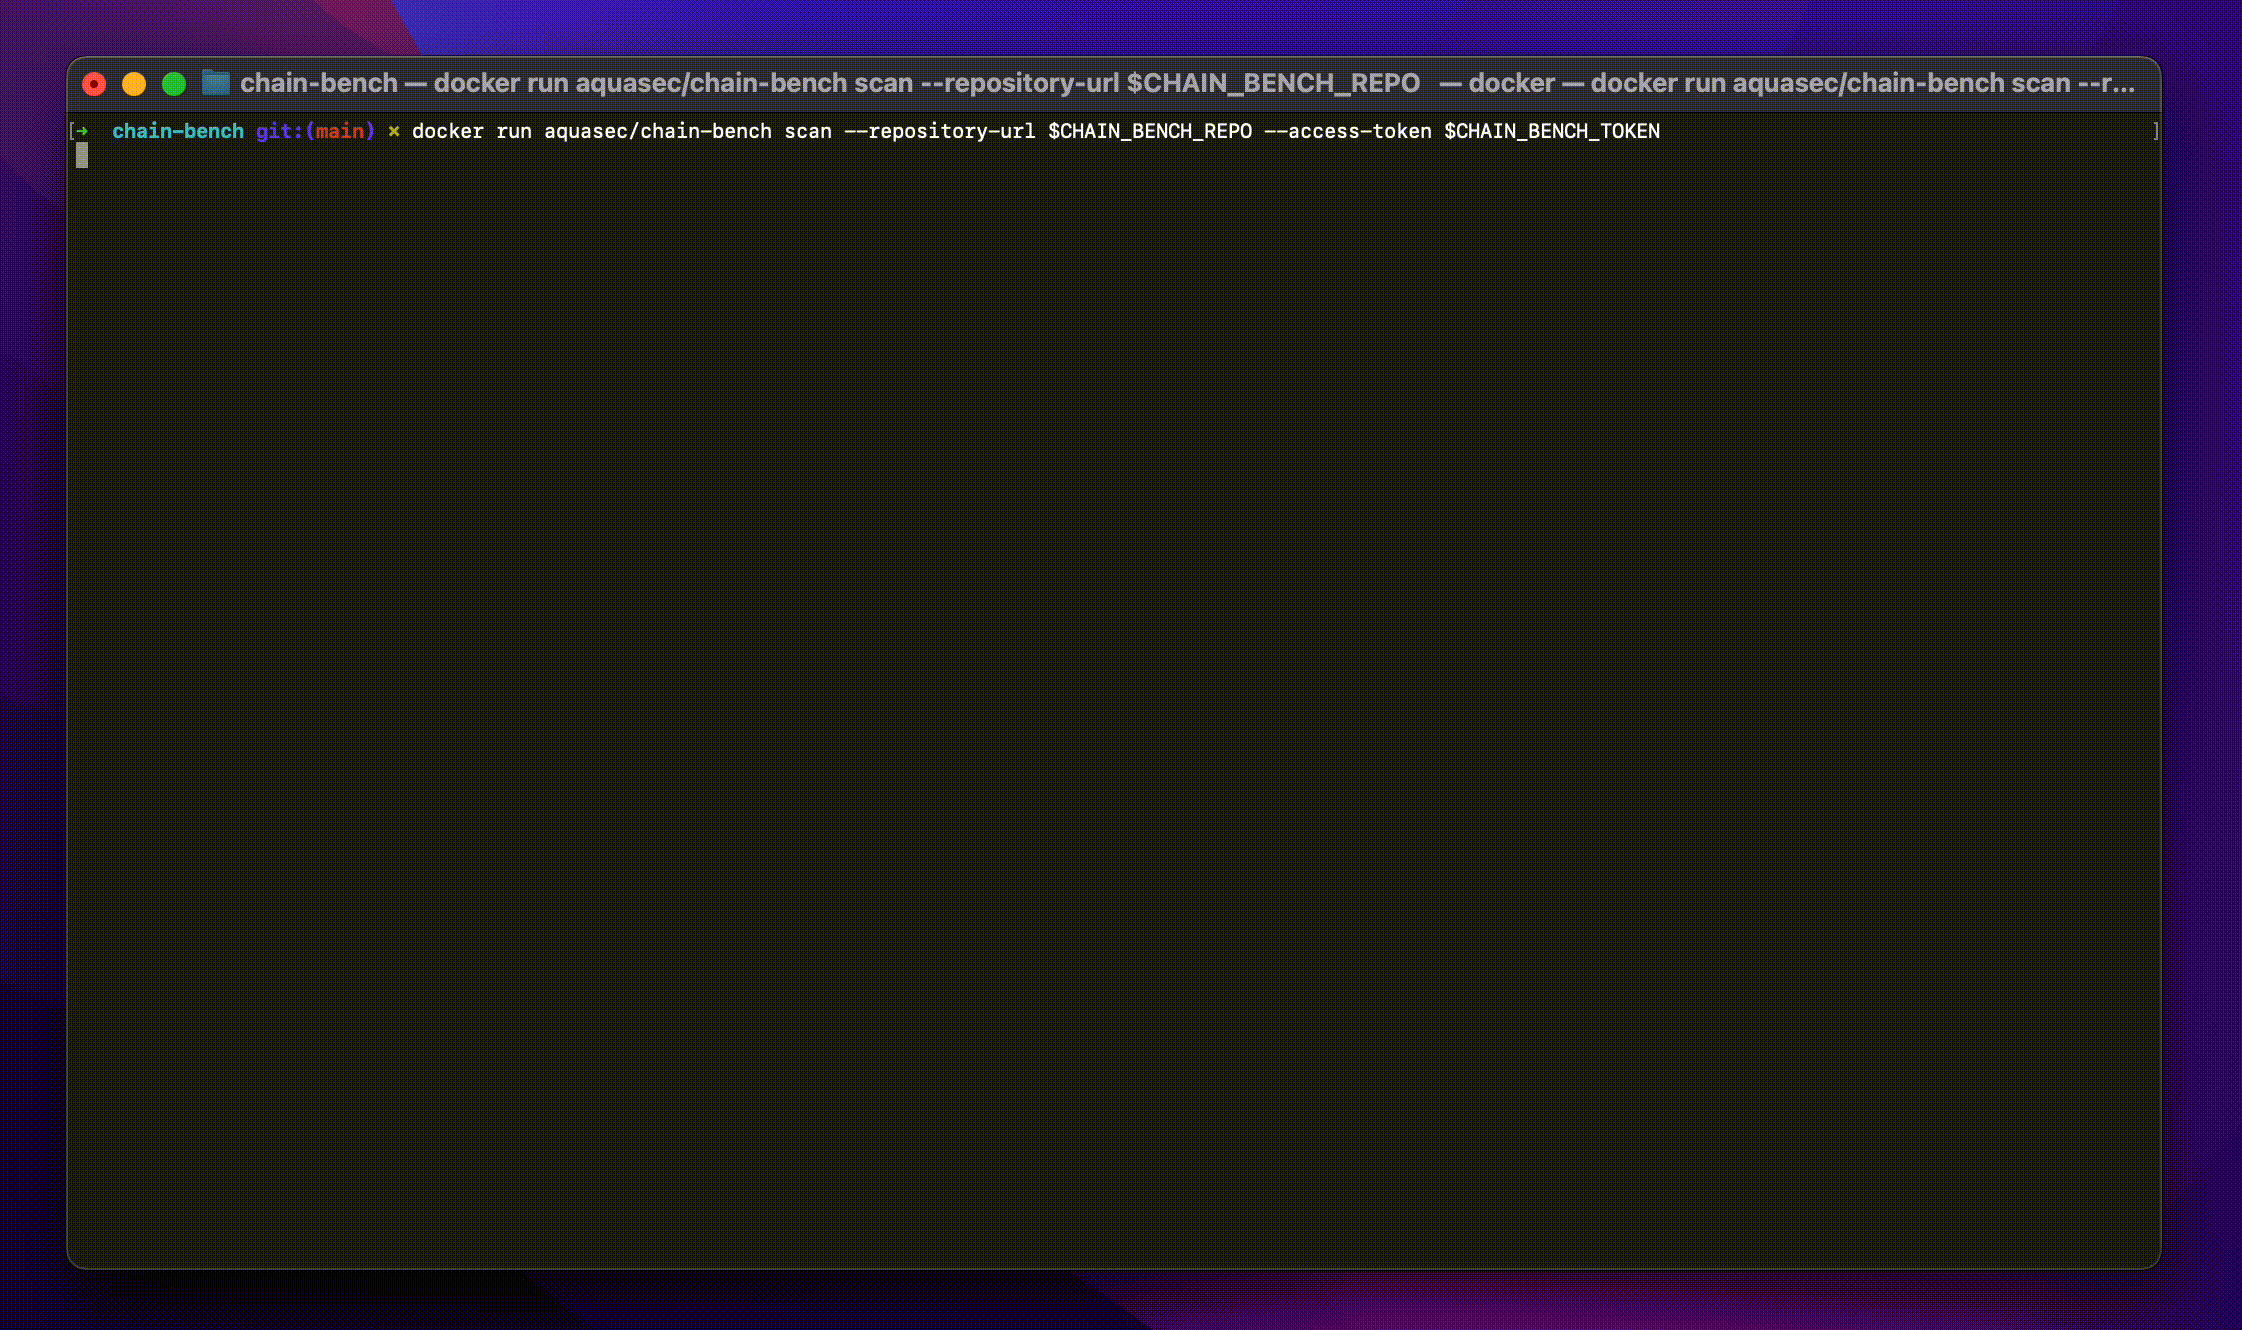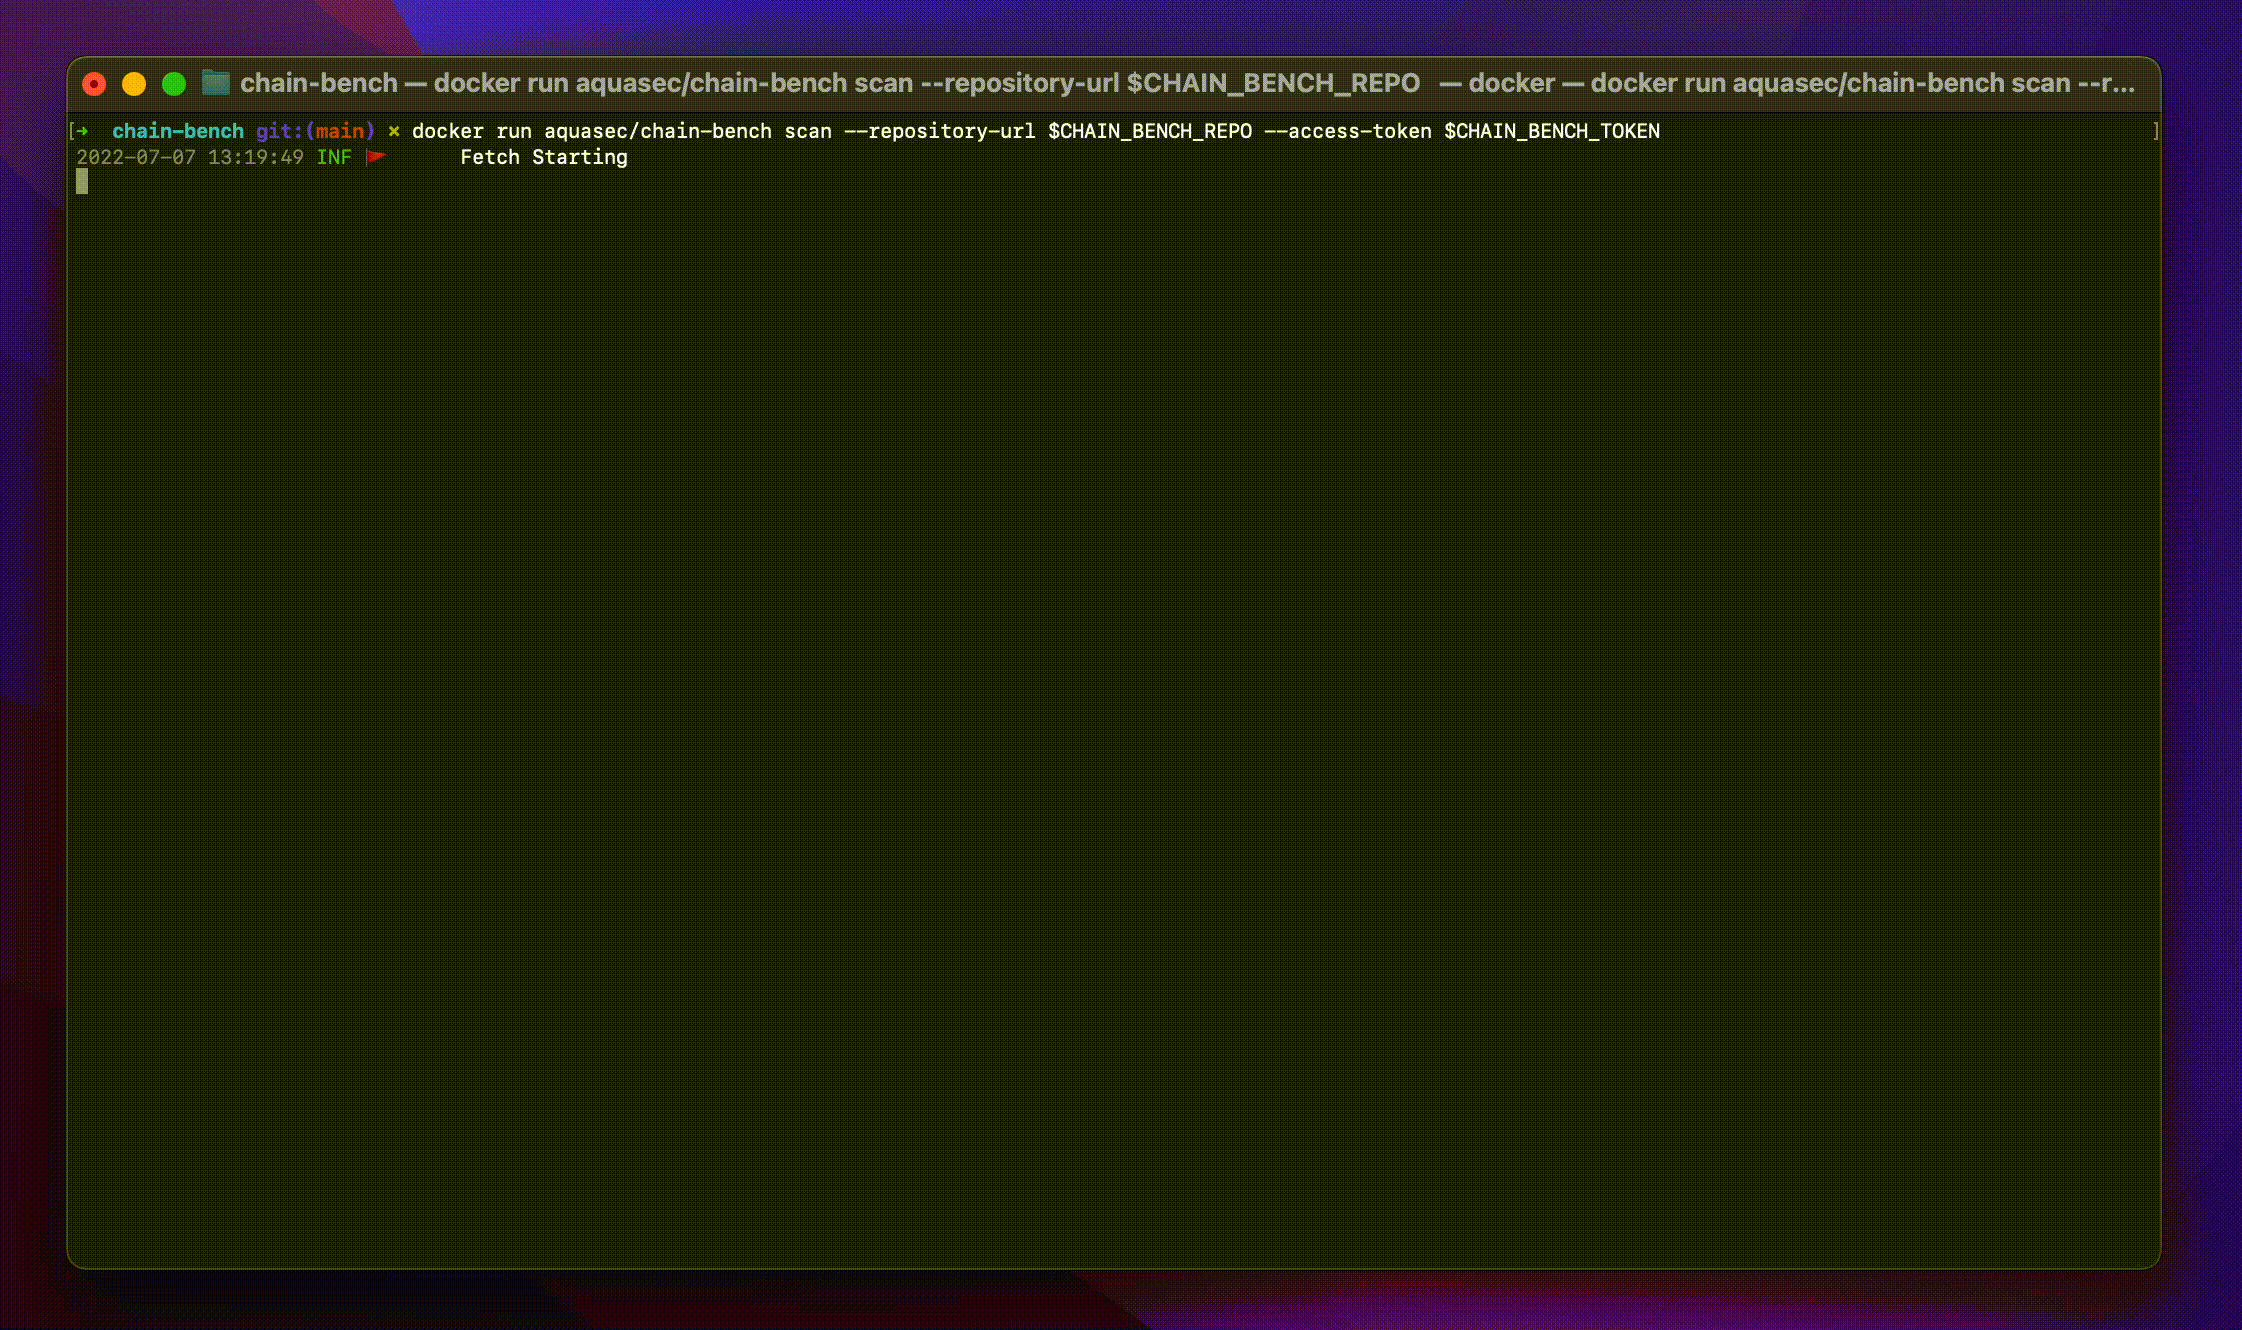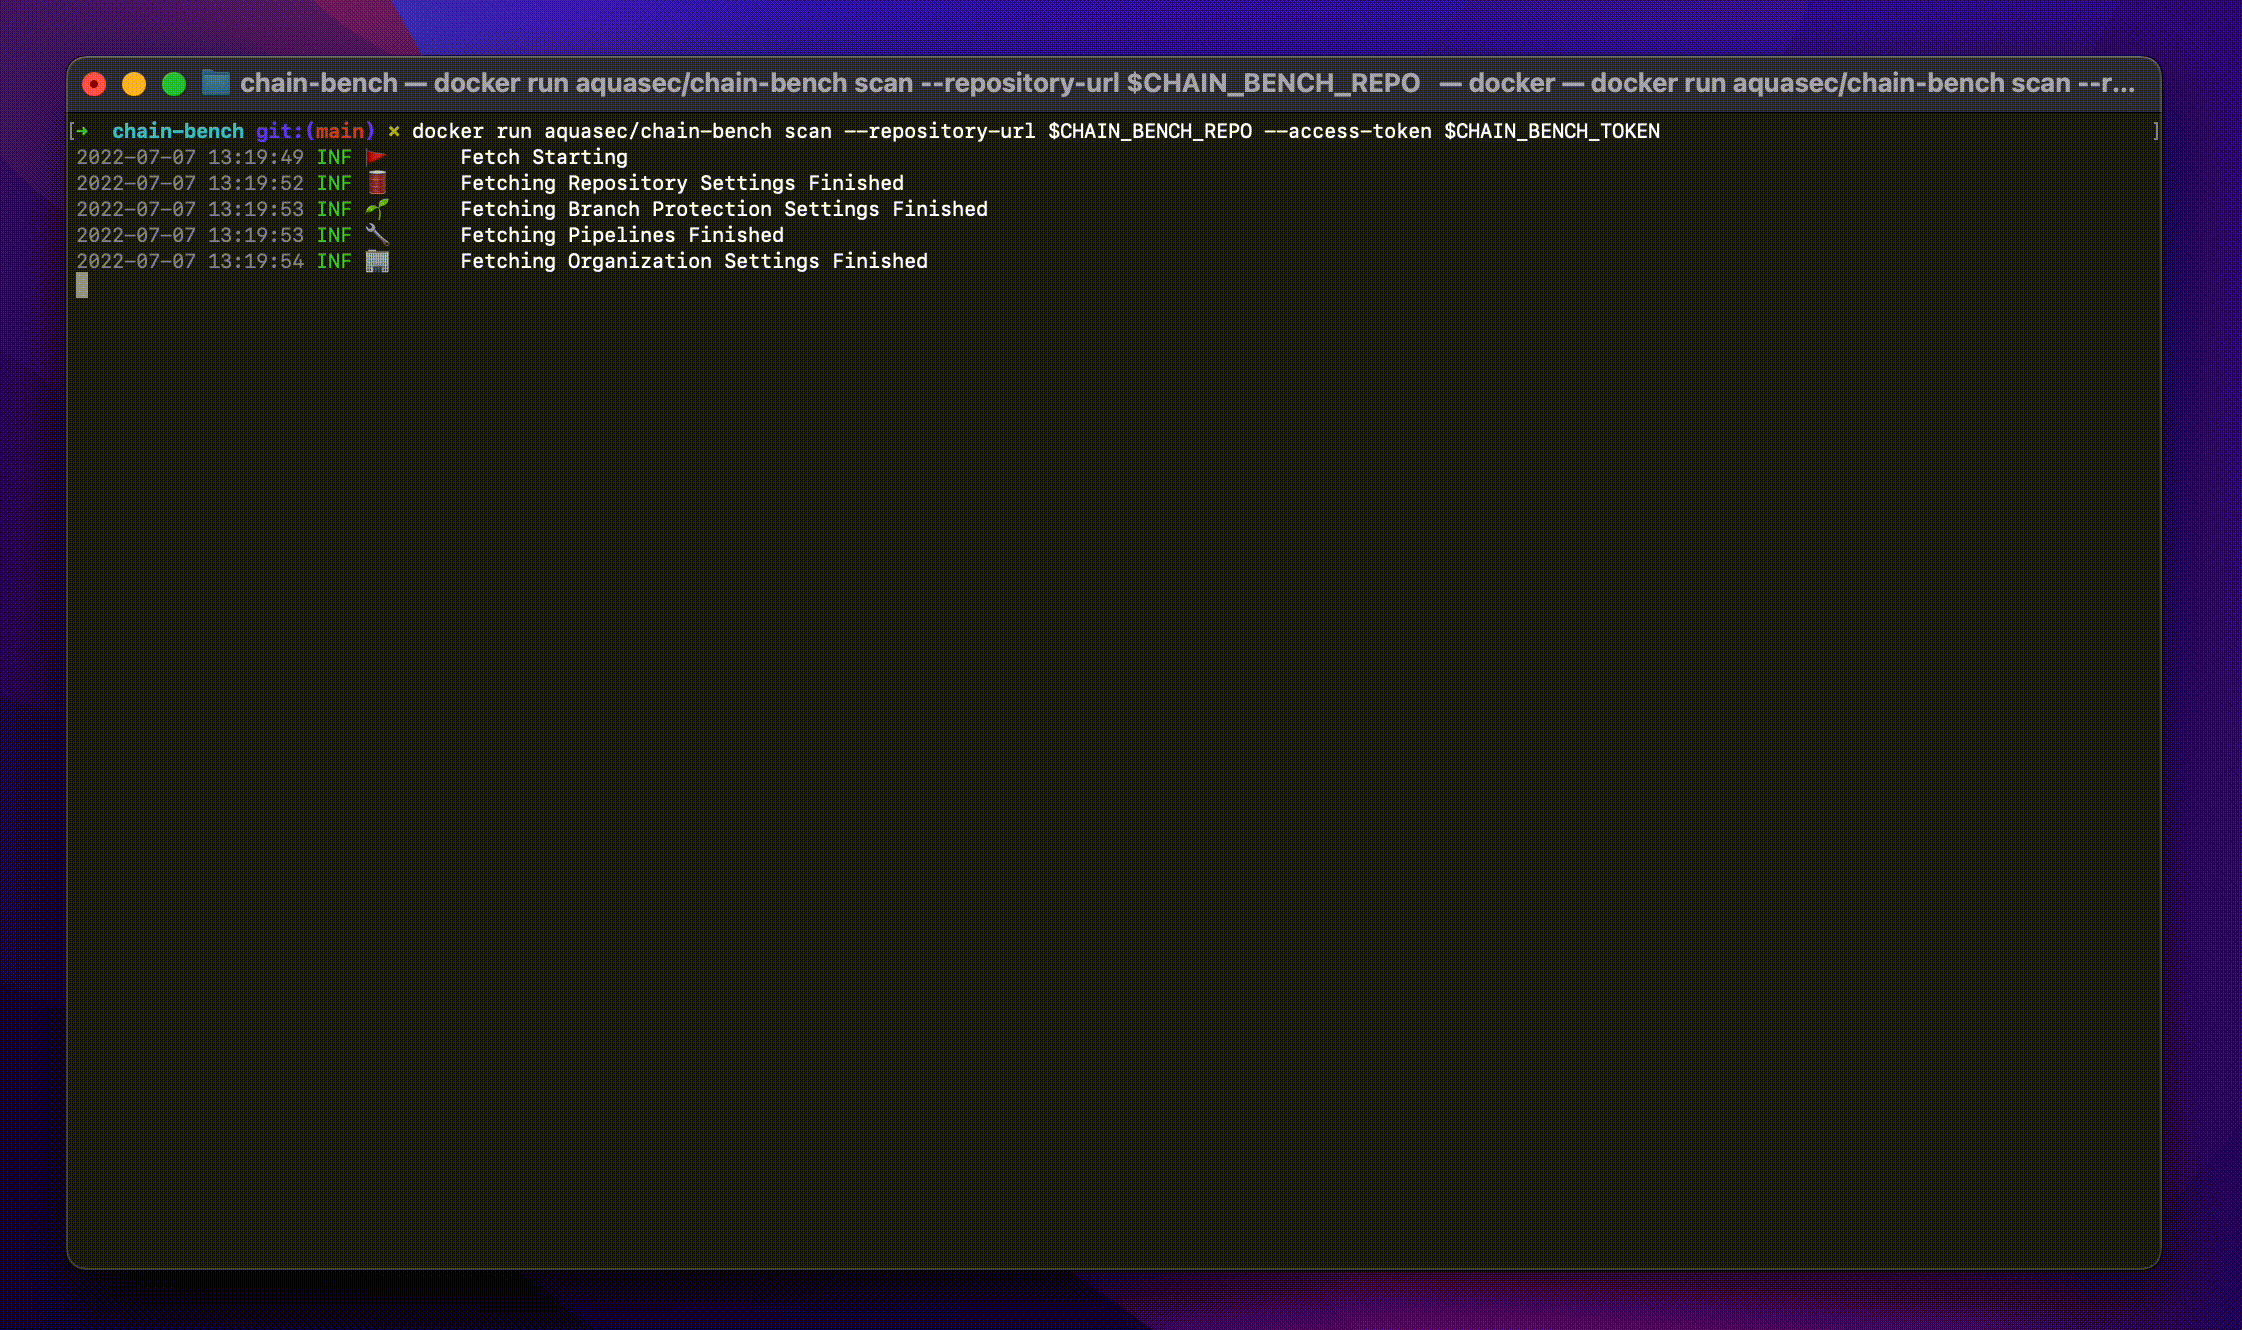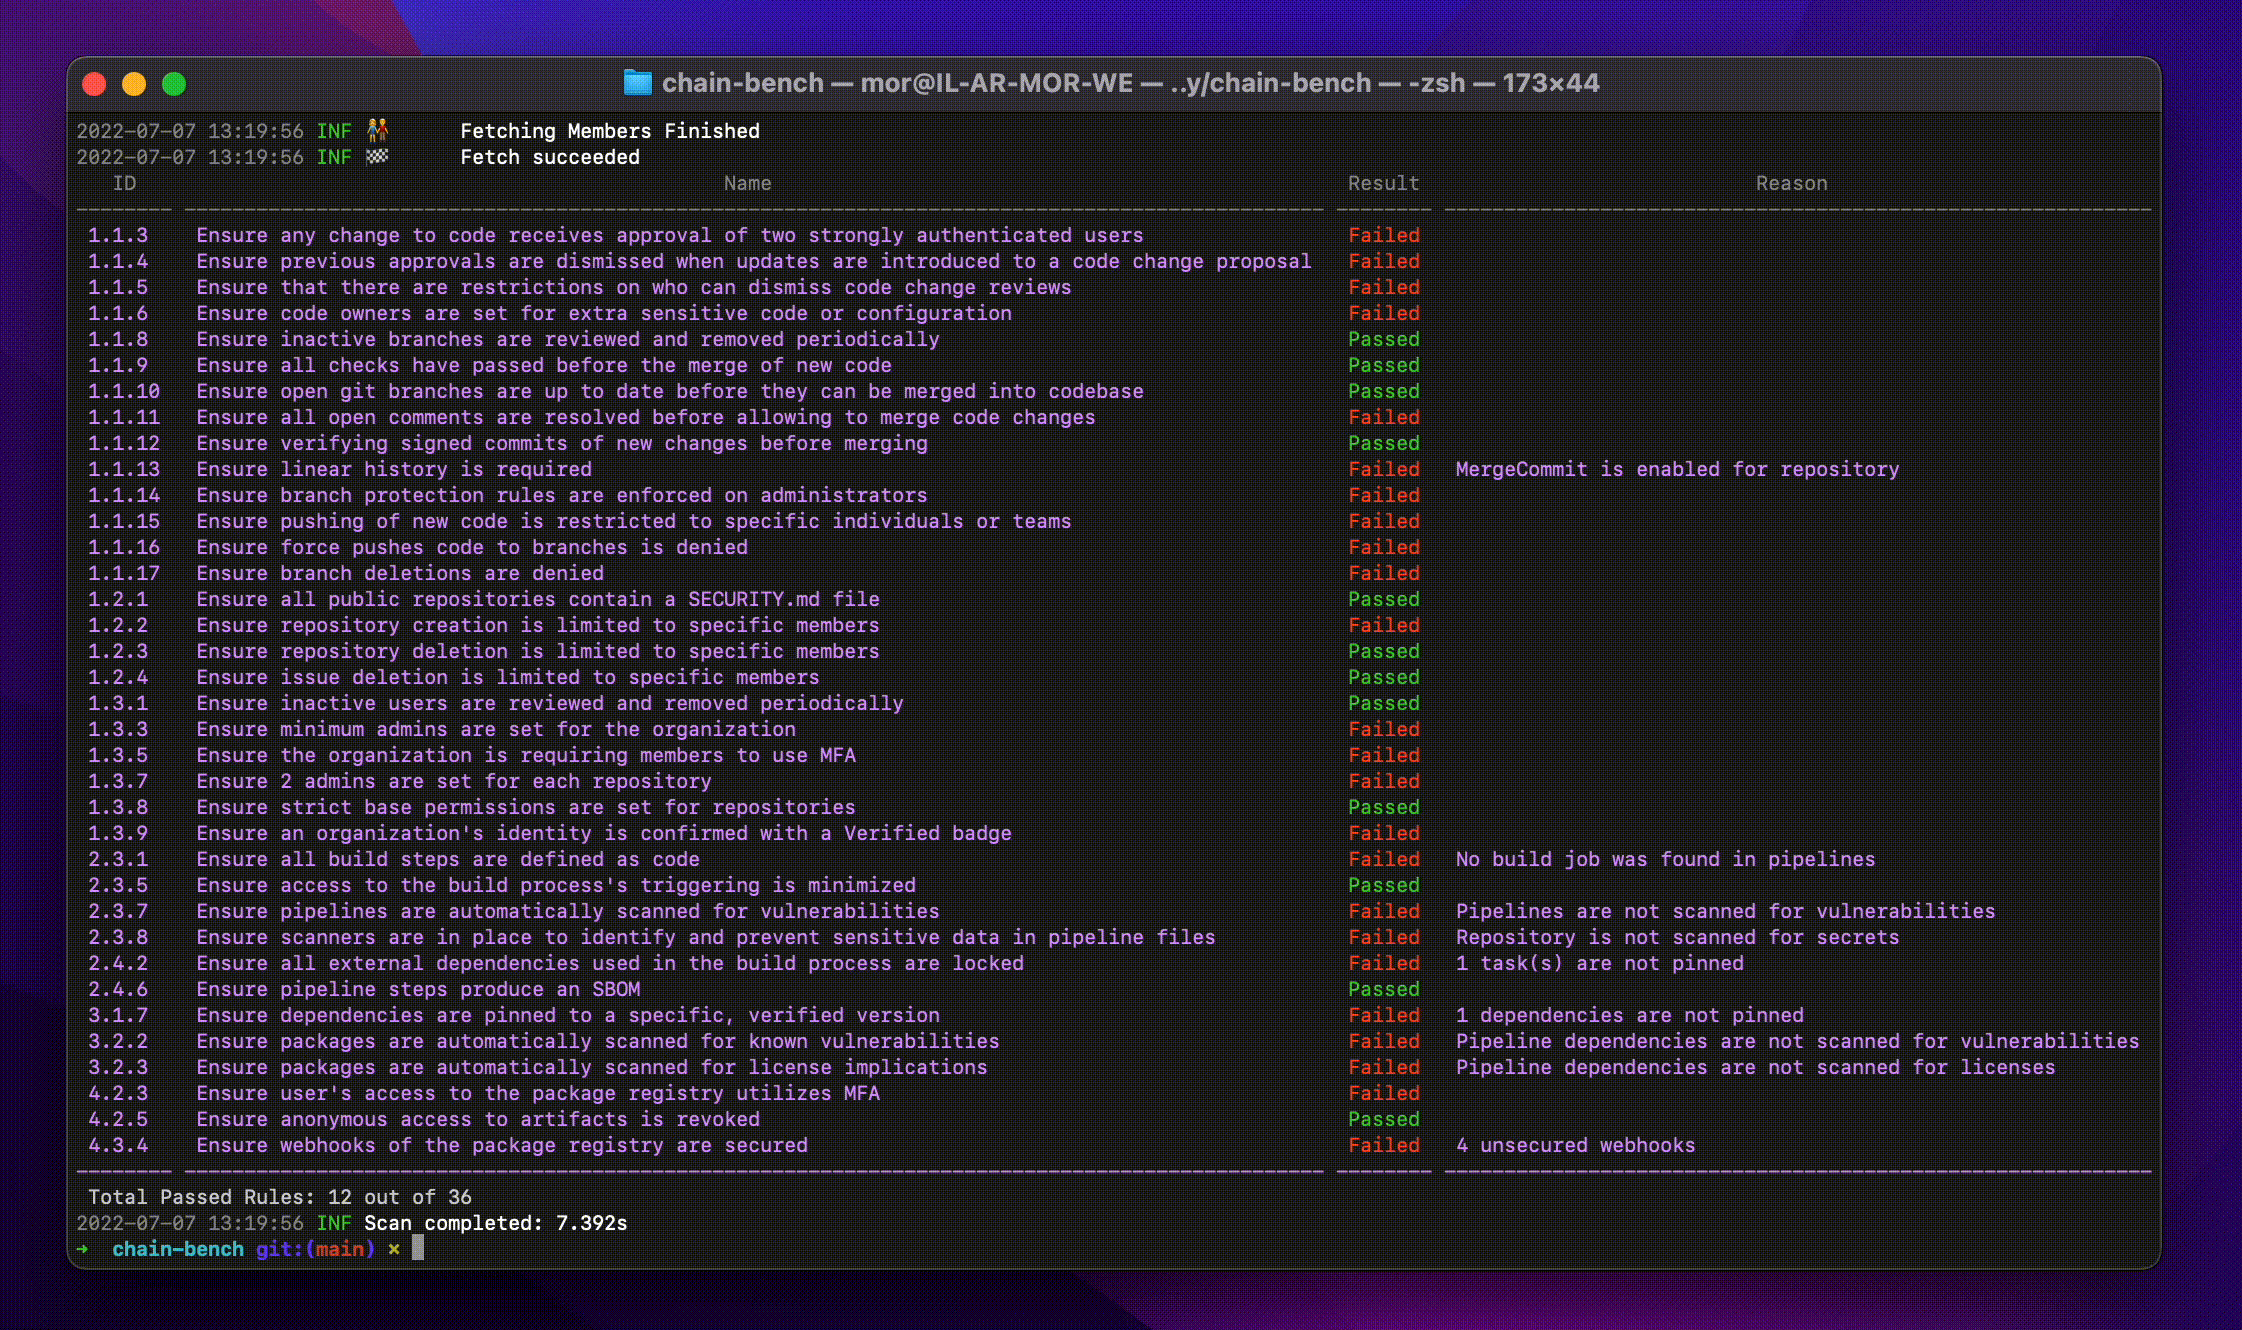 aquasecurity/chain-bench
Audits software supply chain security compliance against the CIS benchmark, scanning SCM settings, branch protections, dependencies, and CI/CD…
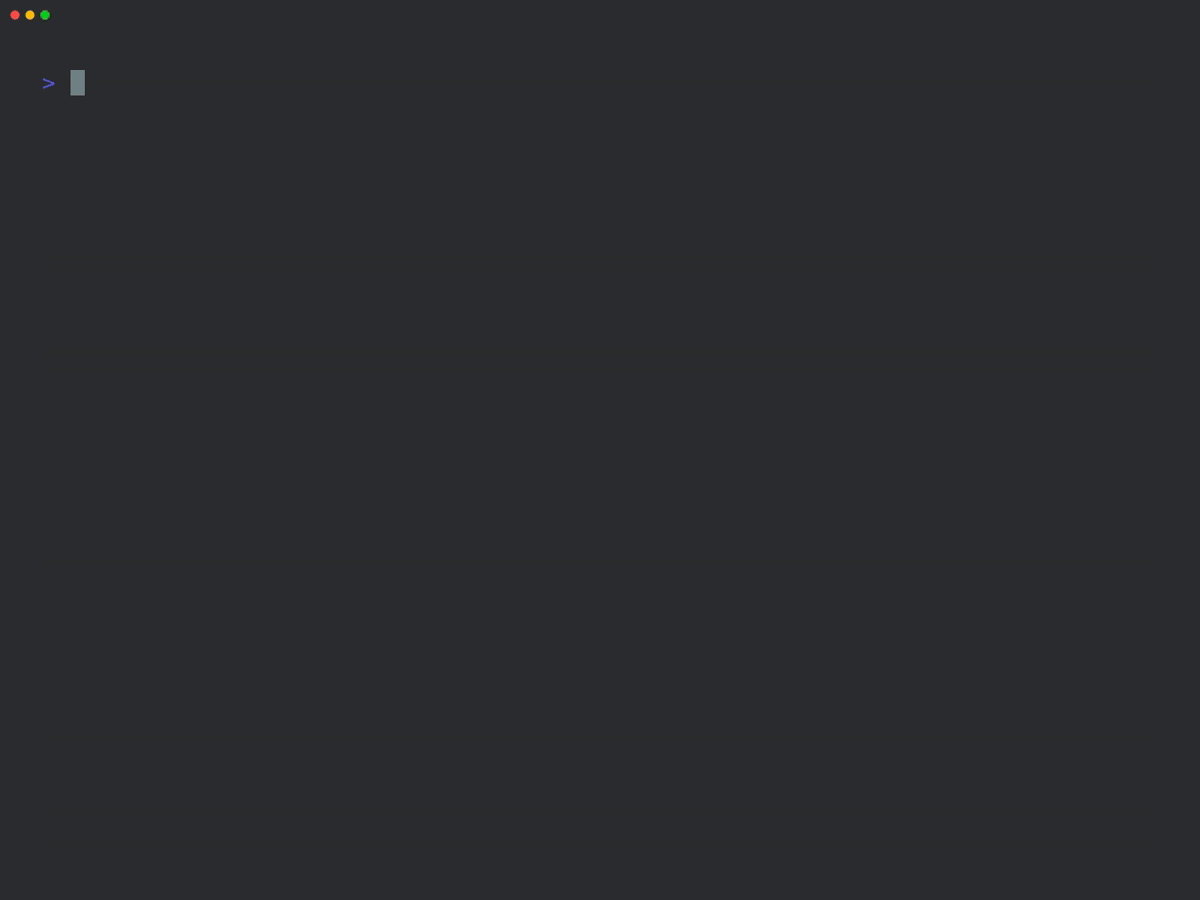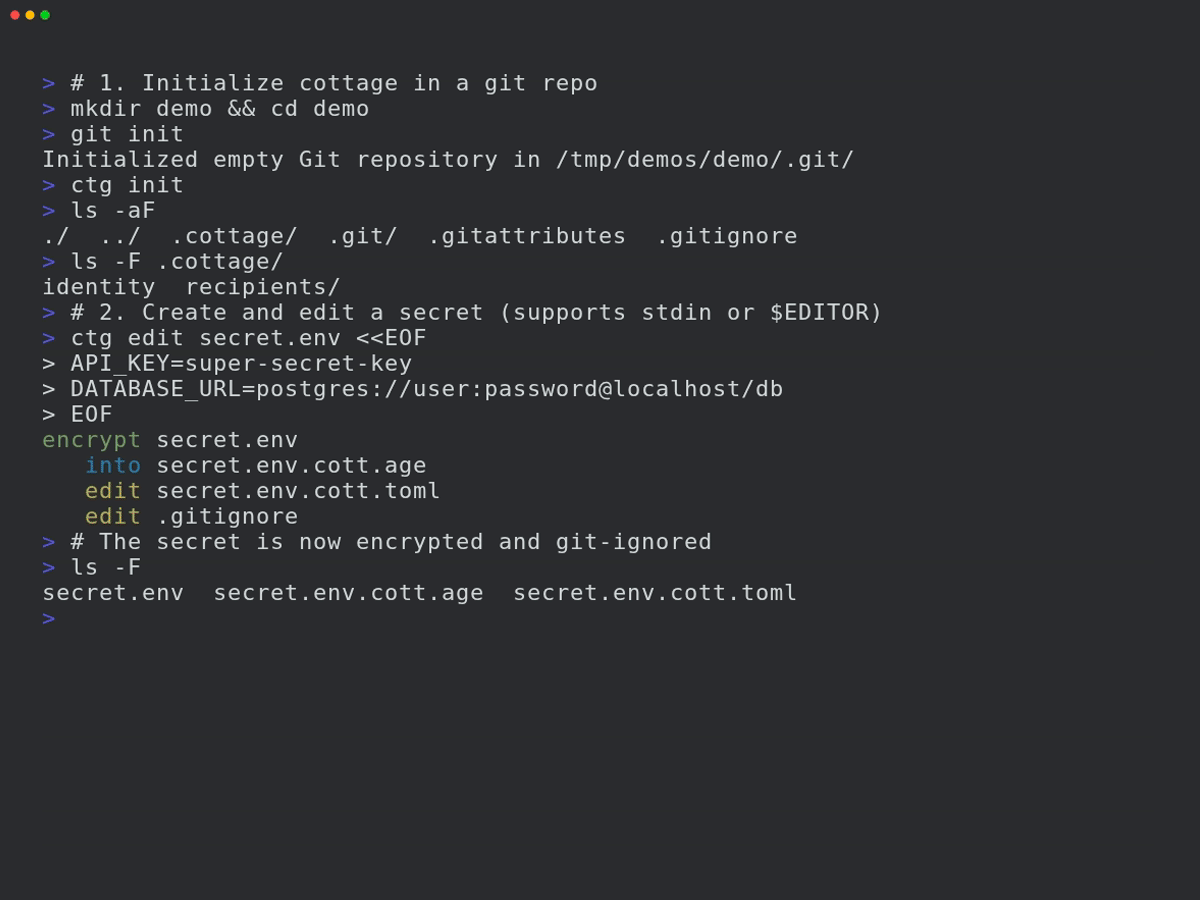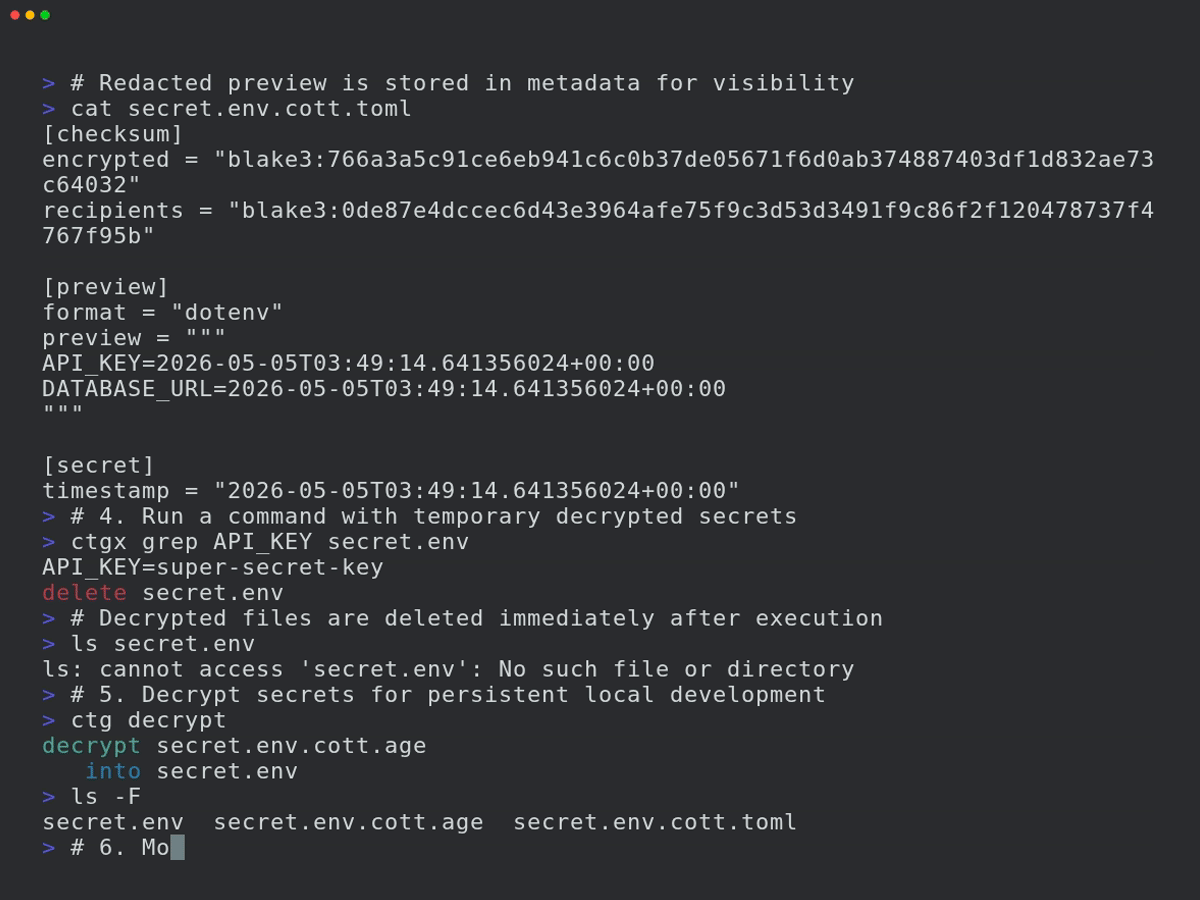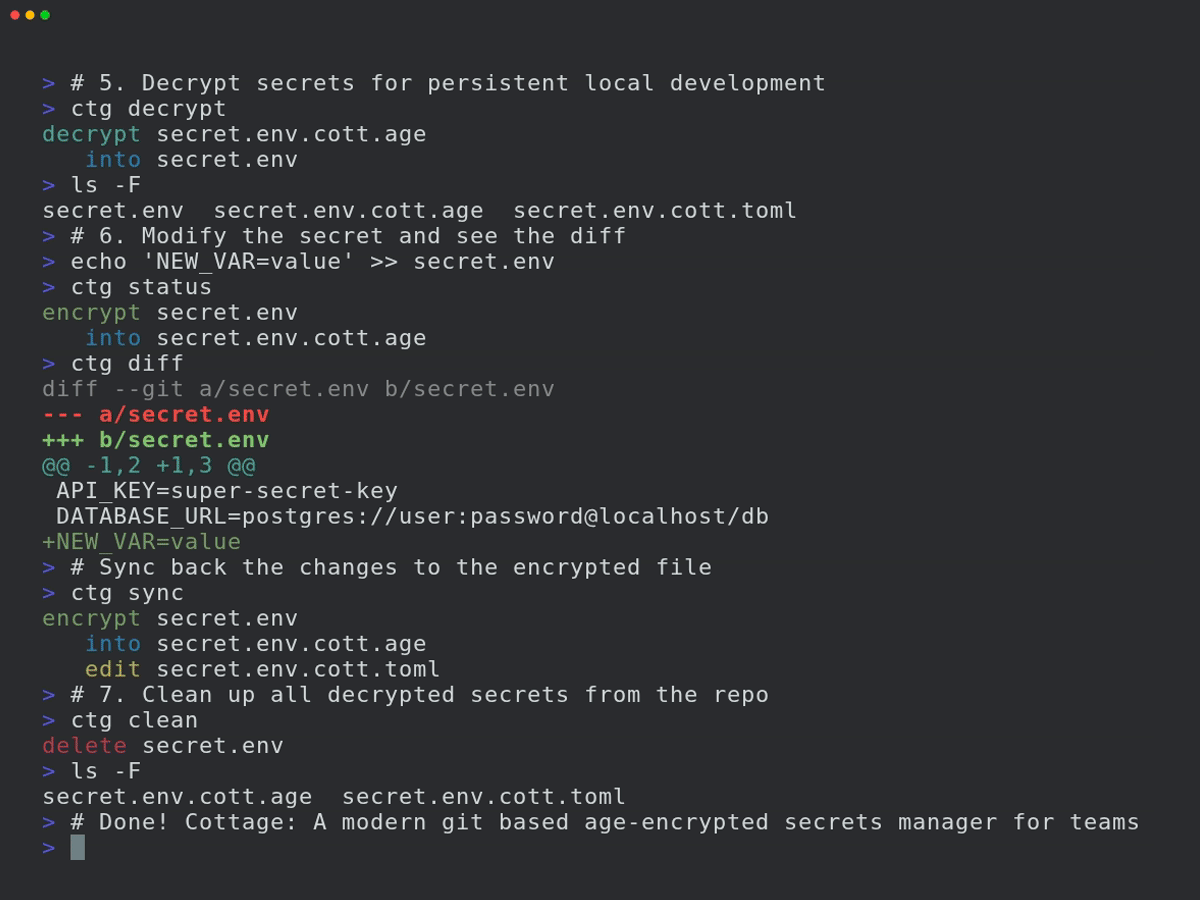 sayanarijit/cottage
A modern git based age-encrypted secrets manager for teams.
 otsmane-ahmed/ci-supplychain-guard
Static analysis tool that detects malicious dependencies in CI/CD pipelines using pattern matching and AST analysis, with a traffic-light risk…
 gmh5225/disclosure-check
Tool to identify the best mechanisms for privately disclosing a security vulnerability for a package/project.
 municipalparkingservices/cve-2021-44228-scanner
Single-binary scanner for CVE-2021-44228 (Log4Shell) that detects vulnerable log4j versions in JAR/WAR/EAR files and applies mitigation patches by…
 cahyod/react2shell
Alat ini mendeteksi potensi kerentanan React2Shell (CVE-2025-55182) dalam proyek React dengan memeriksa: - File `package.json` dan file lock untuk…
 openclarity/openclarity
OpenClarity is an open source platform built to enhance security and observability of cloud native applications and infrastructure
 rapticore/ore-mal-pkg-inspector
Multi-Ecosystem Malicious Package Detection and Supply Chain Security Scanner
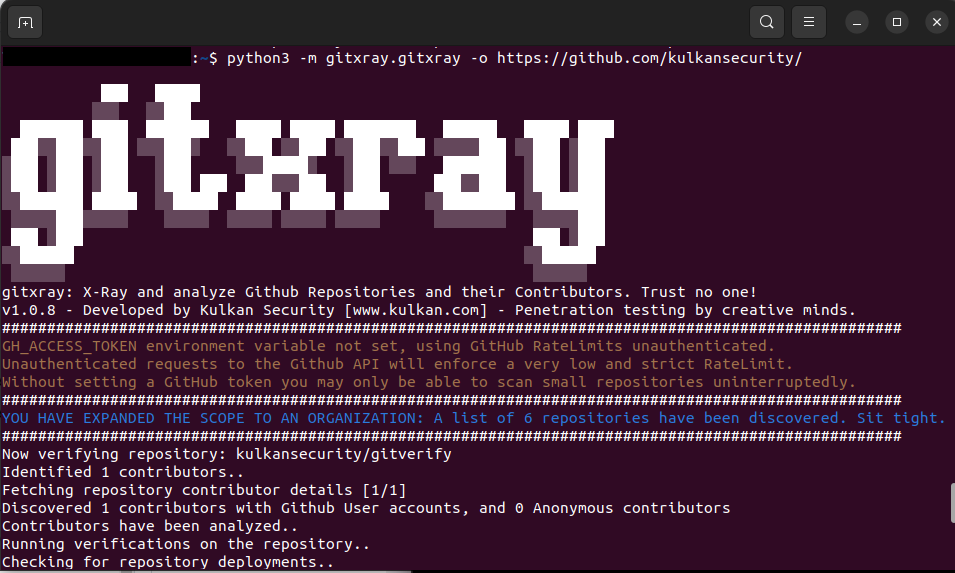 kulkansecurity/gitxray
A multifaceted security tool which leverages Public GitHub REST APIs for OSINT, Forensics, Pentesting and more.
 skyscanner/whispers
Identify hardcoded secrets in static structured text
 anchore/syft
CLI tool and library for generating a Software Bill of Materials from container images and filesystems
 aquasecurity/vexhub
Aggregates Vulnerability Exploitability eXchange (VEX) documents from open-source projects. Organizes by PURL for automated security tool integration.
 scopeblind/scopeblind-gateway
Fail-closed Cedar policy gate plus signed receipts for AI agent tool calls. npx protect-mcp
 ry-allan/tanstack-compromise-checker
Detects CVE-2026-45321 (TanStack supply chain compromise) and Mini Shai-Hulud worm artifacts. Scans node_modules, lockfiles, persistence hooks…
 az9713/cve-lite-on-pi
Running OWASP cve-lite-cli against the pi monorepo: scan journey and key finding (vitest CVE-2026-47429).
 preflightsh/preflight
Go-based CLI tool that scans codebases for launch readiness, detecting missing configuration, security hygiene issues, secret leaks, and integration…