
advisories
 justinsteven/advisories
Personal repository of security advisory disclosures covering vulnerabilities in web, cloud, infrastructure, and open-source software.
cloud-securitycurated-resourceseducation+3
justinsteven/advisoriesPersonal repository of security advisory disclosures covering vulnerabilities in web, cloud, infrastructure, and open-source software.
 purs3lab/argus
Staged static taint analysis framework for GitHub Actions workflows. Detects code injection vulnerabilities using taint-tracking and an impact…
 platanor/hardware-compliance-handbook
AI-ready knowledge base of security & compliance regulations for hardware and connected-device manufacturers - structured, indexed, and…
 codeshield-security/log4jshell-bytecode-detector
Local Bytecode Scanner for the Log4JShell Vulnerability (CVE-2021-44228)
 pvharmo2/gha-lab-ca4fa82ac5
Security-research lab: reproduction of CVE-2026-29075 (GHSA-3j55-5q6x-2h48) in mesa/mesa benchmarks.yml pull_request_target workflow — single-commit…
 pvharmo2/gha-lab-becf103a54
Authorized security-research reproduction of CVE-2025-15617 (GHSA-6xqr-4q5g-xc7x): artipacked GITHUB_TOKEN leak in wazuh FIM Windows integration…
 nserser/lr-webpki
Reference implementation of LR+ post-quantum authentication over WebPKI CA context, with corpus pipeline, reconstruction, evaluation, and provenance…
 j4ck3lsyn-gen2/reports
Curated collection of cybersecurity research reports covering CVE analysis, exploit research, threat intelligence, and offensive security from…
 pvharmo2/gha-lab-2f775f277c
Authorized lab reproduction of CVE-2025-47928 (spotipy-dev/spotipy pull_request_target secrets exfiltration) — snapshot at vulnerable commit 4f5759d
 chaitanyagarware/cve-2026-54520
Public advisory landing page documenting CVE-2026-54520, a high-severity path traversal vulnerability in ai-agent-automation's workflow executor,…
 horrister/solarwinds-sunburst-cve-2020-10148
Curated vulnerability writeups with full technical analysis, proof-of-concept scripts, IOC listings, and remediation guidance for real-world software…
 soliantconsulting/cve-2025-46295-fix-fms
Automated script suite to detect and remediate CVE-2025-46295 by replacing vulnerable Apache Commons JARs in FileMaker Server installations with…
 owasp/software-component-verification-standard
Software Component Verification Standard (SCVS)
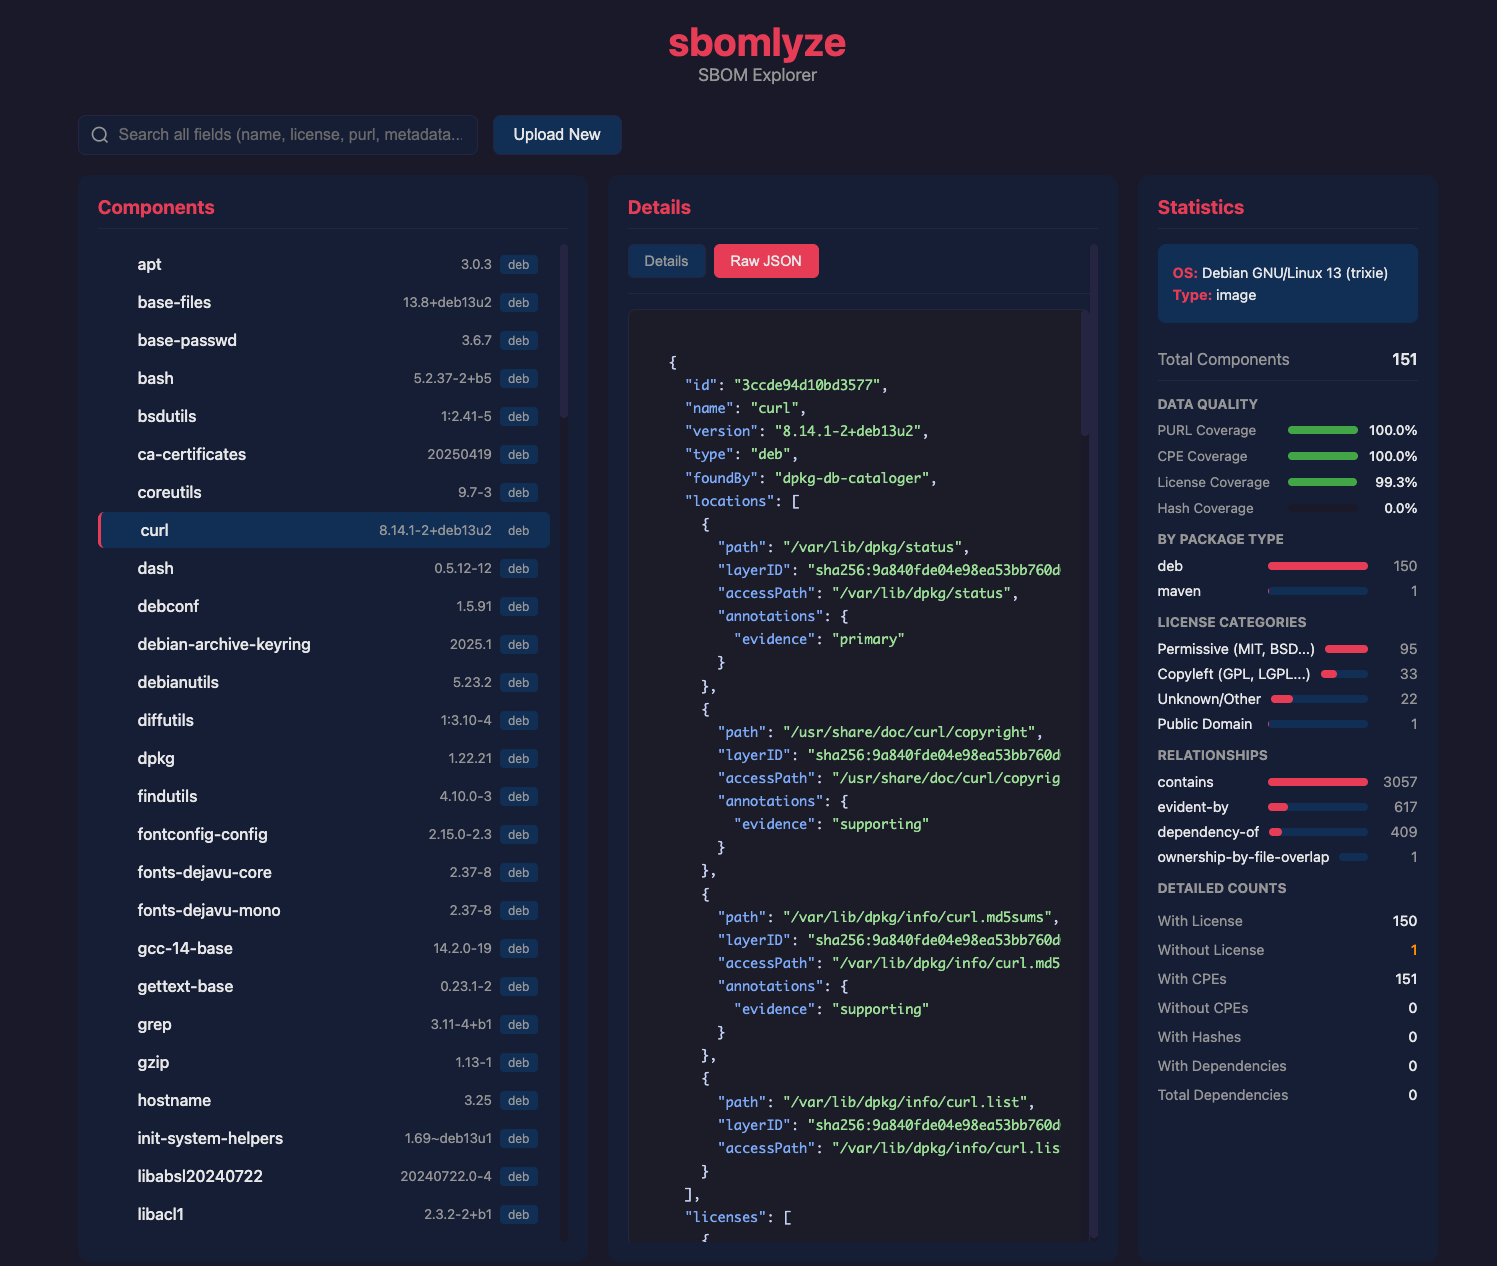 rezmoss/sbomlyze
Git diff for SBOMs—compare CycloneDX, SPDX, and Syft documents, detect tampering, and gate CI.
 oopsiewoopsie/mc-log4j-patcher
CVE-2021-44228 server-side fix for minecraft servers.
 horrister/axios-supply-chain-cve-2026-26555
Curated vulnerability writeup collection with full technical analysis, proof-of-concept scripts, IOC listings, and remediation guidance for…
 andrewd-cg/cve-2024-52005-poc
Proof-of-Concept for CVE-2024-52005: ANSI escape sequence injection in Git. Demonstrates incorrect 'not_affected' VEX claims in hardened container…
 chainguard-dev/text4shell-policy
ClusterImagePolicy demo for cve-2022-42889 text4shell