vulns-2026-fatfs-chance

Documented security vulnerabilities in the FatFs embedded filesystem library with CVE details, fuzzing harness, exploit disk-image generator, and…

Documented security vulnerabilities in the FatFs embedded filesystem library with CVE details, fuzzing harness, exploit disk-image generator, and…

Proof-of-concept demonstrating a race condition in the tar npm package (v7.5.3) causing file collisions during parallel extraction, leading to data…

Minimal CVE-2024-3094 reference repository documenting the xz backdoor vulnerability, affected versions (5.6.0/5.6.1), and mitigation steps. Includes…

Security-research lab reproducing CVE-2021-4281 (GHSA-3796-3f93-cfvx): shell command injection via PR head-branch name in…

Security-research lab: controlled reproduction of CVE-2024-4254 (GHSA-fc78-c36r-cc59) — deploy-website.yml fork checkout/code execution in…

Malicious Maven pom.xml that uses "groovy-maven-plugin" to get RCE

Demonstration of CVE-2021-43616: npm `ci` command ignoring package-lock.json, causing unintended dependency version installation and supply-chain…

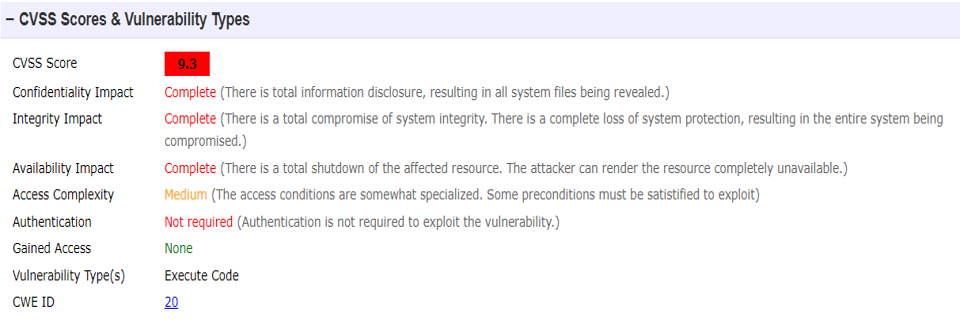
Azure IoT Hub where exposure of an owner-level Shared Access Key enables unauthenticated remote code execution (RCE) against connected IoT devices.…

Detailed analysis of CVE-2022-21668, a critical RCE vulnerability in Pipenv's requirements.txt parsing, including bug code, exploit mechanics, and…

Educational lab replicating the XZ Utils backdoor (CVE-2024-3094) with a custom Ed448 key pair. Includes a patched liblzma, systemd service, and…

Proof of Concept for CVE-2024-32002: Git submodule path injection vulnerability.

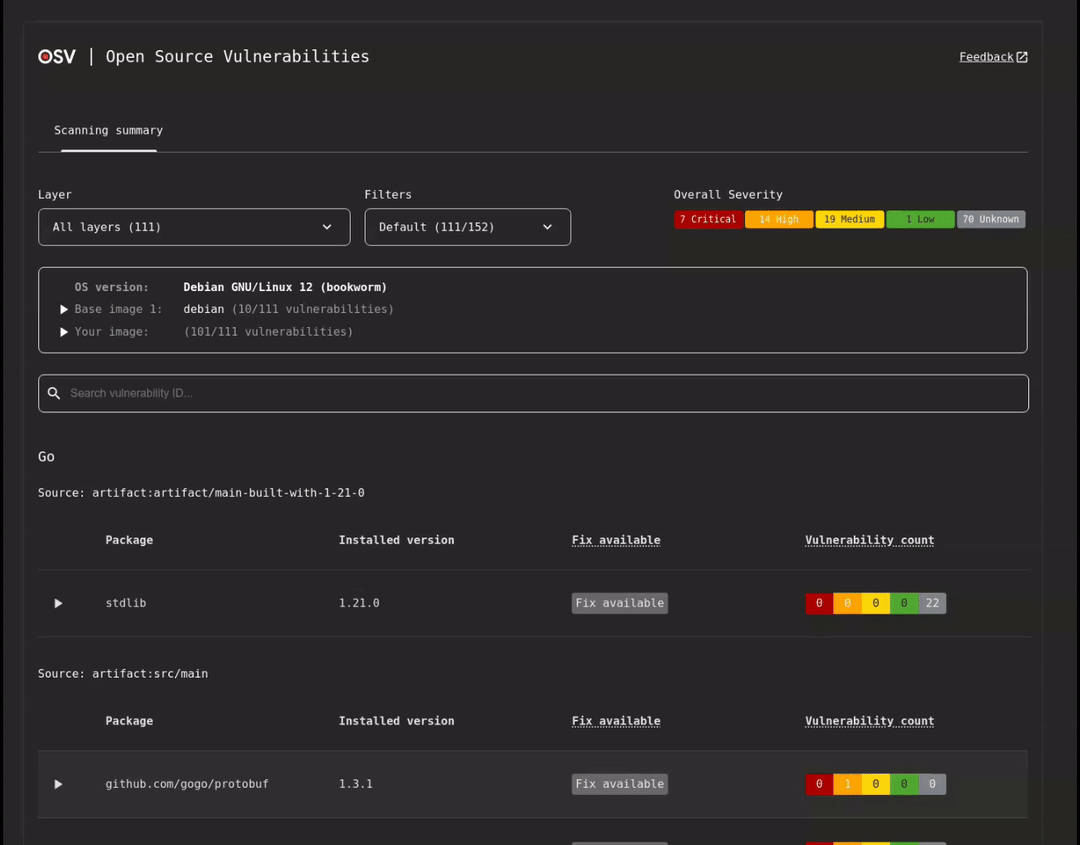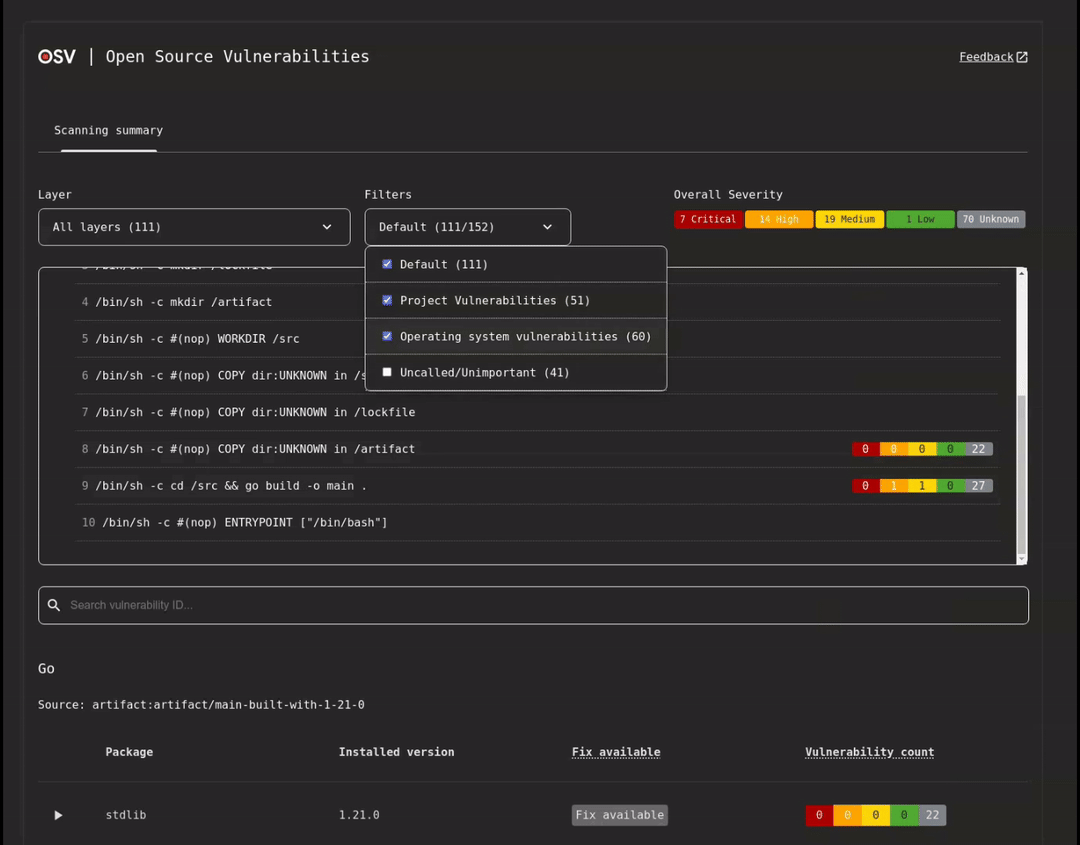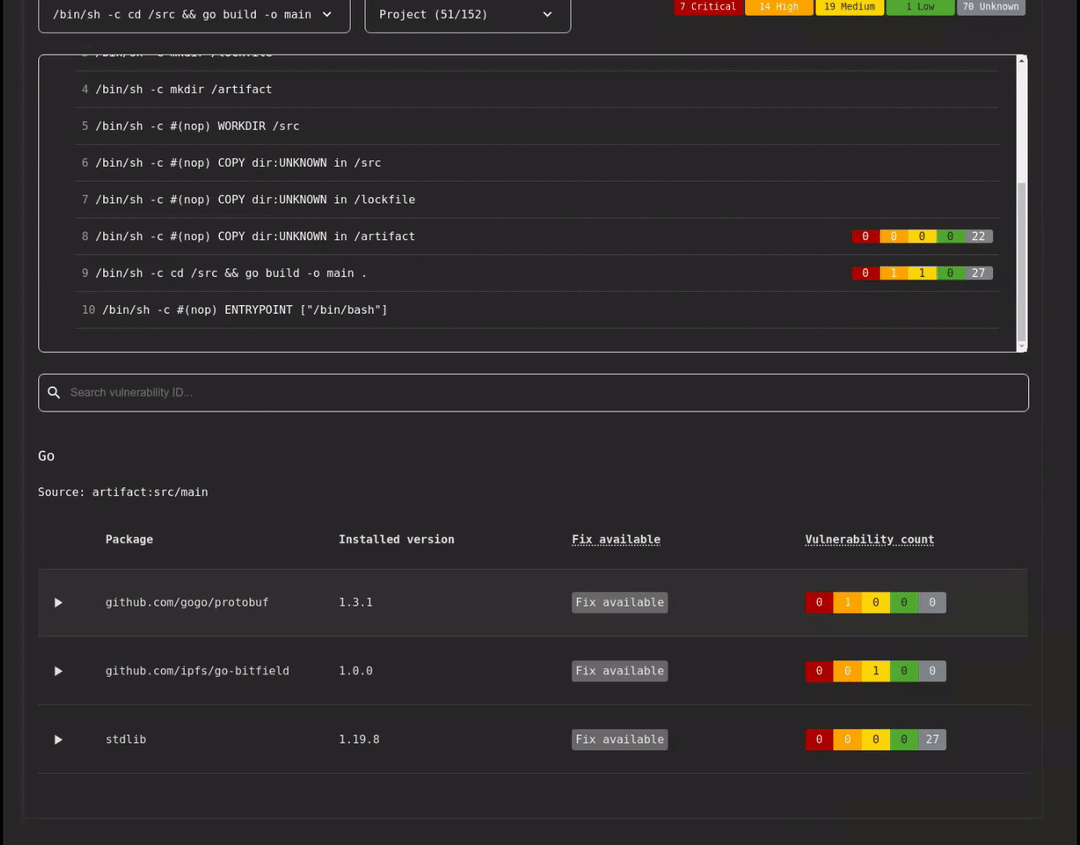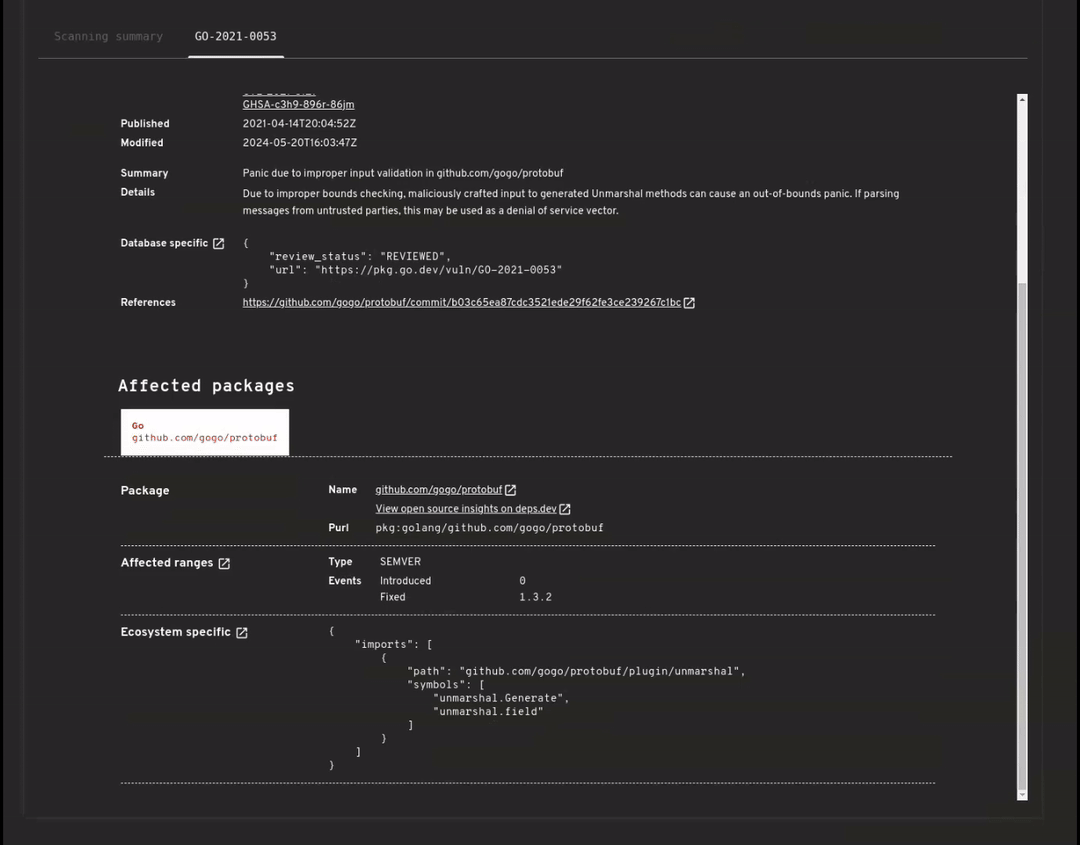
Vulnerability scanner written in Go which uses the data provided by https://osv.dev

A collection of awesome resources related AI security

Safety checks Python dependencies for known security vulnerabilities and suggests the proper remediations for vulnerabilities detected.

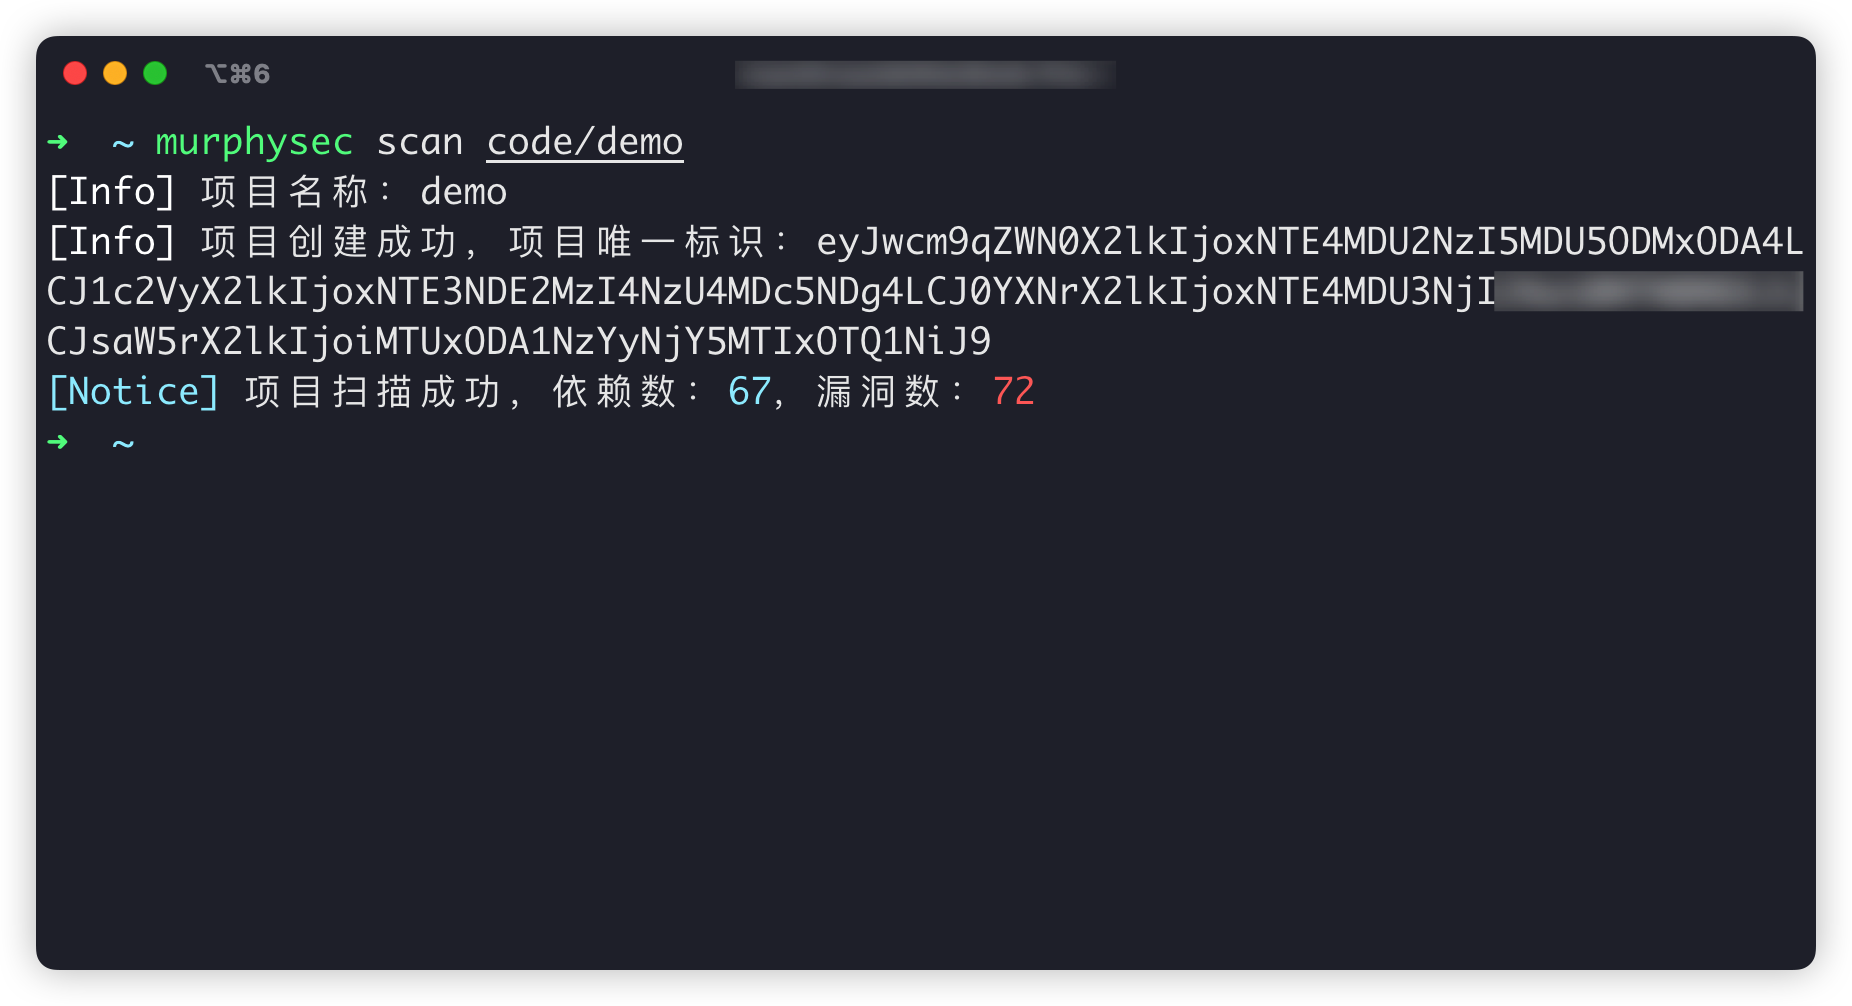
An open source tool focused on software supply chain security. 墨菲安全专注于软件供应链安全,具备专业的软件成分分析(SCA)、漏洞检测、专业漏洞库。

Curated repository of Qubes OS security bulletins, canaries, PGP keys, and ISO digests, with authenticated verification via git tags and detached…

Microsoft's curated repository of secure boot objects (KeK, Db, Dbx) for firmware and runtime, enabling transparent revocation updates and…

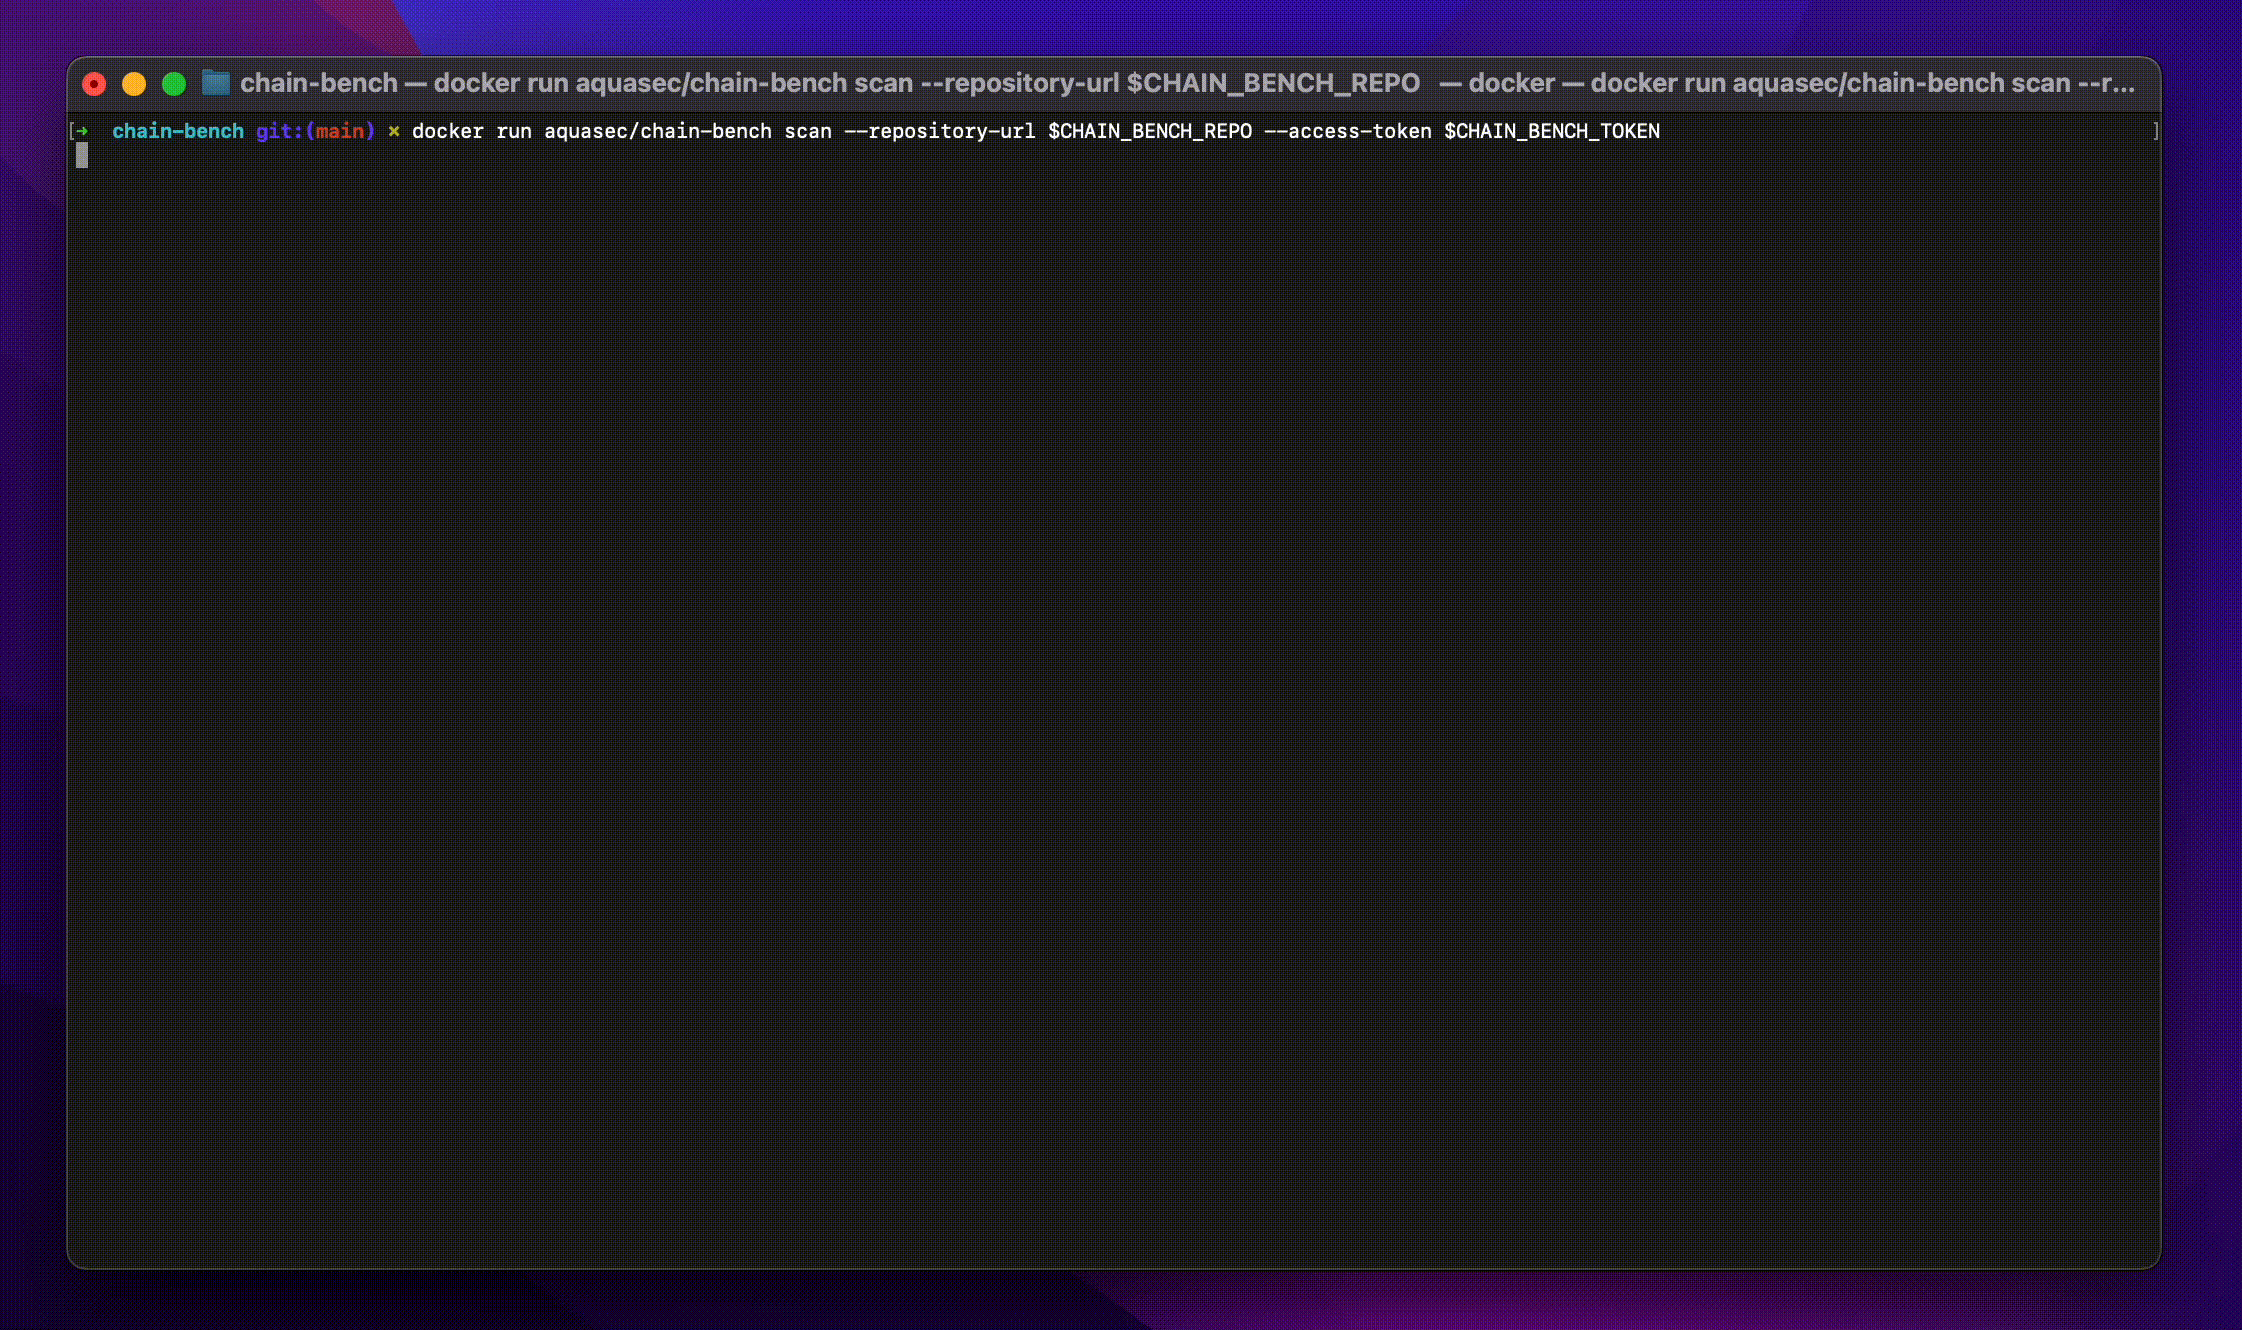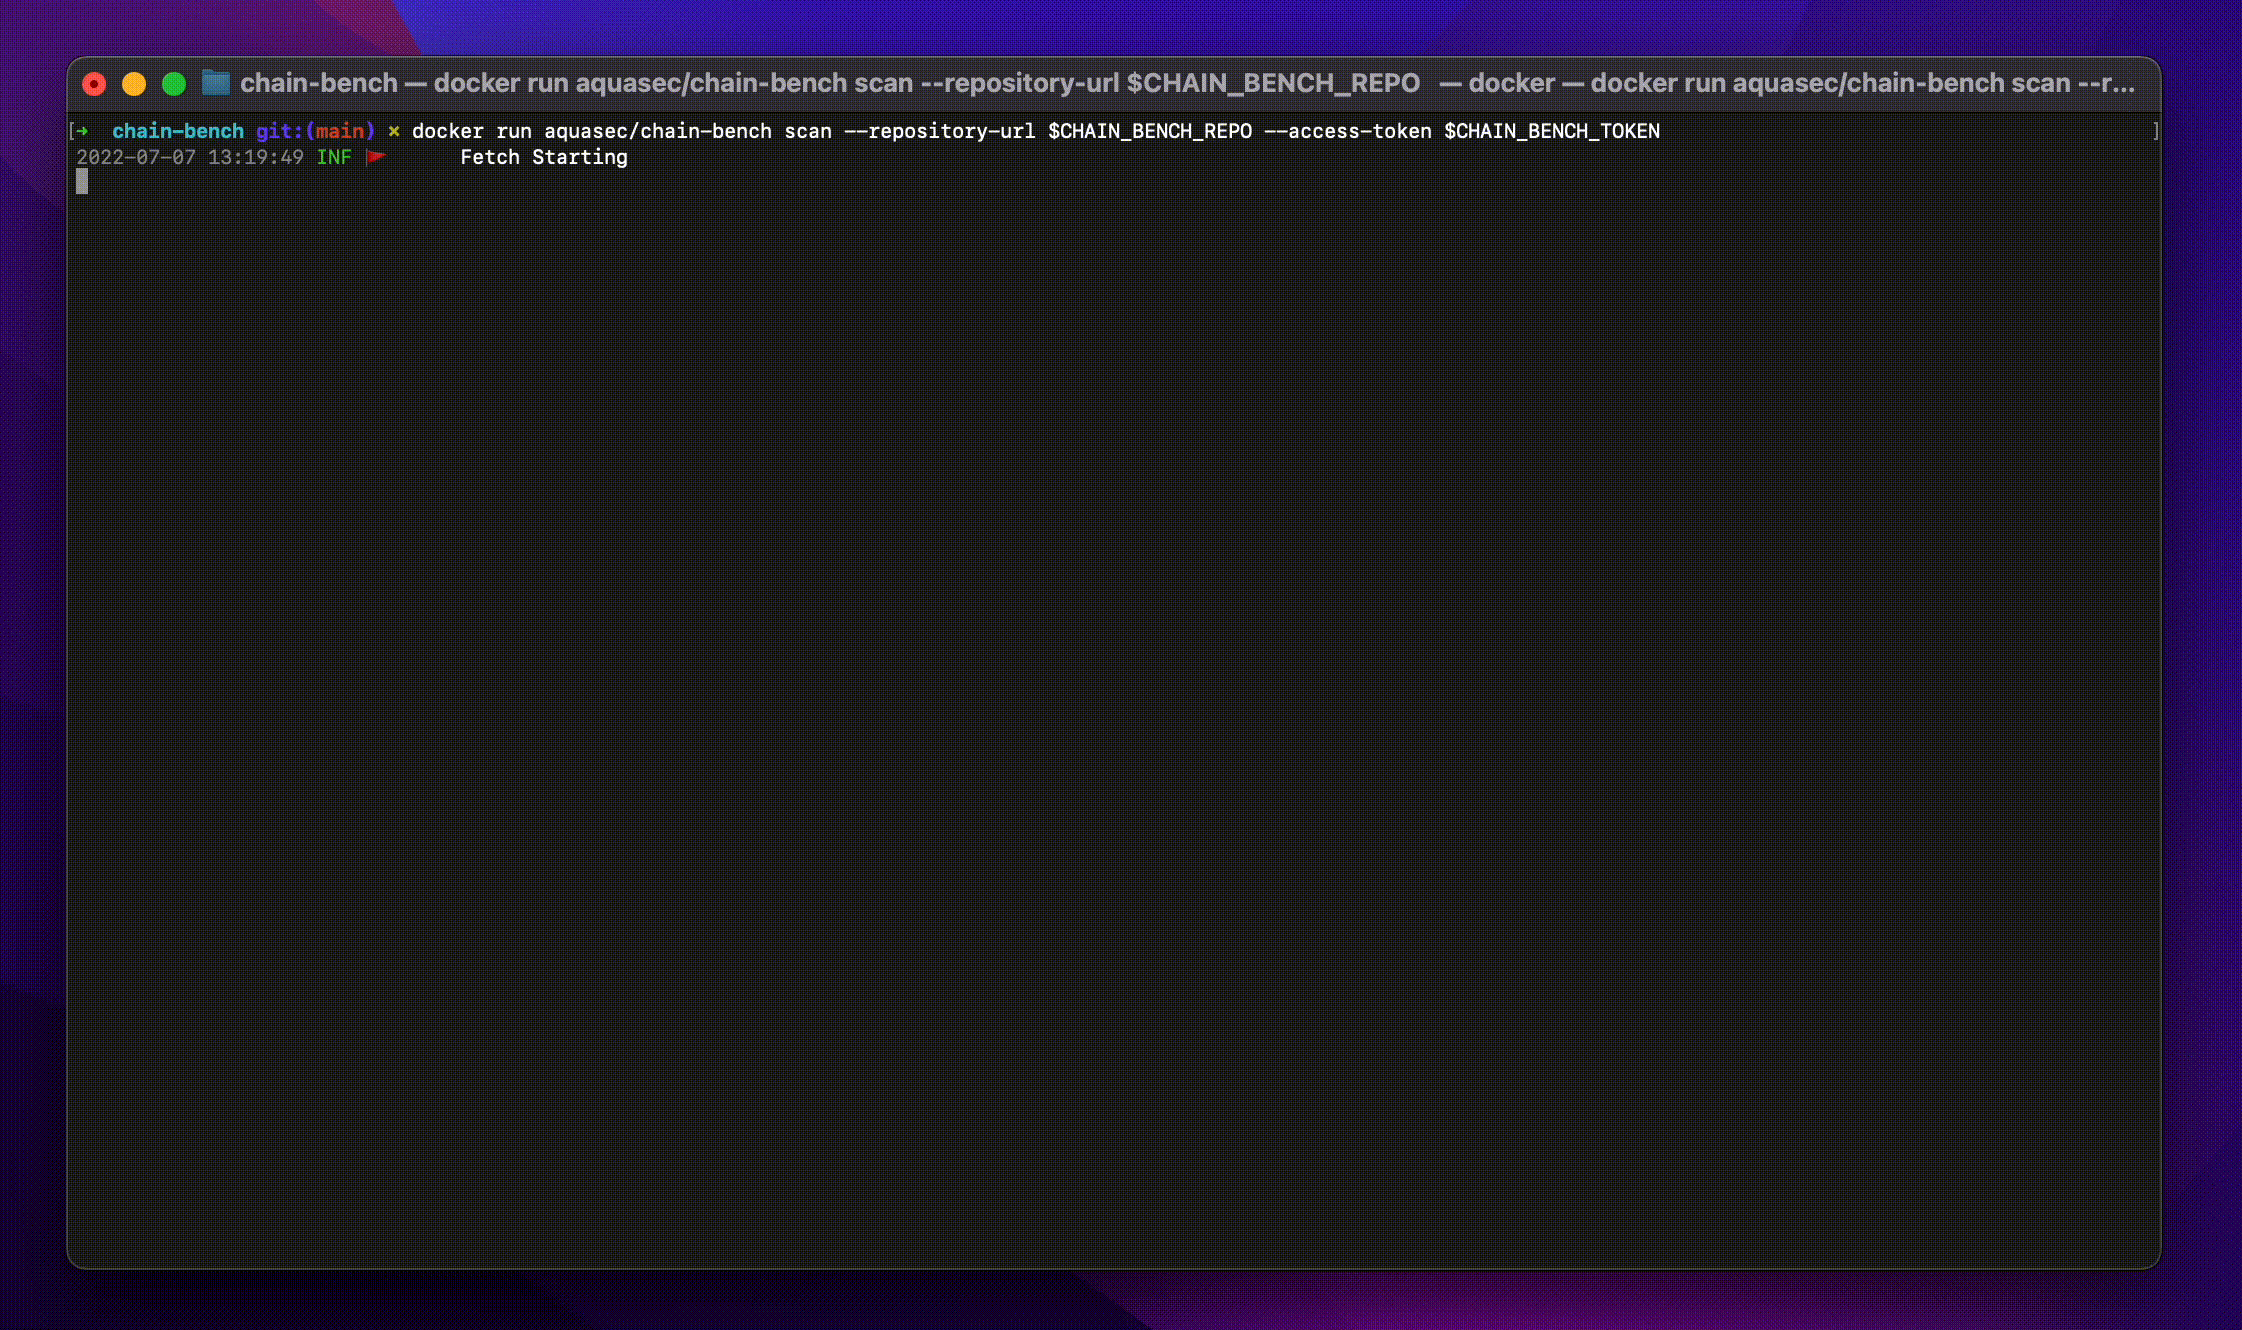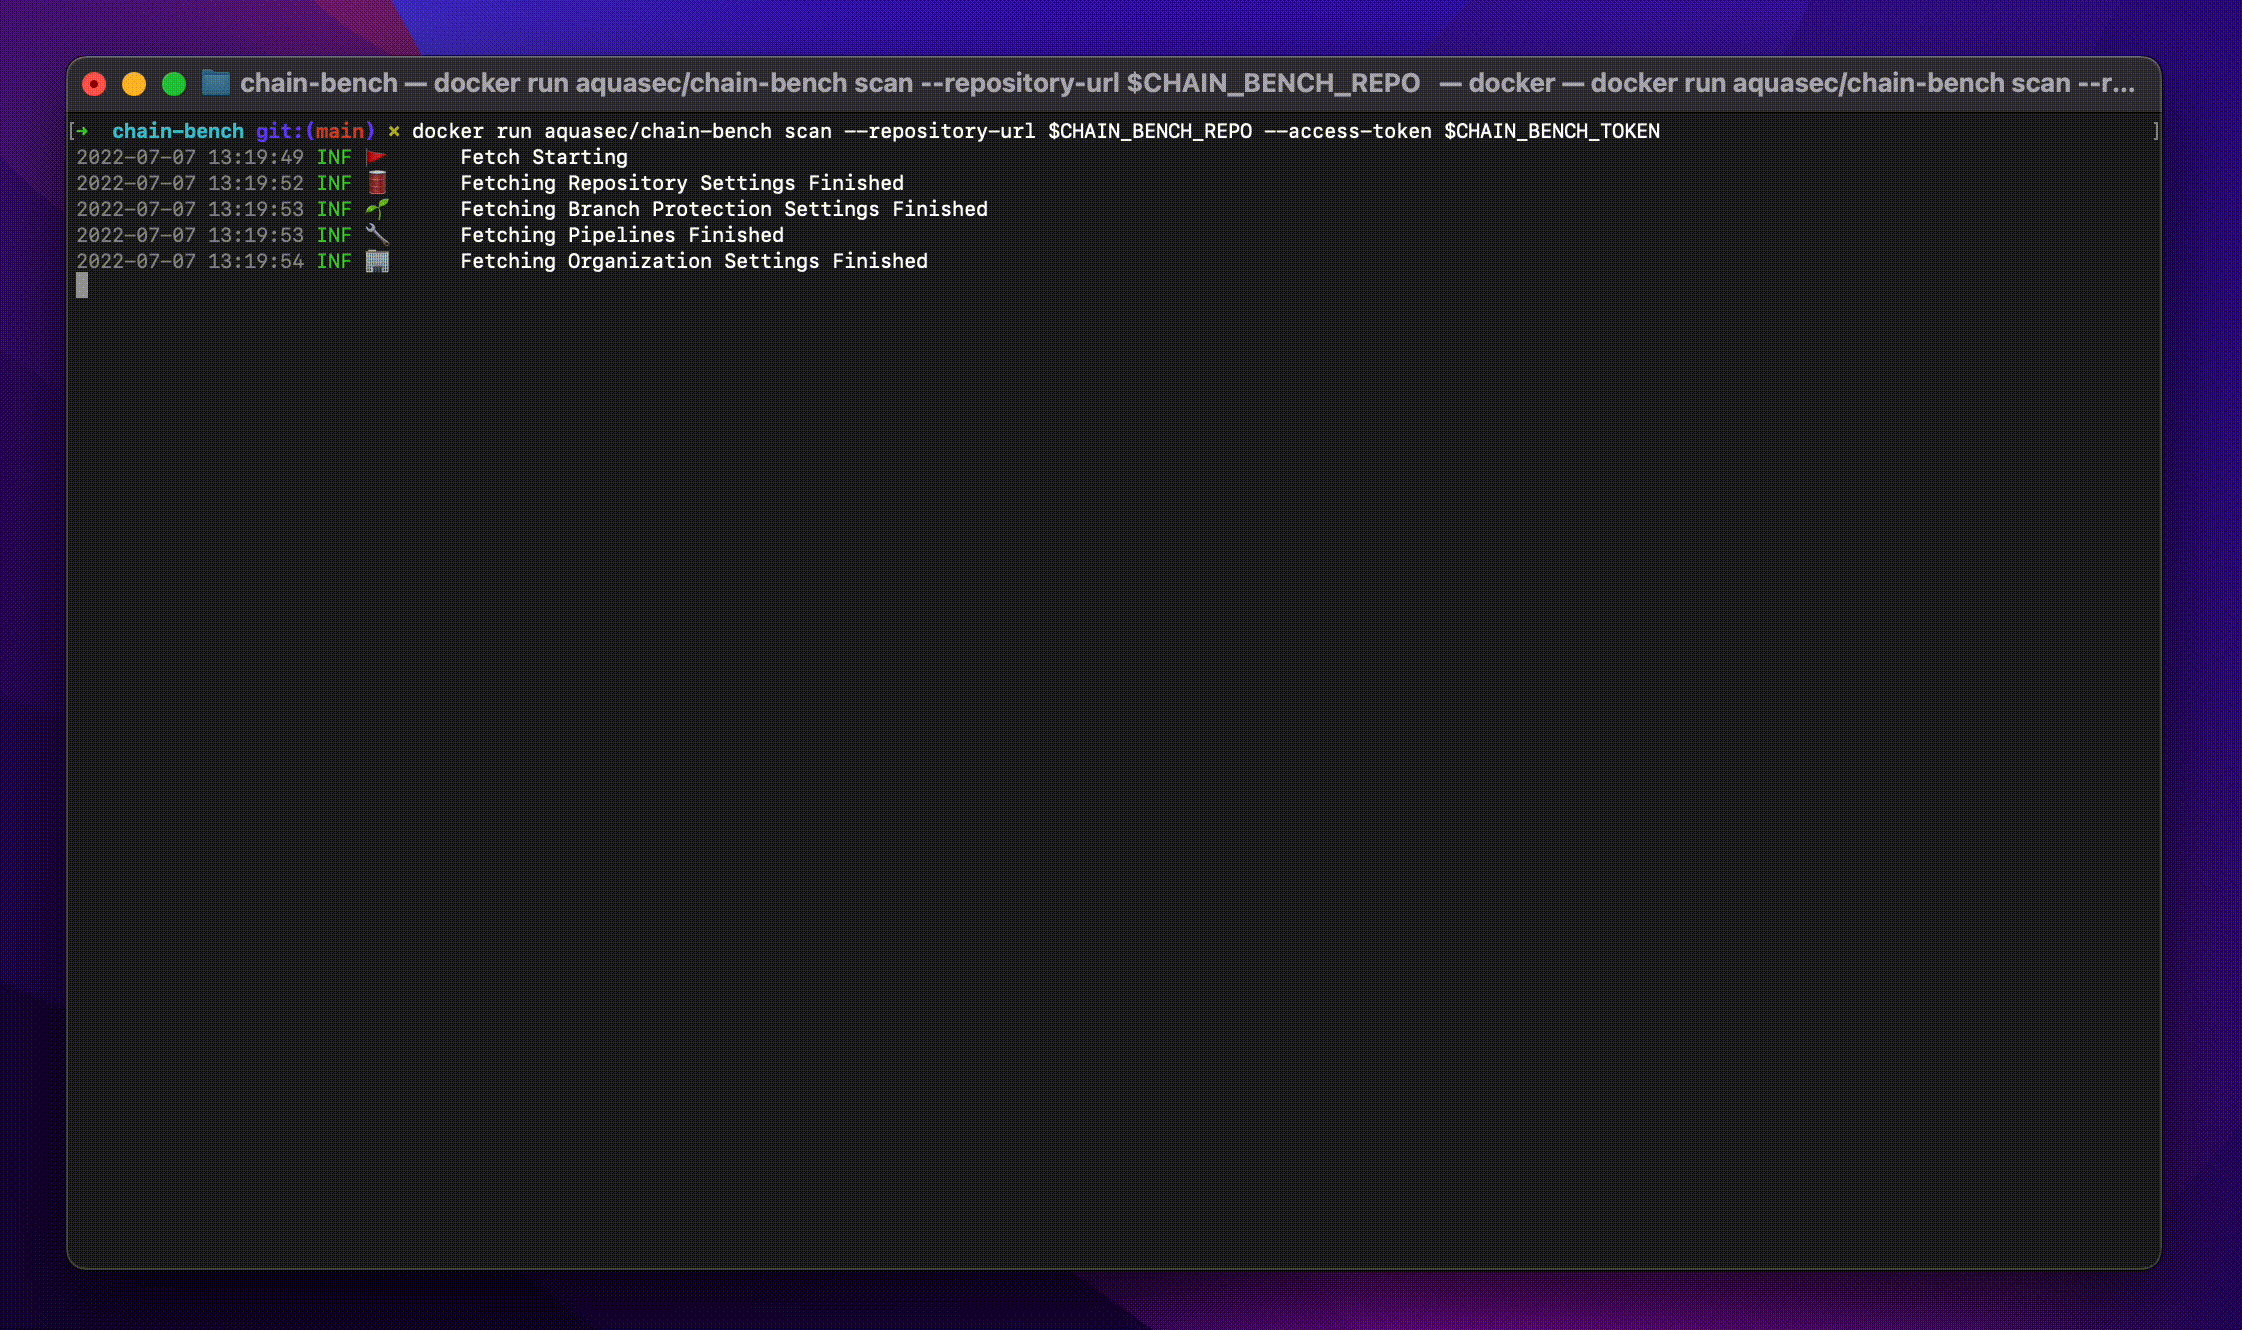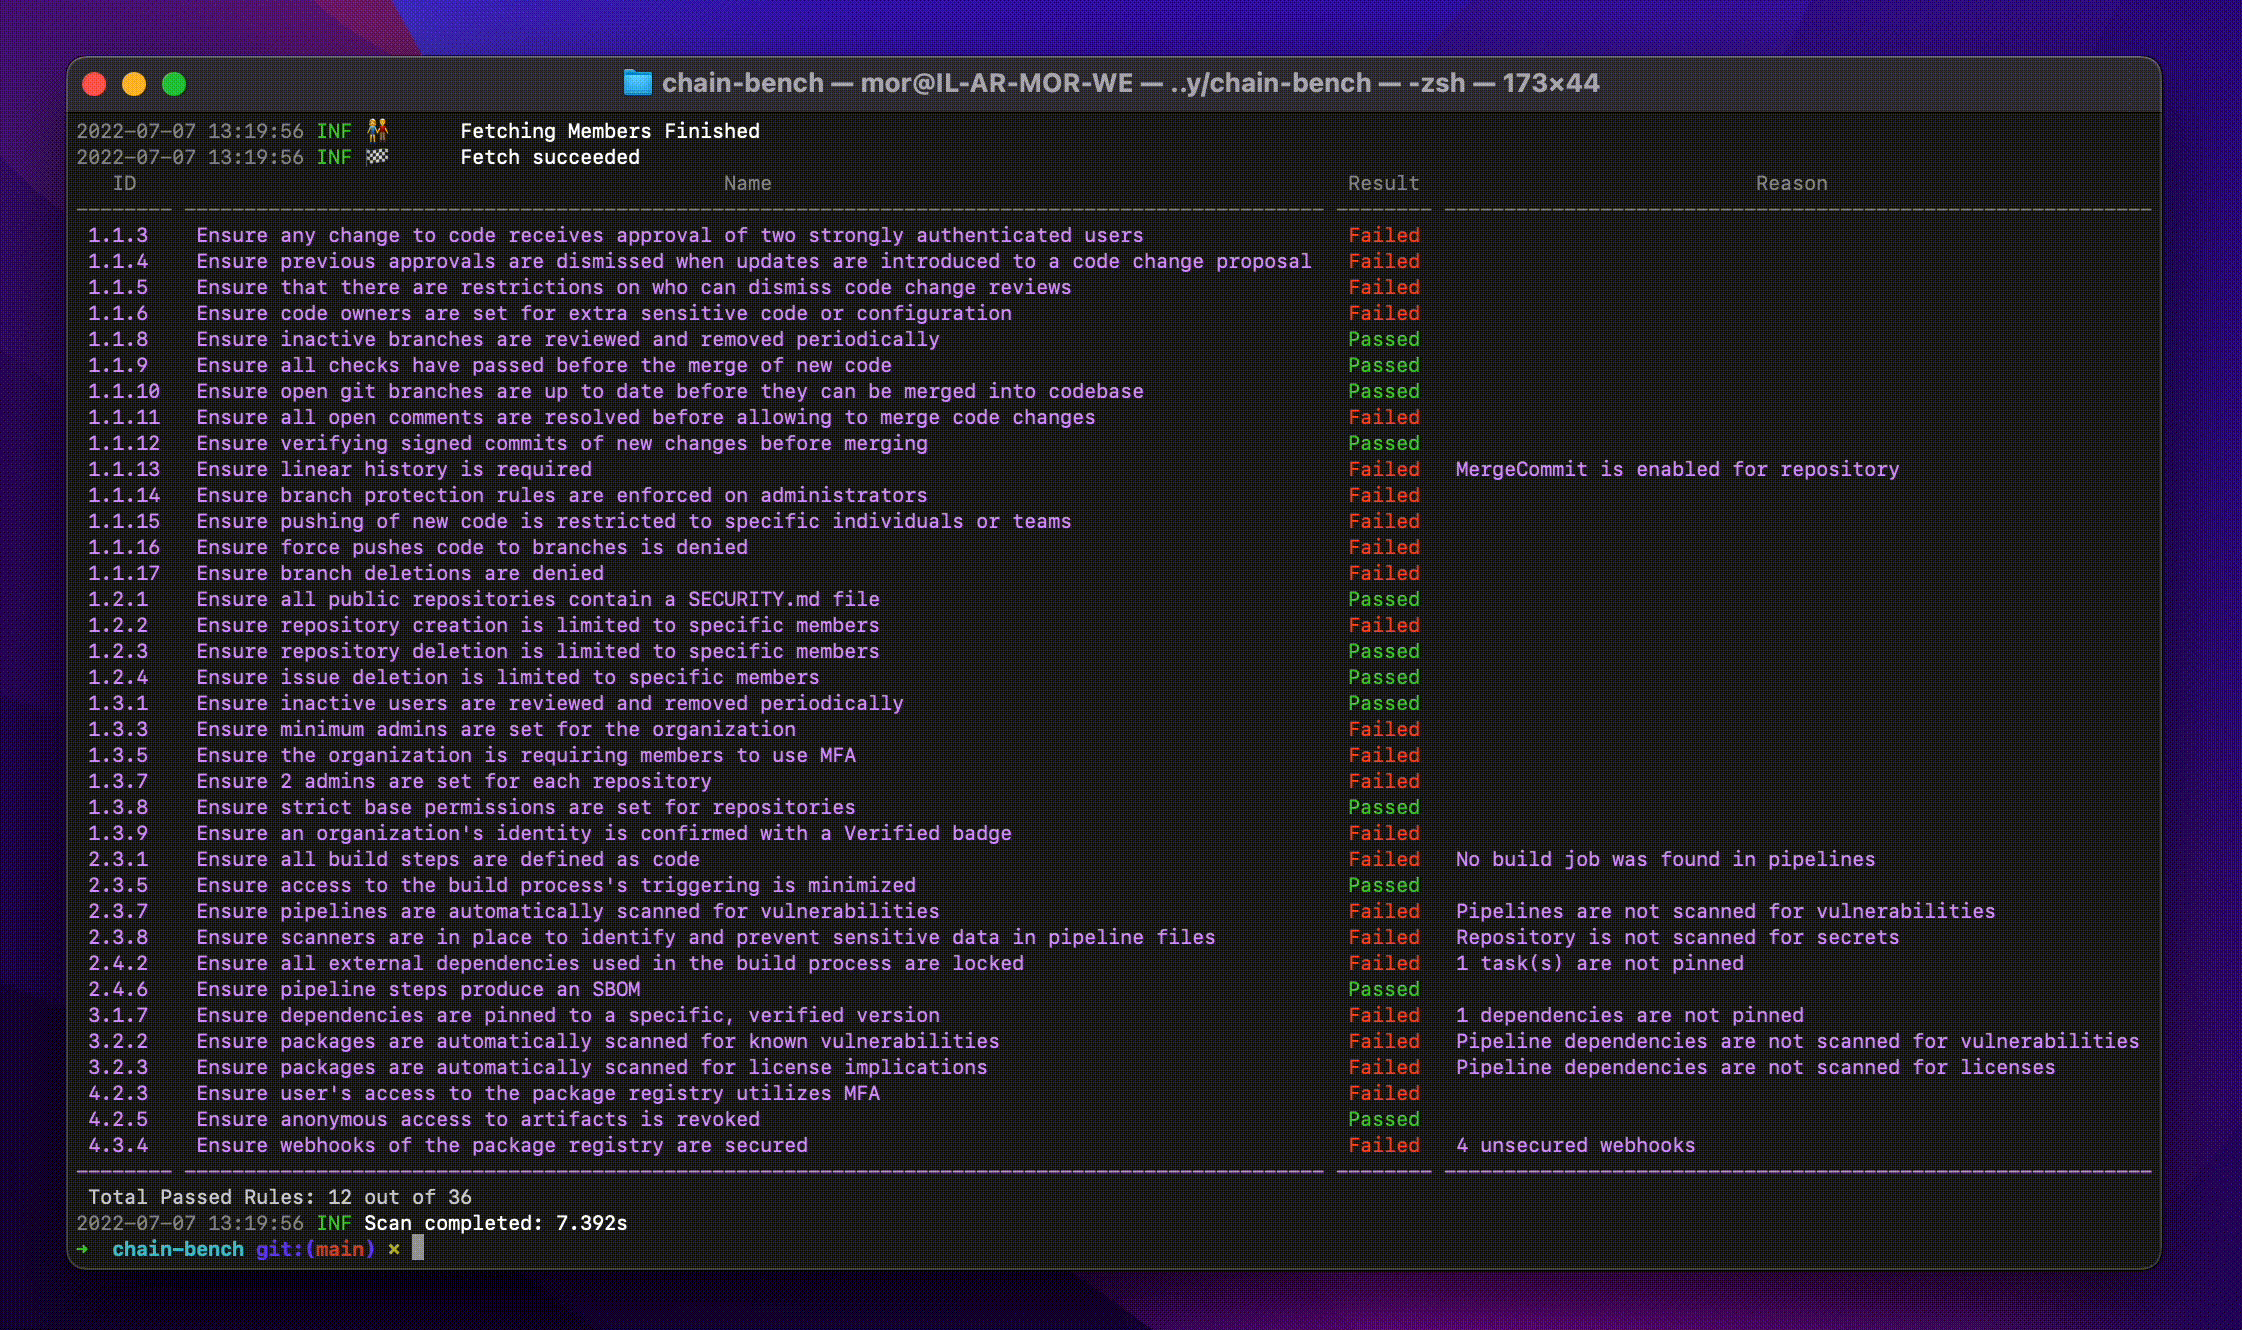
Audits software supply chain security compliance against the CIS benchmark, scanning SCM settings, branch protections, dependencies, and CI/CD…